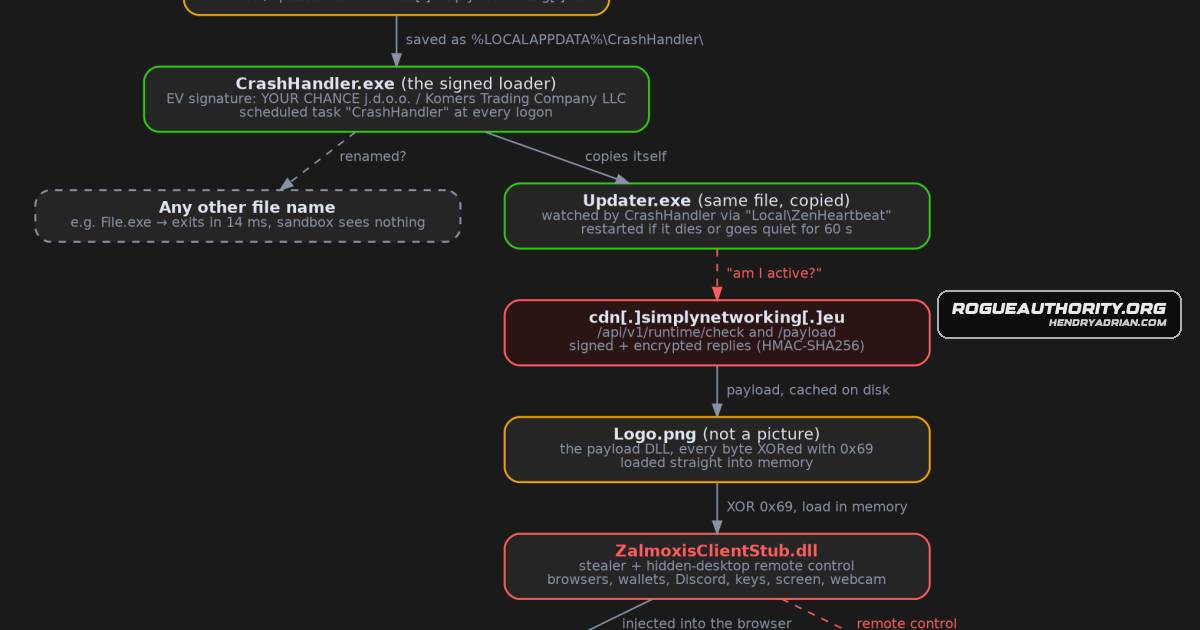
Zalmoxis Stealer Hides Behind Signed Loader and Name-Based Execution
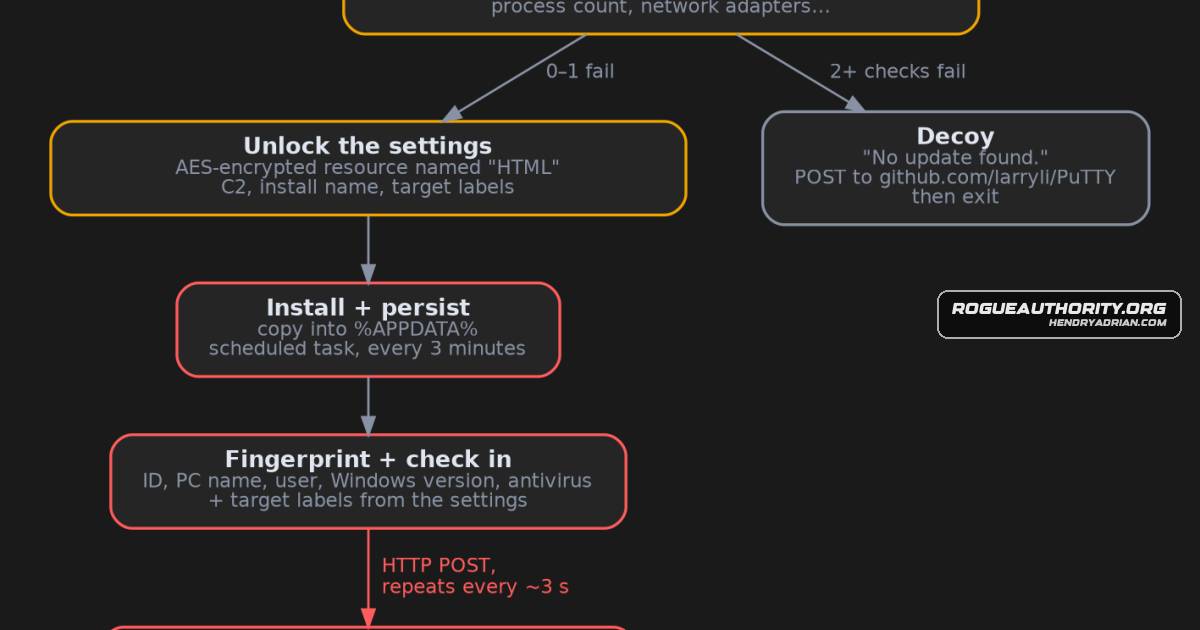
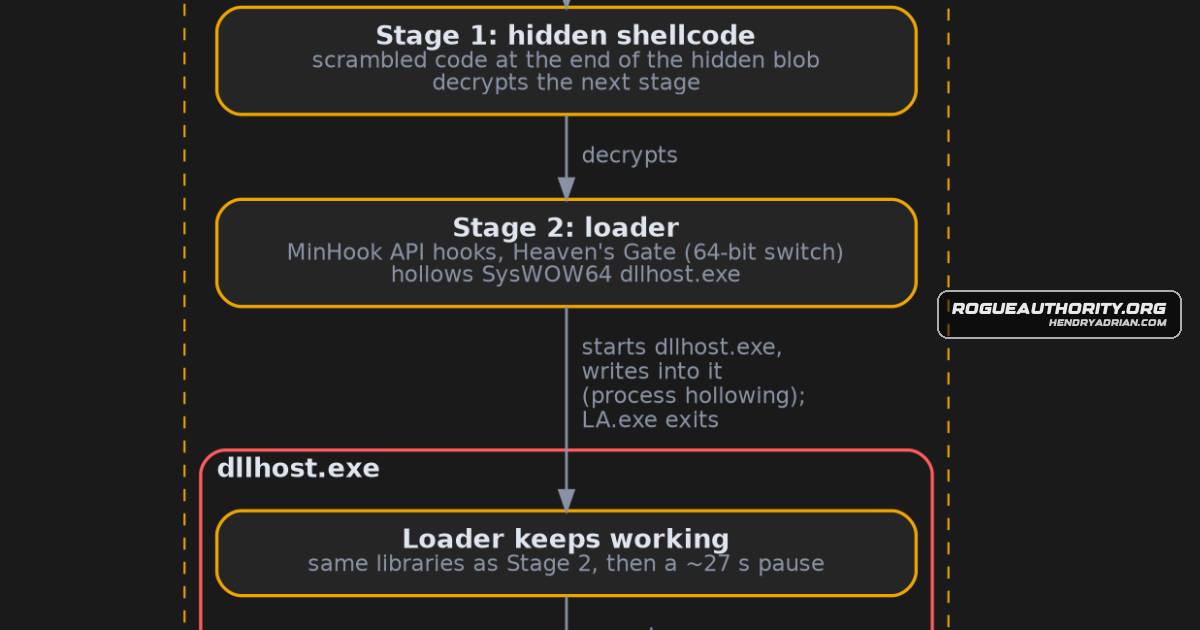
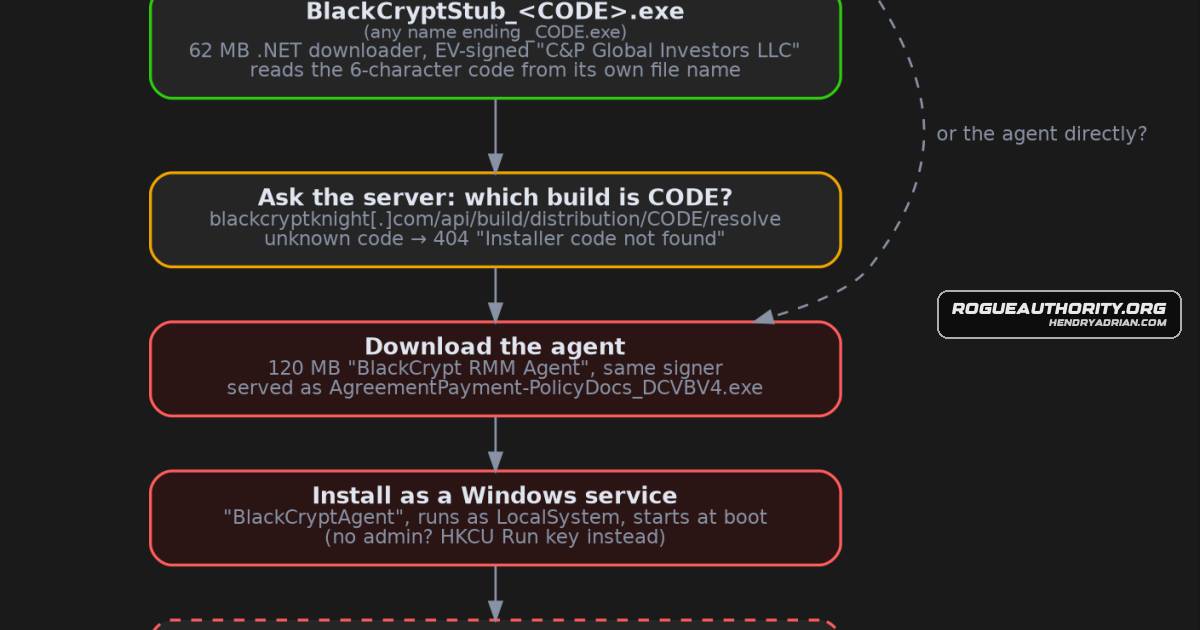
Researchers analyzed a signed loader that activates only under specific filenames, installs persistence, and retrieves the Zalmoxis stealer. The malware targets browser data, crypto wallets, and Chrome’s App-Bound Encryption key.