
BeCtrl Backdoor Uses DLL Sideloading in Policy-Themed Lures
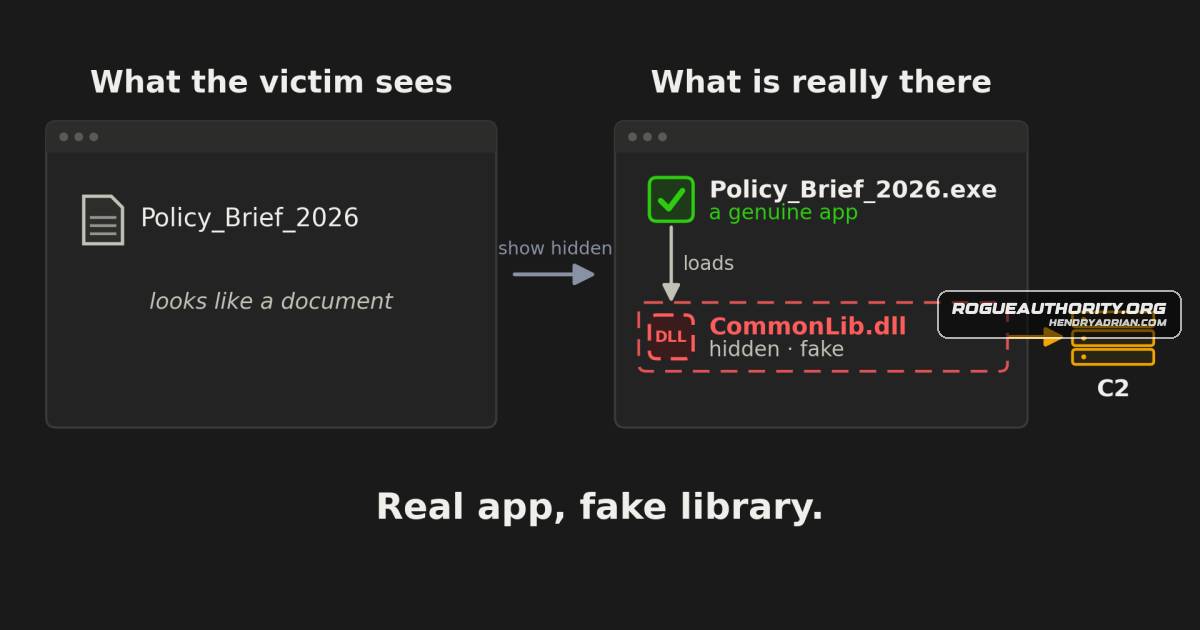
Summary
Researchers analyzed BeCtrl, a backdoor delivered through trojanized PDFgear, Greenshot, and Snoop applications. It uses DLL sideloading, persists via registry entries or scheduled tasks, and supports remote commands and file uploads; observed C2 sessions received no.
Key points
- BeCtrl is delivered in policy-themed archives that contain genuine signed applications alongside malicious DLLs loaded through DLL sideloading.
- The backdoor can run operator-supplied commands and upload files up to 10 MiB to a specified path.
- It persists through registry autostart entries or scheduled tasks and uses parent PID spoofing to make relaunches appear to come from Explorer.
- C2 communication uses a custom PRO1 protocol over UDP port 53, with encrypted WebSocket connections as alternatives.
- Two public sandbox runs connected to the live C2 and exchanged login and heartbeat messages, but no commands or files were observed.
- Analysis linked ten samples across PDFgear, Greenshot, and Snoop builds through a shared RSA public key and protocol; attribution remains unknown.
- Defenders can look for the DeviceSync installation path, a PDFgear file association pointing into it, PRO1 traffic, and QFC-Server TLS certificates.
Article Details
- Attack Vectors
- Policy- and government-themed ZIP lures contain a genuine signed application alongside a malicious DLL.
- DLL sideloading: a modified library placed beside a legitimate host application is loaded and starts the BeCtrl backdoor.
- BeCtrl persists through registry autostart entries; sibling builds also use scheduled tasks or other registry values.
- The backdoor communicates with operator infrastructure using a custom protocol over UDP port 53 and encrypted WebSockets over TLS.
- The operator can execute commands or programs and write files of up to 10 MiB to specified paths.
- Defensive Notes
- Investigate RegExt.exe and CommonLib.dll under C:\ProgramData\Microsoft\DeviceSync\, the specified legacy HKCU Load value, and the PDFgear DeviceSync Run value.
- Look for a PdfGear.App.1 file association pointing into ProgramData\Microsoft\DeviceSync.
- Investigate UDP port 53 traffic to non-resolver IPs when payloads begin with PRO1, and TLS certificates named QFC-Server.
- Do not rely only on the DeviceSync path: the article describes sibling builds using different folders, scheduled tasks, and registry values.
- Treat a signed vendor executable running from a user folder or ProgramData beside an unsigned DLL with the same company name as suspicious.
- The article recommends stopping when an archive presented as a report or assessment opens to an executable, even if Windows displays a valid signature.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 103[.]175[.]50[.]32 | C2 server for the analyzed sample and earlier PDFgear builds. |
| IPV4 | 139[.]84[.]169[.]184 | C2 server used by earlier PDFgear BeCtrl builds. |
| IPV4 | 31[.]59[.]184[.]185 | C2 server for the analyzed sample; used for the BeCtrl PRO1 UDP channel and WebSocket connections. |
| IPV4 | 5[.]253[.]28[.]160 | C2 server used by the Greenshot and Snoop BeCtrl builds. |
| SHA256 | 04c729b5fd540e15952d8d9b954ea5616e9670821b914d0c063b453aface5386 | SHA-256 of a Snoop.Core.dll BeCtrl build. |
| SHA256 | 080cd3b79fa1eb7e523dab3d4edf4e703a33e8530233d99234a3b79d5cbc81aa | SHA-256 fingerprint of the QFC-Server TLS certificate on C2 server 31[.]59[.]184[.]185. |
| SHA256 | 11908bbfdea5e8d9f87fbe045816fff927d17f32b6e89e17ad2be27a57579ff8 | SHA-256 of an archive named for the Nepal-India_Hydropower_Projects lure associated with the BeCtrl campaign. |
| SHA256 | 45095e850d54f5ccf0ca20527ec6f8aed6d5d8eaa3a002255cea06c87627dd48 | SHA-256 of a CommonLib.dll BeCtrl build hosted by PDFgear 2.1.16. |
| SHA256 | 4748571d98c6af34f4967a3886f73b4421239a1203f048140d3bfdaf8aa78937 | SHA-256 of the CommonLib.dll identified as the BeCtrl backdoor in the analyzed sample. |
| SHA256 | 486119e45dadf2b3bafd974e0ea5e1e8e8bc35be320649bfb03ceb12406e7dcd | SHA-256 of a CommonLib.dll BeCtrl build hosted by PDFgear 2.1.18. |
| SHA256 | 692e93fd1fc9922bfea801f8ece908e40c0e299f51e907b39114461dbd3ab66d | SHA-256 of a CommonLib.dll BeCtrl build hosted by PDFgear 2.1.16. |
| SHA256 | 6e802cd13ece669a0467ad828b40076af760ee730636a973245722948cf6807e | SHA-256 fingerprint of the QFC-Server TLS certificate on C2 server 103[.]175[.]50[.]32. |
| SHA256 | 6ed06f2e552f1e42643acf2014dcca678638a3c665d75891c70770f6f4278563 | SHA-256 of an archive named for the MM_Gov_Secure_Portal_Ref_992_2026 lure associated with the BeCtrl campaign. |
| SHA256 | 7ecac9d9d59a43e710a67f8377f40d5c1f50e113dc302db0f0fe377fd0558a52 | SHA-256 of an archive named for the MOU USI-INDSR, TAIWAN lure associated with the BeCtrl campaign. |
| SHA256 | 8507d593880dfeb8b56ca8caceb72887bcb8cd7455891e89be3860bf4d2d5e16 | SHA-256 of an archive named for the MoU_USI_India_and_INDSR_Taiwan lure associated with the BeCtrl campaign. |
| SHA256 | 94275fed254303780d9034c0e6a380db59221b6f13a897bf2a9e49e0fa3b0e64 | SHA-256 of a second archive carrying the analyzed sample's CommonLib.dll. |
| SHA256 | a2b65ea2e827637890d55cf681705ea4639f75fae1a185b05b8425ae6d05a617 | SHA-256 of an archive named for the IPRD-2026_Invitation_Letter lure associated with the BeCtrl campaign. |
| SHA256 | aa424e71f1c25d2455e14dadae35b380950dd4c73988183e7df88e1ed67e4d27 | SHA-256 of a CommonLib.dll BeCtrl build hosted by PDFgear 2.1.18. |
| SHA256 | b542e171c8da17958538d5e5a2b10d2fdc0e2c049d12f7f339d5e723b1238949 | SHA-256 of an archive named for the Thai Talking Points lure associated with the BeCtrl campaign. |
| SHA256 | cdc31b7b51538f9eb766ee21ae25fd4de7197556ac0b8b49ad39aaaa62f5c7a8 | SHA-256 of a Snoop.Core.dll BeCtrl build. |
| SHA256 | d02492ac26c886235ecc6792b630787559f09116e19373edb3021687d5be012e | SHA-256 of an archive named for the Internal_Protocol_Revised_Sept2026 lure associated with the BeCtrl campaign. |
| SHA256 | d429ad9e8710bc1d5fd4f9354812784df3dadc81258f27847a218dce7277d422 | SHA-256 of a CommonLib.dll BeCtrl build hosted by PDFgear 2.1.16. |
| SHA256 | d74fee10090cae17655d137e060398ce6fe52eb811ebc67a439ef37297e5014f | SHA-256 of the Integrated_Assessment_Indo-Pacific_Economic_and_Security.zip sample containing the BeCtrl lure. |
| SHA256 | e026f584df835d58d73f8a05566213b157edb6db8858d067d1076ab457b1c4f2 | SHA-256 of a CommonLib.dll BeCtrl build hosted by PDFgear 2.1.16. |
| SHA256 | e3b3599d9efcaea3fd2c4835c31144b883b4858a9d17d8c1b3bd9a65e31181c5 | SHA-256 of an MM_Gov_Secure_Portal_Ref_992_2026 archive associated with the BeCtrl campaign. |
| SHA256 | e650a935e00bb51e2bcbf975a7bdfc0f03d18e9079e4bceaeff2c915d194231b | SHA-256 of a Greenshot.Base.dll BeCtrl build. |
MITRE ATT&CK
T1053.005 · Scheduled TaskThe article reports scheduled-task persistence in Greenshot and Snoop sibling builds.T1059.003 · Windows Command ShellThe operator can execute commands through cmd.exe /c, or specify another program to run.T1071.001 · Web ProtocolsBeCtrl also uses WebSocket connections over TLS for its C2 channel on ports including 443 and 80.T1095 · Non-Application Layer ProtocolBeCtrl communicates using its custom PRO1 protocol over UDP port 53 rather than DNS.T1105 · Ingress Tool TransferThe operator can send files to BeCtrl and have them written to a specified path on the infected system.T1134.004 · Parent PID SpoofingBeCtrl uses parent PID spoofing so the relaunched process and later operator-launched programs appear to have Explorer as their parent.T1204.002 · Malicious FileThe lure presents an executable inside a policy-themed archive as a document, relying on a user to open the disguised program.T1547.001 · Registry Run Keys / Startup FolderBeCtrl establishes logon persistence using registry autostart values, including the legacy HKCU Load value and Run keys.T1573.001 · Symmetric CryptographyAfter login, BeCtrl encrypts session traffic with AES-256-GCM using a session key protected with the operator's RSA public key.T1574.002 · DLL Side-LoadingThe malicious CommonLib.dll is placed beside a legitimate host executable and loaded in place of the expected library to start BeCtrl.
Malware
Products
GreenshotGreenshot (a free screenshot tool), with a fake Greenshot.Base.dll;PDFgearInside is a "document" that is a validly signed PDF editor "PDFgear" and a hidden CommonLib.dll that the program loads automatically.SnoopSnoop (a free developer tool for inspecting Windows apps), with a fake Snoop.Core.dll.
Tools
ANY.RUNTools used: Malcat, ILSpy (ilspycmd), capa, osslsigncode, tshark, Recorded Future Triage, ANY.RUN, Censys and VirusTotal.CensysTools used: Malcat, ILSpy (ilspycmd), capa, osslsigncode, tshark, Recorded Future Triage, ANY.RUN, Censys and VirusTotal.KesaKodeCode-similarity search (KesaKode) found no meaningful match to known families either.Recorded Future TriageTools used: Malcat, ILSpy (ilspycmd), capa, osslsigncode, tshark, Recorded Future Triage, ANY.RUN, Censys and VirusTotal.VirusTotalTools used: Malcat, ILSpy (ilspycmd), capa, osslsigncode, tshark, Recorded Future Triage, ANY.RUN, Censys and VirusTotal.
Countries
IndiaUSI (the United Service Institution of India) and INDSR (Taiwan’s Institute for National Defense and Security Research) are real defence think tanks whose names the lures borrow.MalaysiaBoth servers in our sample are rented Windows machines, one in India and one in Malaysia.Myanmar"MM" in the Greenshot lure is the country code for Myanmar, which fits the UTC+06:30 timestamps in our ZIP.NepalNepal-India_Hydropower_Projects (program named Nepal-India_Hydropower_Cooperation_Proposal_2026.exe)SingaporeM247 (Singapore)TaiwanMOU USI-INDSR, TAIWANThailandThai Talking Points(PM) 14 00hrs(Final version) – PW