
Signed Funding-Form Decoy Delivers an Unattributed Plugin-Based RAT
Summary
Analysis traces a signed funding-form decoy through DLL side-loading to an unattributed plugin-based RAT. Sandbox traffic showed an operator viewing the screen and browsing files; the article also details persistence and defensive hunting advice.
Key points
- The signed executable displays a clean bilingual funding-form PDF while deploying its payload; the EV signature does not establish that the file is safe.
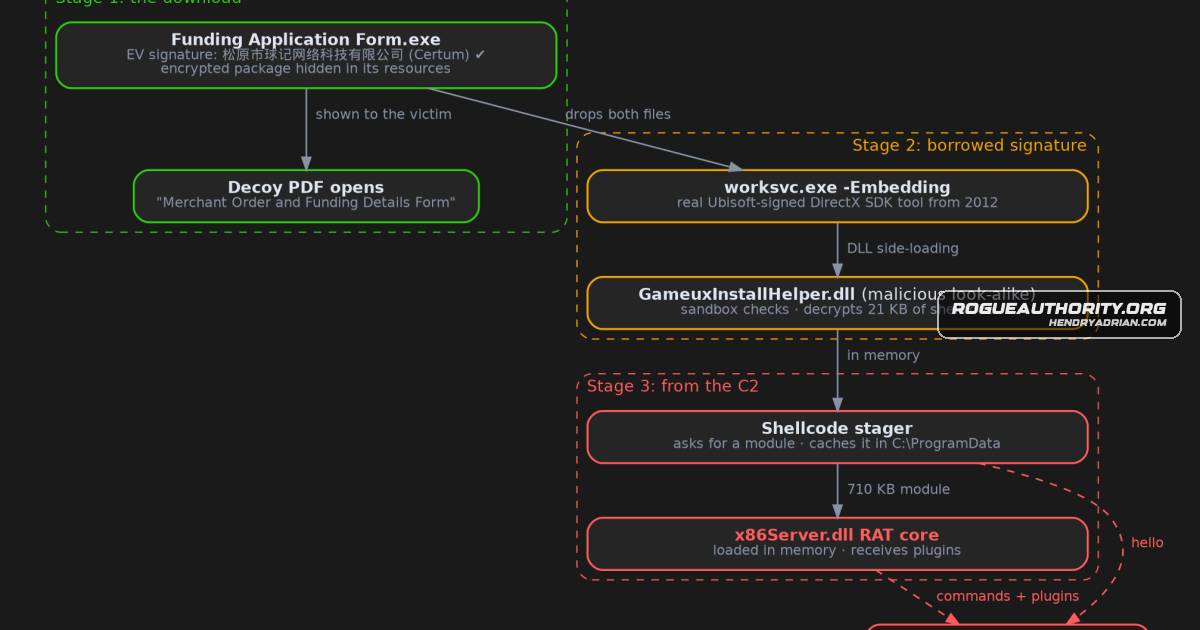
- The dropper uses a genuine Ubisoft-signed DirectX tool to load a malicious DLL, which launches a shellcode stager that downloads the RAT core.
- In sandbox runs, the server supplied eight plugins, including screen viewing, hidden-desktop access, browser-data theft, file management, system management and webcam capture.
- During a longer deception-sandbox run, an operator viewed the screen, listed browser profiles and browsed file and folder listings; the article reports no file contents were returned.
- The persistence plugin uses a WNF-triggered scheduled task with backup startup methods; the article describes a LuaJIT-based execution chain.
- The sample remains unattributed: the authors found the sandbox’s DanaBot label was a false match and said the code did not closely match a known family.
- The article recommends blocking the C2 IP and hunting for the side-loaded DLL, related command lines, scheduled-task artifacts and cached RAT files.
Article Details
- Attack Vectors
- A signed executable disguised as a funding application drops a clean decoy PDF and malicious files into %LOCALAPPDATA%.
- The dropper launches a genuine Ubisoft-signed GDFInstall program beside a malicious GameuxInstallHelper.dll, which is loaded through DLL side-loading.
- The malicious DLL runs an in-memory shellcode stager that downloads the RAT core from the C2 server.
- A persistence plugin downloads another DLL and establishes scheduled-task persistence; backup mechanisms include a Startup-folder shortcut.
- The RAT receives plugins on demand, enabling remote screen viewing, browser-data access, file browsing, system management, webcam access, and other functions.
- Defensive Notes
- Do not treat an executable funding form, invoice, or order form as a document, even if it opens a PDF or has a valid signature.
- Block 192[.]238[.]177[.]20 and treat files signed with certificate serial 3538cc642d4c910e8ebb661b9b4fe253 as malicious, as advised by the article.
- Hunt for GameuxInstallHelper.dll loaded by a Ubisoft-signed GDFInstall program from a user folder, and for worksvc.exe -Embedding.
- Look for rundll32.exe using ,#1 MyCustomParam123, and wscript.exe launched by Task Scheduler from C:\ProgramData\<8 hex>\; also search for h_x86_*.dat and s_x86_*.dat files.
- Check the TaskScheduler\Schedules registry path for entries that launch scripts, and monitor for unexpected shadow-copy creation and qcap.dll loading.
- If the executable was run, assume browser sessions may be compromised; sign out everywhere and change passwords from a clean device.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 192[.]238[.]177[.]20 | Attacker-controlled C2 IP used by the stager and RAT; the article also advises blocking it. |
| SHA256 | 27bbf23d973825bcdb94367f585f5e3eda7bc14e05a24b373916a1e0188f7175 | SHA-256 of MainBussinessServer.dll, a RAT plugin. |
| SHA256 | 303dea5f95f218b87f973a4818b636e8bbf15d0ebf4b1b869d8ef27c19a9d50e | SHA-256 of the malicious GameuxInstallHelper.dll side-loaded by the signed program. |
| SHA256 | 3387a45ddd8ca576e03115b3d96df00bec5924e0cac04e34bb0afaee2f72f82d | SHA-256 of CameraServer.dll, a RAT webcam plugin. |
| SHA256 | 3e62e44398d2ef6ab3fbb166be11a42c5efbd4ea14e11aa794e14514b51beaa1 | SHA-256 of the RAT module downloaded from the C2 server. |
| SHA256 | 5055e333daee878332927693cca0ee398b131d1cd4a5c224565d6a32f7ebc36c | SHA-256 of x86Server.dll, the RAT core. |
| SHA256 | 583cd2b314ea08b54c082e0f8fd1bb55694b6c1f0b695cdac881455e8dfb850e | SHA-256 of SystemMgrServer.dll, a RAT system-management plugin. |
| SHA256 | 608271220c42acf369c2f4404f411204663db257deeed43217a15d62b9756ad4 | SHA-256 of StartupItemServer.dll, the RAT persistence plugin. |
| SHA256 | 73412a80b878a4777f3afc1f10ab16f63a7a407bbcffa14bf0e68be14179bedf | SHA-256 of RemoteScreenServer.dll, a RAT plugin for viewing the victim's screen. |
| SHA256 | 851678eb93f204e84c61b4faf89bd47892005fa1565f9dcab2d861bc2ebea3b5 | SHA-256 of HiddenDesktopServer.dll, a RAT hidden-desktop plugin. |
| SHA256 | a1538039a7e07e7d00de3aeb132ec723e0656f39091be3fb800f65d27294ddba | SHA-256 of the shellcode stager that downloads the RAT. |
| SHA256 | a62c87a28f32b2a2965653f587cd3cfdcc42d13a59bc365261adc7cd342235cc | SHA-256 of the malicious Funding Application Form.exe dropper. |
| SHA256 | a8610d6c480a7bec9b047484d65bbd4393ee00357f94dd31bbc972cd75828319 | SHA-256 of WebDataServer.dll, a RAT plugin described as stealing browser data. |
| SHA256 | cc8dd9cbf2ea6177b7bc2d1d01e7cc5120628509d3795453eeaef26ae468bd13 | SHA-256 of FileMgrServer.dll, a RAT file-management plugin. |
| SHA256 | f1fd6975b7e736239d355596f0a43e38eb6e437f2b31460a7b92c3f9ad743678 | SHA-256 of the malicious DLL downloaded for persistence. |
| URL | hxxp[:]//192[.]238[.]177[.]20:7858/dcd | URL used by the persistence plugin to download a malicious DLL. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe dropper stores its payload in an encrypted, compressed resource that it decrypts with ChaCha20 and decompresses with LZ4.T1053.005 · Scheduled TaskThe persistence plugin creates a scheduled task using Windows Task Scheduler mechanisms, including an internal-event trigger.T1056.001 · KeyloggingMainBussinessServer contains keylogging functionality, although the article says keylogging was not observed in the sandbox traffic.T1057 · Process DiscoveryThe operator used SystemMgrServer to retrieve lists of running programs and open windows.T1059.005 · Visual BasicA scheduled task launches wscript.exe to run a VBS script in the persistence chain.T1083 · File and Directory DiscoveryThe operator used FileMgrServer to list drives and browse the victim's Recent files and Desktop; the observed traffic returned folder listings, not file contents.T1105 · Ingress Tool TransferThe shellcode stager downloads a RAT module from the C2 server; the persistence plugin also downloads a DLL.T1113 · Screen CaptureThe operator used the RemoteScreenServer plugin to view the victim's screen during the longer sandbox run.T1125 · Video CaptureThe CameraServer plugin loads Windows' video-capture library to access a webcam; the article reports the plugin was sent, but does not confirm captured footage.T1140 · Deobfuscate/Decode Files or InformationThe dropper decrypts and decompresses its embedded package, and the malicious DLL reverses and XOR-decodes the shellcode before execution.T1204.002 · Malicious FileThe victim is prompted to open Funding Application Form.exe, which masquerades as a business form.T1218.011 · Rundll32The persistence chain invokes the downloaded DLL using rundll32.exe with the argument #1 MyCustomParam123.T1547.001 · Registry Run Keys / Startup FolderThe article says a Startup-folder shortcut is maintained as a backup persistence method.T1555.003 · Credentials from Web BrowsersThe WebDataServer plugin is described as collecting browser profile data; the article says its code can also read and plant cookies, but does not report observing browser-data theft in the traffic.T1574.002 · DLL Side-LoadingThe dropper places a malicious GameuxInstallHelper.dll beside a genuine signed GDFInstall program, which loads the DLL by its expected name.
Vendors
CertumSigned: Certum EV certificate, serial 3538cc642d4c910e8ebb661b9b4fe253, file built on 1 November 2026.Sangfor TechnologiesThe LuaJIT runner and its library carry a valid signature from Sangfor Technologies, a Chinese security vendor.UbisoftBorrowed trust: the dropper runs a genuine 2012 Ubisoft-signed DirectX tool, which loads a malicious DLL placed next to it.
Products
BraveIt packs the profile folders of Chrome, Edge, Brave, Firefox and the Chinese 360 browsers into a zip.DirectX SDKIt is GDFInstall, a sample program from Microsoft’s DirectX SDK, signed by Ubisoft in 2012.Edgesent WebDataServer and got back a list of the user’s browser profiles (Edge and Chrome), including whether Telegram or WhatsApp Desktop was present;Google Chromesent WebDataServer and got back a list of the user’s browser profiles (Edge and Chrome), including whether Telegram or WhatsApp Desktop was present;Microsoft WindowsIf Windows is in test-signing mode (common on analysis machines), it shows a fake “Initialization failed.Mozilla FirefoxIt packs the profile folders of Chrome, Edge, Brave, Firefox and the Chinese 360 browsers into a zip.
Tools
ANY.RUNTools used: Malcat, KesaKode, Python (pefile, cryptography, lz4), speakeasy, Ghidra, capa, ANY.RUN, Deception Pro, Triage and tshark.capaTools used: Malcat, KesaKode, Python (pefile, cryptography, lz4), speakeasy, Ghidra, capa, ANY.RUN, Deception Pro, Triage and tshark.Deception.ProFor this, we use Deception.Pro.GhidraTools used: Malcat, KesaKode, Python (pefile, cryptography, lz4), speakeasy, Ghidra, capa, ANY.RUN, Deception Pro, Triage and tshark.KesaKodeTools used: Malcat, KesaKode, Python (pefile, cryptography, lz4), speakeasy, Ghidra, capa, ANY.RUN, Deception Pro, Triage and tshark.MalcatTools used: Malcat, KesaKode, Python (pefile, cryptography, lz4), speakeasy, Ghidra, capa, ANY.RUN, Deception Pro, Triage and tshark.speakeasyTools used: Malcat, KesaKode, Python (pefile, cryptography, lz4), speakeasy, Ghidra, capa, ANY.RUN, Deception Pro, Triage and tshark.TriageTools used: Malcat, KesaKode, Python (pefile, cryptography, lz4), speakeasy, Ghidra, capa, ANY.RUN, Deception Pro, Triage and tshark.tsharkTools used: Malcat, KesaKode, Python (pefile, cryptography, lz4), speakeasy, Ghidra, capa, ANY.RUN, Deception Pro, Triage and tshark.