
Fake Microsoft-Branded DUI70.dll Uses BITS to Relaunch a Backdoor
Summary
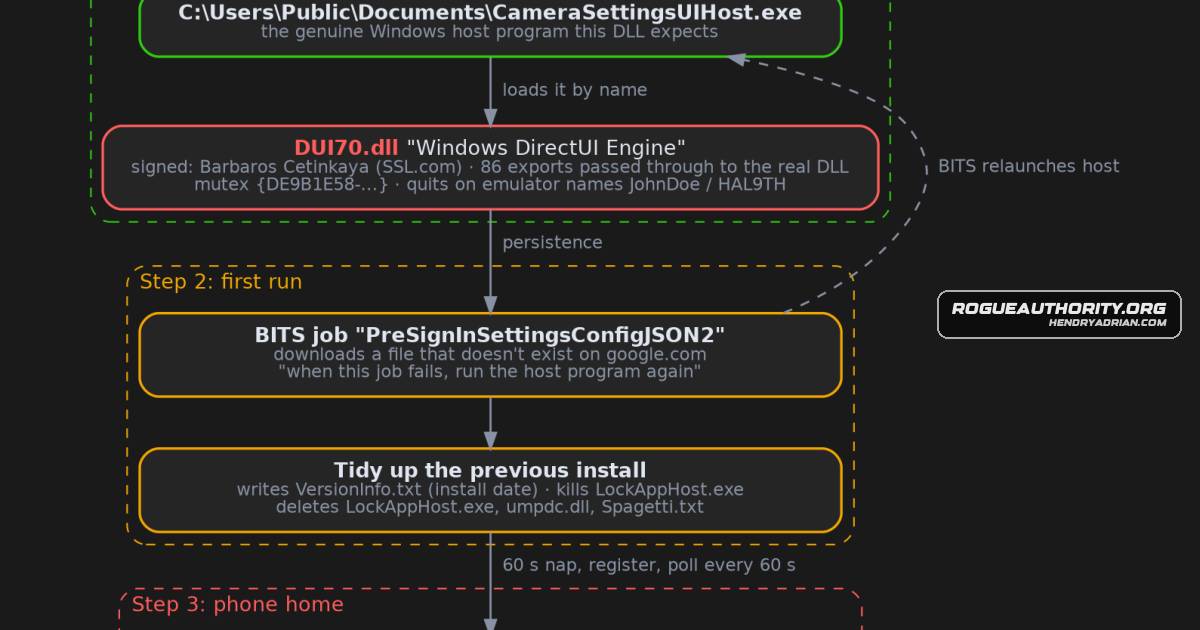
Analysis details a fake Microsoft-branded DUI70.dll, signed by an individual, that sideloads through CameraSettingsUIHost.exe and uses a failing BITS job to relaunch. The 14-command backdoor's C2 was not observed; its listed domains no longer resolved.
Key points
- DUI70.dll claims to be a Microsoft component but was signed with a valid certificate issued to an individual, according to the analysis.
- The DLL sideloads alongside the genuine CameraSettingsUIHost.exe and forwards its 86 functions to the real Windows DLL.
- It creates a BITS job named PreSignInSettingsConfigJSON2 that requests a nonexistent resource at google[.]com; the job's failure triggers the host program to relaunch.
- The analysis says the job may relaunch the program after a restart, but the researchers did not observe this across a restart.
- The backdoor supports 14 commands, including file transfer, program execution, shell commands, and process management.
- The DLL is configured to contact healthlys[.]com and four Azure App Service hostnames, but the sandbox did not observe C2 communication and none of the five names resolved when checked.
- The article recommends reviewing BITS jobs for suspicious notification commands and checking public folders for named files associated with the sample.
Article Details
- Attack Vectors
- A malicious DUI70.dll is sideloaded beside the genuine CameraSettingsUIHost.exe in C:\Users\Public\Documents.
- The DLL creates a BITS job with a notify command that relaunches the host program when the job fails, providing persistence.
- The backdoor communicates with its C2 servers over HTTPS and supports remote shell commands, file upload and download, and program execution.
- Defensive Notes
- Inspect BITS jobs for PreSignInSettingsConfigJSON2 and for notify commands that launch programs outside C:\Windows.
- Hunt in C:\Users\Public\Documents for DUI70.dll, umpdc.dll, CameraSettingsUIHost.exe, LockAppHost.exe, VersionInfo.txt, and Spagetti.txt.
- Investigate HTTPS POST requests using the user agent WinHTTP Example/1.0 and paths under /market-api/.
- Treat Windows components located outside C:\Windows, especially files claiming to be Microsoft products but signed by an individual, as suspicious.
- The article recommends alerting on certificate serial 237DD9C69CE233B0CF24AA24AA803DA4.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | healthlys[.]com | Reported C2 domain used by the backdoor. |
| HOSTNAME | sync-endpoint-1[.]azurewebsites[.]net | Reported Azure App Service hostname used as a fallback C2 endpoint. |
| HOSTNAME | sync-endpoint-2[.]azurewebsites[.]net | Reported Azure App Service hostname used as a fallback C2 endpoint. |
| HOSTNAME | sync-endpoint-3[.]azurewebsites[.]net | Reported Azure App Service hostname used as a fallback C2 endpoint. |
| HOSTNAME | sync-endpoint[.]azurewebsites[.]net | Reported Azure App Service hostname used as a fallback C2 endpoint. |
| SHA256 | adf0957559b8914b125ef263959f2882481df3b5dd0472888bf07e4e455a5d34 | SHA-256 hash of the malicious DUI70.dll sample. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe article reports that strings and Windows function names in the DLL are scrambled using XOR.T1033 · System Owner/User DiscoveryThe backdoor reports the computer name and user name to its operator.T1036.005 · Match Legitimate Resource Name or LocationThe DLL claims Microsoft Windows DirectUI Engine version information and uses a BITS job name resembling a OneDrive job.T1041 · Exfiltration Over C2 ChannelThe backdoor can upload files from the victim's computer to its server over the C2 channel.T1057 · Process DiscoveryThe backdoor can list running processes.T1059.003 · Windows Command ShellThe backdoor can run shell commands and invokes cmd.exe /C for .bat and .cmd files.T1071.001 · Web ProtocolsThe backdoor communicates with its servers over HTTPS using paths styled as an online shop API.T1082 · System Information DiscoveryThe backdoor's registration data includes the victim machine's IP addresses.T1083 · File and Directory DiscoveryThe backdoor can list the contents of folders and enumerate drives.T1105 · Ingress Tool TransferThe operator can download files from the server to the victim's computer and run downloaded files.T1197 · BITS JobsThe DLL creates a BITS job whose notify command relaunches the host program when the download fails.T1497.001 · System ChecksThe DLL exits when it detects the username JohnDoe or computer name HAL9TH, which the article identifies as names used by Windows Defender's built-in emulator.T1574.001 · DLLThe malicious DUI70.dll is placed beside the genuine CameraSettingsUIHost.exe so the program loads the malicious DLL.
Vendors
MicrosoftDUI70.dll claims to be Microsoft’s "Windows DirectUI Engine," but it was signed with a code-signing certificate issued to an individual, Barbaros Cetinkaya.SSL.comSignature: SSL.com certificate for "Barbaros Cetinkaya" (serial 237DD9C69CE233B0CF24AA24AA803DA4), valid and not revoked at the time of writing.
Products
Tools
ANY.RUNTools used: Malcat, capstone, Ghidra (headless), FLOSS, capa, osslsigncode and ANY.RUN.capaTools used: Malcat, capstone, Ghidra (headless), FLOSS, capa, osslsigncode and ANY.RUN.CapstoneTools used: Malcat, capstone, Ghidra (headless), FLOSS, capa, osslsigncode and ANY.RUN.FLOSSTools used: Malcat, capstone, Ghidra (headless), FLOSS, capa, osslsigncode and ANY.RUN.GhidraTools used: Malcat, capstone, Ghidra (headless), FLOSS, capa, osslsigncode and ANY.RUN.MalcatTools used: Malcat, capstone, Ghidra (headless), FLOSS, capa, osslsigncode and ANY.RUN.osslsigncodeTools used: Malcat, capstone, Ghidra (headless), FLOSS, capa, osslsigncode and ANY.RUN.