
Signed Photo-Themed Executable Installs Python-Based Wraith Remote-Control Agent
Summary
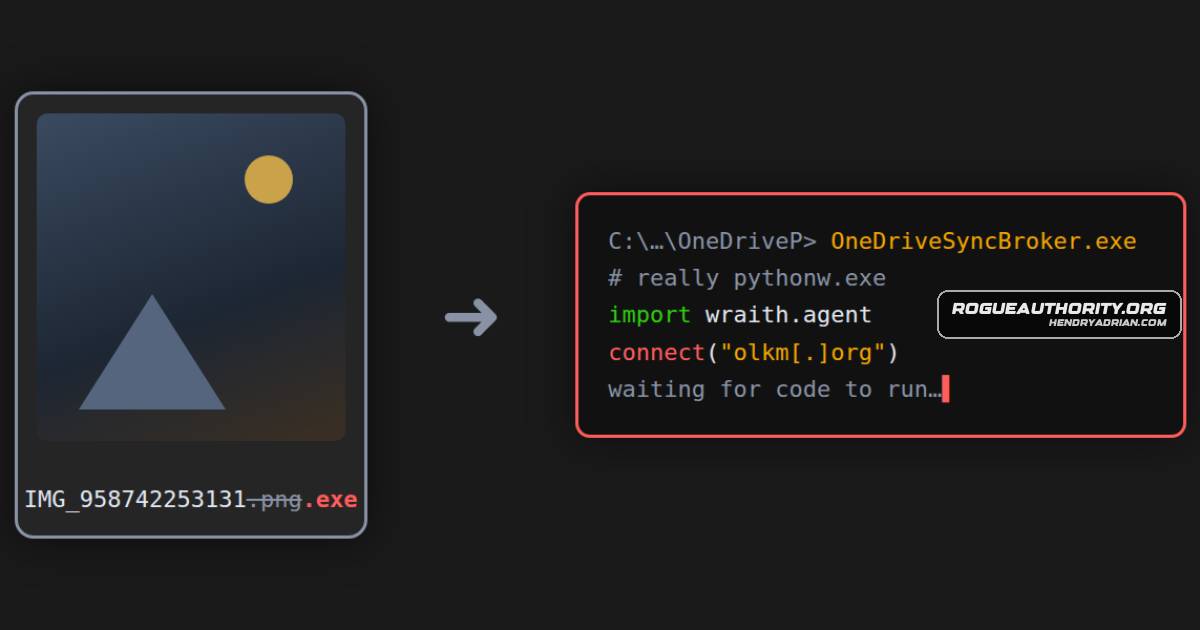
Analysis of a photo-themed Windows executable found it installs legitimate Python files and a Wraith agent that runs operator-supplied code, with DNS-based fallback and server-delivered persistence observed in a sandbox.
Key points
- The photo-named executable checks for sandbox-like sleep timing and recent user input, then attempts a hidden Windows Installer deployment; a fallback displays a decoy while unpacking a junk-wrapped cabinet archive.
- The payload places genuine Python 3.8 files in an AppData folder named OneDriveP and uses sitecustomize.py to launch the Wraith agent when the renamed interpreter starts.
- The agent connects to olkm[.]org over WebSocket, identifies the computer and user, and runs Python modules sent by the operator; researchers could not inspect the encrypted module contents.
- A DNS-based fallback checks TXT-record markers and generates candidate domains; none of the candidate domains were registered at the time of the analysis.
- In one sandbox run, the server sent code that created Startup shortcuts and a Run key entry; these persistence entries did not appear in a second run.
- Microsoft revoked the short-lived Trusted Signing certificate. Suggested hunting indicators include the OneDriveP folder, sitecustomize.py, the Wraith mutex, and Python processes using OneDrive-like names.
Article Details
- Attack Vectors
- A Windows executable named and presented like a phone photo serves as the initial lure.
- The executable attempts a hidden Windows Installer installation from msvcic[.]com; if that fails, it displays a decoy while downloading and unpacking a cabinet archive.
- The installed Python agent connects to an operator-controlled server over WebSocket and executes Python modules sent by the server.
- Defensive Notes
- Treat affected computers as fully compromised because the operator can send and execute arbitrary Python code; disconnect them and change passwords from a different device.
- Investigate %LOCALAPPDATA%\OneDriveP\, sitecustomize.py in an embeddable Python folder, and python38._pth files ending in import site.
- Check the user Startup folder and HKCU\Software\Microsoft\Windows\CurrentVersion\Run for OneDriveUpdate shortcuts or values.
- Look for Python processes running from AppData under OneDrive-like names, the mutex Local\WraithClient_7f3a9c21, WebSocket connections to /socket.io/, and DNS TXT lookups of random-looking 16-character domains.
- Do not open photo-like files delivered as .exe files.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | msvcic[.]com | Payload and decoy host used by the malicious executable. |
| DOMAIN | olkm[.]org | Command server contacted by the wraith agent over WebSocket. |
| SHA256 | 58376da37fb3877a138ee23d7f26dca4b3a039710dacf7068fd5ab4b9b532548 | SHA-256 hash of the junk-wrapped cabinet archive downloaded by the loader. |
| SHA256 | 951f09debd9fe0f7d5ee0ff7230f568822e1f60ecd97a1824f8f98a0b52ae911 | SHA-256 hash of the decoy “Transfer details” PNG. |
| SHA256 | a4dc7f6ca11bd07162b43f6c6804927569c97c5640b4c3c6dde0c150402a63e1 | SHA-256 hash of the IMG_958742253131.exe loader. |
| SHA256 | acbd65cf8efa6e318b241bd62d52a7664c0ce107cebdc27542aaa0cab6afa122 | SHA-256 hash of the malicious “Photo Gallery Package” MSI. |
| SHA256 | b471b01310fa00aaf83b757407405d47c8a54930593c3ce105bd23c5bad2dc4f | SHA-256 hash of the wraith DNS fallback component sfinder.py. |
| SHA256 | c2e01eb210673ea8c31249bfbd37c36856e8eaa808455d4e0def8c49727a4e96 | SHA-256 hash of sitecustomize.py, which loads the wraith agent when Python starts. |
| SHA256 | d0d7b8b2be9ba8a0f794ec2b67171d78c74616233c171f58eb06f75ef8493317 | SHA-256 hash of the wraith server-address component surl.py. |
| SHA256 | ee24ac09796a0d29e8f41a20d2cd2a41db8870a015821b7b5ee03b7d4a5942cb | SHA-256 hash of the wraith agent file agent.py. |
| SHA256 | fcb8ef5a82486b5d42246d27166c26aed413c02d045ad04629159700da27d440 | SHA-256 hash of the unwrapped cabinet archive containing the installed files. |
| URL | hxxps[:]//msvcic[.]com/cdn/ | Payload-delivery URL path on the host identified as serving the installer or changing payload downloads. |
| URL | hxxps[:]//msvcic[.]com/media/IMG_958742253131[.]png | URL used to deliver the decoy image alongside the malicious payload. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe loader's web address, folder names, and campaign code are encrypted, and the downloaded cabinet archive is wrapped with junk bytes.T1036 · MasqueradingThe executable is presented as a photo, and the installed Python interpreter is renamed OneDriveSyncBroker.exe to resemble legitimate software.T1059.006 · PythonThe wraith agent executes Python modules pushed by its server.T1071.001 · Web ProtocolsThe wraith agent communicates with olkm[.]org over a WebSocket using Socket.IO.T1105 · Ingress Tool TransferThe loader downloads an installer package or, on its fallback path, a cabinet archive and decoy from msvcic[.]com.T1497.001 · System ChecksThe loader checks recent mouse or keyboard activity and exits if the computer has been inactive for a minute, a check the article says automated analysis systems often fail.T1497.003 · Time Based ChecksThe loader measures a two-second sleep and exits if the elapsed time suggests the environment may be accelerating or disrupting sleeps.T1547.001 · Registry Run Keys / Startup FolderThe server-delivered persistence creates a Startup-folder shortcut and a Run key value that relaunch the renamed Python interpreter.T1568.002 · Domain Generation AlgorithmsThe sfinder component computes candidate domains using a domain-generation algorithm and checks DNS records for a marker and replacement server.
Malware
Vendors
MicrosoftIMG_958742253131.exe is named like a phone photo, but it’s a Windows program signed with a three-day Microsoft Trusted Signing certificate issued to “MARQUEE AUDIO VISUAL LIMITED”.Python Software FoundationThe main program, OneDriveSyncBroker.exe, is the genuine pythonw.exe, signed by the Python Software Foundation, just renamed.
Products
Microsoft OneDriveStep 3: real Python, wearing a OneDrive costumeMicrosoft Trusted SigningIMG_958742253131.exe is named like a phone photo, but it’s a Windows program signed with a three-day Microsoft Trusted Signing certificate issued to “MARQUEE AUDIO VISUAL LIMITED”.Microsoft WindowsIMG_958742253131.exe is named like a phone photo, but it’s a Windows program signed with a three-day Microsoft Trusted Signing certificate issued to “MARQUEE AUDIO VISUAL LIMITED”.PythonIt quietly installs a real copy of Python into a folder called OneDriveP, renames Python to OneDriveSyncBroker.exe, and adds a small Python file, run every time Python starts, that launches a remote-access agent its
Tools
ANY.RUNTools used: Malcat, capa, msitools, cabextract, tshark and ANY.RUN.cabextractTools used: Malcat, capa, msitools, cabextract, tshark and ANY.RUN.capaTools used: Malcat, capa, msitools, cabextract, tshark and ANY.RUN.MalcatTools used: Malcat, capa, msitools, cabextract, tshark and ANY.RUN.msitoolsTools used: Malcat, capa, msitools, cabextract, tshark and ANY.RUN.tsharkTools used: Malcat, capa, msitools, cabextract, tshark and ANY.RUN.