
Analysis Finds Signed “Abe Office” RAT Built to Steal Browser Data via Hidden Browsers
Summary
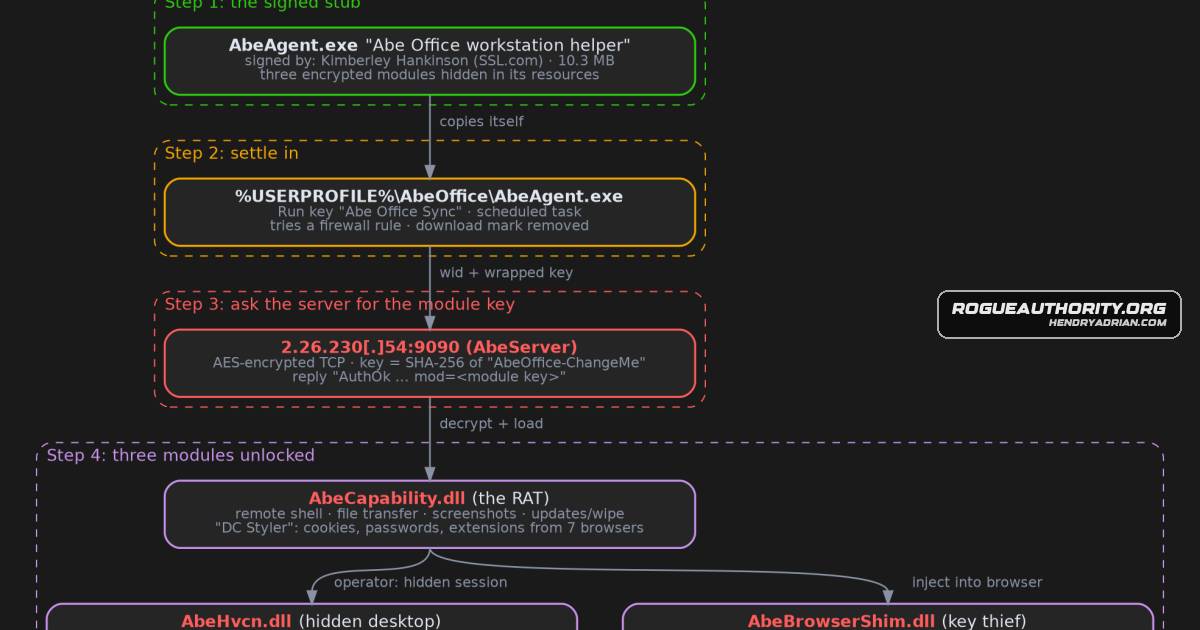
Analysis of AbeAgent.exe found a signed modular RAT that can clone Chrome and Edge profiles for hidden-browser control and steal browser data, including Chrome cookies via an App-Bound Encryption bypass. Operators sent no commands during sandboxing; delivery is unknown.
Key points
- The analysis found that the signed AbeAgent.exe carries three encrypted add-ons; a default password embedded in the file allowed researchers to decrypt the add-ons and captured network traffic.
- AbeHvcn.dll can create an invisible Windows desktop, copy Chrome and Edge profiles, and let an operator control browsers using the victim’s sessions.
- The DC Styler stealer is designed to collect passwords, cookies, and extensions from several browsers; its code also looks for payment-card numbers.
- AbeBrowserShim.dll can ask Chrome’s own elevation service to decrypt its App-Bound Encryption key, enabling the stealer to access protected cookies.
- The malware adds a Run key and scheduled task for persistence. Its attempted Windows Firewall rule failed in the sandbox.
- The server replied and unlocked the add-ons during sandboxing, but researchers observed no operator commands or live data theft; delivery method and operator identity remain unknown.
- The article recommends checking for AbeOffice files and persistence artifacts, monitoring browser launches and browser-data access, and blocking the reported C2 address, 2.26.230[.]54:9090.
Article Details
- Attack Vectors
- AbeAgent.exe installs itself under %USERPROFILE%\AbeOffice\ and establishes persistence with a Run key and scheduled task.
- The RAT contacts its C2 server to obtain a key for decrypting three add-on modules; the article reports that the key can also be derived from the hardcoded default password AbeOffice-ChangeMe.
- The hidden-desktop module copies Chrome and Edge profiles and opens browsers on an invisible Windows desktop for remote interaction with the victim’s logged-in sessions.
- The browser stealer, identified in its messages as DC Styler, is designed to collect passwords, cookies, and extensions from Chrome, Edge, Brave, Opera, and Firefox. It uses a browser helper to obtain Chrome’s App-Bound Encryption key.
- The code supports command execution through cmd.exe and PowerShell, file transfer, screenshots, and uploading browser data. These activities were not observed live during the sandbox run.
- Defensive Notes
- Look for %USERPROFILE%\AbeOffice\, C:\ProgramData\AbeOffice\, the Run value Abe Office Sync, and processes started with --autostart from the installation folder.
- Block or alert on outbound TCP connections to 2.26.230[.]54 on port 9090.
- Monitor for browsers started with --window-position=-32000,-32000 or remote debugging bound to 127.0.0.1, and for non-browser processes reading browser Login Data, Cookies, and Local State files.
- If AbeAgent.exe ran on a system, treat browser sessions as potentially compromised: sign out of sessions and change important passwords from a clean device, enable two-factor authentication, and clean or reinstall the affected PC.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 2[.]26[.]230[.]54 | C2 server on TCP port 9090; it responded and unlocked the add-ons during the sandbox run. |
| SHA256 | 39b0650828531011c1c2ca7657067b6385a53c274c339c89563a111cac88737e | SHA-256 hash of the encrypted AbeBrowserShim.abe1 browser-helper add-on. |
| SHA256 | 3cec97aadc8e0da11e89a4aa454829292599b6b852afa620bb0aa811e9662d71 | SHA-256 hash of AbeHvcn.dll, the hidden-desktop module. |
| SHA256 | 681293cbcf1436de6d8ae4c358a1e76677593155fe393055376aa535809b5ffd | SHA-256 hash of the signed AbeBrowserShim.dll browser helper. |
| SHA256 | 977f5a0124c4484772517336019d8f9a03d27abf9207b64ff225b7b35c7ff277 | SHA-256 hash of AbeCapability.dll, identified as the main RAT module. |
| SHA256 | af5dbf6c5590c3e805a272edec363d0caacc3491570971a84d58a921feb4997f | SHA-256 hash of the encrypted AbeHvcn.abe1 hidden-desktop add-on. |
| SHA256 | b659c968b1e7dab906c9c984faf88ca7390378d41cc4f103be846bc34905cd6e | SHA-256 hash of the encrypted AbeCapability.abe1 RAT add-on. |
| SHA256 | eda3e8e4e87ccb0423886ae5cfd1d488481d4ce16ab5b5efdfbce6f9f1a35dd9 | SHA-256 hash of the AbeAgent.exe malware sample. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe stealer is designed to upload passwords, cookies, and extensions to the server in parts; this was not observed live during the sandbox run.T1053.005 · Scheduled TaskAbeAgent.exe registers a scheduled task that starts it with --autostart.T1055.001 · Dynamic-link Library InjectionAbeHvcn.dll injects AbeBrowserShim.dll into a browser process to request decryption of Chrome’s App-Bound key.T1059.001 · PowerShellThe malware code supports running commands through PowerShell.T1059.003 · Windows Command ShellThe malware code supports running commands through cmd.exe.T1082 · System Information DiscoveryThe malware code can collect basic system information.T1105 · Ingress Tool TransferThe RAT can receive new or updated add-ons from its operator.T1113 · Screen CaptureThe RAT module can take screenshots of the real desktop and the hidden desktop.T1539 · Steal Web Session CookieThe malware copies browser profiles containing cookies and is designed to collect and upload browser cookies.T1547.001 · Registry Run Keys / Startup FolderAbeAgent.exe adds the Abe Office Sync value under the current user’s Run registry key to start at logon.T1553.005 · Mark-of-the-Web BypassOn first run, AbeAgent.exe removes the Mark-of-the-Web tag from its file.T1555.003 · Credentials from Web BrowsersThe stealer is designed to collect saved passwords from browser profiles, including copied Chrome and Edge profiles.
Malware
Products
BraveBrowser stealer ("DC Styler"): passwords, cookies and extensions from Chrome, Edge, Brave, Opera and Firefox, including a tool that gets the browser to decrypt its own App-Bound key.EdgeHidden desktop (hVNC): the victim’s Chrome and Edge profiles are copied to C:\ProgramData\AbeOffice\SystemCache\ and opened on an invisible desktop, so the operator can use the victim’s logged-in sessions without themGoogle Chromea hidden desktop with the victim’s own logged-in browsers, plus a browser stealer built to defeat Chrome’s newest cookie protection, App-Bound Encryption.Microsoft Windowsremoves the "downloaded from the internet" mark (the Mark of the Web, a hidden tag Windows uses to warn you about downloaded files);Mozilla FirefoxBrowser stealer ("DC Styler"): passwords, cookies and extensions from Chrome, Edge, Brave, Opera and Firefox, including a tool that gets the browser to decrypt its own App-Bound key.OperaBrowser stealer ("DC Styler"): passwords, cookies and extensions from Chrome, Edge, Brave, Opera and Firefox, including a tool that gets the browser to decrypt its own App-Bound key.
Tools
ANY.RUNTools used: Malcat, capa, Python, Wireshark, a sandboxed Wine run and ANY.RUN.capaTools used: Malcat, capa, Python, Wireshark, a sandboxed Wine run and ANY.RUN.MalcatTools used: Malcat, capa, Python, Wireshark, a sandboxed Wine run and ANY.RUN.PythonTools used: Malcat, capa, Python, Wireshark, a sandboxed Wine run and ANY.RUN.REMnuxThis analysis and write-up were produced by Claude (Opus 5.5), working as an agent in Claude Code on a REMnux analysis VM.WiresharkTools used: Malcat, capa, Python, Wireshark, a sandboxed Wine run and ANY.RUN.