
CookUp Campaign Linked to Nine Signing Companies and 25 C2 Domains
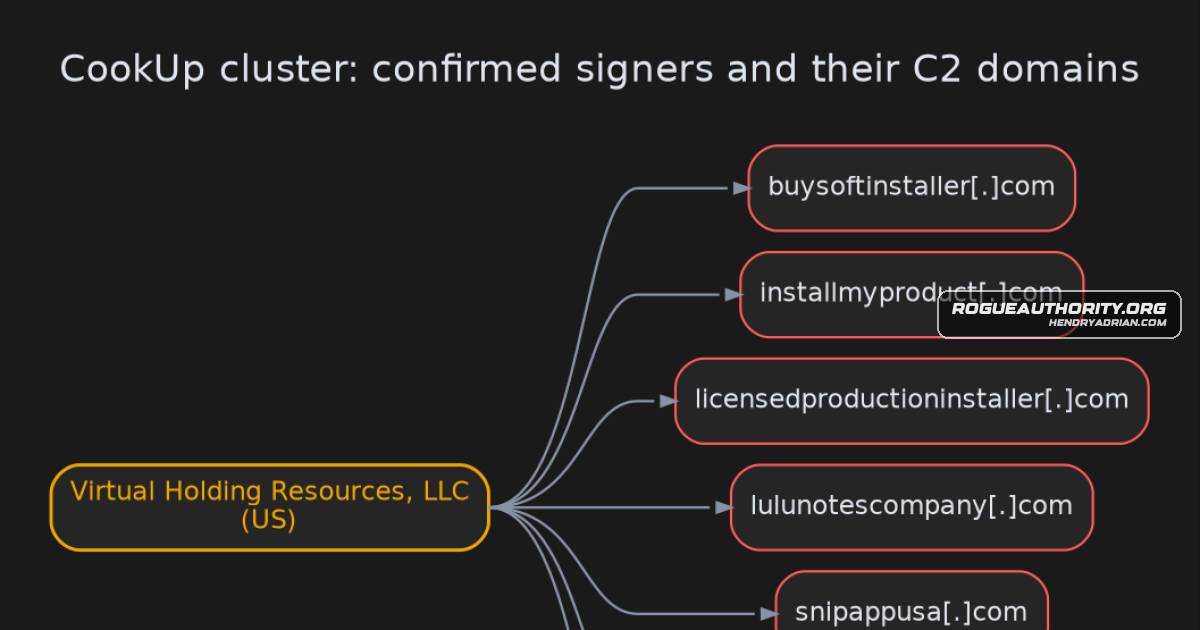
Summary
An investigation links installers from nine EV-certified companies to the CookUp campaign through shared loader code and 25 C2 domains. Researchers could not retrieve the final payload, and recommend blocking the domains and hunting for related files.
Key points
- Installers signed by nine companies share CookUp’s payload-unpacking code and the same 32-byte constant, despite using different installer formats and lures.
- The investigation associates the installers with 25 C2 domains; the article says all are behind Cloudflare.
- The installers use padded signature areas that can make some tools fail to display them as signed.
- The article connects OpenSUpdater samples to the cluster based on shared code and the same unpacking constant.
- Researchers could not retrieve the final payload because the servers did not deliver it to the systems they observed.
- Defenders are advised to block the domains, hunt for files signed by the listed companies, and watch for suspicious recipe, PDF, or note-taking installers.
Article Details
- Attack Vectors
- Trojanized, EV-signed installers were disguised as recipe apps, PDF tools, note-takers, game cheats, and generic download-ready installers.
- The installers carried a loader with shared code that unpacked a hidden DLL; some builds concealed it in a doctored 7z.dll.
- Installers contacted campaign C2 domains, whose servers reportedly selected whether to deliver the final payload per victim. The researchers did not observe a payload being delivered.
- Installers used junk-byte padding in the signature area, which could make tools fail to show them as signed even though Windows accepted the signatures.
- Defensive Notes
- Block the listed C2 domains and alert on hosts that resolve them.
- Hunt for files signed by the nine companies identified in the article, particularly recently downloaded files; the article notes that some clean-looking files may also use a listed certificate.
- Monitor for recently installed recipe, PDF, or note-taking apps under %LOCALAPPDATA%\Programs\ when installed by Document_, PDF_, or CookingApp_-style executables.
- Download software from the vendor's own site. Treat files named like documents but ending in .exe as programs, and do not treat a valid signature as proof that a file is safe.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | applicensingstudio[.]com | Listed as a C2 domain contacted by a CookUp-related installer. |
| DOMAIN | buysoftinstaller[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | codeonicinc[.]com | Reported by G DATA as a C2 domain for related OpenSUpdater samples. |
| DOMAIN | cookingsuiteinstaller[.]com | Listed as a C2 domain contacted by a campaign installer. |
| DOMAIN | foodcooksoftware[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | innodocumentsetup[.]com | Listed as a C2 domain contacted by a campaign installer. |
| DOMAIN | installerpdf[.]com | Listed as a C2 domain contacted by a campaign installer. |
| DOMAIN | installmyproduct[.]com | Listed as a C2 domain contacted by a campaign installer. |
| DOMAIN | licensedproductioninstaller[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | lulunotescompany[.]com | Listed as a C2 domain contacted by a campaign installer. |
| DOMAIN | mypdfsoftware[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | nomadiccookapp[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | nomadiccooknow[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | peregrinecooksoft[.]com | Listed as a C2 domain contacted by a campaign installer. |
| DOMAIN | perfectcookingsuite[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | recipecookingapp[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | recipeinstaller[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | reciperoverapp[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | securedocinstaller[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | setuppdfsoft[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | snipappusa[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | softsetupstudio[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | thesoftwarerepo[.]com | Listed as a C2 domain contacted by a campaign installer. |
| DOMAIN | vegapdf[.]com | Listed as a C2 domain contacted by campaign installers. |
| DOMAIN | webpdfinstallerstudio[.]com | Listed as a C2 domain contacted by campaign installers. |
| SHA256 | 40798b13e16d6a83cf5b828d7eca110b433eaabf8ca5c83511425eb24bbaee4f | SHA-256 of a campaign installer listed as contacting recipecookingapp[.]com. |
| SHA256 | a7666e5aa3c6ecae0295caa7c3f49714eb561d6e1be6807cf1020b79f1902cd0 | SHA-256 of a related installer listed as contacting codeonicinc[.]com. |
| SHA256 | af74f8974df1bff1c938a6f8f585cc8b5f370c98d41e7c5f476a4abda3cbfa2e | SHA-256 of a campaign installer listed as contacting setuppdfsoft[.]com. |
| SHA256 | e7bc65daf98767646cb1a0e8c3d19cf0db0dce4618a9bcd2d287426cfd2c9034 | SHA-256 of a campaign installer listed as contacting applicensingstudio[.]com. |
| SHA256 | ffde5fbba662c27dbdf89236b16c80fcef3e5552d8ff98c052dd69b434fadf15 | SHA-256 of a campaign installer listed as contacting buysoftinstaller[.]com. |
People
Malware
OpenSUpdaterG DATA describes the same “bloated certificate” in its write-up on OpenSUpdater, and the trick also shows up in the Projextor installers G DATA reported, a similar campaign of trojanized Electron productivity apps.TamperedChefSeveral antivirus vendors label these installers as TamperedChef, the name already used publicly for “useful app” installers with a hidden loader.
Vendors
Products
Tools
ANY.RUNTools used: Malcat, innoextract, 7-Zip, VirusTotal, Censys, and public ANY.RUN and Triage reports.CensysTools used: Malcat, innoextract, 7-Zip, VirusTotal, Censys, and public ANY.RUN and Triage reports.innoextractTools used: Malcat, innoextract, 7-Zip, VirusTotal, Censys, and public ANY.RUN and Triage reports.MalcatTools used: Malcat, innoextract, 7-Zip, VirusTotal, Censys, and public ANY.RUN and Triage reports.REMnuxThis analysis and write-up were produced by Claude (Opus 5.5), working as an agent in Claude Code on a REMnux analysis VM.TriageTools used: Malcat, innoextract, 7-Zip, VirusTotal, Censys, and public ANY.RUN and Triage reports.VirusTotalTools used: Malcat, innoextract, 7-Zip, VirusTotal, Censys, and public ANY.RUN and Triage reports.
Countries
UkraineUkraine (Kyiv)United KingdomNine signers, three countries: five US LLCs, three Ukrainian LLCs based in Kyiv, and one UK limited company.United StatesFour of the five US companies are registered in Wyoming or New Mexico, states that publish little about a company’s owners, and for four of the five the address in the certificate is in yet another state.