
CookUp Installer Uses Server-Side Gating to Hide an In-Memory DLL Loader
Summary
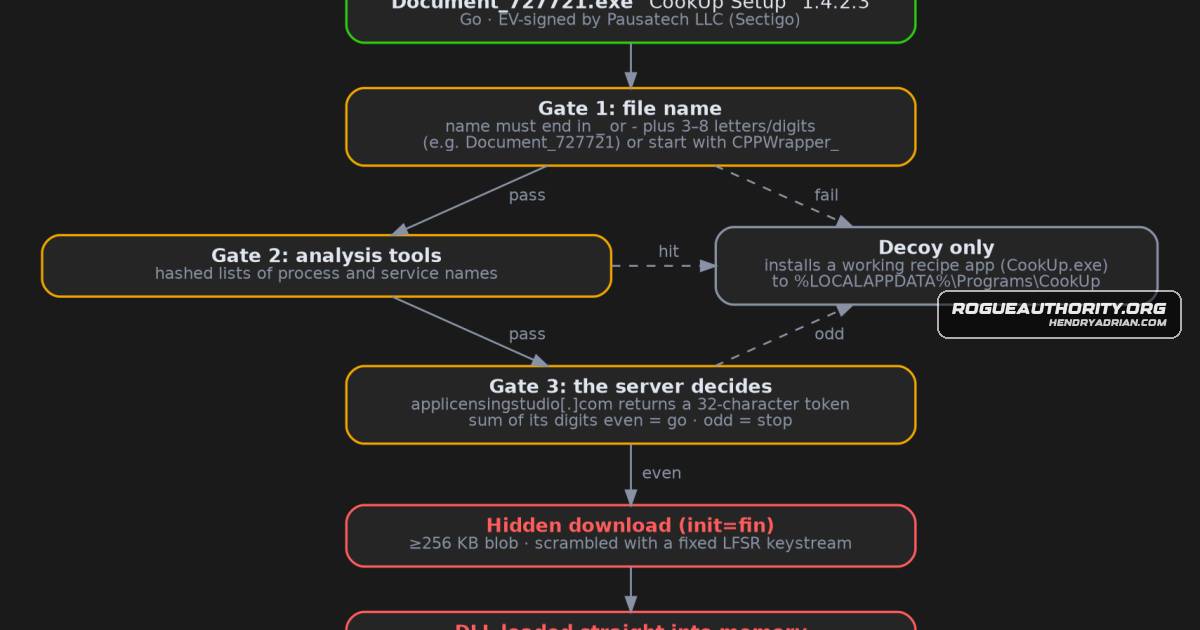
Researchers mapped a signed CookUp installer that installs a harmless recipe app but can use three gates and a server-issued token to fetch and run a DLL in memory. The server refused observed sessions, leaving the final payload unknown.
Key points
- The signed installer sets up a working, harmless CookUp recipe app while containing a separate Go loader.
- The loader checks its filename, scans for analysis tools using hashed process and service names, and uses the digit sum of a server-issued token to decide whether to proceed.
- If permitted, it downloads a scrambled blob, unpacks it with an LFSR-based keystream, and maps a DLL into memory; a relay of three hidden DLLs is described.
- The researchers observed only odd tokens, so the server did not provide the payload and the final DLL's function is unknown. A test blob validated the unpacking format.
- CookUp, GooPDF, and Catchlight share the same scrambler and other implementation details despite being built in different languages; the operators remain unidentified.
- GooPDF analysis found that the installer encodes antivirus information in an ID sent to the server, allowing per-victim delivery decisions.
- The article recommends defenders block applicensingstudio[.]com and monitor for the User-Agent Mozilla/5.0WP and unexpected CookUp installation paths.
Article Details
- Attack Vectors
- A signed installer posing as the CookUp recipe app installs the working decoy app while containing a hidden loader.
- The loader checks its filename and running processes and services against hashed analysis-tool blocklists before proceeding.
- The loader contacts applicensingstudio[.]com for a token and proceeds only when the token’s digit sum is even.
- After a qualifying server response, the loader downloads a scrambled blob, unpacks DLLs, and maps them into memory without writing them to disk.
- Defensive Notes
- Block applicensingstudio[.]com and alert on the HTTP User-Agent Mozilla/5.0WP.
- Hunt for Go binaries signed by Pausatech LLC and for the string cookup/installer/internal/memload.
- Monitor for %LOCALAPPDATA%\Programs\CookUp\CookUp.exe appearing after an unexpected setup executable runs.
- Treat an EV signature as insufficient evidence that an installer is safe; verify that the signer matches the expected product.
- If the installer was run, the article advises assuming the hidden component may have executed, disconnecting, running a full scan, and considering a reinstall.
- An init=fin response can be unpacked offline using the format described in the article.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | applicensingstudio[.]com | Server-side check-in and payload-delivery domain used by the loader; the article recommends blocking it. |
| SHA256 | e7bc65daf98767646cb1a0e8c3d19cf0db0dce4618a9bcd2d287426cfd2c9034 | SHA-256 hash of the CookUp installer containing the gated loader. |
| URL | hxxps[:]//applicensingstudio[.]com/?ver=3b0d&chan=618&lang=3b1&arch=1b1&build=f9b&init=prep | Additional specific loader check-in URL used to request the server-side prep token. |
| URL | hxxps[:]//applicensingstudio[.]com/?ver=9de1&chan=2d6&lang=f24&arch=23a&build=301&init=prep | Specific loader check-in URL used to request the server-side prep token. |
MITRE ATT&CK
T1007 · System Service DiscoveryThe loader enumerates services and checks them against a hashed analysis-tool blocklist.T1027 · Obfuscated Files or InformationThe Go loader is heavily obfuscated, with encrypted strings and scrambled function names.T1057 · Process DiscoveryThe loader enumerates running processes and compares their hashes against a blocklist of analysis tools.T1071.001 · Web ProtocolsThe loader uses HTTP requests to check in with applicensingstudio[.]com and request its token and payload.T1105 · Ingress Tool TransferAfter receiving an even-token response, the installer fetches a scrambled blob containing the hidden DLL payload.T1518.001 · Security Software DiscoveryThe GooPDF variant checks which antivirus is running and encodes the result in its server-bound ID.T1620 · Reflective Code LoadingThe installer uses a home-made loader to map the downloaded DLL into its own memory without writing it to disk.
People
Vendors
Products
CatchlightWindow, LLC; PDF tools (GooPDF, MyPdfSoftware, Paperly, Velum) signed by Net Sourcing Experts LLC; and Catchlight and Zippex signed by Virtual Holding Resources, LLC.CookUpDocument_727721.exe presents itself as the setup program for "CookUp", a little app that suggests recipes from the ingredients you have.DiskWiseThe same Pausatech certificate also signed an earlier installer, for a disk-cleaning app called "DiskWise", which first turned up about two months before CookUp.GooPDFmore recipe apps (Pantry, RecipeRover, NomadicCookNow, Foodzi) signed by Launch Window, LLC; PDF tools (GooPDF, MyPdfSoftware, Paperly, Velum) signed by Net Sourcing Experts LLC; and Catchlight and Zippex signed by
Tools
ANY.RUNTools used: Malcat, capa, KesaKode, unicorn, capstone, ILSpy, Wine (sandboxed), ANY.RUN and tshark.capaTools used: Malcat, capa, KesaKode, unicorn, capstone, ILSpy, Wine (sandboxed), ANY.RUN and tshark.CapstoneTools used: Malcat, capa, KesaKode, unicorn, capstone, ILSpy, Wine (sandboxed), ANY.RUN and tshark.ILSpyTools used: Malcat, capa, KesaKode, unicorn, capstone, ILSpy, Wine (sandboxed), ANY.RUN and tshark.KesaKodeTools used: Malcat, capa, KesaKode, unicorn, capstone, ILSpy, Wine (sandboxed), ANY.RUN and tshark.MalcatTools used: Malcat, capa, KesaKode, unicorn, capstone, ILSpy, Wine (sandboxed), ANY.RUN and tshark.tsharkTools used: Malcat, capa, KesaKode, unicorn, capstone, ILSpy, Wine (sandboxed), ANY.RUN and tshark.unicornTools used: Malcat, capa, KesaKode, unicorn, capstone, ILSpy, Wine (sandboxed), ANY.RUN and tshark.WineTools used: Malcat, capa, KesaKode, unicorn, capstone, ILSpy, Wine (sandboxed), ANY.RUN and tshark.