
Analysis Finds Fake Zscaler Tunnel Is a Go Backdoor Signed With an Unrelated EV Certificate
Summary
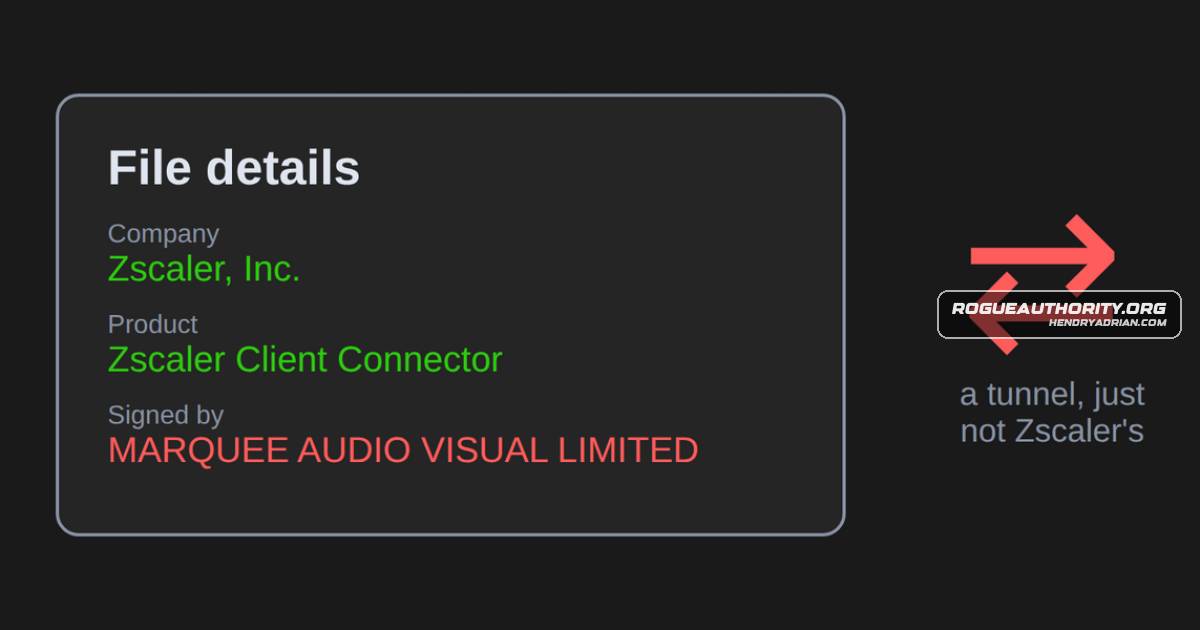
Analysis of ZSATunnel_x86.exe found a Go backdoor disguised as Zscaler Client Connector and signed with an unrelated valid EV certificate. It supports command execution, file transfer and SOCKS5 pivoting; its server address comes from URSPLUNK.
Key points
- The sample uses Zscaler product names and version information but is signed with a valid EV certificate issued to MARQUEE AUDIO VISUAL LIMITED.
- The backdoor obtains its server address from the URSPLUNK environment variable; the analyzed copy did not contact a real server during testing.
- It moves itself to a Zscaler-looking per-user folder and periodically checks in using the path /v2/alive.
- Its tasks include running commands through cmd or PowerShell, transferring files, and opening a SOCKS5 tunnel through the infected computer.
- The analysis describes code-level behavior, but the researchers did not establish how the sample was delivered or what sets URSPLUNK on a victim’s system.
- Defenders are advised to check for the sample’s install path, URSPLUNK, related proxy requests, leftover temporary files, and the signer.
Article Details
- Attack Vectors
- The backdoor masquerades as Zscaler Client Connector using Zscaler names, version information, and a ZSATunnel-looking install path; it is signed with a valid EV certificate issued to an unrelated company.
- The server address is supplied through the URSPLUNK environment variable; the analyzed sample otherwise defaults to https://localhost. The article says the component that sets the variable and the delivery method are unknown.
- According to code analysis, the backdoor checks in at /v2/alive, accepts remote tasks, and can execute commands through cmd or PowerShell.
- The backdoor can download files from its server and upload files or folders from the infected PC as chunked .tar.gz archives.
- A SOCKS5 task can route attacker connections through the infected PC to other systems it can reach.
- Defensive Notes
- Check for ZSATunnel_x86.exe under %LOCALAPPDATA%\Programs\ZSATunnel\ and investigate random .tmp files left in the same folder.
- Check user and system settings, and running-process environments, for the URSPLUNK variable.
- Hunt proxy logs for /v2/alive, /v2/hook, /v2/submit, /v2/export, and /v2/relay requests with user agent axios/1.7.2; the article also identifies Accept-Language: en-NZ,en;q=0.9 and a _session cookie as clues.
- Block or alert on the signer MARQUEE AUDIO VISUAL LIMITED and the certificate associated with the sample.
- Advise users to verify with company IT before running a Zscaler file received through email, chat, or a download link.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| MD5 | 1576a17f54c5b149139e6c8f1b2e6b20 | MD5 hash of the analyzed ZSATunnel_x86.exe backdoor. |
| SHA1 | eae2226416cdd4b72b68d1408e8a8a1ba1e28819 | SHA-1 hash of the analyzed ZSATunnel_x86.exe backdoor. |
| SHA256 | fe9829f1c102a79b4ca33c8c8bda8ef2236dc94c6d1de88249c89e82681adc8c | SHA-256 hash of the analyzed ZSATunnel_x86.exe backdoor. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe code replaces internal function names with random social-media words and pads startup code with meaningless arithmetic.T1036.005 · Match Legitimate Resource Name or LocationThe backdoor uses Zscaler product names and version information and moves itself to a Zscaler-looking per-user install path to appear legitimate.T1041 · Exfiltration Over C2 ChannelA download task uploads files, folders, or wildcard matches from the infected PC to the server, packaged as .tar.gz and sent in chunks.T1059.001 · PowerShellThe article says the backdoor can execute server-issued commands through PowerShell.T1059.003 · Windows Command ShellThe article says the backdoor can execute server-issued commands through cmd /C.T1071.001 · Web ProtocolsThe code is described as checking in with its server at /v2/alive using browser-like HTTP headers and the axios/1.7.2 user agent; the article says this network behavior was not observed in the sandbox.T1090.001 · Internal ProxyA SOCKS5 task lets the attacker route connections to reachable internal systems through the infected PC.T1105 · Ingress Tool TransferA push task downloads a file from the server and saves it on the infected PC.T1553.002 · Code SigningThe backdoor is signed with a valid EV certificate issued to MARQUEE AUDIO VISUAL LIMITED, an unrelated company, while its file details claim Zscaler.
Products
Tools
ANY.RUNTools used: Malcat, Go toolchain (go version -m, go tool nm), capstone, osslsigncode, a sandboxed Wine setup and ANY.RUN.CapstoneTools used: Malcat, Go toolchain (go version -m, go tool nm), capstone, osslsigncode, a sandboxed Wine setup and ANY.RUN.MalcatTools used: Malcat, Go toolchain (go version -m, go tool nm), capstone, osslsigncode, a sandboxed Wine setup and ANY.RUN.osslsigncodeTools used: Malcat, Go toolchain (go version -m, go tool nm), capstone, osslsigncode, a sandboxed Wine setup and ANY.RUN.