
Technical Analysis Links Three-Stage IEProc Chain and Golden Gh0st RAT to APT-Q-27
Summary
Technical analysis traces a signed, three-stage IEProc chain to Golden Gh0st RAT, linking it to APT-Q-27 through a reused plugin and C2 key. The backdoor contacted app[.]probref[.]com, but received no commands in testing.
Key points
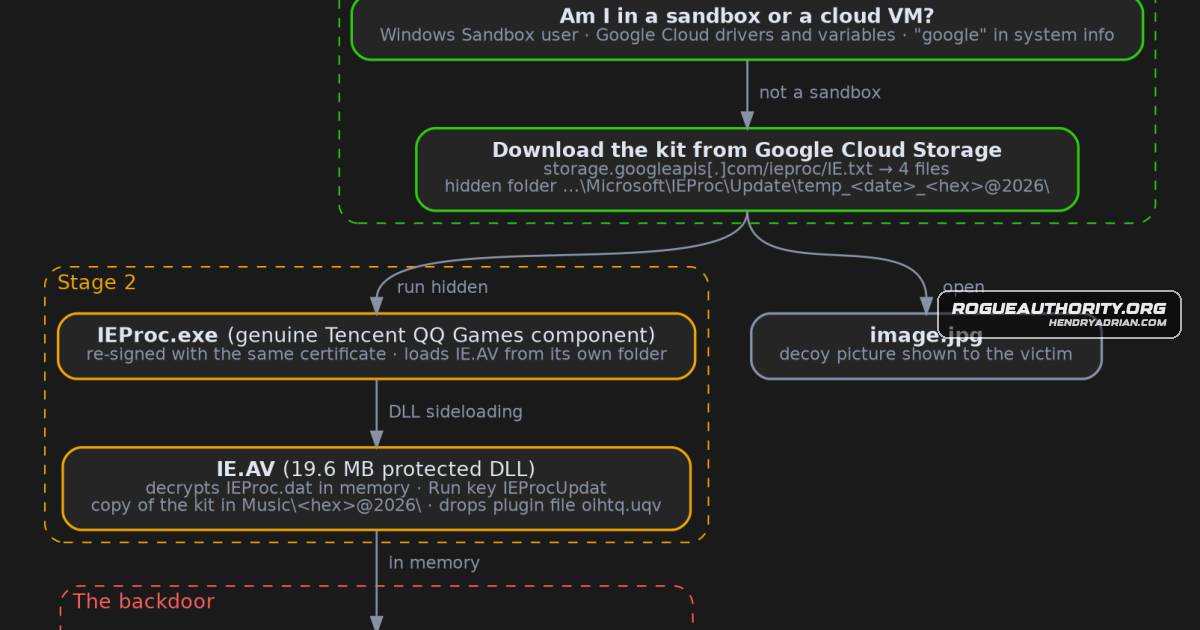
- A signed .NET IEProc.exe downloader retrieves an attack kit from storage.googleapis[.]com; a genuine Tencent QQ Games component then sideloads the protected IE.AV loader.
- IE.AV decrypts the Golden Gh0st RAT core in memory, establishes Run-key persistence, and copies the kit to a user-profile folder.
- The chain checks for Windows Sandbox and Google Cloud indicators, and stage two only fully runs from the expected folder.
- The analysis links the sample to APT-Q-27 using a byte-identical plugin, a C2 key matching earlier waves, a legacy C2 string, and a reused decoy.
- Golden Gh0st RAT supports screen capture, keylogging, remote shell, file management, and proxy functions. In testing, app[.]probref[.]com:5188 returned a keepalive but sent no commands.
- A recovered email from the same campaign used a fake screenshot lure aimed at a support desk; the authors did not identify the delivery email for this sample or visit the earlier email’s link.
- Suggested defenses include blocking executable attachments disguised as images and monitoring for the reported folders, Run key, and C2 indicators.
Article Details
- Attack Vectors
- A phishing email to a company support desk used a linked, blurry screenshot as a lure; the image link was hosted at myphotos.s[.]gy.
- The executable downloader was disguised as an image with a .scr filename.
- Stage 1 downloaded the kit from Google Cloud Storage.
- A genuine Tencent QQ Games component loaded a malicious helper DLL placed beside it (DLL sideloading).
- The loader checked its execution folder and sandbox or Google Cloud indicators before fully running.
- Defensive Notes
- Block or quarantine executable attachments disguised as images, including .scr, .com, and .pif files, in email and support-ticket portals.
- Block or alert on app.probref[.]com and 13.231.249[.]106, and monitor for WebSocket handshakes using the path GET /\.
- Monitor for downloads from storage.googleapis[.]com/ieproc/ and small signed programs fetching .txt file lists from new storage buckets.
- Hunt for \Microsoft\IEProc\Update\temp_*@2026\ and \Music\*@2026\ folders, and the IEProcUpdat Run value.
- Use sandboxes with realistic file paths and non-cloud fingerprints to reduce evasion caused by folder checks and Google Cloud environment checks.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | app[.]probref[.]com | C2 domain contacted by Golden Gh0st RAT in the reported sandbox run. |
| DOMAIN | e[.]nkking[.]com | Legacy C2 server name embedded in the core from a 2025 sample; the article says it was not contacted in this wave. |
| IPV4 | 13[.]231[.]249[.]106 | C2 IP address that accepted the backdoor's registration in the reported sandbox run. |
| SHA256 | 21498faad7283839d0b055c618693eb2affe910b6e8d030592d92a94cd266144 | Hash of the stage 1 IEProc.exe downloader, also seen as Image202610305689.scr. |
| SHA256 | 42e6b4e4ff08b80e45e5e8991c53fadce950541506bab1141153da5a4c960ea4 | Hash of IEProc.dat, the encrypted container holding the backdoor core. |
| SHA256 | 7d6ab192aec5f0afea841f97951bf6dad746c766b989eb59efffa529c713e010 | Hash of the Golden Gh0st RAT core carved from memory. |
| SHA256 | 813c4a2aab04fbb1f56ae5c0b4cb73188de57ffb3dc58b6019f631560de4ad33 | Hash of plugin32.dll, a decrypted plugin reported as byte-for-byte identical to one used in earlier waves. |
| SHA256 | 88ea8bda73c76d5e247e88abb1fa69ec374ac9ae35ace16f2036db5608c05f75 | Hash of the stage 2 IEProc.exe, the re-signed Tencent host used for DLL sideloading. |
| SHA256 | b30886bf461f3d27c7d83bf1678c1fc4fe9ca1b709caf26b624d14f7f8b2ec61 | Hash of oihtq.uqv, the encrypted plugin file. |
| SHA256 | e4ce31ca2ba1c1052b5583656137a59432aa0bb2d150431615210525f4ae47e4 | Hash of IE.AV, the sideloaded loader DLL. |
| URL | hxxps[:]//myphotos[.]s[.]gy/photo20260729.png | Linked screenshot URL in the campaign's phishing email; the article says it was not visited. |
| URL | hxxps[:]//storage[.]googleapis[.]com/ieproc/IE.txt | Specific cloud-hosted URL used by stage 1 to fetch the kit's file list. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe downloader is protected by code virtualization, and the backdoor core and plugin are stored encrypted.T1056.001 · KeyloggingThe plugin provides keylogging capability.T1059 · Command and Scripting InterpreterThe plugin provides a remote shell.T1071.001 · Web ProtocolsThe backdoor communicates with its C2 over WebSocket.T1082 · System Information DiscoveryThe backdoor fingerprints the machine, including its Windows version, disks, memory, CPU, and drives.T1090 · ProxyThe plugin provides a SOCKS proxy that can route attacker traffic through the compromised PC.T1105 · Ingress Tool TransferStage 1 downloads the kit files from Google Cloud Storage.T1113 · Screen CaptureThe plugin provides screen-capture capability.T1204.002 · Malicious FileThe campaign used an image-like .scr executable that runs when opened.T1497.001 · System ChecksStage 1 exits when it detects Windows Sandbox or Google Cloud environment indicators.T1547.001 · Registry Run Keys / Startup FolderIE.AV adds the IEProcUpdat value under the current user's Windows Run key for logon persistence.T1566.002 · Spearphishing LinkThe article describes a phishing email to a support desk with a link to a screenshot hosted outside the email.T1574.002 · DLL Side-LoadingThe genuine Tencent QQ Games component loads the malicious IE.AV DLL placed in its folder.
Threat Actors
APT-Q-27The article links the samples to APT-Q-27 based on matching plugin and C2-key evidence, and says Qi’anxin tracks GoldenEyeDog by this name.CylindricalCanineExpel attributes Golden Gh0st RAT to CylindricalCanine, described as a subgroup of GoldenEyeDog.GoldenEyeDogThe article describes GoldenEyeDog as a Chinese cybercrime group and says CylindricalCanine is its subgroup; Expel attributes Golden Gh0st RAT to that subgroup.
Malware
Products
Google Cloud StorageIEProc.exe is a small signed .NET program that downloads the rest of an attack kit from Google Cloud Storage.Microsoft WindowsSandbox-shy: it checks for Windows Sandbox and Google Cloud machines.QQ GamesThe second IEProc.exe is a genuine Tencent "QQ Games" Internet Explorer component, re-signed with the same Hangzhou Yueque Li certificate.
Tools
ANY.RUNTools used: malcat, de4dotEx, ILSpy, dnlib, capa, Wine, gdb, ANY.RUN and Triage.capaTools used: malcat, de4dotEx, ILSpy, dnlib, capa, Wine, gdb, ANY.RUN and Triage.de4dotExTools used: malcat, de4dotEx, ILSpy, dnlib, capa, Wine, gdb, ANY.RUN and Triage.dnlibTools used: malcat, de4dotEx, ILSpy, dnlib, capa, Wine, gdb, ANY.RUN and Triage.gdbTools used: malcat, de4dotEx, ILSpy, dnlib, capa, Wine, gdb, ANY.RUN and Triage.ILSpyTools used: malcat, de4dotEx, ILSpy, dnlib, capa, Wine, gdb, ANY.RUN and Triage.MalcatTools used: malcat, de4dotEx, ILSpy, dnlib, capa, Wine, gdb, ANY.RUN and Triage.REMnuxThis analysis and write-up were produced by Claude (Opus 5.5), working as an agent in Claude Code on a REMnux analysis VM.TriageTools used: malcat, de4dotEx, ILSpy, dnlib, capa, Wine, gdb, ANY.RUN and Triage.WineTools used: malcat, de4dotEx, ILSpy, dnlib, capa, Wine, gdb, ANY.RUN and Triage.