
Talos Links UAT-9244 to South American Telecom Espionage Campaign
Summary
Cisco Talos attributes a campaign targeting South American telecom providers since at least 2024 with high confidence to UAT-9244, describing TernDoor, PeerTime and BruteEntry and their roles in persistence, C2 and lateral movement.
Key points
- Cisco Talos attributes the campaign with high confidence to China-nexus APT UAT-9244 and says it has targeted South American telecommunications providers since at least 2024.
- Talos says UAT-9244 may be associated with Famous Sparrow based on shared targeting patterns and tool preferences.
- TernDoor is a Windows backdoor deployed through DLL side-loading; its loader decrypts the final payload in memory.
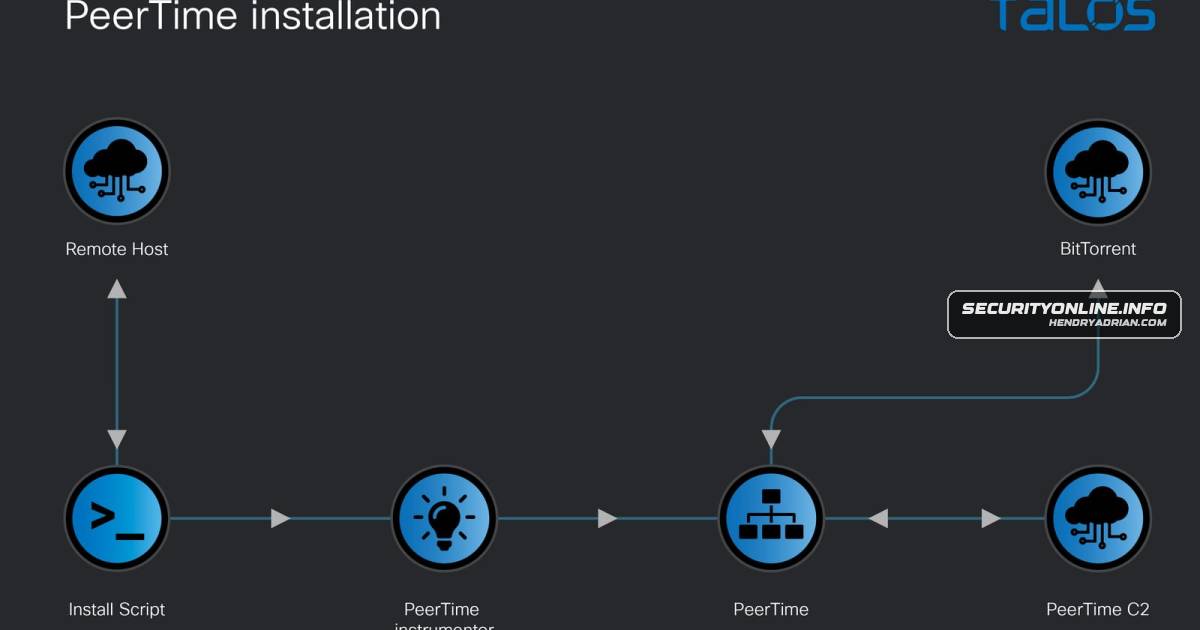
- PeerTime is an ELF backdoor that uses BitTorrent traffic for command and control.
- BruteEntry turns compromised edge devices into proxy nodes for brute-force attempts against SSH, Postgres and Tomcat services.
- Credentials obtained through successful logins can be sent to the C2 server to support lateral movement, according to the article.
Article Details
- Attack Vectors
- TernDoor is deployed through DLL side-loading and decrypts its final payload in memory.
- PeerTime uses the BitTorrent protocol for command-and-control traffic.
- BruteEntry on compromised edge devices brute-forces SSH, Postgres, and Tomcat services.
- BruteEntry uses compromised edge devices as proxy nodes for mass scanning; credentials from successful logins are sent to the C2 server and used for lateral movement.
MITRE ATT&CK
T1021.004 · SSHThe article reports brute-force attempts against SSH and says harvested credentials enable lateral movement into provider networks.T1046 · Network Service DiscoveryBruteEntry conducts mass scanning of SSH, Postgres, and Tomcat servers from compromised edge devices.T1078 · Valid AccountsThe operators use credentials obtained from successful BruteEntry logins to move deeper into victim networks.T1090 · ProxyBruteEntry turns compromised edge devices into proxy nodes used for scanning.T1110.001 · Password GuessingBruteEntry systematically brute-forces SSH, Postgres, and Tomcat services.T1140 · Deobfuscate/Decode Files or InformationThe TernDoor loader decrypts the final payload in memory.T1574.002 · DLL Side-LoadingTernDoor is deployed through DLL side-loading, using a benign file to load a malicious loader.
Threat Actors
Famous SparrowThe article says UAT-9244 is believed to be closely associated with Famous Sparrow, citing similar targeting patterns and preferences; it does not state that Famous Sparrow was confirmed to conduct this campaign.FamousSparrowCisco Talos attributes the South American telecommunications espionage campaign to UAT-9244 with high confidence; the campaign has been active since at least 2024.
Malware
BruteEntryThe group uses a trio of implants—TernDoor, PeerTime, and BruteEntry—employing DLL side-loading, BitTorrent-based C2, and edge-device brute-forcing to maintain persistent access and move laterally.CrowDoorTernDoor: This Windows-based backdoor is a new variation of the previously disclosed CrowDoor malware.PeerTimeThe group uses a trio of implants—TernDoor, PeerTime, and BruteEntry—employing DLL side-loading, BitTorrent-based C2, and edge-device brute-forcing to maintain persistent access and move laterally.TernDoorThe group uses a trio of implants—TernDoor, PeerTime, and BruteEntry—employing DLL side-loading, BitTorrent-based C2, and edge-device brute-forcing to maintain persistent access and move laterally.