
Pwn Request Exploits kubernetes-el Workflow to Steal Secrets and Inject Destructive Code
Summary
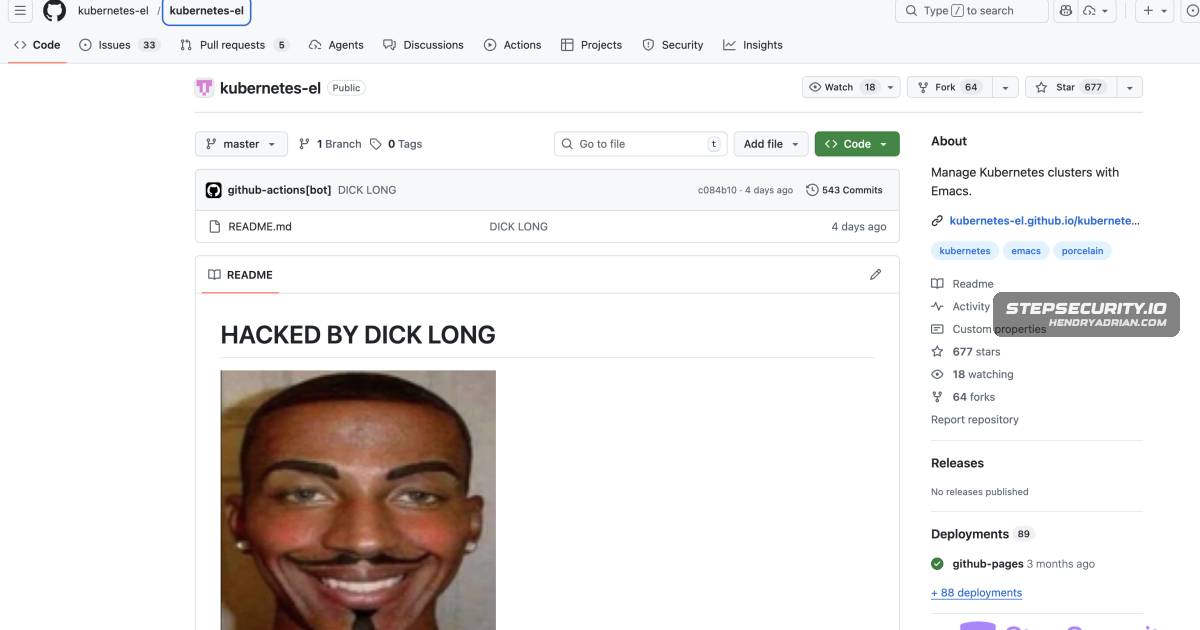
A Pwn Request in kubernetes-el’s GitHub Actions workflow let an attacker use pull_request_target with fork code to exfiltrate runner secrets and push destructive commits. The package was removed from MELPA and blocked on Emacsmirror.
Key points
- A fork-based PR (#382) triggered the repository’s CI workflow; the account quicktrinny was created the day before the attack.
- The workflow combined pull_request_target with a checkout of the attacker’s PR code, then ran make build with a write-capable GITHUB_TOKEN and access to secrets.
- The payload used the Cacheract memory-dump tool and sent extracted secrets to webhook.site; workflow logs showed successful uploads.
- Using the stolen token, the attacker pushed commits that defaced the repository, replaced kubernetes.el with a destructive command, and deleted most repository files.
- The article warns that installing or updating the package after the malicious commit could have run the destructive command; it does not report that users did so.
- The Emacsmirror maintainer reported the compromise on March 7, 2026; the package was removed from MELPA and blocked from updates on Emacsmirror.
- Recommended defenses include not checking out untrusted PR code in privileged workflows, restricting GITHUB_TOKEN permissions, and monitoring CI runner egress.
Article Details
- Attack Vectors
- A pull_request_target workflow checked out the pull request's untrusted fork code and ran make build with write-enabled repository credentials and secrets.
- The attacker modified the Makefile to execute a shell payload that dumped runner memory and extracted the GITHUB_TOKEN and other secrets.
- The payload uploaded extracted secrets to two webhook.site endpoints. The stolen token was then used to push defacement and destructive changes to the repository.
- Defensive Notes
- Do not check out or execute untrusted pull-request code in a pull_request_target workflow. Use a pull_request workflow with read-only permissions for builds and tests, separating privileged operations into a workflow_run workflow when needed.
- Grant GITHUB_TOKEN only the minimum permissions required; the article recommends read-only contents access for CI/test workflows.
- Monitor and restrict network egress from CI runners. The article identifies StepSecurity Harden-Runner as a tool that can detect and block unexpected outbound connections.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
jump-kept-freckles@duck[.]com | Email identified by the article as belonging to the attacker account. | |
| URL | hxxps[:]//webhook[.]site/18c6f9e6-1dce-4b6a-975a-4f0fe0114f65 | Specific webhook.site endpoint used in the initial payload to exfiltrate the stolen GITHUB_TOKEN. |
| URL | hxxps[:]//webhook[.]site/2a7334c9-64a7-48cf-8b22-409028d50d9d | Specific webhook.site endpoint used by the final payload to upload secrets extracted from runner memory. |
MITRE ATT&CK
T1059.004 · Unix ShellThe attacker modified the Makefile to run a Bash payload that dumped runner memory and extracted secrets.T1078.004 · Cloud AccountsThe attacker used the stolen GITHUB_TOKEN, associated with github-actions[bot], to push commits to the repository.T1195.002 · Compromise Software Supply ChainThe attacker compromised the kubernetes-el repository and injected destructive code into the package's main file.T1567.004 · Exfiltration Over WebhookThe payload uploaded stolen token and runner secrets to specific webhook.site endpoints.
People
Products
Emacsa classic "Pwn Request" vulnerability in the CI workflow of kubernetes-el/kubernetes-el, a popular Emacs package for managing Kubernetes clusters. The attacker stole the repository's GITHUB_TOKEN (with fullEmacsmirrorThe package has since been removed from MELPA (a popular third-party Emacs package repository) and blocked from updating on the Emacsmirror, affecting users who depend on it for Kubernetes management within Emacs.GitHub Actionscheckout of the attacker's fork code. This gave the attacker arbitrary code execution inside a GitHub Actions runner with full write permissions to the target repository.kubernetes-elOn March 5, 2026, a threat actor exploited a classic "Pwn Request" vulnerability in the CI workflow of kubernetes-el/kubernetes-el, a popular Emacs package for managing Kubernetes clusters. The attacker stole theMELPAThe package has since been removed from MELPA (a popular third-party Emacs package repository) and blocked from updating on the Emacsmirror, affecting users who depend on it for Kubernetes management within Emacs.