
BeatBanker Android Malware Uses Fake Starlink App to Deliver BTMOB RAT
Summary
Kaspersky reports BeatBanker campaigns targeting users in Brazil with a fake Starlink app. The malware uses stealth and persistence techniques, mines Monero, and its latest version deploys BTMOB RAT for remote device access.
Key points
- Kaspersky found BeatBanker campaigns targeting users in Brazil; fake Google Play Store sites use a Starlink-themed app to lure users into sideloading an APK.
- The APK decrypts and loads hidden DEX code in memory, checks for analysis environments, and delays malicious activity.
- The latest version deploys BTMOB RAT instead of the banking module, enabling capabilities including keylogging, screen and camera access, GPS tracking, and credential capture.
- BeatBanker uses a modified ARM build of XMRig to mine Monero and can start or stop mining based on device conditions.
- Firebase Cloud Messaging telemetry reports device battery, temperature, charging, and usage status to help adjust mining activity.
- A nearly inaudible five-second MP3 loop keeps a foreground service active to help prevent the malware from being suspended.
Article Details
- Attack Vectors
- BeatBanker is distributed as an APK on websites impersonating the Google Play Store and posing as a Starlink app, prompting users to sideload it.
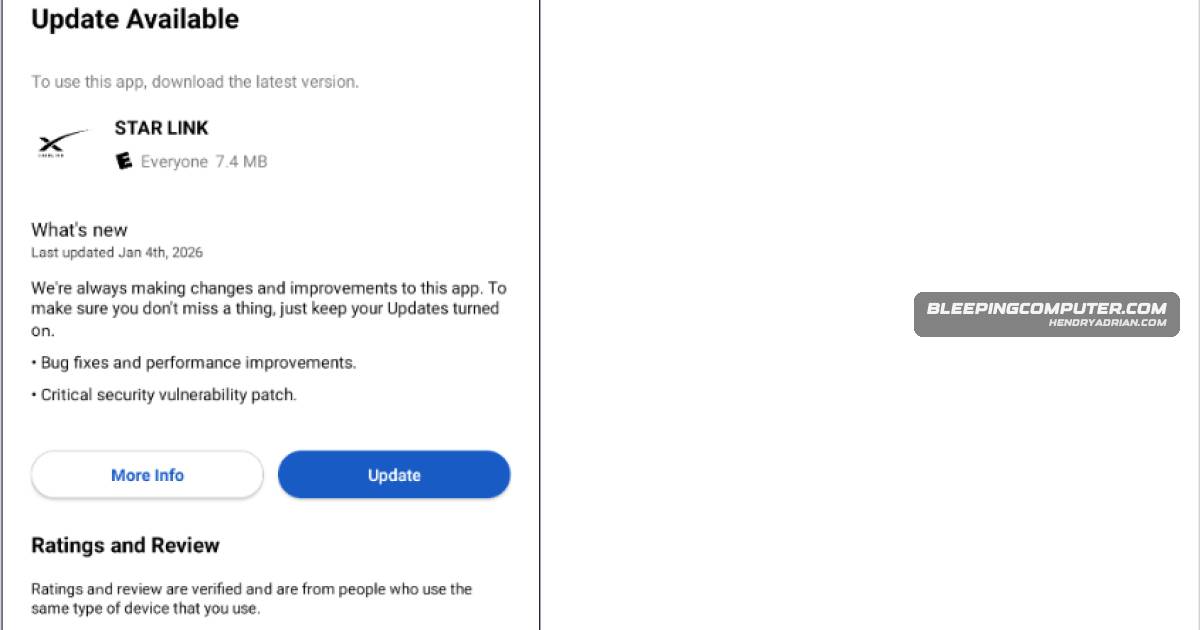
- A fake Play Store update screen tricks victims into granting permissions to install additional payloads.
- The latest reported version deploys BTMOB RAT, which enables remote device control, keylogging, screen recording, camera access, GPS tracking, and credential capture.
- BeatBanker mines Monero using a modified XMRig miner and adjusts mining activity according to device conditions.
- The malware uses Firebase Cloud Messaging to send device status information to its command-and-control server.
- Defensive Notes
- Avoid sideloading APKs from outside the official Google Play Store unless the publisher or distributor is trusted.
- Review granted permissions and be cautious of risky permissions unrelated to an app’s functionality.
- Perform regular Play Protect scans.
MITRE ATT&CK
T1417.001BTMOB RAT provides operators with keylogging capabilities on infected devices.T1430BTMOB RAT can track device location using GPS.T1476BeatBanker is delivered as a sideloaded APK from websites impersonating the Google Play Store.T1496 · Resource HijackingBeatBanker uses a modified XMRig miner to mine Monero on infected Android devices.T1512BTMOB RAT provides camera access.T1513BTMOB RAT can record the device screen.
Malware
BeatBankerBeatBanker is a new Android malware discovered by Kaspersky that poses as a Starlink app on fake Google Play Store sites to trick users into sideloading an APK that combines banking trojan functions, Monero mining, andBTMOBinto sideloading an APK that combines banking trojan functions, Monero mining, and now deploys the BTMOB RAT.
Products
AndroidBeatBanker is a new Android malware discovered by Kaspersky that poses as a Starlink app on fake Google Play Store sites to trick users into sideloading an APK that combines banking trojan functions, Monero mining, andGoogle Play StoreBeatBanker is a new Android malware discovered by Kaspersky that poses as a Starlink app on fake Google Play Store sites to trick users into sideloading an APK that combines banking trojan functions, Monero mining, andStarlinkBeatBanker is a new Android malware discovered by Kaspersky that poses as a Starlink app on fake Google Play Store sites to trick users into sideloading an APK that combines banking trojan functions, Monero mining, and