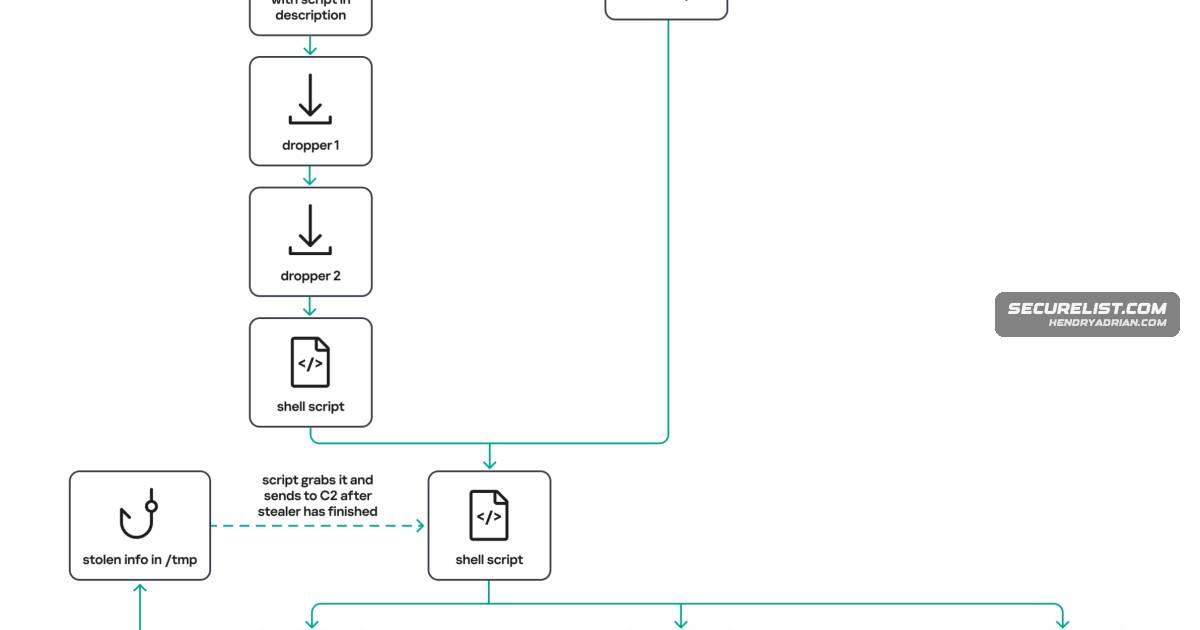
New MacSync macOS Stealer Uses Binary Loaders to Target Crypto Users and Developers
Kaspersky analyzed a new MacSync infection chain using malicious DMG apps, binary droppers and iCloud-hosted content to install a macOS infostealer and backdoor targeting crypto users and developers.