
BeatBanker Android Trojan Combines Monero Mining With Banking Theft and BTMOB RAT
Summary
Kaspersky details BeatBanker, an Android campaign targeting Brazil that uses fake app stores to deliver a Monero miner and a banking module that redirects USDT transactions; newer samples deploy the BTMOB RAT instead.
Key points
- The campaign uses phishing pages posing as Google Play to distribute malicious apps, including a fake INSS Reembolso app; samples were detected on victims in Brazil.
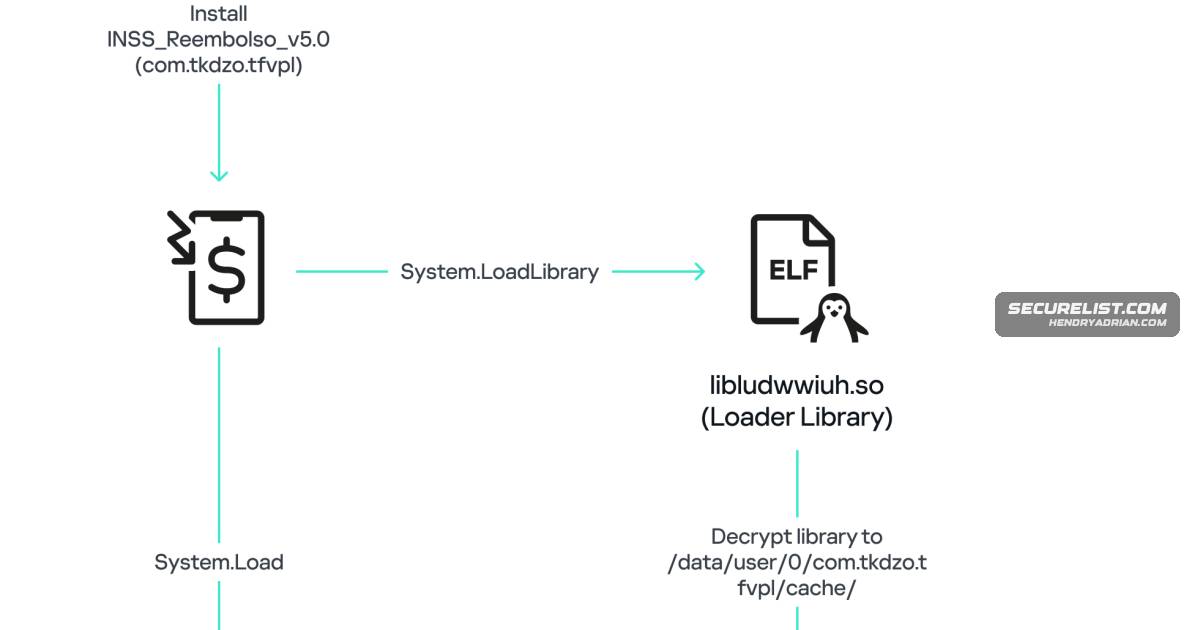
- A packed APK uses a native library and an in-memory DEX loader, with obfuscation and anti-analysis checks to hinder detection and investigation.
- BeatBanker downloads and decrypts an XMRig Monero miner and uses Firebase Cloud Messaging to receive commands and monitor device conditions.
- A looping, nearly inaudible audio file and a pinned notification help keep the malware’s foreground service running.
- The banking module abuses Android Accessibility and overlays to replace USDT withdrawal destinations in Binance and Trust Wallet.
- Newer samples distributed as a fraudulent StarLink app deploy BTMOB RAT instead of the banking module; BTMOB supports remote control, screen capture, and keylogging.
- Some BTMOB-distributing samples appear to spread through WhatsApp as well as phishing pages.
Article Details
- Attack Vectors
- A counterfeit Google Play Store site, cupomgratisfood[.]shop, distributes malicious APKs disguised as apps such as INSS Reembolso.
- The initial APK downloads additional payloads by imitating an application update; newer samples were also reported to spread through WhatsApp and phishing pages.
- The malware uses Accessibility permissions and overlays to replace USDT transaction destinations in Binance and Trust Wallet.
- Recent samples replace the banking module with the BTMOB remote administration tool.
- Defensive Notes
- Download apps only from official app stores and verify the app and developer.
- Review requested permissions, particularly Accessibility and permission to install packages from unknown sources.
- Keep Android and mobile security software updated.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | accessor[.]fud2026[.]com | Attacker-used host serving the downloadable cryptomining payload. |
| DOMAIN | aptabase[.]fud2026[.]com | Listed in the article’s domain indicators associated with BeatBanker infrastructure. |
| DOMAIN | aptabase[.]khwdji319[.]xyz | Listed in the article’s domain indicators associated with BeatBanker infrastructure. |
| DOMAIN | bt-mob[.]net | Listed in the article’s domain indicators associated with the BTMOB RAT. |
| DOMAIN | btmob[.]xyz | Website described as providing BTMOB RAT information and redirecting to a Telegram contact. |
| DOMAIN | cupomgratisfood[.]shop | Phishing site impersonating Google Play Store and distributing malicious APKs. |
| DOMAIN | fud2026[.]com | Attacker-used infrastructure hosting the downloadable cryptomining payload. |
| DOMAIN | pool-proxy[.]fud2026[.]com | Fallback proxy mining endpoint used by the XMRig payload. |
| DOMAIN | pool[.]fud2026[.]com | Cryptocurrency mining pool endpoint used by the XMRig payload. |
| MD5 | d3005bf1d52b40b0b72b3c3b1773336b | MD5 hash identified for the malicious StarLink APK. |
| MD5 | f6c979198809e13859196b135d21e79b | MD5 hash identified for the malicious INSS Reebolso APK. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe APK is packed, and the loader uses XOR-encrypted strings and decrypts payloads at runtime.T1102.002 · Bidirectional CommunicationThe malware uses Firebase Cloud Messaging to receive commands and report device telemetry.T1105 · Ingress Tool TransferBeatBanker downloads additional APKs and an ELF cryptomining payload from attacker-used servers.T1204.002 · Malicious FileThe campaign uses a fake Play Store site and app-update screen to trick users into installing malicious APKs.T1417.001The article reports that BTMOB can capture keystrokes in real time.T1429BeatBanker command handling can record audio through the device microphone and send recordings to the C2.T1430BTMOB is reported to monitor GPS location on compromised devices.T1513The article reports real-time screen recording and screen capture capabilities in BTMOB.T1541A foreground service, persistent notification, and looped audio are used to keep the malware running.T1626.001The banking module abuses Android Accessibility services to monitor apps and replace USDT transaction destinations.
Threat Actors
Malware
BeatBankerBeatBanker is an Android Trojan campaign that targets users in Brazil via phishing sites impersonating the Google Play Store to deliver a crypto miner and a banking module (recent samples drop the BTMOB RAT instead).BTMOBBeatBanker is an Android Trojan campaign that targets users in Brazil via phishing sites impersonating the Google Play Store to deliver a crypto miner and a banking module (recent samples drop the BTMOB RAT instead).CraxsRATBTMOB is an Android remote administration tool that evolved from the CraxsRAT, CypherRAT, and SpySolr families.CypherRATBTMOB is an Android remote administration tool that evolved from the CraxsRAT, CypherRAT, and SpySolr families.SpySolrBTMOB is an Android remote administration tool that evolved from the CraxsRAT, CypherRAT, and SpySolr families.
Vendors
Products
AndroidBeatBanker is an Android Trojan campaign that targets users in Brazil via phishing sites impersonating the Google Play Store to deliver a crypto miner and a banking module (recent samples drop the BTMOB RAT instead).BinanceThe banking module abuses Accessibility permissions and overlays to intercept and replace USDT transaction destinations in Binance and Trust Wallet, stealing funds silently.Firebase Cloud MessagingIt maintains persistence by looping an almost inaudible audio file, abuses Accessibility and overlay capabilities to intercept USDT transactions, and uses Firebase Cloud Messaging for command-and-control.Google AuthenticatorOpens Google Authenticator (if installed) and enables the AccessService.SendGoogleAuth flag used to monitor and retrieve authentication codesGoogle Play StoreBeatBanker is an Android Trojan campaign that targets users in Brazil via phishing sites impersonating the Google Play Store to deliver a crypto miner and a banking module (recent samples drop the BTMOB RAT instead).Trust WalletThe banking module abuses Accessibility permissions and overlays to intercept and replace USDT transaction destinations in Binance and Trust Wallet, stealing funds silently.WhatsAppSome of the samples that deliver BTMOB appear to use WhatsApp to spread, as well as phishing pages.