
TaxiSpy Android RAT Targets Russian Banking Apps with VNC-Style Remote Control
Summary
CYFIRMA analyzes TaxiSpy, an Android banking RAT targeting Russian users, detailing native-code XOR obfuscation, Firebase C2, WebSocket remote control and theft of SMS, contacts, call logs, notifications and keystrokes. Its C2 was unresponsive during testing.
Key points
- The analyzed TaxiSpy sample identifies Russian banking apps and can request default SMS status, potentially enabling SMS and OTP interception.
- Researchers describe how the sysruntime.so native library conceals C2 and Firebase configuration with rolling XOR routines and non-linear memory access.
- The malware uses HTTP POST and WebSocket communications with an identified C2 IP, and Firebase-backed command delivery.
- Reported capabilities include collecting SMS, contacts, call logs, clipboard contents, notifications and keystrokes, as well as screen capture and remote interaction through Accessibility and MediaProjection.
- The report describes persistence through boot startup, foreground services, scheduled jobs, Accessibility abuse and push messaging.
- During dynamic testing, the app's WebView attempt to reach taxi[.]ru and its connection attempts to the C2 were unsuccessful.
- The researchers provide a YARA rule and recommend monitoring suspicious permissions, native libraries and network activity.
Article Details
- Attack Vectors
- The report says the malware is distributed through social engineering, repackaged popular apps, and localized distribution channels.
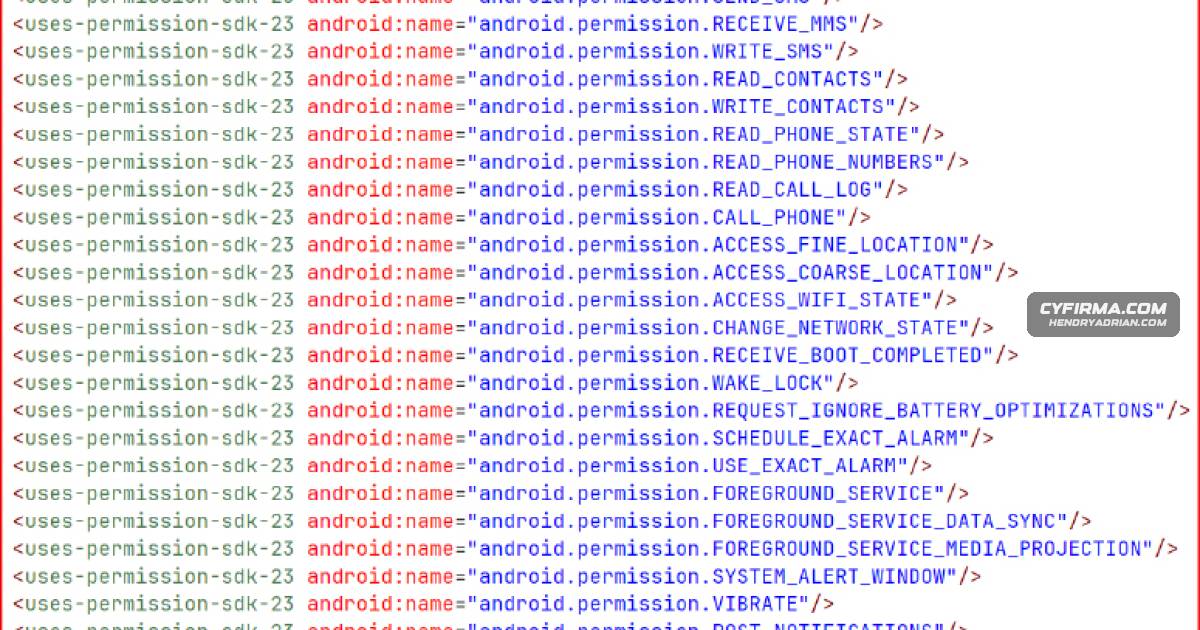
- It requests extensive permissions and asks to become the default SMS app, enabling SMS and OTP access if the user grants the request.
- It communicates with its command server using HTTP POST and WebSocket connections, and uses Firebase push messages for command delivery.
- Defensive Notes
- Monitor for the identified command server and suspicious HTTP POST requests to /api/v1/sync/* or WebSocket connections associated with remote control.
- Restrict installation of untrusted apps and monitor for apps requesting SMS, Accessibility, overlay, and boot-persistence permissions or attempting to become the default SMS app.
- Detect hidden or disguised apps and unexpected native libraries such as sysruntime.so; audit installed apps and permissions for abnormal activity.
- Consider authentication methods resistant to SMS interception, and prepare procedures to isolate infected devices and revoke compromised credentials.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 193[.]233[.]112[.]229 | Command-and-control and data-exfiltration server used by the malware. |
| SHA256 | 67d5d8283346f850eb560f10424ea5a9ccdca5e6769fbbbf659a3e308987cafd | Hash of the RuTaxi APK sample analyzed as the TaxiSpy Android banking malware. |
MITRE ATT&CK
T1414Captures clipboard contents and sends them to the command server.T1417.001Captures keystrokes and forwards the logged input to the command server.T1418Enumerates installed apps and classifies banking, marketplace, government, and cryptocurrency apps.T1422Detects network changes to reconnect to its command infrastructure.T1426Collects device and system details including model, OS version, and SIM metadata.T1437.001Uses HTTP POST and WebSocket communications for control and data transfer.T1513Uses MediaProjection and WebSockets for real-time screen streaming.T1516Uses Accessibility and MediaProjection for remote interaction with the device.T1541Maintains long-running foreground services to reduce the chance of termination.T1628.002Changes the launcher category from LAUNCHER to INFO to conceal the app icon.T1629.001Uses Accessibility abuse and other mechanisms to hinder app removal.T1636.002Collects call history and sends it to the command server.T1636.003Collects contacts, including names and phone numbers, and sends them to the command server.T1636.004Reads and exfiltrates SMS messages and can take over default SMS handling.T1646Exfiltrates SMS, contacts, call logs, clipboard data, notifications, and keystrokes over its command channel.