
Fake Google Meet Update Abuses Windows Enrollment to Give Attackers MDM Control
Summary
A fake Google Meet update page invokes Windows’ ms-device-enrollment: handler and can enroll PCs in an attacker-controlled Esper MDM server if users complete the prompt. The attacker can then manage devices without malware or credential theft.
Key points
- Fake Google Meet update buttons invoke Windows’ ms-device-enrollment: URI and open the native work-or-school enrollment dialog.
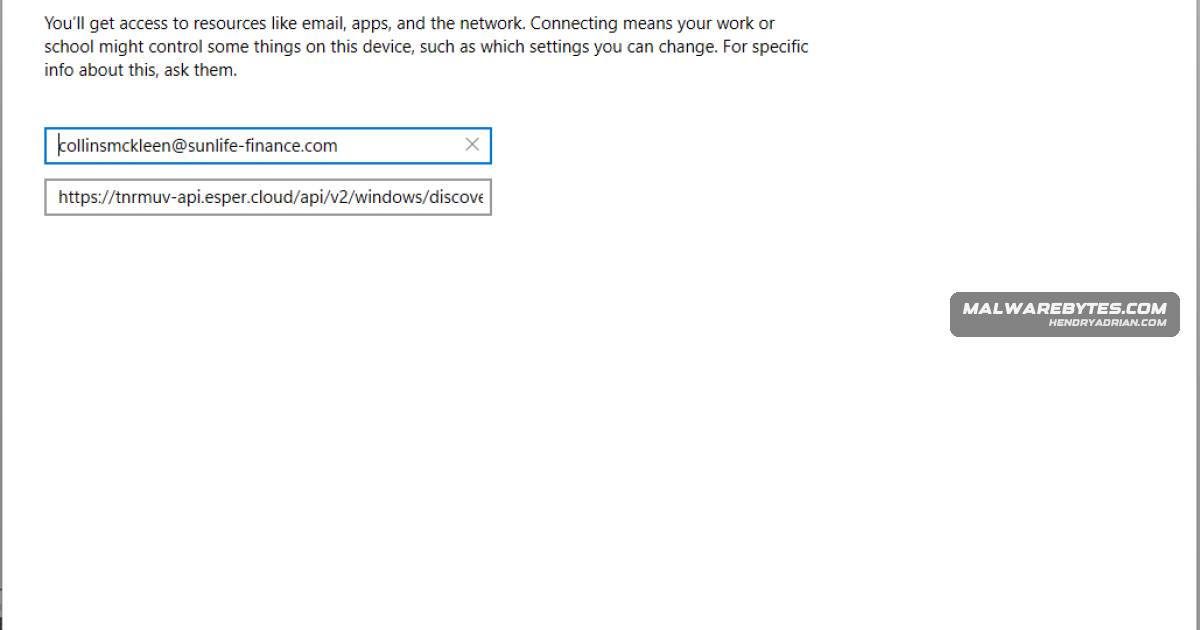
- Completing the enrollment wizard can connect a PC to an attacker-controlled Esper MDM server; the URI includes a prefilled username using sunlife-finance[.]com.
- The article identifies preconfigured Esper blueprint and group IDs embedded in the server URL.
- An MDM administrator can install or remove software, change settings, read files, lock the screen, or wipe an enrolled device.
- The attack abuses legitimate Windows and Esper features; the article reports no malicious executable or credential theft.
- Users should check Settings > Accounts > Access work or school for unknown enrollments and disconnect them; administrators can restrict unapproved MDM enrollment.
Article Details
- Attack Vectors
- A fake Google Meet update page uses the Windows ms-device-enrollment: URI scheme to open the native work-or-school enrollment dialog.
- The enrollment URI is pre-populated with an attacker-controlled Esper MDM server and management profile identifiers; completing the wizard enrolls the device.
- The page uses a username with a domain impersonating Sun Life Financial as part of the enrollment prompt.
- Defensive Notes
- Check Settings > Accounts > Access work or school for unrecognized enrollments and disconnect them.
- If enrollment was completed through updatemeetmicro[.]online, treat the device as potentially compromised and run an up-to-date, real-time anti-malware scan for secondary payloads.
- IT administrators can consider policies that block unapproved MDM enrollment, including restrictions on which MDM servers Windows devices may join.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | sunlife-finance[.]com | Domain used in the enrollment username that the article identifies as impersonating Sun Life Financial. |
| DOMAIN | updatemeetmicro[.]online | Phishing page domain impersonating a Google Meet update; cited as the page used to initiate enrollment. |
| HOSTNAME | tnrmuv-api[.]esper[.]cloud | Attacker-controlled Esper MDM server specified in the Windows enrollment URI. |
MITRE ATT&CK
Vendors
Products
Google MeetA convincing fake Google Meet update page uses Windows’ ms-device-enrollment deep link to silently enroll victims’ PCs into an attacker-controlled MDM server hosted on Esper.IntuneIf affected, check Settings > Accounts > Access work or school for unknown entries and disconnect them, run up-to-date anti-malware scans, and consider policies to block unapproved MDM enrollments via Intune.Microsoft WindowsA convincing fake Google Meet update page uses Windows’ ms-device-enrollment deep link to silently enroll victims’ PCs into an attacker-controlled MDM server hosted on Esper.