
Validin Maps Coruna iOS Exploit Kit Infrastructure to Iran-Themed Lures
Summary
Validin used historical DNS, host-response fingerprints and YARA hunts to map suspected PLASMAGRID C2 and Coruna dropper infrastructure, finding 200+ possible delivery domains and Iran-themed lures among broader scam themes.
Key points
- Coruna, first seen in February 2025, has five exploit chains comprising 23 exploits targeting iOS 13–17.2.1.
- Earlier reporting linked Coruna to a surveillance customer, a July 2025 watering-hole campaign on Ukrainian websites, and Chinese scam sites used in crypto-draining schemes.
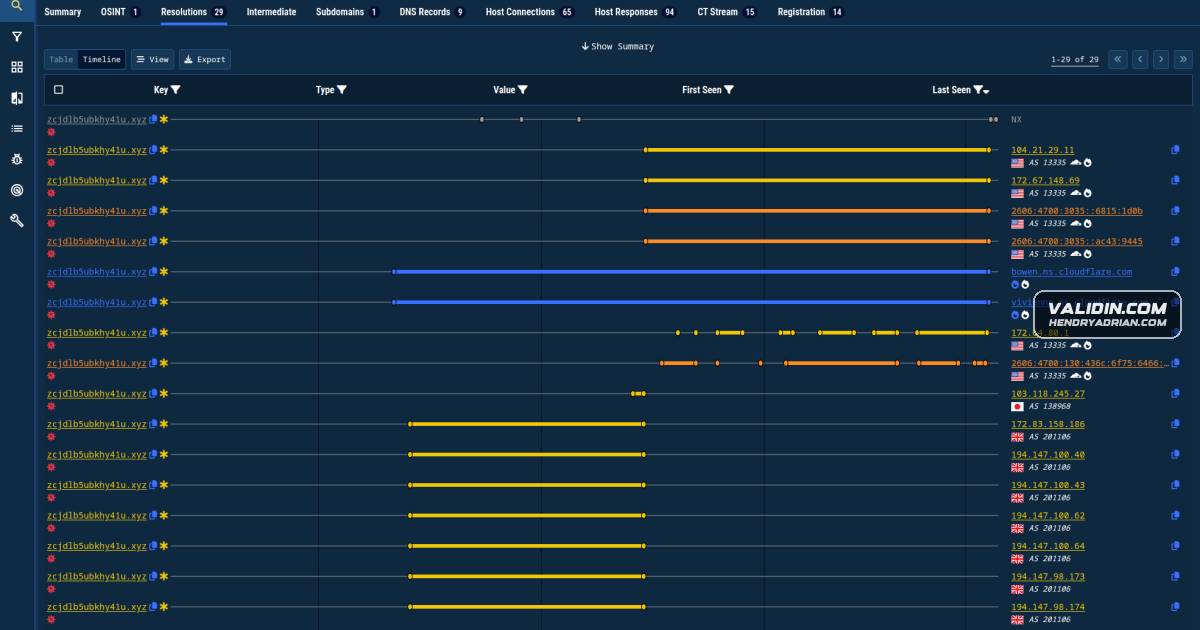
- Validin used historical DNS A-record pivots and distinctive HTTP response fingerprints to identify additional suspected PLASMAGRID C2 domains; many of the domains were no longer resolving.
- YARA hunts for LaSDK initialization patterns, JavaScript files and concealed iframe behavior found more than 200 domains and subdomains that appeared to deliver the exploit path.
- The researchers found 27 unique hosts returning seemingly malicious iframe content and identified recently registered Iran-themed lure sites; the article says the varied themes may indicate opportunistic use and possibly multiple actors.
- Validin published domain, URL and response-hash indicators to support further threat hunting, while describing the related infrastructure as suspected rather than confirmed.
Article Details
- Attack Vectors
- Coruna was delivered through watering-hole pages on compromised Ukrainian websites and through mass-deployed scam websites.
- Dropper pages used JavaScript SDK initialization and offscreen iframes to load exploit code in the browser.
- Iran-themed support pages were among the lure pages observed hosting suspected droppers.
- Defensive Notes
- The article used historical DNS records and low-volume IP pivots to identify domains associated with the C2 infrastructure.
- HTTP response fingerprints and banner hashes were used to find additional potentially related C2 hosts.
- YARA hunts for LaSDK initialization, related JavaScript, and offscreen iframe patterns identified suspected delivery domains and URLs.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 6cxrf02iacu9s87[.]xyz | Domain found through historical DNS pivots among domains with overlapping suspected C2 activity. |
| DOMAIN | fgr1w3gnsdvsb[.]xyz | Domain identified as part of the expanded PLASMAGRID C2 infrastructure. |
| DOMAIN | firansupport[.]cyou | Recently registered Iran-themed page identified as hosting a suspected Coruna dropper. |
| DOMAIN | fwz1x2jtnvsb[.]xyz | Domain serving a C2 endpoint found in YARA analysis of Coruna-related pages. |
| DOMAIN | gr1w2gnsdvsb[.]xyz | Domain identified as part of the expanded PLASMAGRID C2 infrastructure. |
| DOMAIN | gr3a1fv80g6sb[.]xyz | Domain identified as part of the expanded PLASMAGRID C2 infrastructure. |
| DOMAIN | h5iixig1wb4ibjo[.]xyz | Domain found through historical DNS pivots among domains with overlapping suspected C2 activity. |
| DOMAIN | iransupport[.]cyou | Recently registered Iran-themed page identified as hosting a suspected Coruna dropper. |
| DOMAIN | nh843cbkjgr1tfh[.]xyz | Domain found through historical DNS pivots among domains with overlapping suspected C2 activity. |
| DOMAIN | nn2a1fv80g6sb[.]xyz | Domain identified as part of the expanded PLASMAGRID C2 infrastructure. |
| DOMAIN | ockkht8v7nv1nuw[.]xyz | Domain found through historical DNS pivots among domains with overlapping suspected C2 activity. |
| DOMAIN | remote222helper[.]com | Domain linked to remote-themed iframe infrastructure by a shared response banner fingerprint. |
| DOMAIN | u-ipzooile00ca1gqid[.]site | Domain hosting a C2 endpoint found in YARA analysis. |
| DOMAIN | v2gmupm7o4zihc3[.]xyz | Domain that resolved to an IP address associated with the suspected C2 activity during the reported period. |
| DOMAIN | wz1w2gnsdvsb[.]xyz | Domain identified as part of the expanded PLASMAGRID C2 infrastructure. |
| DOMAIN | wzk2nbdawerbsb[.]online | Domain hosting a C2 endpoint found in YARA analysis. |
| DOMAIN | wzk2nccccrbsb[.]online | Domain hosting a C2 endpoint found in YARA analysis. |
| DOMAIN | ztvnhmhm4zj95w3[.]xyz | Domain that resolved to an IP address associated with the suspected C2 activity during the reported period. |
| IPV4 | 119[.]8[.]238[.]183 | Historical DNS pivot point connecting multiple domains associated with the suspected C2 activity. |
| IPV4 | 156[.]254[.]5[.]4 | Host serving recently registered Iran-themed pages identified as dropper sites. |
| IPV4 | 203[.]168[.]129[.]71 | IP address linking domains identified in the suspected C2 infrastructure. |
| MD5 | a205ca801f41dcb4d2ad4fa82b50c651 | HTTP response banner fingerprint used to identify additional PLASMAGRID C2 domains. |
| MD5 | de652f1142d47ee89253ff4e65759045 | Response banner fingerprint linking remote-themed iframe domains to related infrastructure. |
| MD5 | e3bc53583ac3a7fcd2ee923dce3fe280 | Cloudflare response banner fingerprint associated with PLASMAGRID C2 domains. |
| URL | hxxps[:]//ai-scorepredict[.]com/static/analytics[.]html | Exploit-delivery URL identified in GTIG indicators and observed serving the Coruna dropper page. |
| URL | hxxps[:]//ajskbnrs[.]xn--jor0b302fdhgwnccw8g[.]com/gogo/list.html | Iframe URL identified in YARA matches as hosting a presumed-malicious resource. |
| URL | hxxps[:]//fgr1w2gnsdvsb[.]xyz/x | C2 endpoint configured in the dropper page's LaSDK initialization. |
| URL | hxxps[:]//ios[.]lgdzwfop[.]cn/details/view.html | Iframe URL identified in YARA matches as hosting a presumed-malicious resource. |
| URL | hxxps[:]//remotehealthcheck[.]com/static/analytics.html | Iframe resource identified by YARA analysis as hosting presumed-malicious content. |
| URL | hxxps[:]//remotexxxyyy[.]com/static/analytics.html | Iframe resource identified by YARA analysis as hosting presumed-malicious content. |
MITRE ATT&CK
T1059.004 · Unix ShellDropper pages used JavaScript, including LaSDK initialization calls, to configure and orchestrate the exploit flow.T1071.001 · Web ProtocolsThe article describes implant-to-C2 communication over HTTPS and identifies C2 endpoints.T1189 · Drive-by CompromiseCoruna was delivered through watering-hole pages on compromised websites and through scam and lure pages.T1203 · Exploitation for Client ExecutionThe kit contained five exploit chains with 23 exploits targeting iOS 13 through 17.2.1 to exploit iPhones.
Vendors
Products
iOSCoruna is a multi-chain iOS exploit kit first seen in February 2025 that contains five exploit chains across 23 exploits targeting iOS 13–17.2.1 and has been observed in watering-hole and mass-deployed scam campaigns.iPhoneGroup (GTIG) and the iVerify Team both detailed findings related to an exploit kit targeting Apple iPhone users nicknamed “Coruna,” publishing indicators related to initial exploit exposure (the infection
Tools
ValidinValidin’s historical DNS and host-response analysis, plus YARA hunts, mapped extensive PLASMAGRID C2 and dropper infrastructure including Iran-themed lures and hundreds of suspected delivery domains.YARAValidin’s historical DNS and host-response analysis, plus YARA hunts, mapped extensive PLASMAGRID C2 and dropper infrastructure including Iran-themed lures and hundreds of suspected delivery domains.