cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2390 articles

Threat Research · securityweek.com

Armored Likho APT Uses BusySnake Stealer in Espionage Operations

Kaspersky reports that Armored Likho targets government and electric power organizations in multiple countries. Its tools include BusySnake Stealer, which can collect credentials and other data, capture screenshots, and provide remote access.
Jul 6, 2026
Threat Research · research.checkpoint.com

Check Point Details Cavern Manticore’s Modular C2 Framework and Intrusions

Check Point analyzes Cavern, a modular .NET C2 framework used by Iran-linked Cavern Manticore against Israeli organizations. The malware supports reconnaissance, data access, credential attacks and tunneling; intrusions abused RMM tools and trusted IT-provider access.

Jul 6, 2026
Threat Research · microsoft.com

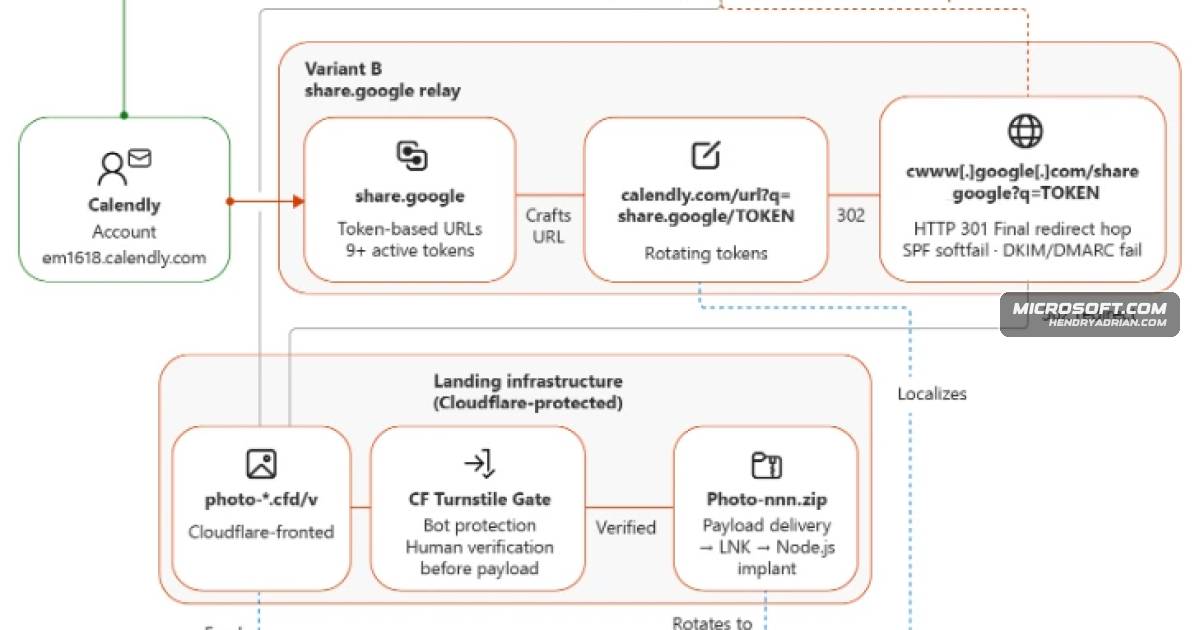
Photo ZIP Campaign Targets Hotels With Persistent Node.js Implant

Microsoft reports a campaign targeting hospitality organizations in Europe and Asia with fake image shortcuts and a Node.js implant. Phishing messages abuse Calendly and Google redirects; the actor and ultimate objective remain unknown.

Jul 6, 2026
Threat Research · microsoft.com

Microsoft Analyzes Chromium Extension That Intercepted Search Queries

Microsoft says a malicious Chromium extension impersonating Perplexity AI routed Omnibox searches and typed suggestions through attacker infrastructure, where its server code logged requests and headers. Google removed it after Microsoft's report; credential theft was未t

Jul 6, 2026
Threat Research · hexastrike.com

STORESOCKS Campaign Uses Trojanized Microsoft Store Apps to Turn Hosts Into Proxies

STORESOCKS distributes signed, trojanized Microsoft Store utilities that install a Go proxy with startup persistence. The campaign remained active in June 2026, using infected hosts for encrypted TCP and UDP relays.

Jul 4, 2026
Threat Research · bleepingcomputer.com

Researchers Say JadePuffer Ransomware Used an AI Agent to Run the Attack

Sysdig researchers say JadePuffer used an LLM agent across a ransomware attack, from exploiting CVE-2025-3248 in Langflow to encrypting 1,342 Alibaba Nacos configuration items. They call it the first documented operation of its kind.

Jul 4, 2026
Threat Research · thehackernews.com

PolinRider Campaign Spreads 108 Malicious Packages and Browser Extensions

Researchers link PolinRider, tied to North Korea-aligned Contagious Interview, to 108 malicious packages and extensions. The campaign abuses developer tooling and repositories to deliver BeaverTail variants and payloads including DEV#POPPER RAT and OmniStealer.

Jul 4, 2026
Threat Research · thehackernews.com

Armored Likho Targets Government and Power Sectors with BusySnake Stealer

Kaspersky details Armored Likho campaigns against government and power-sector targets in Russia, Brazil and Kazakhstan, including spear-phishing chains and BusySnake Stealer capabilities for stealing credentials, documents, screenshots and Telegram data.

Jul 3, 2026
Threat Research · thehackernews.com

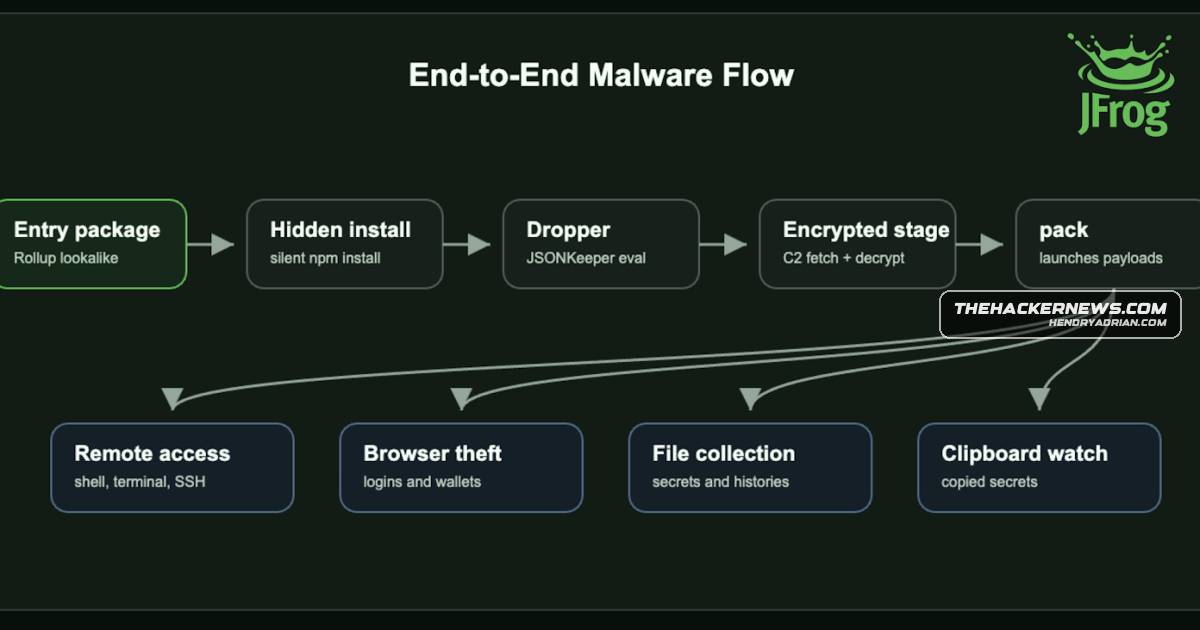
North Korea-Linked Actors Use Fake Rollup npm Packages to Steal Developer Secrets

JFrog identified fake Rollup polyfill npm packages that use staged payloads to provide remote access and steal developer credentials, files, browser data, and cryptocurrency wallet information. The packages have been removed from npm.

Jul 3, 2026
Threat Research · securelist.com

Researchers Detail Armored Likho’s BusySnake Stealer Campaign

Researchers detail campaigns attributed with medium confidence to Armored Likho against government and power-sector targets in Russia, Brazil and Kazakhstan, and analyze BusySnake Stealer’s credential theft, persistence, C2 tasking and reverse-SSH capabilities.

Jul 3, 2026
Threat Research · bleepingcomputer.com

Talos Finds Technical Ties Between ARToken and EvilTokens Phishing Services

Cisco Talos reverse-engineered ARToken, a Microsoft 365 phishing platform that appears linked to EvilTokens. The toolkit steals authentication tokens, supports persistent access, and enables mailbox and cloud-file access.

Jul 3, 2026
Threat Research · labs.k7computing.com

Boss Scam Malware Uses DLL Sideloading to Target WhatsApp Web Sessions

K7 analysis describes Boss Scam lures that deliver a signed executable and malicious DLL, which sideloads malware to persist, collect Chromium browser artifacts, and send them over TCP—potentially enabling WhatsApp Web session hijacking and internal impersonation.

Jul 3, 2026
Threat Research · securityweek.com

Sysdig Details AI-Agent-Assisted Ransomware Attack via Langflow

Sysdig reports that JadePuffer exploited CVE-2025-3248 in an exposed Langflow instance, using an LLM to find credentials, move to a production server, exploit Nacos, and encrypt 1,342 service configuration items.

Jul 3, 2026
Threat Research · levelblue.com

Phishing Campaign Uses Obfuscated Excel-to-HTA Chains to Deliver Remcos and AsyncRAT

LevelBlue SpiderLabs traced a global phishing campaign using macro-enabled Excel files, obfuscated HTA and PNG stages, and rotating infrastructure to deliver Remcos and AsyncRAT; FormBook and Lumma may also be involved.

Jul 3, 2026
Threat Research · thehackernews.com

Reports Detail Anubis Citrix Bleed 2 Exploitation, The Gentlemen BYOVD and VECT-TeamPCP Alliance

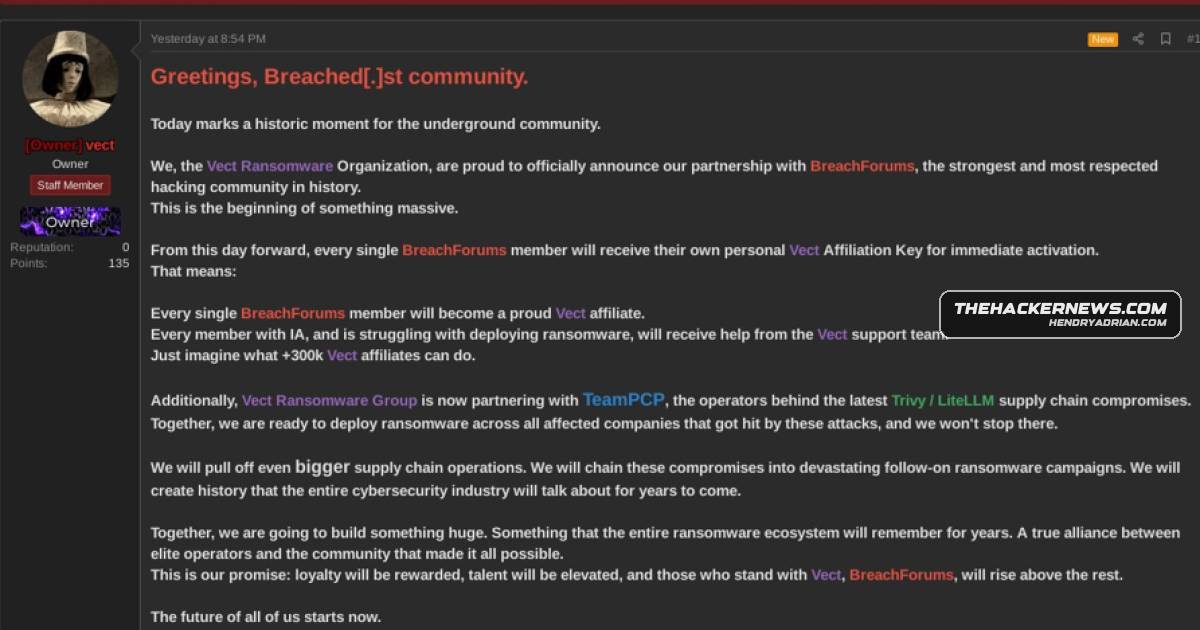
Reports describe Anubis affiliates exploiting Citrix CVE-2025-5777 and using VPN credentials, The Gentlemen’s Go backdoor and BYOVD activity, and VECT-TeamPCP’s supply-chain-to-ransomware partnership.

Jul 2, 2026
Threat Research · arcticwolf.com

Arctic Wolf details Anubis affiliates’ use of CitrixBleed 2 and legitimate RMM tools

Arctic Wolf’s review of multiple Anubis intrusions found initial access via valid VPN credentials or CitrixBleed 2 (CVE-2025-5777), followed by RMM abuse, credential access and pre-encryption exfiltration activity. Logs did not confirm a usable Cloudflare Tunnel.

Jul 2, 2026
Threat Research · thehackernews.com

ChocoPoC RAT Hides in Fake Python PoCs to Steal Researchers’ Data

YesWeHack and Sekoia found ChocoPoC RAT hidden in dependencies of at least seven fake GitHub Python PoCs. It steals browser data and files, enables remote commands, and uses Mapbox and DNS-over-HTTPS for C2; downloads do not confirm infections.

Jul 2, 2026
Threat Research · sysdig.com

Sysdig Reports JADEPUFFER Agentic Ransomware Operation Targeting Langflow and Nacos

Sysdig TRT says JADEPUFFER used CVE-2025-3248 to access Langflow, harvest credentials and reach a production MySQL/Nacos server, where it encrypted and deleted configuration data. The team assesses the campaign was LLM-driven; claimed exfiltration was not verified.

Jul 2, 2026
Threat Research · zscaler.com

Hidden Website Instructions Target AI Agents in Two Prompt-Injection Campaigns

Zscaler ThreatLabz describes two campaigns using hidden website instructions and SEO poisoning to manipulate AI agents, and reports that some of 26 tested LLMs mishandled the sites.

Jul 2, 2026
Threat Research · esentire.com

DenoGate Backdoor Delivered Through Microsoft Teams IT-Helpdesk Impersonation

eSentire analyzed a campaign that used email bombing and Microsoft Teams helpdesk impersonation to trick a retail customer into installing DenoGate, a Deno-based backdoor capable of command execution, persistence, and TCP tunneling.

Jul 2, 2026
Threat Research · bleepingcomputer.com

ChocoPoC RAT Targets Researchers Through Trojanized GitHub PoCs

Sekoia found GitHub PoC repositories delivering the ChocoPoC RAT through malicious PyPI dependencies. The malware can run commands and collect files and browser data; researchers say the campaign likely used compromised accounts.

Jul 1, 2026
Threat Research · securelist.com

Kaspersky Details ScreenConnect-to-AsyncRAT Campaign Using Fake Freeware Sites

Kaspersky MDR traced a campaign using fake freeware sites to sideload ScreenConnect and deploy AsyncRAT. Its investigation describes the multi-stage infection chain, persistence methods, and more than 90 localized domains.

Jul 1, 2026
Threat Research · feeds.fortinet.com

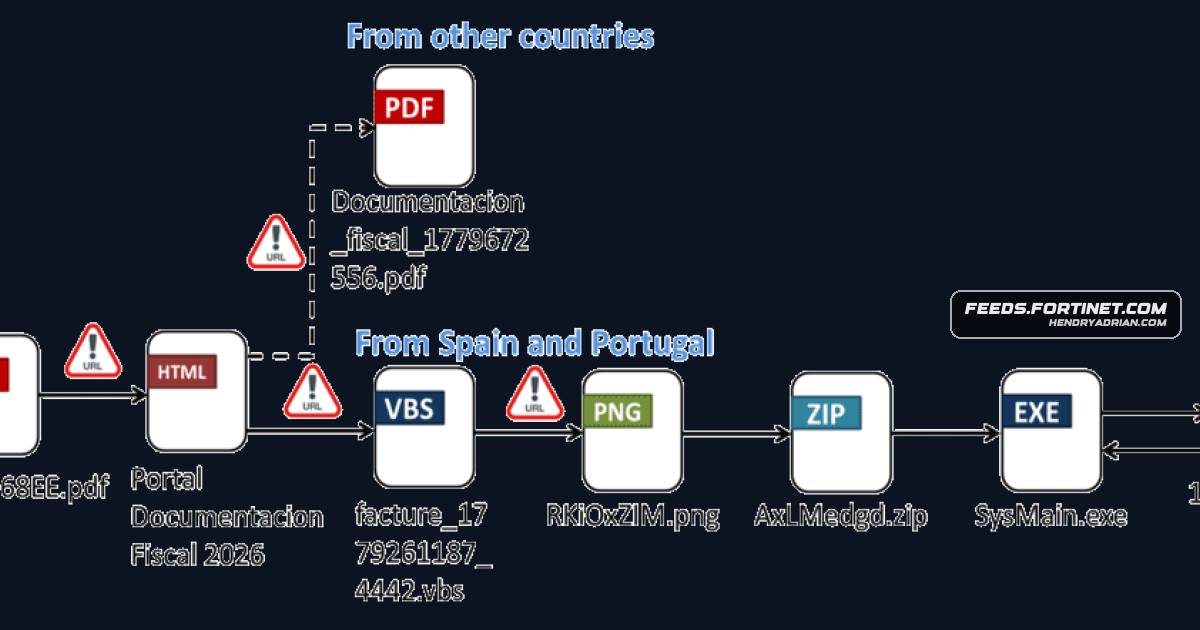
Ousaban Banking Trojan Targets Users in Spain and Portugal

FortiGuard details an Ousaban campaign targeting Spain and Portugal through phishing PDFs and a staged payload, with geofencing, evasion, persistence, and daily changing C2 domains.

Jul 1, 2026
Threat Research · sekoia.com

Trojanized PoCs Target Vulnerability Researchers with ChocoPoC Python RAT

Researchers identified a campaign using malicious GitHub PoCs and trojanized PyPI dependencies to infect vulnerability researchers and pentesters with ChocoPoC, a persistent Python RAT that steals credentials and files and executes commands.

Jul 1, 2026
PreviousPage 47 of 100 Next
© 2026 cyber.hendryadrian.com