
DNS Deep Dive Examines Infrastructure Behind macOS ClickFix Campaign
Summary
A DNS investigation of a Microsoft-reported macOS ClickFix campaign examined infrastructure linked to Macsync, Shub Stealer and AMOS, including 691 email-connected domains, 14 of which investigators identified as malicious.
Key points
- Microsoft reported that ClickFix actors used malicious commands hosted on blogs and other user-generated content platforms to lure people seeking macOS help; the campaign delivered Macsync, Shub Stealer and AMOS.
- The investigators began with 140 network indicators and retained 138 after filtering out items they considered legitimate or inactive: nine subdomains, 121 domains and eight IP addresses.
- Network traffic data showed 11 client IP addresses queried 14 domain indicators 5,375 times between March 24 and April 9, 2026.
- The researchers found 119 IP addresses potentially owned by victims communicating with five IP indicators between December 9, 2025, and May 22, 2026.
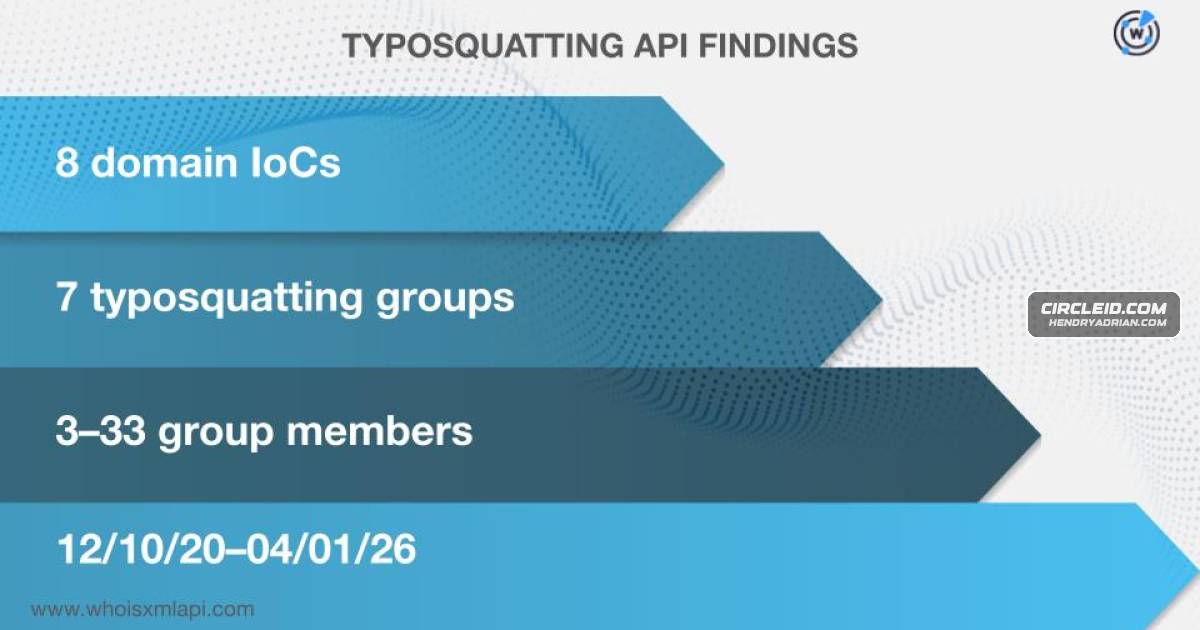
- Eight domain indicators appeared in seven typosquatting groups; the investigators also assessed eight domains as likely registered with malicious intent.
- Historical WHOIS records linked 61 domains to 375 email addresses; reverse-WHOIS searches expanded the investigation to 691 email-connected domains, 14 of which threat-intelligence queries identified as malicious.
Article Details
- Attack Vectors
- Attackers used ClickFix lures on blog and other user-generated content platforms to reach people seeking macOS troubleshooting advice, hosting malicious commands that delivered Macsync, Shub Stealer, and AMOS.
- The campaign used typosquatting and domains reported as likely registered with malicious intent.
- Defensive Notes
- The article recommends supplementary investigation to corroborate entities identified as malicious or suspicious.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | atcoconst[.]com | Email-connected domain reported as weaponized for malware distribution. |
| DOMAIN | coco2-hram[.]com | Campaign domain IoC listed in the First Watch Malicious Domains Data Feed. |
| DOMAIN | cvols[.]com | Email-connected domain reported as weaponized for malware distribution. |
| DOMAIN | ejecen[.]com | Email-connected domain reported as weaponized for malware distribution. |
| DOMAIN | quantumdataserver5[.]homes | Campaign domain IoC listed in the First Watch Malicious Domains Data Feed. |
| DOMAIN | rapidfilevault4[.]cyou | Campaign domain IoC listed in the First Watch Malicious Domains Data Feed and included in a typosquatting group. |
| DOMAIN | rapidfilevault5[.]sbs | Campaign domain IoC in the same typosquatting group as rapidfilevault4[.]cyou; the group’s domains were reported as look-alikes. |
| DOMAIN | res2erch-sl0ut[.]com | Campaign domain IoC listed in the First Watch Malicious Domains Data Feed. |
| DOMAIN | rvdownloads[.]com | Email-connected domain reported as weaponized for malware distribution. |
| DOMAIN | tmcnex[.]com | Campaign domain IoC listed in the First Watch Malicious Domains Data Feed. |
| DOMAIN | woupp[.]com | Email-connected domain reported as weaponized for malware distribution. |
| HOSTNAME | apple-mac-fix-hidden[.]medium[.]com | Subdomain IoC described as a suspicious tech-support or SEO lure hosted on a publishing platform. |
| HOSTNAME | claudecodedoc[.]squarespace[.]com | Subdomain IoC that the article says possibly impersonates official Claude Code documentation. |
| IPV4 | 199[.]217[.]98[.]33 | Campaign IP IoC; the article reports 173 historical IP-to-domain resolutions and says victim-owned IPs communicated with campaign IP IoCs. |
MITRE ATT&CK
T1036.005 · Match Legitimate Resource Name or LocationThe claudecodedoc[.]squarespace[.]com subdomain was reported as possibly impersonating official Claude Code documentation.T1204.001 · Malicious LinkThe campaign lured macOS users into interacting with malicious commands hosted on blog and user-generated content platforms.T1583.001 · DomainsThe campaign involved numerous domain IoCs, including typosquatting domains and domains reported as likely registered with malicious intent.
Malware
Atomic macOS Stealer (AMOS)Microsoft analyzed a ClickFix campaign that targeted macOS users with Macsync, Shub Stealer, and AMOS, using malicious commands hosted on blog and other user-generated content platforms to lure people seeking macOS help.MacSyncMicrosoft analyzed a ClickFix campaign that targeted macOS users with Macsync, Shub Stealer, and AMOS, using malicious commands hosted on blog and other user-generated content platforms to lure people seeking macOS help.SHub StealerMicrosoft analyzed a ClickFix campaign that targeted macOS users with Macsync, Shub Stealer, and AMOS, using malicious commands hosted on blog and other user-generated content platforms to lure people seeking macOS help.