
RedWing Android Spyware Offers Custom Droppers and Remote Control as a Service
Summary
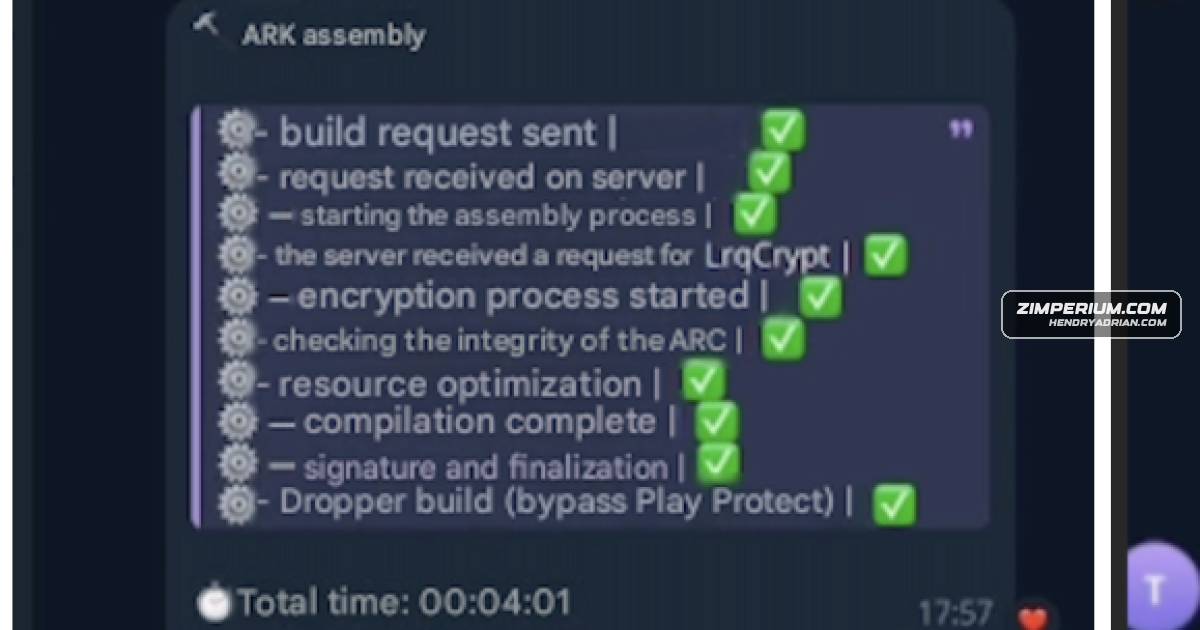
Zimperium researchers analyzed RedWing, an Android spyware service promoted through Telegram. It uses customizable phishing droppers, credential-stealing overlays and remote device controls, and can redirect calls using USSD commands.
Key points
- RedWing operators can create phishing pages that impersonate app stores and customize their appearance to distribute malicious Android packages.
- The analyzed payload uses deceptive prompts to seek SMS, notification and Accessibility access; its dropper impersonated RuStore.
- The malware can deploy banking and cryptocurrency overlays, while its control panel lets operators change targeted apps without distributing a new version.
- Researchers identified 82 targeted institutions, with a strong focus on Russian financial organizations.
- A call-forwarding command issues a USSD request to redirect incoming calls, potentially intercepting voice-based authentication.
- RedWing uses Android’s MediaProjection API for screen streaming and supports remote interaction, data theft, camera and microphone capture, and HTTP flood attacks.
- Researchers noted similarities to Oblivion malware and apparent links to Russian threat actors, but did not establish definitive attribution.
Article Details
- Attack Vectors
- Mobile-targeted phishing sites imitate app marketplaces and deliver malicious Android APKs.
- Custom onboarding screens persuade victims to grant Accessibility, notification and default SMS permissions and disable battery optimization.
- Fraudulent overlays target banking and cryptocurrency apps to harvest credentials and device unlock information.
- C2 commands enable remote device control, data theft, call forwarding and HTTP-flood DDoS attacks.
- Defensive Notes
- Zimperium says its Mobile Threat Defense and zDefend products detect RedWing and its droppers on-device, and that Web Content Filtering can block malicious sites.
- The article recommends using fraud indicators such as active screen sharing to help detect malicious activity and prevent credential theft.
MITRE ATT&CK
T1406.002The analyzed malware dynamically loads encrypted DEX components from its assets.T1417.001A live keylogger captures user interactions and sends them to the server.T1418The get_apps command retrieves the device's installed applications.T1429The start_recording command uses MediaRecorder to capture ambient audio.T1512The take_photo command remotely captures images using the device camera.T1513RedWing captures screenshots and streams the device screen using MediaProjection.T1516RedWing uses Accessibility to simulate taps, swipes and text entry during remote device control.T1517The malware requests notification access and can monitor device notifications.T1616The call_forward_set command uses a hidden USSD request to forward incoming calls to an attacker-controlled number.T1636.002The get_calls command collects call logs from the infected device.T1636.003The malware reads and exports device contacts.T1636.004RedWing collects SMS messages, including verification messages, from infected devices.T1646RedWing sends stolen data, including keylogs and captured recordings, to its C2 server.T1655.001Droppers imitate app marketplaces, including a sample masquerading as RuStore.T1660Operators distribute malicious APKs through mobile-targeted phishing sites that imitate app stores.
Malware
oblivionThis discovery looks like a new variant of the oblivion malware, due to the similarity on the dropper stage and some of the overlays used.RedWingRedWing is a new Android spyware MaaS promoted through Telegram, with phishing-based distribution, customizable droppers, and strong links to Russian threat actors.
Vendors
Products
AndroidRedWing is a new Android spyware MaaS promoted through Telegram, with phishing-based distribution, customizable droppers, and strong links to Russian threat actors.Mobile Runtime Protection (zDefend)Zimperium’s Mobile Threat Defense (MTD) and Mobile Runtime Protection (zDefend) provide on-device, behavioral detection that identifies RedWing and similar droppers the moment they are installed on the device withoutMobile Threat DefenseZimperium’s Mobile Threat Defense (MTD) and Mobile Runtime Protection (zDefend) provide on-device, behavioral detection that identifies RedWing and similar droppers the moment they are installed on the device without