
Proofpoint Details UNK_MassTraction Campaign Exploiting Roundcube to Steal University Credentials
Summary
Proofpoint details suspected China-aligned UNK_MassTraction activity targeting US and Canadian university departments via Roundcube flaws CVE-2024-42009 and CVE-2025-49113, deploying credential-stealing IceCube and SquareShell or VShell.
Key points
- Proofpoint says it has tracked suspected China-aligned cluster UNK_MassTraction since May 2026, targeting physics and engineering departments at US and Canadian universities.
- CVE-2024-42009 lets malicious JavaScript run when an email is opened in a vulnerable Roundcube webmail client; IceCube then steals credentials, two-factor authentication material, cookies, and browser data.
- IceCube uses the session’s CSRF token and CVE-2025-49113, a deserialization flaw, to install the SquareShell webshell, which is timestomped to resemble a legitimate plugin.
- If webshell deployment fails, a fallback shell script loads an architecture-specific loader identified as SNOWLIGHT, which retrieves and runs the VShell backdoor in memory.
- The chain uses deferred triggers to retry exploitation and removes user and malware-initiated sessions, which Proofpoint says can remove forensic evidence.
- Proofpoint assesses the cluster as likely espionage-motivated and China-aligned, citing infrastructure, VShell use, targeting, and Chinese-language artifacts; it says it cannot currently link the activity to a separate Trellix-reported campaign.
Article Details
- Attack Vectors
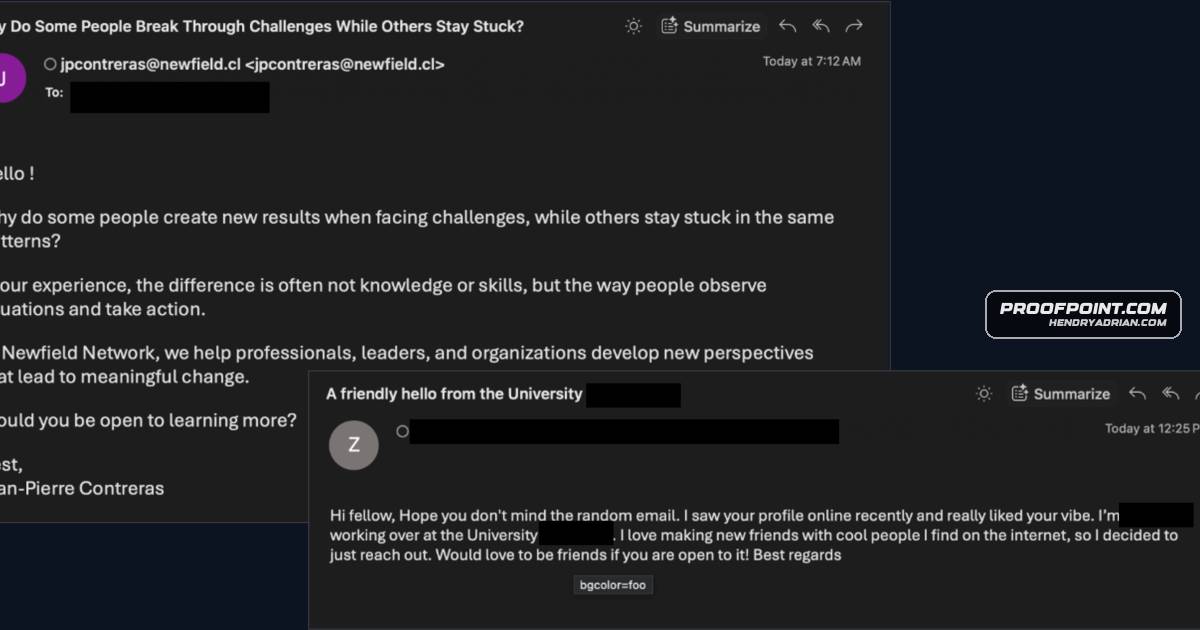
- Phishing emails targeting university physics and engineering departments exploited CVE-2024-42009 when opened in vulnerable Roundcube webmail, executing embedded JavaScript.
- The IceCube JavaScript payload stole credentials, two-factor authentication material, cookies, and browser data, then sent the collected information to C&C.
- IceCube used CVE-2025-49113 to exploit Roundcube deserialization and attempt to install the SquareShell webshell.
- If webshell deployment failed, a fallback shell script fetched and executed a loader that loaded the VShell backdoor in memory.
- Defensive Notes
- Prioritize defending mailservers as thoroughly as VPN concentrators and other remote-access nodes.
- Proofpoint reported scanning relevant address space for SquareShell and coordinating with government and industry partners to notify identified victims.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
jpcontreras@newfield[.]cl | Compromised sender address observed in phishing email headers. | |
| IPV4 | 194[.]213[.]18[.]133 | Reported IceCube JavaScript delivery and C&C infrastructure. |
| IPV4 | 45[.]150[.]109[.]151 | Reported IceCube JavaScript delivery and C&C infrastructure. |
| IPV4 | 45[.]86[.]229[.]111 | Reported VShell C&C infrastructure. |
| SHA256 | a02f124c5ce4180bd130a62ee03262f399c33491de3aed36e0b15155ae4926c0 | SHA-256 hash identified for the IceCube stealer. |
| URL | hxxp[:]//45[.]86[.]229[.]111/slw:8080 | Reported VShell delivery URL. |
| URL | hxxps[:]//194[.]213[.]18[.]133[.]sslip[.]io:23088 | Reported IceCube delivery/C&C URL. |
| URL | hxxps[:]//194[.]213[.]18[.]133[.]sslip[.]io:23088/app/js/jquery.min.js | Specific URL reported for IceCube JavaScript delivery and C&C. |
| URL | hxxps[:]//45[.]150[.]109[.]151[.]sslip[.]io:23088 | Reported IceCube delivery/C&C URL. |
| URL | hxxps[:]//45[.]150[.]109[.]151[.]sslip[.]io:23088/app/js/jquery.min.js | Specific URL reported for IceCube JavaScript delivery and C&C. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe article describes decimal-decoded JavaScript in the email message body and encoded payloads.T1036 · MasqueradingThe VShell loader spoofed its process name as [kworker/0:2].T1036.005 · Match Legitimate Resource Name or LocationSquareShell was placed in a plugin path and timestomped using a legitimate plugin's modification time.T1059.004 · Unix ShellThe fallback chain used a shell script to set up and execute the loader.T1059.007 · JavaScriptEmbedded JavaScript executed in the victim's Roundcube browser and loaded the IceCube payload.T1071.001 · Web ProtocolsIceCube sent stolen data via HTTP POST and the loader communicated with C&C over HTTP/HTTPS.T1082 · System Information DiscoveryThe fallback script identified the host architecture before fetching the corresponding loader payload.T1105 · Ingress Tool TransferThe fallback shell script fetched a loader payload from C&C and executed it.T1185 · Browser Session HijackingIceCube accessed the Roundcube browser session and stole cookies and authentication material.T1190 · Exploit Public-Facing ApplicationThe campaign exploited CVE-2024-42009 and CVE-2025-49113 in Roundcube mailservers to gain access and install a webshell or run a backdoor.
CVE
Threat Actors
Malware
IceCubeThe intrusions deployed the IceCube stealer, SquareShell webshell, and VShell backdoor while using layered evasion, persistence, and fallback mechanisms to maintain access.SNOWLIGHTIf webshell deployment failed, the chain could fall back to a shell script that loaded SNOWLIGHT and then VShell into memory.SquareShellThe intrusions deployed the IceCube stealer, SquareShell webshell, and VShell backdoor while using layered evasion, persistence, and fallback mechanisms to maintain access.VshellThe intrusions deployed the IceCube stealer, SquareShell webshell, and VShell backdoor while using layered evasion, persistence, and fallback mechanisms to maintain access.