
ASEC Details Vidar Infostealer Campaigns Targeting Korea in 2026
Summary
ASEC analyzed Vidar phishing campaigns targeting Korea in the first half of 2026. A Go-based packer decrypts the infostealer in memory; Vidar uses Telegram and Steam profiles to find its C&C server and steals credentials, browser data, tokens, and files.
Key points
- ASEC observed Vidar distribution campaigns targeting Korea in the first half of 2026 and assessed that the campaigns likely involved the same threat actor.
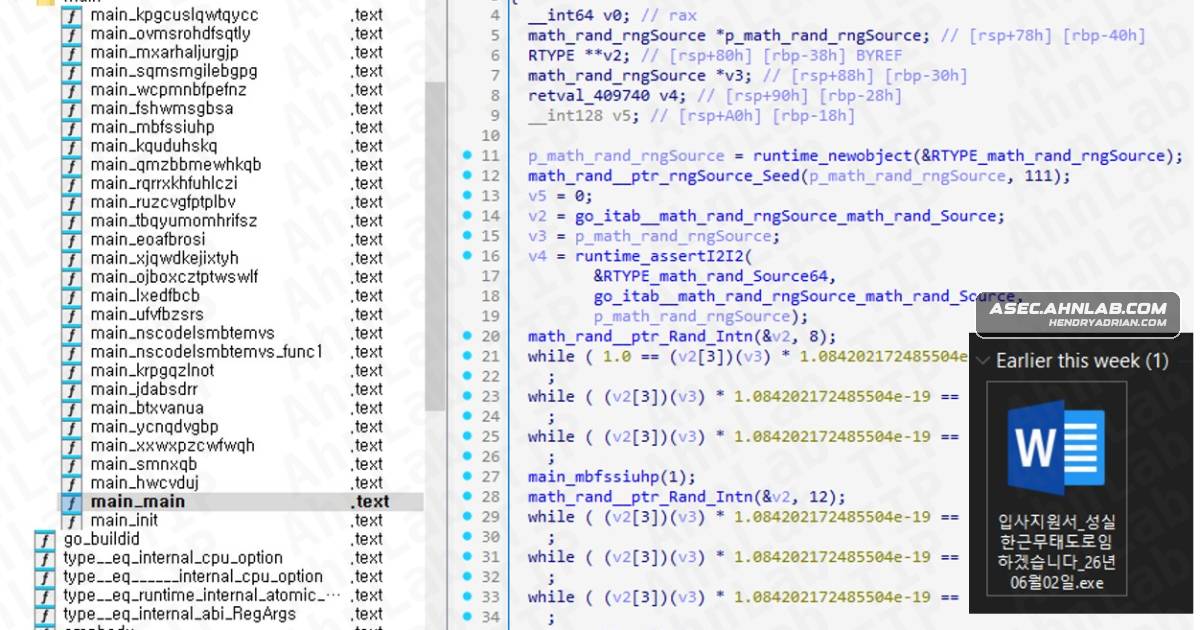
- Phishing emails used job-application and copyright-infringement themes, with resume-like text and executable attachments disguised with a Word document icon.
- A Go-based packer decrypts and executes Vidar in memory; the malware also uses obfuscation, NtGlobalFlag checks, and VM and sandbox checks.
- Vidar uses a Dead Drop Resolver: it checks Telegram and Steam profile pages for a C&C address, using a hard-coded marker to identify it.
- The malware can download additional configuration, payloads, or commands from its C&C server, including lists of targeted browsers, plugins, wallets, and files.
- ASEC found Vidar targeting browser credentials, cookies and history, FTP client credentials, cryptocurrency-related files, Discord, Telegram and Steam data, Azure data, and screenshots.
- ASEC advises caution with email attachments and unknown executables and recommends keeping V3 updated.
Article Details
- Attack Vectors
- Phishing emails used job-application and copyright-infringement themes, with resume-like body text and executable attachments disguised with a Word document icon.
- When a victim ran the attachment, a Go-based packer decrypted Vidar in memory and executed it.
- Vidar retrieved its C&C address from attacker-posted Telegram and Steam profile pages using a hard-coded marker string.
- Vidar collected browser data, credentials, cookies, history, screenshots, cryptocurrency-related files, Discord, Telegram and Steam data, and Azure data, then transmitted stolen information to its C&C server.
- Defensive Notes
- Exercise extreme caution with email attachments and executable files from unknown sources.
- Keep V3 updated to the latest version.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | ctl[.]it-bd[.]com | Campaign-related domain listed by ASEC in the indicators of compromise. |
| DOMAIN | frr[.]ambil-disini[.]web[.]id | Campaign-related domain listed by ASEC in the indicators of compromise. |
| DOMAIN | gor[.]emiraride[.]com | Campaign-related domain listed by ASEC in the indicators of compromise. |
| DOMAIN | gre[.]syslicense[.]net | Campaign-related domain listed by ASEC in the indicators of compromise. |
| DOMAIN | lat[.]sodstreams[.]com | Campaign-related domain listed by ASEC in the indicators of compromise. |
| IPV4 | 107[.]189[.]24[.]190 | C&C server IP address listed in ASEC's indicators of compromise. |
| MD5 | 0b8af4afd26175ba818c0fdb4622bf14 | MD5 hash listed by ASEC for a Vidar malware sample. |
| MD5 | 1bbf1e83eea55e70d59f0d633789011e | MD5 hash listed by ASEC for a Vidar malware sample. |
| MD5 | 2fba9ec34fdf4b1584dd9c69b9ec9393 | MD5 hash listed by ASEC for a Vidar malware sample. |
| MD5 | 4e885b1a0c1d0636e940b4af20fdc8db | MD5 hash listed by ASEC for a Vidar malware sample. |
| MD5 | 536dd0b0f6dff75dc01869df9809df61 | MD5 hash listed by ASEC for a Vidar malware sample. |
| URL | hxxp[:]//107[.]189[.]24[.]190/ | C&C server URL listed in ASEC's indicators of compromise. |
| URL | hxxps[:]//steamcommunity[.]com/profiles/76561198694626397 | Specific Steam profile page used by Vidar to retrieve the C&C address. |
| URL | hxxps[:]//steamcommunity[.]com/profiles/76561198698223785 | Specific Steam profile page used by Vidar to retrieve the C&C address. |
| URL | hxxps[:]//steamcommunity[.]com/profiles/76561198703616215 | Specific Steam profile page used by Vidar to retrieve the C&C address. |
| URL | hxxps[:]//steamcommunity[.]com/profiles/76561198706525776 | Specific Steam profile page used by Vidar to retrieve the C&C address. |
MITRE ATT&CK
T1005 · Data from Local SystemVidar collected local browser databases, application data, wallet files, and other targeted files from the infected system.T1027 · Obfuscated Files or InformationVidar variants used obfuscated code and data to hinder analysis.T1041 · Exfiltration Over C2 ChannelVidar transmitted collected information, including information.Txt and other stolen files, to its C&C server.T1102.001 · Dead Drop ResolverVidar accessed attacker-posted Telegram and Steam profile pages to obtain its actual C&C server address.T1105 · Ingress Tool TransferVidar could download additional payloads or commands from its C&C server.T1113 · Screen CaptureVidar captured and exfiltrated screenshots.T1119 · Automated CollectionVidar automatically collected data specified by configuration, including browser information, wallet files, screenshots, and files matching grabber criteria.T1140 · Deobfuscate/Decode Files or InformationThe Go-based packer decrypted the embedded Vidar payload before executing it in memory.T1204.002 · Malicious FileThe malicious attachment ran when a victim executed the executable disguised with a Word document icon.T1497.001 · System ChecksVidar checked CPU, RAM, and disk usage to detect virtual environments or sandboxes.T1539 · Steal Web Session CookieVidar collected web browser cookies, including Chromium and Firefox cookie data.T1555.003 · Credentials from Web BrowsersVidar collected Chromium-based saved logins and related browser credential data.T1566.001 · Spearphishing AttachmentThe campaign delivered Vidar through phishing emails with executable attachments and job-application or copyright-infringement lures.T1622 · Debugger EvasionVidar used NtGlobalFlag checks as an anti-debugging measure.
Malware
Products
AzureVidar exfiltrated browser data, cookies, history, credentials, Discord/Telegram/Steam tokens, Azure data, screenshots, and cryptocurrency-related files.DiscordVidar exfiltrated browser data, cookies, history, credentials, Discord/Telegram/Steam tokens, Azure data, screenshots, and cryptocurrency-related files.Mozilla FirefoxInformation Targets for Information Theft: List of Firefox-based Web Browser PluginsSteamIt used Dead Drop Resolver via Telegram and Steam profile pages to fetch the real C&C server address, with a hard-coded marker string.TelegramIt used Dead Drop Resolver via Telegram and Steam profile pages to fetch the real C&C server address, with a hard-coded marker string.V3Also, V3 should be updated to the latest version so that malware infection can be prevented.