
RedWing MaaS Rents Android Banking-Fraud Malware Through Telegram
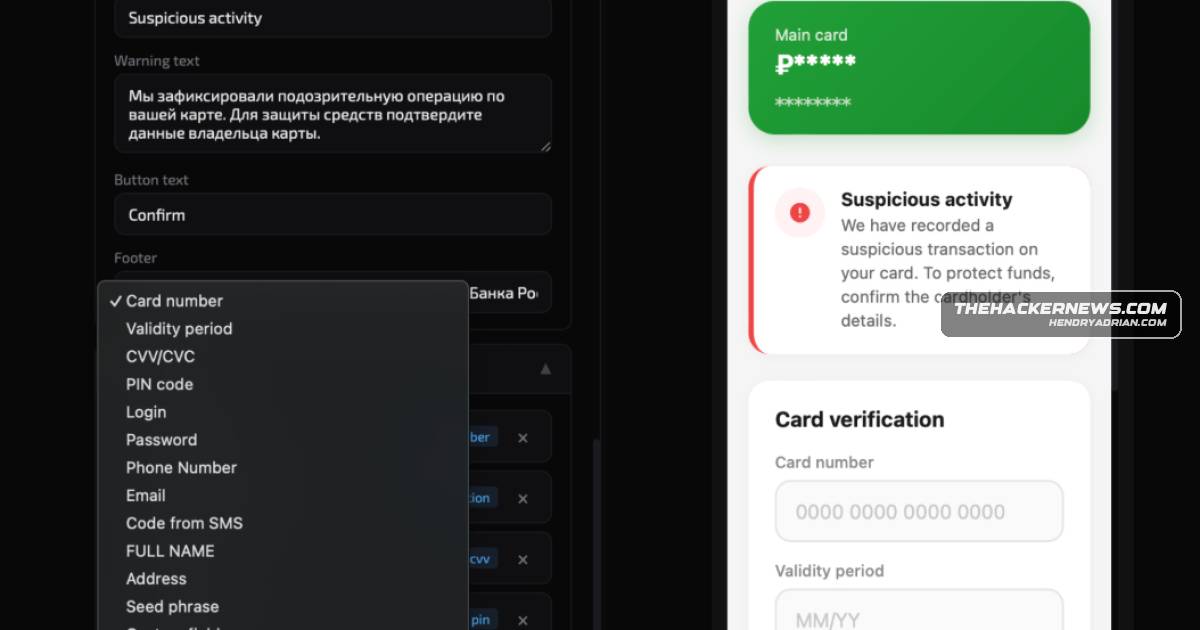
Summary
Zimperium describes RedWing, a Telegram-rented Android fraud service that uses fake app-store pages and abused permissions to steal banking data and control phones. Researchers say it may be linked to Russian threat actors, but have not confirmed that link.
Key points
- RedWing is marketed through Telegram as a subscription service; a bot builds custom apps for buyers.
- Infection begins with phishing links to fake app-store pages that persuade users to sideload an app and grant permissions.
- The malware abuses Accessibility and SMS permissions to steal credentials, one-time codes, card numbers, and PINs through overlays and screen access.
- Its capabilities include call forwarding, keylogging, live screen viewing and control, and access to device data and sensors.
- Zimperium counted 82 targeted institutions, with a strong focus on Russian financial firms; researchers say a Russian-actor link is possible but unconfirmed.
- The article recommends installing apps only from official stores and treating unnecessary Accessibility, default-SMS, and sideloading requests as warning signs.
Article Details
- Attack Vectors
- A phishing link leads to a fake app-store page that persuades users to sideload a RedWing app and approve staged permission requests.
- RedWing abuses Android Accessibility and SMS-related permissions to control devices, capture credentials and one-time codes, and display fake login overlays over banking and cryptocurrency apps.
- The malware can use a hidden carrier code to enable call forwarding, and provides operators with live screen streaming, keylogging, camera and microphone access, and file and contact theft.
- Infected phones can be pooled to flood a target website with traffic in a denial-of-service attack.
- Defensive Notes
- Install apps only from official stores; treat app updates delivered through links or text messages as suspicious.
- Do not enable installation from unknown sources or grant Accessibility, default-SMS, or battery-exemption access without a clear reason.
- Watch for apps that hide their icon after installation.
- On managed devices, block sideloading and flag apps requesting Accessibility or the default-SMS role.
- Track suspicious behavior and permissions rather than relying on app names, since RedWing can be reskinned and overlay targets can be changed.
MITRE ATT&CK
T1411RedWing displays fake login overlays over banking and cryptocurrency apps to capture credentials.T1412RedWing reads incoming text messages to obtain one-time passcodes.T1417RedWing uses a keylogger and captures codes, card numbers, and PINs through Accessibility.T1429RedWing can switch on the device's microphone.T1430RedWing can track the victim device's location.T1432RedWing can steal contacts from infected devices.T1433RedWing can steal call logs from infected devices.T1476RedWing is installed by sideloading an app from outside an official store.T1498 · Network Denial of ServiceThe article says operators can pool infected phones to flood a target website with traffic.T1512RedWing can switch on the device's camera.T1513Operators can stream the victim's screen in real time.T1626.001RedWing abuses Android Accessibility to read screen content and control the victim's phone.T1660A phishing link directs users to a fake app-store page that prompts them to install RedWing.
Malware
Albiriox#RedWingFantasy HubResearchers linked it to Russian-market targeting and shared tactics seen in Oblivion, Fantasy Hub, Albiriox, and Klopatra.Klopatra#RedWingoblivionZimperium says it resembles the Oblivion rental malware and may be linked to Russian threat actors, while defenders are advised to focus on install-time abuse and suspicious permission requests rather than app names.RedWingRedWing is a Telegram-rented Android bank-fraud service that helps criminals hijack phones, steal banking credentials, capture one-time codes, and control calls, screens, and devices in real time.
Products
AndroidRedWing is a Telegram-rented Android bank-fraud service that helps criminals hijack phones, steal banking credentials, capture one-time codes, and control calls, screens, and devices in real time.AppGalleryIts fake app-store pages mimic Google Play, Galaxy Store, AppGallery, and RuStore.Galaxy StoreIts fake app-store pages mimic Google Play, Galaxy Store, AppGallery, and RuStore.Google PlayIts fake app-store pages mimic Google Play, Galaxy Store, AppGallery, and RuStore.RuStoreIts fake app-store pages mimic Google Play, Galaxy Store, AppGallery, and RuStore.TelegramRedWing is a Telegram-rented Android bank-fraud service that helps criminals hijack phones, steal banking credentials, capture one-time codes, and control calls, screens, and devices in real time.