
Google Dialogflow CX Flaw Could Have Exposed Chats Across Agents
Summary
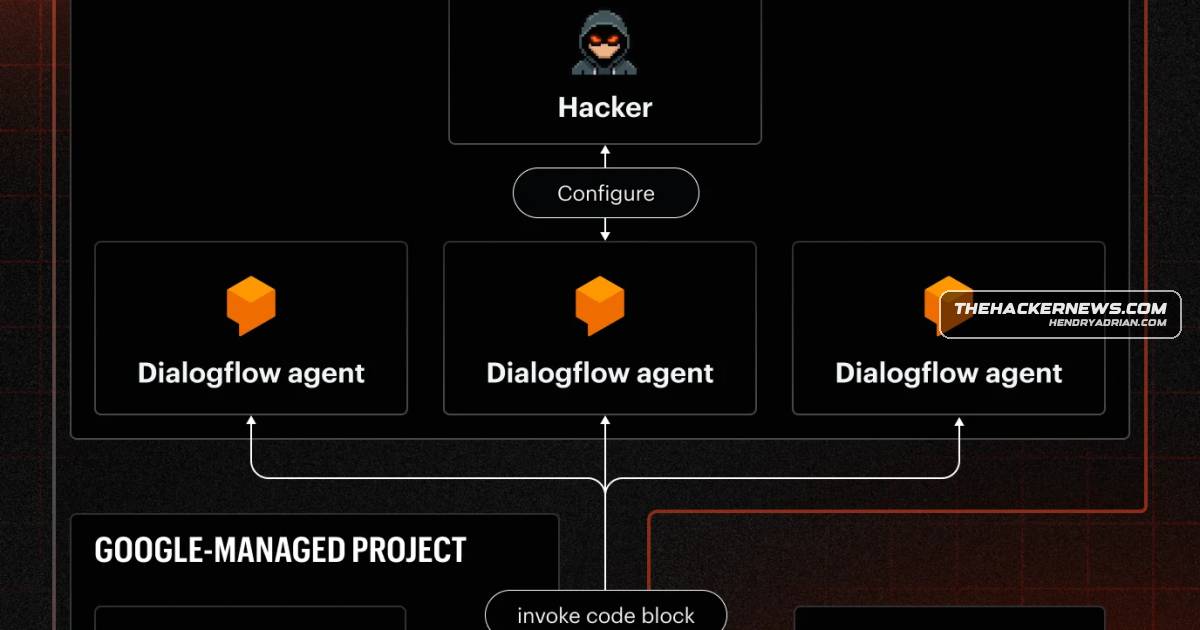
Varonis reported that Dialogflow CX’s shared Code Block runtime could let an attacker with playbook-update permission alter code across agents, read chats, and send forged bot messages. Google fixed the flaws by June 2026; no real-world exploitation was found.
Key points
- Exploitation required the dialogflow.playbooks.update permission on a Code Block-enabled agent; the reported scope was other Code Block-enabled agents in the same Google Cloud project.
- Varonis found that a writable code_execution_env.py file in the shared runtime could be replaced, allowing attacker-controlled code to access conversation history and send forged bot replies.
- Varonis also reported unrestricted outbound internet access in the Code Block environment, which it said could bypass VPC Service Controls.
- The environment exposed IMDS and returned a token for a low-privilege Google-managed service account.
- Customers could not inspect the runtime, and Cloud Logging did not record the file overwrite or injected code, according to the report.
- Google shipped an initial fix in April 2026 and fully resolved the issue in June 2026. Varonis and Google reported no evidence of real-world exploitation.
- Varonis recommended auditing playbook-update permissions, reviewing Dialogflow DATA_WRITE audit logs and failed-request errors, and checking Code Blocks in the console.
Article Details
- Attack Vectors
- An attacker needed the dialogflow.playbooks.update permission on a Code Block-enabled agent; the article says this was not a remote, unauthenticated attack.
- A Code Block could overwrite the writable code_execution_env.py file in a shared runtime, affecting Code Blocks across agents in the same Google Cloud project.
- The shared environment allowed unrestricted outbound internet access, enabling data to be sent to an external server and commands to be received.
- The environment exposed the Instance Metadata Service, which returned a token for a low-privilege Google-managed service account.
- Defensive Notes
- Google fixed the flaw by June 2026; the article reports no evidence of real-world exploitation.
- Audit which roles and accounts hold the dialogflow.playbooks.update permission.
- Review Dialogflow API DATA_WRITE audit logs for unexpected playbook updates and correlate them with unusual users, IP addresses, or access times.
- Check Cloud Logging for failed user requests whose error messages may reveal exceptions from malicious Code Blocks.
- Review each agent’s Playbooks in the Dialogflow console and verify that every Code Block is approved.
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe injected code could send conversation data to an attacker-controlled server and receive commands back through the environment's outbound internet access.T1059.006 · PythonThe attack path used custom Python in a Dialogflow CX Code Block; the modified shared setup code was executed with Python's exec().T1105 · Ingress Tool TransferThe malicious Code Block downloaded a modified code_execution_env.py file from an attacker-controlled server and overwrote the file in the running container.T1552.005 · Cloud Instance Metadata APIThe exposed Instance Metadata Service returned a token for a Google-managed service account when queried.
Vendors
Products
Cloud LoggingThe overwrite happened inside Google’s environment, where customers have no visibility, and Cloud Logging did not record the file change or the injected code.Dialogflow CXA critical flaw in Google Dialogflow CX, dubbed Rogue Agent by Varonis, could have let an attacker with edit rights on one Code Block-enabled agent compromise other agents in the same Google Cloud project.Google CloudA critical flaw in Google Dialogflow CX, dubbed Rogue Agent by Varonis, could have let an attacker with edit rights on one Code Block-enabled agent compromise other agents in the same Google Cloud project.Google Cloud RunThat code runs in a Google-managed Cloud Run environment, and every agent that uses Code Blocks in the same Google Cloud project shares one instance of it.VPC Service ControlsVaronis says this bypasses VPC Service Controls, the Google Cloud perimeter meant to stop data from leaving protected services.