
Researchers Detail Coordinated GitHub API Scraping and Private Repository Access
Summary
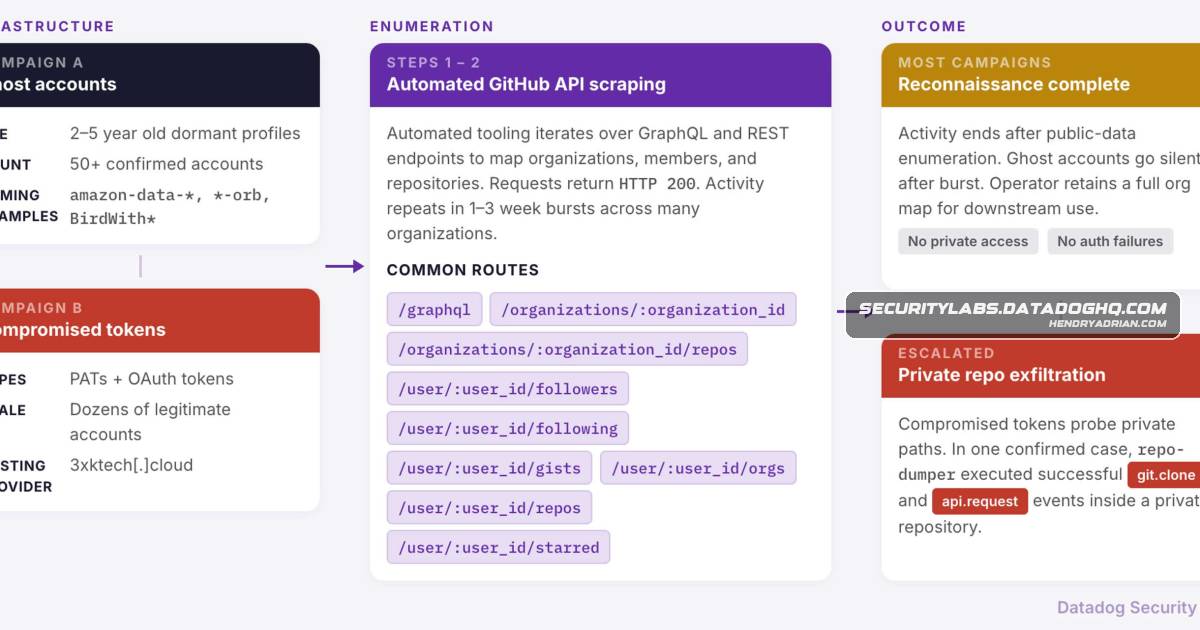
Datadog researchers describe campaigns using dormant accounts and compromised tokens to enumerate GitHub organizations. One actor successfully accessed a private repository; audit-log indicators and queries can help defenders detect activity.
Key points
- Researchers observed coordinated campaigns mapping GitHub organizations, repositories, and users through public API endpoints, especially GraphQL.
- More than 50 dormant “ghost” accounts were used across organizations, often with custom or legitimate-sounding user agents.
- Other campaigns used compromised OAuth tokens and personal access tokens; one series of attempts to access private repository paths failed.
- In a separate case, the user agent repo-dumper successfully accessed a private repository, with audit logs recording git.clone and api.request events.
- Recommended detection pivots include user agent, actor, token type, private-resource actions, and source ASN when available.
- The article provides audit-log queries for private API requests, git clones, and ZIP downloads, and recommends enabling log streaming, baselining normal activity, and threat hunting.
Article Details
- Attack Vectors
- Automated enumeration of GitHub organizations, repositories, user accounts, and public data through the GitHub API, including GraphQL and REST routes.
- Use of dormant GitHub accounts and custom or legitimate-sounding user agents to distribute API requests across organizations.
- Use of compromised OAuth access tokens and personal access tokens to probe private repository paths; the reported attempts in one campaign failed.
- Cloning and other API requests to private repository paths resulted in confirmed access and exfiltration in one reported case.
- Defensive Notes
- Review anomalous GitHub audit-log user agents, especially activity reaching private repositories.
- Monitor private-resource actions and the associated IP address, actor name, and programmatic access type.
- Enable GitHub audit-log streaming, baseline normal user agents, and develop detections tailored to the organization.
- Hunt for private-repository API requests, git.clone events, and repo.download_zip events using OAuth or personal access tokens.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 3xktech[.]cloud | Listed as a hosting provider in the indicators; the article says a campaign's infrastructure ran on 3xK Tech. |
| DOMAIN | cherryservers[.]com | Listed as a hosting provider in the article's indicators of compromise. |