cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2389 articles

Threat Research · thehackernews.com

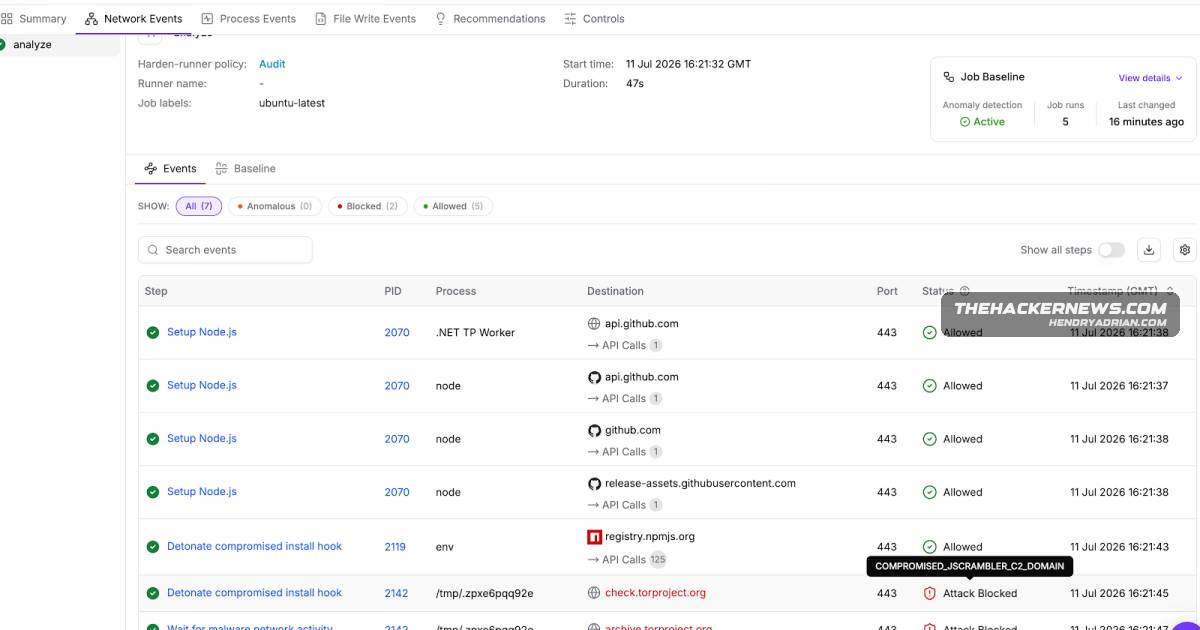
Compromised jscrambler npm Release Delivered Cross-Platform Rust Infostealer

Socket and security researchers reported that jscrambler 8.14.0 contained an install hook that launched a cross-platform Rust infostealer targeting developer secrets. The release remains available; the account or pipeline compromise is unresolved.

Jul 11, 2026
Threat Research · socket.dev

Compromised Jscrambler npm Releases Deliver Cross-Platform Infostealer

Five compromised Jscrambler npm releases delivered a cross-platform infostealer targeting developer credentials and secrets. Jscrambler confirmed unauthorized publication; version 8.22.0 is reported clean, and affected environments should be audited.

Jul 11, 2026
Threat Research · asec.ahnlab.com

Linux SSH Attacks Spread XMRig Miners and Additional Malware

AhnLab analyzed attacks on poorly managed Linux servers that use SSH-scanning malware to spread XMRig miners, ShellBot, and other tools. The malware establishes persistence and disguises mining activity; the campaign appears active since at least 2023.

Jul 11, 2026
Threat Research · bleepingcomputer.com

Ghostcommit Hides Instructions in PNGs to Trick AI Agents Into Exposing Repository Secrets

Researchers demonstrated Ghostcommit, a pull-request attack that hides instructions in a PNG and can lead coding agents to encode .env secrets in committed code. They also tested a multimodal reviewer that blocked nearly all attacks in an 80-PR trial.

Jul 11, 2026
Threat Research · stepsecurity.io

StepSecurity Analyzes Malicious jscrambler npm Releases Hiding Cross-Platform Payloads

StepSecurity reports that five jscrambler npm releases contained native payloads that could run during installation or package import. Analysis found browser credential and wallet-storage capabilities; investigation of the full payload remains ongoing.

Jul 11, 2026
Threat Research · sentinelone.com

SentinelLABS Details Suspected China- and India-Nexus Espionage Against Pakistani Police

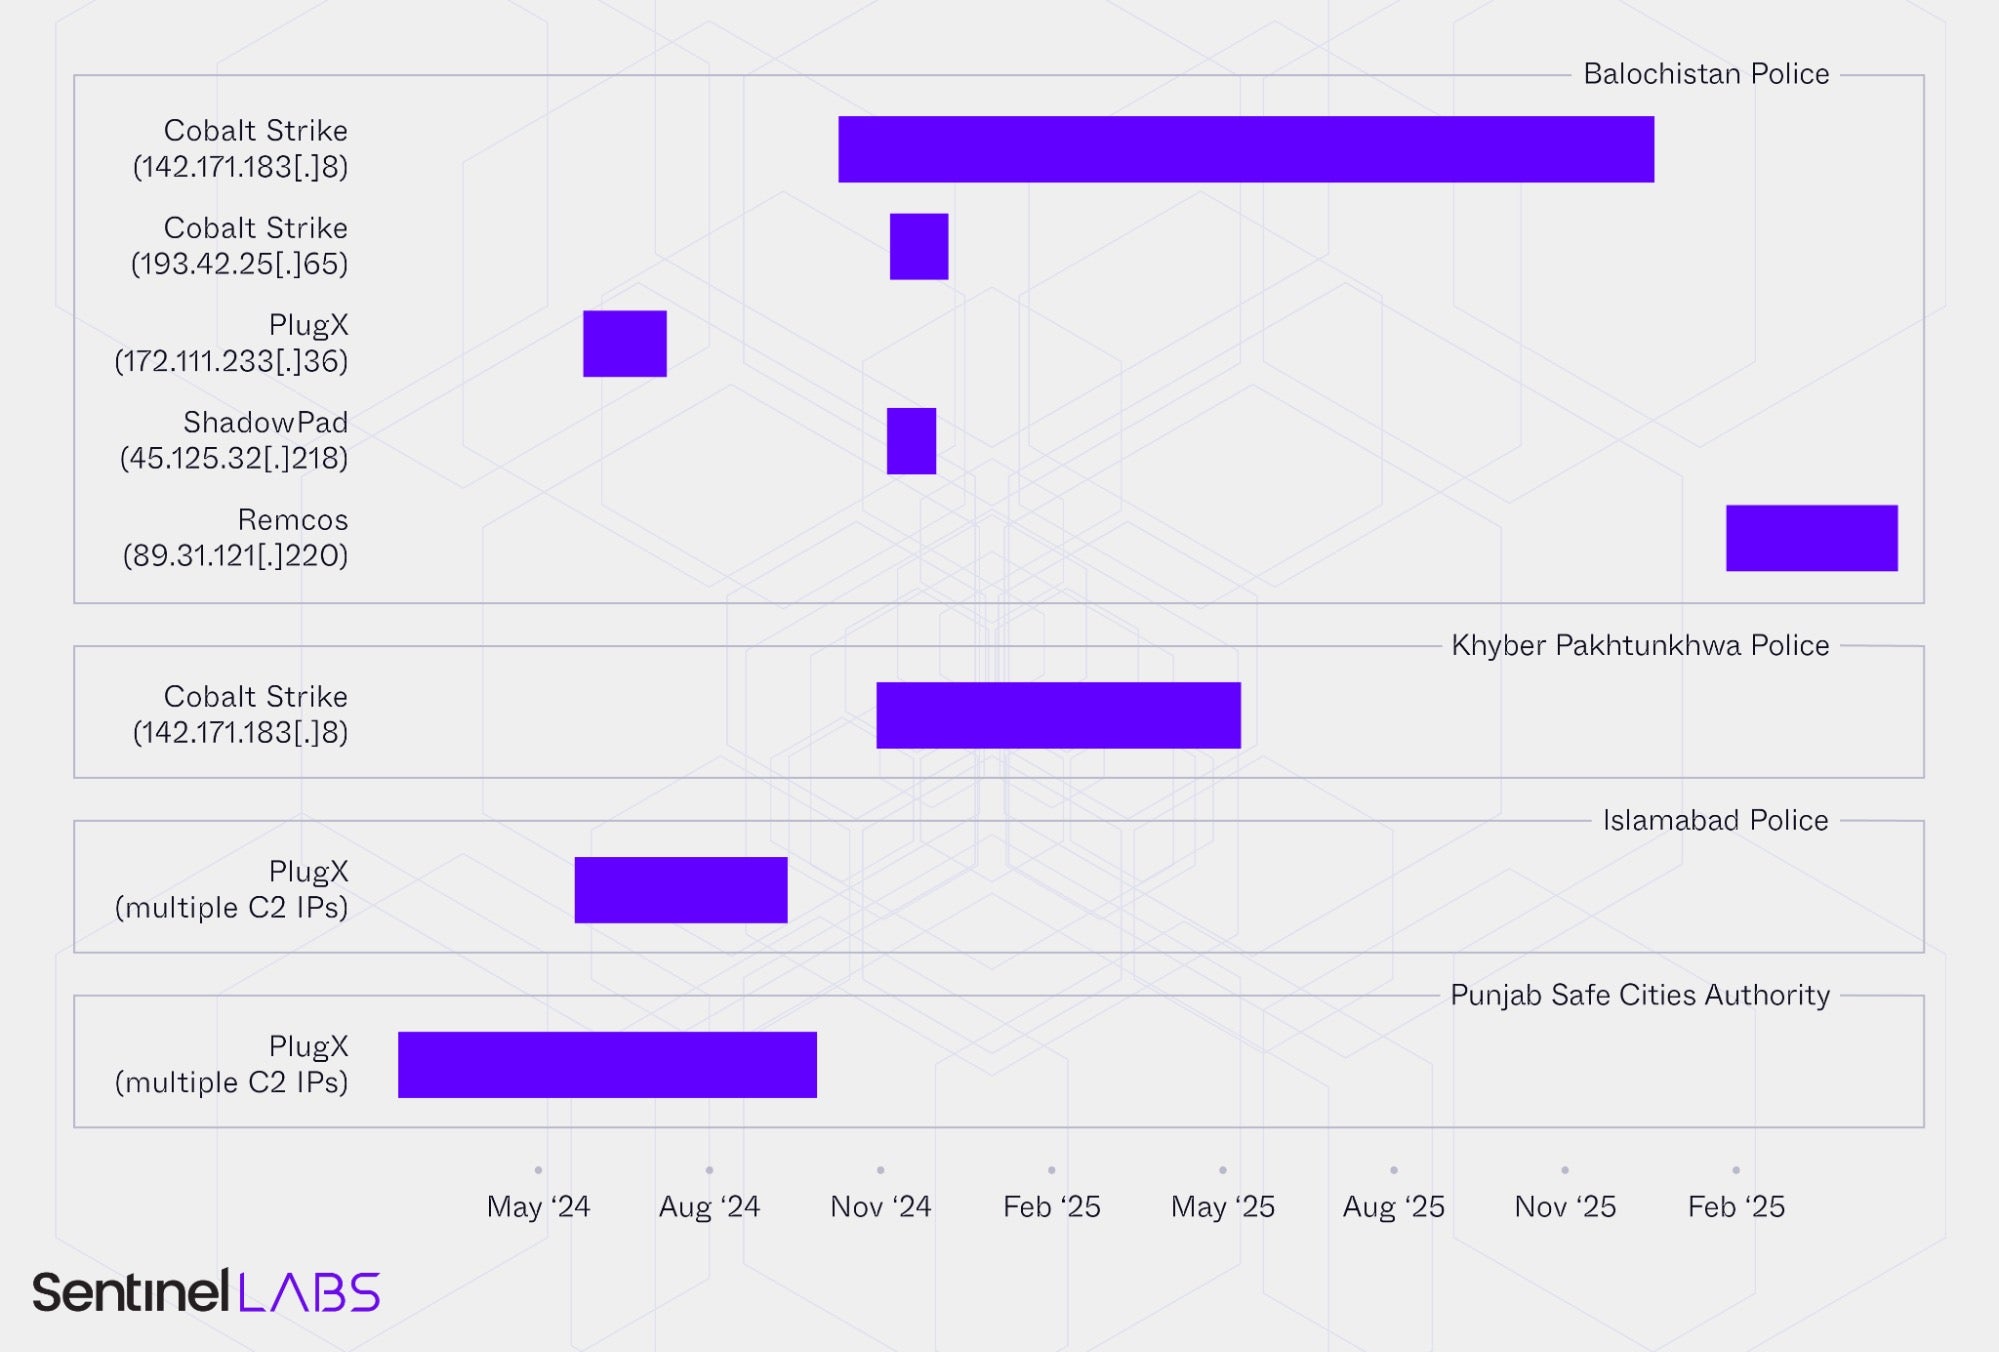
SentinelLABS tracked suspected China- and India-nexus intrusions against Pakistani law enforcement from 2024 to 2026, identifying Balochistan Police as the main target and a compromised complaint portal hosting malware implants.

Jul 10, 2026
Threat Research · circleid.com

DNS Analysis Maps Infrastructure Used in MSHTA-Delivered CountLoader Campaigns

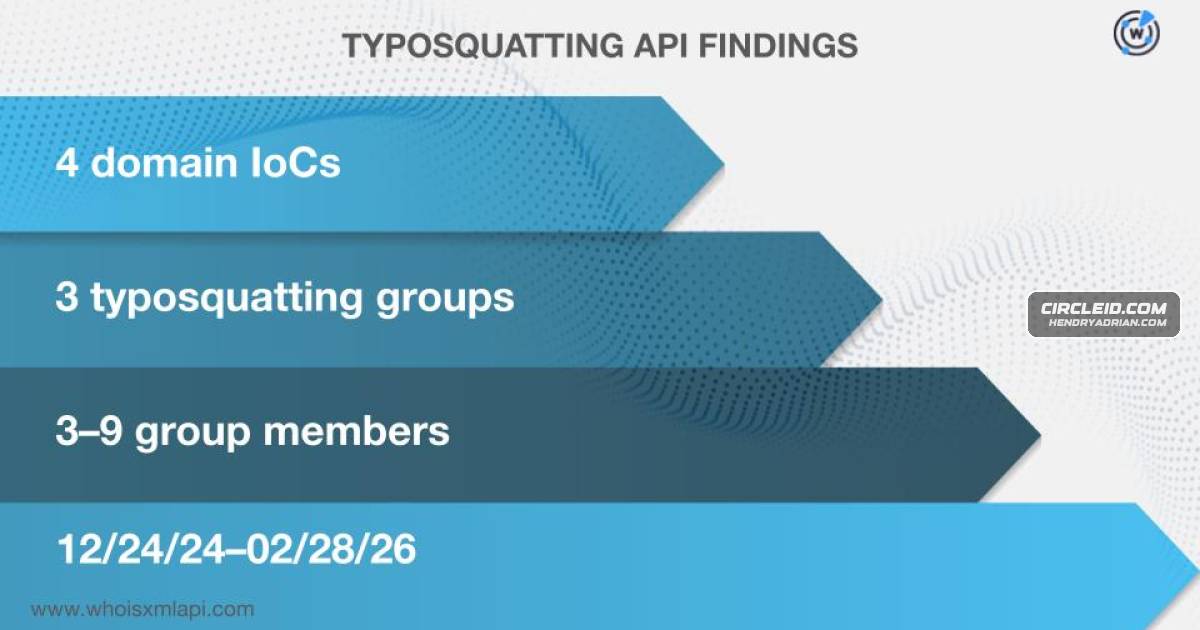
A DNS investigation of MSHTA-related IoCs linked infrastructure to CountLoader campaigns deploying LummaStealer and Amatera. It identified typosquatting clusters, historical resolutions and additional domains, while describing some victim connections as potential.

Jul 10, 2026
Threat Research · securityweek.com

Okta Warns of Vishing Campaign Using Fake Passkey Enrollment Pages

Okta says a campaign uses vishing and fake Microsoft Entra ID passkey pages to target organizations. Its operator-controlled phishing kit guides victims through authentication while the actor may enroll an attacker-controlled passkey.

Jul 10, 2026
Threat Research · zimperium.com

Zimperium Details GoldPickaxe Variant Stealing Banking and Biometric Data

Zimperium’s zLabs describes a GoldPickaxe variant attributed to GoldFactory, distributed through KuaiBo-spoofing phishing sites. It reports 19 samples across five countries and details Android techniques used to steal banking credentials, biometrics and other data.

Jul 10, 2026
Threat Research · thehackernews.com

GigaWiper Combines Three Wiping Methods With Spyware Capabilities

Microsoft’s analysis describes GigaWiper, a Windows backdoor combining three destructive methods with surveillance and remote control. Binary Defense links the same samples to BLUERABBIT and, citing Google’s Threat Intelligence Group, assesses a likely Iran-nexus link.

Jul 10, 2026
Threat Research · opensourcemalware.com

Malicious npm Packages Profile Developers Through Install-Time Scripts

Researchers analyzed malicious npm packages that used install-time scripts to collect developer and environment data. They report the packages and associated account were taken down; the operator’s motive remains unverified.

Jul 9, 2026
Threat Research · socket.dev

Fake Braintree NuGet Packages Steal Payment Card Data and Merchant Credentials

Socket researchers found malicious NuGet packages impersonating Braintree that steal payment card data, merchant credentials, and host secrets. The packages send data to attacker-controlled infrastructure; Socket reported them to NuGet and recommends removal and key and

Jul 9, 2026
Threat Research · bleepingcomputer.com

Researchers Detail Forg365 Phishing Platform Targeting Microsoft 365 Accounts

ZeroBEC researchers detail Forg365, a phishing platform combining device-code and AiTM attacks with AI-generated lures. Its ForgCookie extension is designed to refresh Microsoft SSO cookies and maintain access to compromised accounts.

Jul 9, 2026
Threat Research · security.com

Symantec Traces GodDamn Ransomware to Beast and Details PoisonX Defense Evasion

Symantec traces GodDamn to the Beast/Monster ransomware lineage and describes a June 2026 intrusion using PoisonX, credential-harvesting tools, AnyDesk and PsExec. Initial access was unknown; AnyDesk deployment reached at least 10 hosts before ransomware detection.

Jul 9, 2026
Threat Research · elastic.co

REF6045 Uses ClickFix and SCMBANKER for Mexican Banking Fraud

Elastic researchers describe REF6045, an operator-assisted banking fraud operation using fake CAPTCHA pages to install SCMBANKER, a PowerShell toolkit that monitors banking sessions and supports phishing, payment redirection and remote access.

Jul 9, 2026
Threat Research · aikido.dev

Malicious @injectivelabs/sdk-ts Release Was Designed to Exfiltrate Wallet Keys

Aikido reports that @injectivelabs/sdk-ts 1.20.21 captured wallet mnemonics and private keys and sent them through disguised requests. Seventeen other republished packages pinned to the release could expose users transitively.

Jul 9, 2026
Threat Research · stepsecurity.io

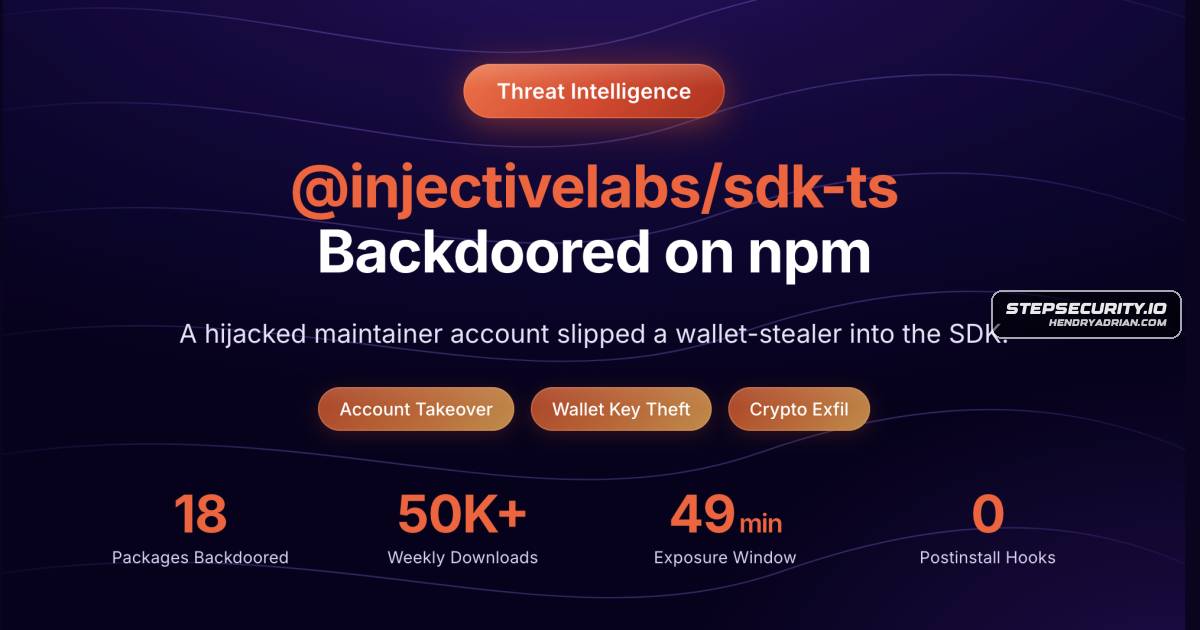
Injective npm Attack Backdoored 18 Packages to Exfiltrate Wallet Keys

Step Security says attackers used a trusted maintainer account to publish malicious Injective SDK version 1.20.21 across 18 npm packages, exfiltrating wallet recovery phrases and private keys. Clean 1.20.23 releases followed about 49 minutes later.

Jul 9, 2026
Threat Research · huntress.com

Huntress Details CitrixBleed 2 Intrusions Leading to DragonForce Ransomware

Huntress describes six similar 2026 intrusions in which attackers exploited CitrixBleed 2 to hijack sessions, escalate privileges, and establish persistence; one intrusion ended with DragonForce ransomware encryption.

Jul 9, 2026
Threat Research · securitylabs.datadoghq.com

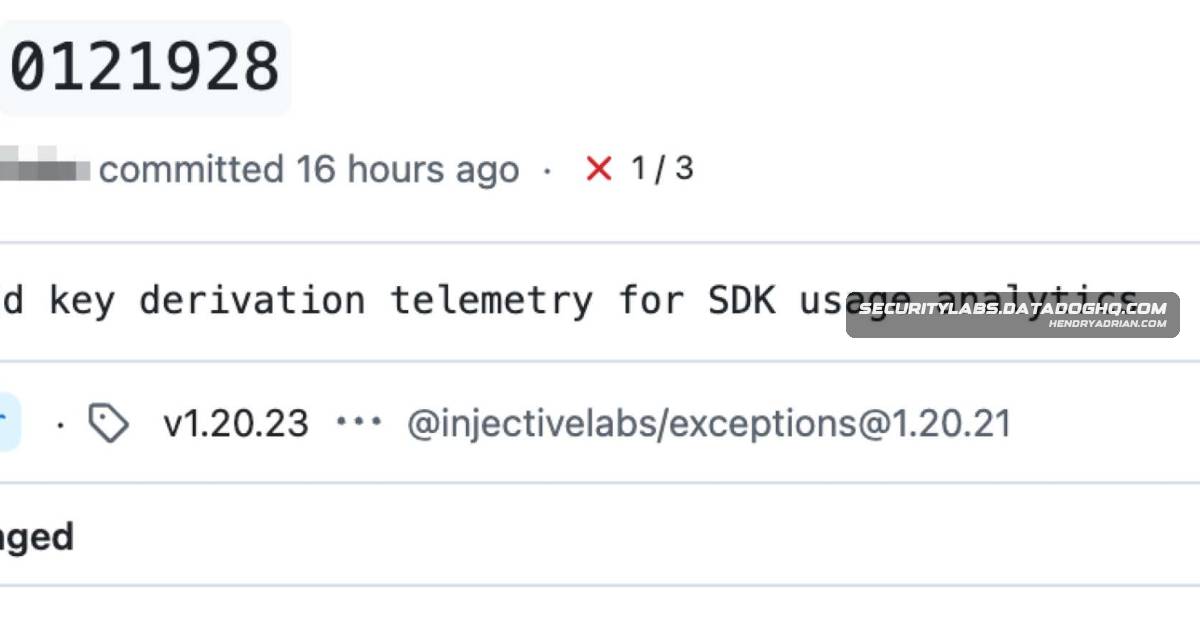
Malicious @injectivelabs/sdk-ts Release Stole Wallet Seed Phrases and Private Keys

Version 1.20.21 of the Injective TypeScript SDK contained code that exfiltrated wallet seed phrases and some private keys through an HTTP header. It was available for about 49 minutes before being removed and replaced with version 1.20.23.

Jul 9, 2026
Threat Research · darktrace.com

Compromised AWS AI Gateway Used for Cryptomining, Darktrace Reports

Darktrace investigated an AWS EC2 instance supporting a LiteLLM gateway that communicated with cryptomining infrastructure. Public SSH exposure was a plausible access path, while separate suspicious IAM activity could not be definitively linked to the compromise.

Jul 9, 2026
Threat Research · thehackernews.com

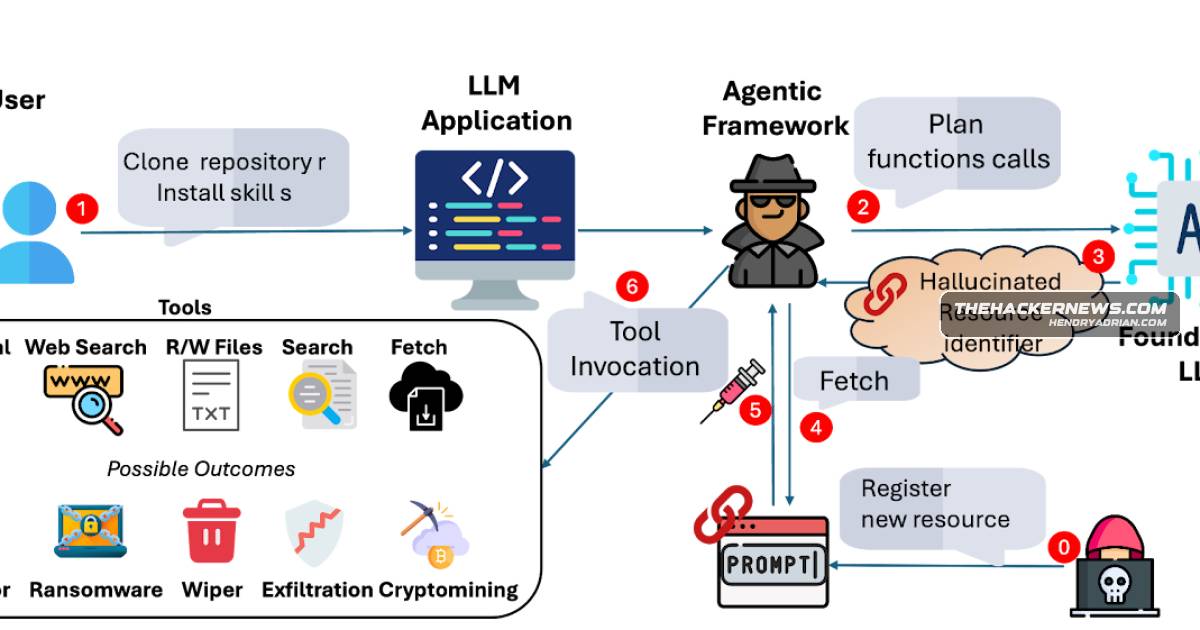
HalluSquatting Uses AI-Coding Assistant Hallucinations to Deliver Attacker Code

Researchers report that attackers could register names hallucinated by AI coding assistants and use hidden instructions to make agents run code. Tests used harmless placeholders, but the technique could enable botnet delivery.

Jul 8, 2026
Threat Research · socket.dev

Malicious Go Module Reveals 222-Repository GitHub Malware Lure Network

Socket Dev Research details a malicious Go module and a 222-repository GitHub lure network across 190 accounts, tracing a hidden PowerShell staging chain to Windows RAT and infostealer activity. The Go security team blocked the module.

Jul 8, 2026
Threat Research · opensourcemalware.com

PolinRider Supply-Chain Campaign Spreads Through Go and Packagist Repositories

Researchers say the DPRK-linked PolinRider campaign used compromised GitHub accounts to distribute malicious code through Go modules and Packagist, where repository access can enable releases. They describe its techniques and recommend auditing repositories and securing

Jul 8, 2026
Threat Research · securityweek.com

China-Linked UAT-7810 Adds Three Backdoors to LapDogs Arsenal

Talos details UAT-7810’s LongLeash, DogLeash, and JarLeash backdoors, their capabilities and deployment, and infrastructure linked to the LapDogs espionage campaign targeting routers.

Jul 8, 2026
PreviousPage 45 of 100 Next
© 2026 cyber.hendryadrian.com