
eSentire Details DEV#POPPER and OmniStealer Supply-Chain Attack
Summary
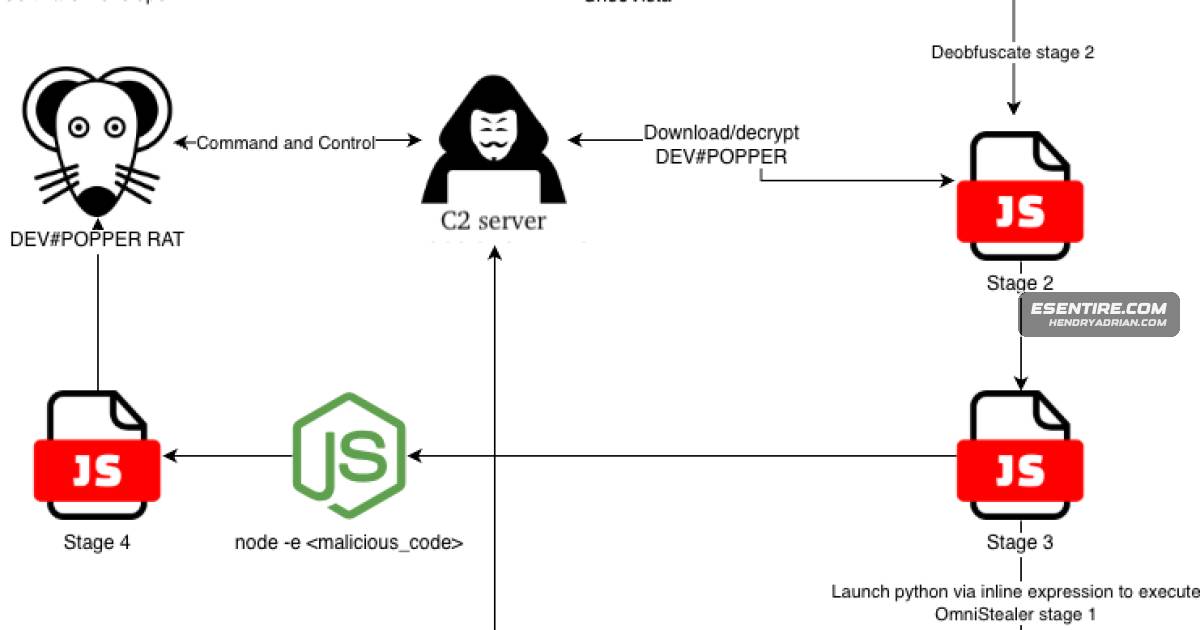
eSentire’s TRU analyzed malware deployed through the ShoeVista GitHub repository, detailing DEV#POPPER and OmniStealer’s staged execution, persistence, and theft of developer credentials and cryptocurrency data.
Key points
- Launching the weaponized ShoeVista repository triggered an obfuscated Node.js backdoor hidden in frontend/tailwind.config.js.
- The multi-stage chain retrieved DEV#POPPER and OmniStealer payloads from command-and-control servers and blockchain transaction data.
- DEV#POPPER used obfuscation and anti-analysis techniques, including RC4-encrypted strings, debugger disruption, and sandbox and cloud-environment checks.
- The RAT could persist by injecting stager code into Node.js applications, including VS Code, GitHub Desktop, and Discord, across macOS, Windows, and Linux.
- OmniStealer targeted browser and cryptocurrency-wallet data, Git credentials, system keychains, environment variables, and cloud-storage artifacts; collected data was archived and exfiltrated over HTTP or Telegram.
- eSentire attributed the campaign with high confidence to a North Korean state-sponsored APT, citing shared TTPs; its analysts isolated the affected customer host.
- eSentire released DEV#STOPPER.js and a YARA rule, and recommended auditing untrusted repositories, isolating development environments, and blocking crypto-network APIs used for staging.
Article Details
- Attack Vectors
- A weaponized GitHub repository named ShoeVista, disguised as an eCommerce project, triggered the attack when the victim launched its frontend.
- The frontend loaded an obfuscated Node.js backdoor from frontend/tailwind.config.js, which fetched additional stages from C2 servers and decrypted and executed them.
- DEV#POPPER retrieved its RAT source code from blockchain transaction data; its stagers also retrieved the OmniStealer payload from C2 infrastructure.
- DEV#POPPER established persistence by injecting stager code into JavaScript files used by Node.js applications, including Visual Studio Code, GitHub Desktop, Discord, Cursor, and Antigravity.
- DEV#POPPER and OmniStealer collected browser credentials and cookies, wallet data, Git credentials, keychain and credential-store data, clipboard contents, and environment variables, then archived and exfiltrated the data.
- Defensive Notes
- Block crypto-network APIs used by the threat actors for payload staging.
- Verify repository authenticity and audit code from untrusted sources before execution; isolate development environments.
- Use hardware wallets for cryptocurrency, store secrets in hardware security keys or password managers with strong 2FA, and do not store seed phrases on disk.
- Implement phishing and security awareness training using real-world scenarios.
- Use a 24/7 Managed Detection and Response provider for threat hunting and rapid response.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 136[.]0[.]9[.]8 | Additional C2 address identified in DEV#POPPER samples. |
| IPV4 | 198[.]105[.]127[.]210 | Campaign-specific C2 address selected by DEV#POPPER based on its campaign identifier. |
| IPV4 | 23[.]27[.]20[.]143 | C2 and staging server used by Stage 2 to retrieve the next payload stage. |
| IPV4 | 23[.]27[.]202[.]27 | Additional C2 address identified in DEV#POPPER samples. |
| URL | hxxp[:]//23[.]27[.]20[.]143:27017/$/boot | Specific C2 URL used by Stage 2 to retrieve the encrypted next stage. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationDEV#POPPER used obfuscated JavaScript, shuffled and encoded strings, RC4 encryption, and encrypted payload stages.T1041 · Exfiltration Over C2 ChannelHarvested data was exfiltrated to C2 over HTTP, with Telegram used as a fallback.T1059.006 · PythonPython stagers retrieved and executed OmniStealer code, including through inline python execution.T1059.007 · JavaScriptThe Node.js stagers and DEV#POPPER RAT executed JavaScript, including code retrieved from C2 and blockchain transaction data.T1071.001 · Web ProtocolsDEV#POPPER used HTTP requests for C2 stage retrieval and data transfer.T1105 · Ingress Tool TransferStagers retrieved additional payload stages and a portable Python archive from C2 servers.T1115 · Clipboard DataDEV#POPPER collected clipboard contents using OS-specific commands on Windows, macOS, and Linux.T1195.002 · Compromise Software Supply ChainThe attack used the weaponized ShoeVista software repository as a supply-chain lure for developers.T1204.002 · Malicious FileThe infection began when the victim launched the frontend application from the cloned ShoeVista repository.T1497.001 · System ChecksThe malware checked system attributes for analysis environments, including cloud, CI/CD, container, and sandbox environments.T1555.001 · KeychainOmniStealer targeted the macOS Keychain database.T1555.003 · Credentials from Web BrowsersOmniStealer collected passwords, cookies, and other data from Chromium-based browsers and Firefox.T1555.004 · Windows Credential ManagerOmniStealer collected credentials stored in Windows Credential Manager.T1560.001 · Archive via UtilityOmniStealer placed collected data in a password-protected ZIP archive before exfiltration.T1622 · Debugger EvasionThe malware used debugger-crashing behavior and checks that could cause debugging or beautified code execution to hang.
Malware
DEV#POPPERGitHub repository named “ShoeVista” deployed highly obfuscated Node.js and Python stagers to retrieve DEV#POPPER RAT and the OmniStealer payloads from blockchain transactions and remote C2 servers.OmniStealer“ShoeVista” deployed highly obfuscated Node.js and Python stagers to retrieve DEV#POPPER RAT and the OmniStealer payloads from blockchain transactions and remote C2 servers.
Products
Antigravityinternally make use of Node.js including, Visual Studio Code, GitHub Desktop, Discord, Cursor, and Antigravity.Cursorapplications that internally make use of Node.js including, Visual Studio Code, GitHub Desktop, Discord, Cursor, and Antigravity.DiscordPersistence is achieved by injecting stager code into Node.js applications (e.g., VS Code, GitHub Desktop, Discord) so the stager executes when those apps launch across macOS, Windows, and Linux.GitHubeSentire TRU analyzed a multi-stage supply-chain attack where a weaponized GitHub repository named “ShoeVista” deployed highly obfuscated Node.js and Python stagers to retrieve DEV#POPPER RAT and the OmniStealerGitHub DesktopPersistence is achieved by injecting stager code into Node.js applications (e.g., VS Code, GitHub Desktop, Discord) so the stager executes when those apps launch across macOS, Windows, and Linux.Mozilla FirefoxFirefox passwords, history, cookies.Node.jssupply-chain attack where a weaponized GitHub repository named “ShoeVista” deployed highly obfuscated Node.js and Python stagers to retrieve DEV#POPPER RAT and the OmniStealer payloads from blockchain transactionsPythonattack where a weaponized GitHub repository named “ShoeVista” deployed highly obfuscated Node.js and Python stagers to retrieve DEV#POPPER RAT and the OmniStealer payloads from blockchain transactions and remoteVSCodefiles belonging to many different applications that internally make use of Node.js including, Visual Studio Code, GitHub Desktop, Discord, Cursor, and Antigravity.
Tools
CensysCensys QueryCyberChefFigure 26 – Exfiltrated environment variables (URL decoded in CyberChef)DEV#STOPPER.jsAPT—focused on developer-targeted credential and crypto-wallet theft; eSentire published tooling (DEV#STOPPER.js), detection guidance, and remediation recommendations.YARAautomation tooling (DEV#STOPPER.js) to deobfuscate intermediary stagers and final payloads, provided Yara detection for the initial stager, and issued operational recommendations (block crypto APIs, audit repos,