
Google Details Coruna iOS Exploit Kit and Its Use by Multiple Actors
Summary
Google GTIG analyzed Coruna, an iOS exploit kit with five exploit chains and 23 exploits targeting iOS 13 through 17.2.1. Its PLASMAGRID payload targets cryptocurrency information, and GTIG recommends updating iOS or enabling Lockdown Mode.
Key points
- GTIG recovered five exploit chains containing 23 exploits targeting iPhones running iOS 13.0 through 17.2.1; some used non-public techniques and mitigation bypasses.
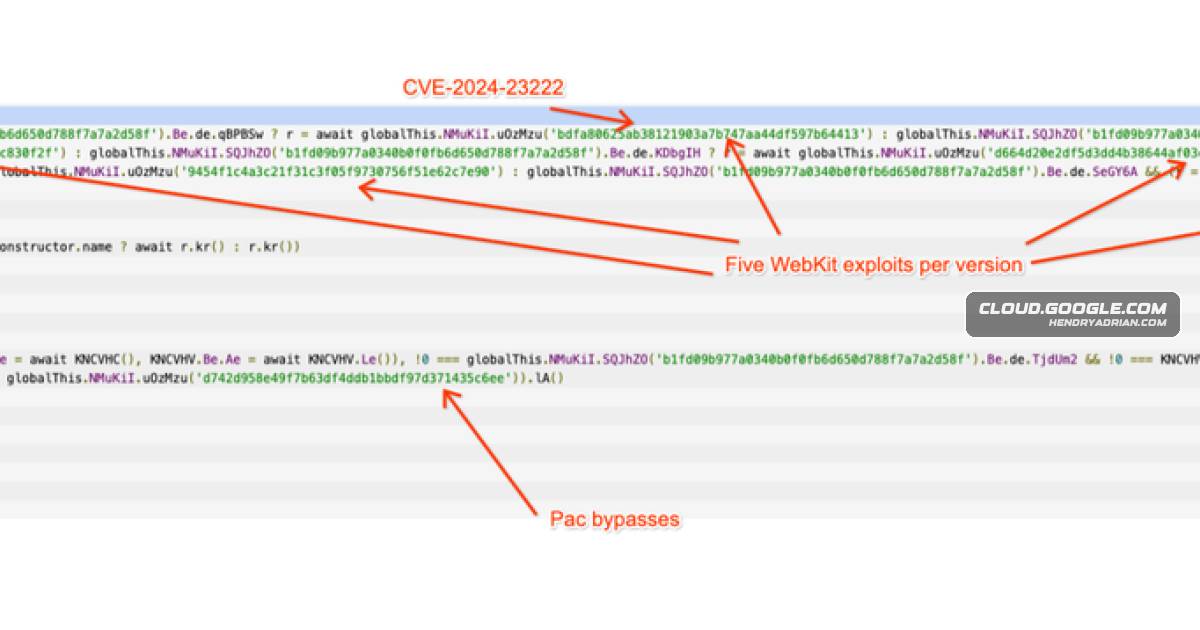
- The kit fingerprints devices to select exploits, including WebKit remote-code-execution exploits, followed by PAC bypasses and other exploit stages.
- GTIG observed Coruna first in operations involving a surveillance-vendor customer, then in watering-hole attacks against Ukrainian sites attributed to UNC6353, and later in scam campaigns attributed to UNC6691.
- The final payload, PLASMAGRID, injects into the root-running iOS process powerd and can collect cryptocurrency-related information, including QR codes and wallet data.
- PLASMAGRID can fetch additional modules and uses encrypted communications, hard-coded command-and-control servers, and a fallback domain-generation algorithm.
- GTIG added identified sites and domains to Safe Browsing and published YARA rules and indicators to aid detection.
- GTIG says the kit does not work against the latest iOS version and recommends updating; it advises enabling Lockdown Mode if updating is not possible.
Article Details
- Attack Vectors
- Coruna was delivered through hidden iFrames on compromised Ukrainian websites and through fake finance and cryptocurrency websites.
- An obfuscated JavaScript framework fingerprinted iPhone models and iOS versions, then selected and delivered a compatible WebKit remote-code-execution exploit.
- The exploit chains used pointer-authentication-code and other mitigation bypasses, followed by kernel exploitation and a sandbox escape.
- The final payload injected into the root-running powerd process, collected cryptocurrency-related data from device files and apps, and could download additional modules from C2 servers.
- Defensive Notes
- Update iOS to the latest version; the article says Coruna is not effective against the latest iOS version.
- Enable Lockdown Mode if an iOS update is not possible.
- Google added identified websites and domains to Safe Browsing and published YARA rules.
- Google worked with CERT-UA to clean up compromised Ukrainian websites.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 6zvjeulzaw5c0mv[.]xyz | PLASMAGRID C2 domain listed in the article. |
| DOMAIN | ol67el6pxg03ad7[.]xyz | PLASMAGRID C2 domain listed in the article. |
| DOMAIN | rlau616jc7a7f7i[.]xyz | PLASMAGRID C2 domain listed in the article. |
| DOMAIN | vvri8ocl4t3k8n6[.]xyz | PLASMAGRID C2 domain listed in the article. |
| SHA256 | 05b5e4070b3b8a130b12ea96c5526b4615fcae121bb802b1a10c3a7a70f39901 | SHA-256 file indicator listed among the implant and module hashes. |
| SHA256 | 0dff17e3aa12c4928273c70a2e0a6fff25d3e43c0d1b71056abad34a22b03495 | SHA-256 file indicator listed among the implant and module hashes. |
| SHA256 | 10bd8f2f8bb9595664bb9160fbc4136f1d796cb5705c551f7ab8b9b1e658085c | SHA-256 file indicator listed among the implant and module hashes. |
| SHA256 | 18394fcc096344e0730e49a0098970b1c53c137f679cff5c7ff8902e651cd8a3 | SHA-256 file indicator listed among the implant and module hashes. |
| SHA256 | 2a9d21ca07244932939c6c58699448f2147992c1f49cd3bc7d067bd92cb54f3a | SHA-256 hash listed for the PLASMAGRID implant. |
| SHA256 | 42cc02cecd65f22a3658354c5a5efa6a6ec3d716c7fbbcd12df1d1b077d2591b | SHA-256 file indicator listed among the implant and module hashes. |
| SHA256 | 6eafd742f58db21fbaf5fd7636e6653446df04b4a5c9bca9104e5dfad34f547c | SHA-256 hash listed for a delivered module with bundle ID com.bitkeep.os. |
| SHA256 | 91d44c1f62fd863556aac0190cbef3b46abc4cbe880f80c580a1d258f0484c30 | SHA-256 file indicator listed among the implant and module hashes. |
| URL | hxxp[:]//cdn[.]uacounter[.]com/stat[.]html | URL used to deliver Coruna in watering-hole attacks attributed to UNC6353. |
| URL | hxxp[:]//ddus17[.]com/tuiliu/group[.]html | URL listed as delivering the Coruna exploit kit in UNC6691 campaigns. |
| URL | hxxp[:]//pepeairdrop01[.]com/static/analytics[.]html | URL listed as delivering the Coruna exploit kit in UNC6691 campaigns. |
| URL | hxxps[:]//3v5w1km5gv[.]xyz/group[.]html | Scam-site URL where the article reports recovering a Coruna exploit. |
| URL | hxxps[:]//ai-scorepredict[.]com/static/analytics[.]html | URL identified as delivering Coruna in campaigns attributed to UNC6691. |
| URL | hxxps[:]//goodcryptocurrency[.]top/details/group[.]html | URL listed as delivering the Coruna exploit kit in UNC6691 campaigns. |
| URL | hxxps[:]//ios[.]teegrom[.]top/tuiliu/group[.]html | URL listed as delivering the Coruna exploit kit in UNC6691 campaigns. |
| URL | hxxps[:]//m[.]pc6[.]com/test/tuiliu/group[.]html | URL listed as delivering the Coruna exploit kit in UNC6691 campaigns. |
| URL | hxxps[:]//osec2[.]668ddf[.]cc/tuiliu/group[.]html | URL listed as delivering the Coruna exploit kit in UNC6691 campaigns. |
| URL | hxxps[:]//sj9ioz3a7y89cy7[.]xyz/list[.]html | URL listed as delivering the Coruna exploit kit in UNC6691 campaigns. |
MITRE ATT&CK
T1005 · Data from Local SystemThe payload read images and Apple Memos on the device to find QR codes, BIP39 phrases, and other sensitive information.T1041 · Exfiltration Over C2 ChannelThe implant encrypted collected data and POSTed it over HTTPS to C2.T1055 · Process InjectionThe final payload injected into powerd, a process running as root on iOS.T1059.007 · JavaScriptThe exploit delivery and loader framework used heavily obfuscated JavaScript.T1203 · Exploitation for Client ExecutionCoruna selected and delivered WebKit remote-code-execution exploits based on the fingerprinted iPhone model and iOS version.T1483 · Domain Generation AlgorithmsThe implant used a custom DGA, seeded with the string “lazarus,” to generate fallback .xyz C2 domains.
CVE
CVE-2022-48503Apple · iOS and iPadOS; Apple · macOS; +3 moreWe collected WebKit RCEs, which included CVE-2024-23222, CVE-2022-48503, and CVE-2023-43000, before the server was shut down.CVE-2023-43000Apple · iOS and iPadOS; Apple · macOS; +1 moreWe collected WebKit RCEs, which included CVE-2024-23222, CVE-2022-48503, and CVE-2023-43000, before the server was shut down.CVE-2024-23222Apple · iOS and iPadOS; Apple · macOS; +3 moreAt that time, we recovered the WebKit RCE delivered to a device running iOS 17.2 and determined it was CVE-2024-23222, a vulnerability previously identified as a zero-day that was addressed by Apple on Jan.
Threat Actors
UNC6353GTIG attributed watering-hole attacks delivering Coruna on compromised Ukrainian websites to UNC6353, described as a suspected Russian espionage group.UNC6691GTIG attributed broad-scale scam campaigns delivering Coruna to UNC6691, described as a financially motivated threat actor operating from China.
Malware
Vendors
Products
Apple Memoswallet data and backup phrases (‘the payload can decode QR codes from images on disk’ and scans Apple Memos for “backup phrase”).iOSGoogle Threat Intelligence Group (GTIG) disclosed the Coruna iOS exploit kit — a commercial-grade package of five full exploit chains and 23 exploits that target iPhone models running iOS 13.0 through 17.2.1 and thatiPhoneiOS exploit kit — a commercial-grade package of five full exploit chains and 23 exploits that target iPhone models running iOS 13.0 through 17.2.1 and that was observed in operations by multiple actors including a
Countries
Industries
CryptocurrencyFinal-stage payload (PlasmaLoader / PLASMAGRID) injects into powerd as root and focuses on stealing cryptocurrency-related information (QR codes, BIP39 phrases, wallet app data) and fetching additional modules from C2eCommerceUkrainian websites, ranging from industrial equipment and retail tools to local services and ecommerce websites.financeAt the end of the year, we identified the JavaScript framework on a very large set of fake Chinese websites mostly related to finance, dropping the exact same iOS exploit kit.Industrial Equipmenta website loaded as a hidden iFrame on many compromised Ukrainian websites, ranging from industrial equipment and retail tools to local services and ecommerce websites.Retailloaded as a hidden iFrame on many compromised Ukrainian websites, ranging from industrial equipment and retail tools to local services and ecommerce websites.