
Cisco Talos Details UAT-9244 Malware Targeting South American Telecoms
Summary
Cisco Talos reports that UAT-9244 has targeted South American telecom providers since 2024 using three malware families. Its research details their deployment and capabilities, and provides indicators of compromise for defenders.
Key points
- Cisco Talos reports UAT-9244 activity targeting South American telecom providers since 2024, involving Windows, Linux, and network-edge devices.
- Talos tracks UAT-9244 as a distinct cluster, while associating its tooling, TTPs, and victimology with FamousSparrow and Tropic Trooper. Researchers found no solid link to Salt Typhoon.
- TernDoor is a Windows backdoor deployed through DLL side-loading; it can execute commands, manage files, collect system information, and establish persistence.
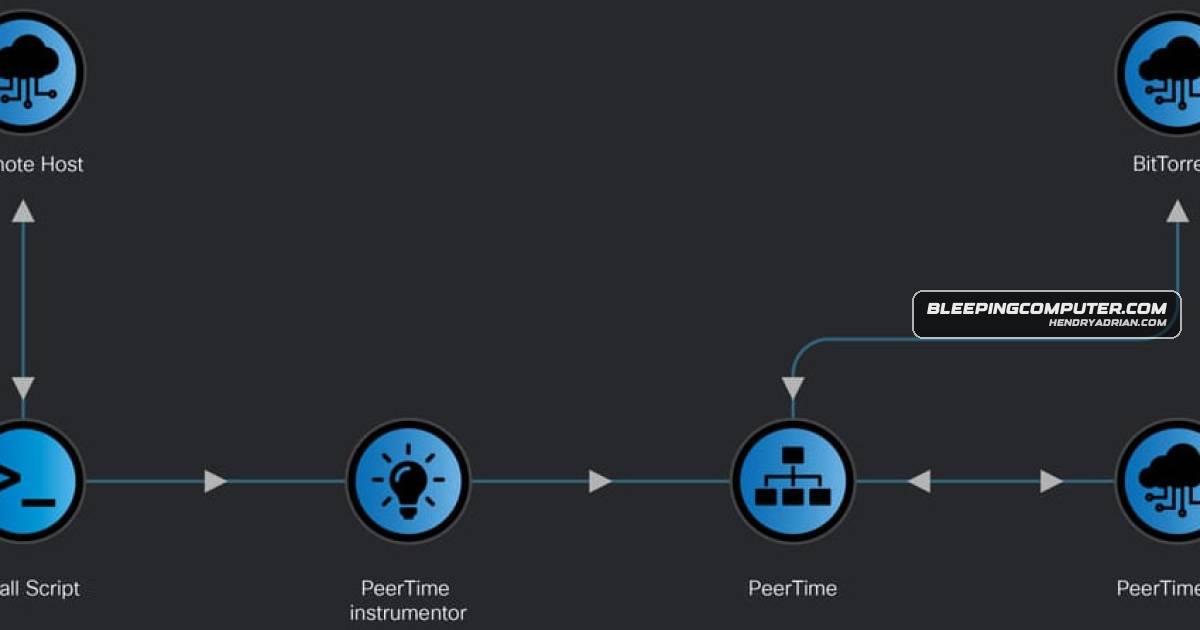
- PeerTime is a multi-architecture Linux backdoor that uses BitTorrent for command-and-control and can download and execute payloads from peers.
- BruteEntry turns compromised devices into scanning nodes that brute-force SSH, Postgres, and Tomcat; it sends login-attempt results to command-and-control.
- Cisco Talos published indicators of compromise associated with the observed activity to help defenders detect and block it.
Article Details
- Attack Vectors
- TernDoor is deployed through DLL side-loading: wsprint.exe loads malicious code from BugSplatRc64.dll, which decrypts and executes a payload injected into msiexec.exe.
- TernDoor establishes persistence with scheduled tasks and Windows Registry modifications.
- PeerTime compromises Linux and network-edge devices, decrypts and loads its payload in memory, and uses BitTorrent for peer-to-peer command-and-control and payload delivery.
- BruteEntry uses compromised devices as scanning nodes to brute-force access to SSH, Postgres, and Tomcat; it reports attempt results and task information to command-and-control.
- Defensive Notes
- Cisco Talos published indicators of compromise associated with the UAT-9244 activity for defenders to use to detect and block attacks.
MITRE ATT&CK
T1036.005 · Match Legitimate Resource Name or LocationPeerTime renames its process to make it appear legitimate.T1046 · Network Service DiscoveryBruteEntry uses compromised devices to scan for targets and brute-force SSH, Postgres, and Tomcat.T1053.005 · Scheduled TaskTernDoor establishes persistence through scheduled tasks and modifies them to hide the task.T1055 · Process InjectionTernDoor injects its decrypted final payload into msiexec.exe.T1059 · Command and Scripting InterpreterTernDoor can execute commands through a remote shell.T1071 · Application Layer ProtocolPeerTime uses the BitTorrent protocol for peer-to-peer command-and-control communications.T1090 · ProxyBruteEntry turns compromised devices into scanning nodes described as Operational Relay Boxes, building proxy infrastructure.T1105 · Ingress Tool TransferPeerTime downloads and executes payloads from peers.T1110.001 · Password GuessingBruteEntry performs brute-force login attempts against SSH, Postgres, and Tomcat.T1112 · Modify RegistryTernDoor modifies the Windows Registry as part of persistence and to hide its scheduled task.T1574.002 · DLL Side-LoadingTernDoor is deployed by having wsprint.exe load malicious code from BugSplatRc64.dll.
Threat Actors
FamousSparrowCisco Talos tracks UAT-9244 as a distinct activity cluster targeting South American telecommunications providers since 2024 and compromising Windows, Linux, and network-edge devices.Tropic TrooperCisco Talos assesses UAT-9244 as closely associated with Tropic Trooper based on similarities in tooling, TTPs, and victimology; it tracks UAT-9244 as a separate cluster.
Malware
BruteEntryCisco Talos links the campaign to three new malware families—TernDoor, PeerTime, and BruteEntry—and published technical details and IoCs to help defenders.PeerTimeCisco Talos links the campaign to three new malware families—TernDoor, PeerTime, and BruteEntry—and published technical details and IoCs to help defenders.TernDoorCisco Talos links the campaign to three new malware families—TernDoor, PeerTime, and BruteEntry—and published technical details and IoCs to help defenders.
Products
BusyBoxPeerTime, an ELF-based peer-to-peer (P2P) backdoor, uses the BitTorrent protocol for command-and-control (C2) communications, downloads and executes payloads from peers, and uses BusyBox to write the files on the host.LinuxUAT-9244, a China-linked APT, has been targeting telecommunication service providers in South America since 2024, compromising Windows, Linux, and network-edge devices.Microsoft WindowsUAT-9244, a China-linked APT, has been targeting telecommunication service providers in South America since 2024, compromising Windows, Linux, and network-edge devices.PostgreSQLBruteEntry turns compromised hosts into scanning ORBs to brute-force SSH, Postgres, and Tomcat, reporting results back to C2; Cisco Talos published IoCs for detection.TomcatBruteEntry turns compromised hosts into scanning ORBs to brute-force SSH, Postgres, and Tomcat, reporting results back to C2; Cisco Talos published IoCs for detection.