
Check Point Details Silver Dragon Espionage Campaign and GearDoor Backdoor
Summary
Check Point Research describes Silver Dragon, a Chinese-nexus actor assessed with high confidence and showing tradecraft overlap with APT41, targeting organizations in Southeast Asia and Europe since mid-2024 with three infection chains and a Google Drive-based .NETバックド
Key points
- Check Point Research says Silver Dragon has targeted government and other high-profile organizations in Southeast Asia and Europe since mid-2024.
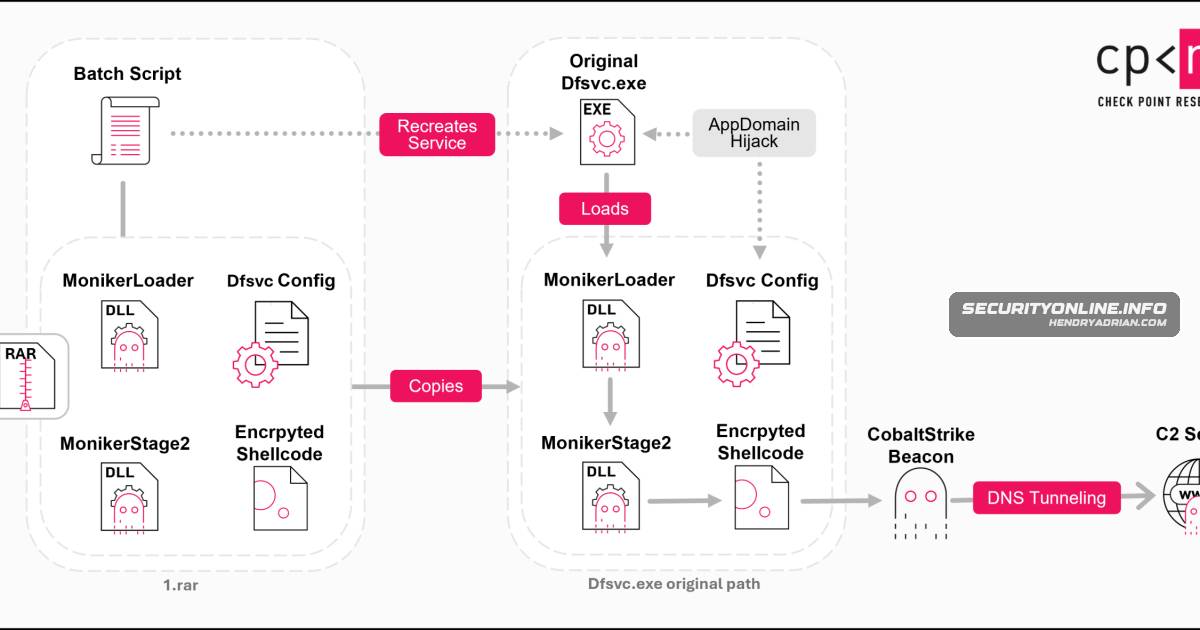
- The reported infection chains use exposed-server exploitation, AppDomain hijacking with malicious .NET DLLs, and spear-phishing LNK files to deliver Cobalt Strike.
- GearDoor uses Google Drive for file-based command-and-control: .png heartbeats, .cab command files, and encrypted .zip uploads for exfiltrated data.
- SliverScreen captures screenshots and uses grayscale thumbnail comparisons to detect changes; SSHcmd supports remote command execution and file transfers.
- MonikerLoader and BamboLoader are described as obfuscated loaders that decrypt and execute shellcode in memory.
- Check Point assesses the actor as Chinese-nexus with high confidence, citing APT41 tradecraft overlap, UTC+8 timestamps, and RC4 decryption followed by LZNT1 decompression.
Article Details
- Attack Vectors
- Exploitation of vulnerable, internet-exposed servers to gain an initial foothold.
- AppDomain hijacking using malicious .NET DLLs and encrypted modules delivered in compressed archives.
- Spear-phishing with malicious LNK attachments that embed a payload and execute hidden PowerShell code.
MITRE ATT&CK
T1021.004 · SSHSSHcmd wraps SSH to facilitate remote command execution on remote systems.T1027 · Obfuscated Files or InformationMonikerLoader and BamboLoader are described as heavily obfuscated loaders.T1059.001 · PowerShellThe malicious LNK files reportedly trick users into executing hidden PowerShell code.T1102.002 · Bidirectional CommunicationGearDoor uses Google Drive for file-based command-and-control, including heartbeat, command, and response files.T1113 · Screen CaptureSliverScreen reportedly captures screenshots across displays on infected systems.T1140 · Deobfuscate/Decode Files or InformationMonikerLoader and BamboLoader reportedly decrypt payloads before executing shellcode in memory.T1190 · Exploit Public-Facing ApplicationSilver Dragon reportedly gains an initial foothold by exploiting vulnerable, internet-exposed servers.T1204.002 · Malicious FileThe LNK infection chain relies on victims executing shortcut files containing the next-stage payload.T1566.001 · Spearphishing AttachmentThe group reportedly uses spear-phishing messages with malicious LNK attachments.T1567.002 · Exfiltration to Cloud StorageGearDoor reportedly encrypts files exfiltrated from infected hosts and uploads them to Google Drive as .zip files.
Threat Actors
Silver DragonCheck Point Research attributes espionage activity against government and high-profile organizations across Southeast Asia and Europe to Silver Dragon, with high confidence assessing it as a Chinese-nexus actor.SPIRE CASTLEThe article says Silver Dragon is believed to operate under APT41's umbrella and cites tradecraft overlaps; this relationship is presented as an assessment, not confirmed attribution.
Malware
Products
Cobalt StrikeThe group delivers Cobalt Strike through three infection chains and operates GearDoor, a .NET backdoor that uses Google Drive for file-based C2, enabling heartbeats, command execution, and data exfiltration.Google DriveThe group delivers Cobalt Strike through three infection chains and operates GearDoor, a .NET backdoor that uses Google Drive for file-based C2, enabling heartbeats, command execution, and data exfiltration.
Tools
BamboLoaderOperators deploy post-exploitation tools such as SliverScreen, SSHcmd, MonikerLoader, and BamboLoader for monitoring and lateral movement.MonikerLoaderOperators deploy post-exploitation tools such as SliverScreen, SSHcmd, MonikerLoader, and BamboLoader for monitoring and lateral movement.SliverScreenOperators deploy post-exploitation tools such as SliverScreen, SSHcmd, MonikerLoader, and BamboLoader for monitoring and lateral movement.SSHcmdOperators deploy post-exploitation tools such as SliverScreen, SSHcmd, MonikerLoader, and BamboLoader for monitoring and lateral movement.
Countries
ChinaTemporal Alignment: “Metadata analysis across multiple samples revealed compilation and file-creation timestamps that consistently align with UTC+8 (China Standard Time)”.UzbekistanSpear-Phishing Campaigns: More recently, Silver Dragon has targeted victims—particularly in Uzbekistan—with malicious LNK attachments.