
Malicious Packagist Packages Deliver RAT Through Laravel Dependencies
Summary
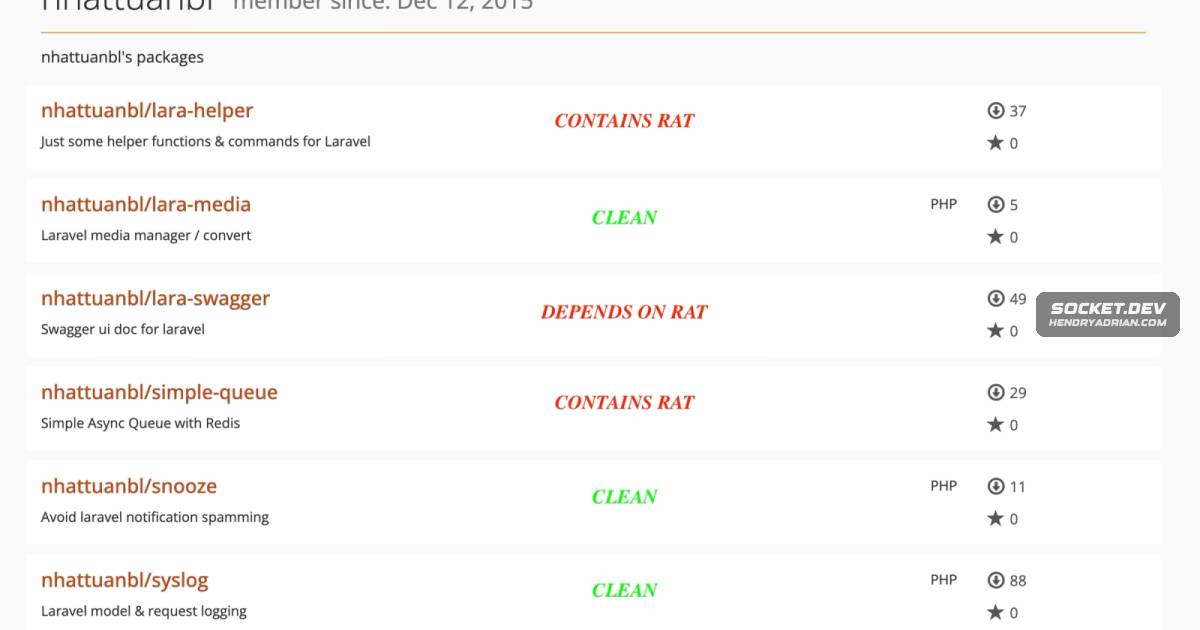
Socket researchers found an obfuscated PHP RAT in Packagist packages nhattuanbl/lara-helper and nhattuanbl/simple-queue, with nhattuanbl/lara-swagger pulling it in transitively. It enables remote commands and file access; affected users should remove packages and rotate
Key points
- Socket researchers found byte-identical RAT payloads in nhattuanbl/lara-helper and nhattuanbl/simple-queue, packages published under the Packagist account nhattuanbl.
- nhattuanbl/lara-swagger contains no malicious code itself but declares lara-helper as a dev-master dependency, pulling in the RAT when installed.
- The payload activates through Laravel boot-time service-provider loading or PHP class autoloading, then launches a detached background process.
- It sends system reconnaissance to helper[.]leuleu[.]net:2096 over raw TCP using AES-128-CTR and supports shell and PowerShell commands, file transfer, and screen capture.
- The report says the C2 host was not responding at publication, but the payload retries every 15 seconds; the packages were still live despite takedown requests.
- Socket recommends treating affected hosts as compromised, rotating accessible secrets, removing the packages and payload, and auditing outbound traffic.
Article Details
- Attack Vectors
- The Packagist packages nhattuanbl/lara-helper and nhattuanbl/simple-queue contain an identical RAT payload in src/helper.php.
- nhattuanbl/lara-swagger has no malicious code itself, but its dev-master dependency on nhattuanbl/lara-helper installs the RAT transitively.
- The payload is activated when the application boots through Laravel service-provider auto-discovery or when PHP autoloads a class from simple-queue; it then launches a detached background process.
- The payload uses layered obfuscation, including goto-based control flow, encoded strings, and randomized identifiers.
- The RAT connects over raw TCP to helper[.]leuleu[.]net on port 2096 using AES-128-CTR, sends system reconnaissance, and accepts remote shell, PowerShell, file upload/download, and screen-capture commands.
- Defensive Notes
- Treat hosts that installed lara-helper or simple-queue as compromised; remove the packages and helper.php, and rotate secrets accessible to the application.
- Delete the RAT's lock file at {sys_get_temp_dir}/wvIjjnDMRaomchPprDBzzVSpzh61RCar.lock and check for files uploaded with permissions set to 0777.
- Audit outbound traffic to helper[.]leuleu[.]net:2096. The article reports that the C2 host was not responding at publication time, but the RAT continues retrying and may be redirected.
- Review transitive dependencies as well as direct installs, and treat dev-master constraints as high risk in production because they bypass version pinning.
- Flag packages that load non-Composer PHP files unconditionally at application boot or autoload time.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | helper[.]leuleu[.]net | C2 domain contacted by the RAT for commands and data exchange; the article reports communication over port 2096. |
nhattuanbl@gmail[.]com | Registered email associated with the Packagist account that published the packages containing the RAT. | |
| SHA256 | a493ce9509c5180e997a04cab2006a48202afbb8edfa15149a4521067191ead7 | SHA-256 hash of the malicious src/helper.php payload found in lara-helper and simple-queue. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe PHP payload uses goto-based control flow, hex/octal string encoding, and randomized identifiers to resist static analysis.T1041 · Exfiltration Over C2 ChannelThe RAT sends system reconnaissance and command results over its encrypted C2 connection.T1059.001 · PowerShellThe RAT supports executing PowerShell commands on Windows hosts.T1059.004 · Unix ShellThe RAT executes operator-supplied shell commands and returns their output.T1105 · Ingress Tool TransferThe malicious PHP payload is delivered inside packages installed into affected applications.T1113 · Screen CaptureThe RAT can capture the host screen and return the image as base64-encoded PNG.T1195.001 · Compromise Software Dependencies and Development ToolsThe RAT was distributed in malicious Packagist packages, including through lara-swagger's dependency on nhattuanbl/lara-helper.T1571 · Non-Standard PortThe RAT communicates with its C2 server over TCP port 2096.
Threat Actors
Products
LaravelActivation occurs at application boot via a Laravel service provider (auto-discovery) or immediately on autoload (class file include), and the payload self-launches as a detached background process to run the RAT loop.nhattuanbl/lara-helpermultiple Packagist PHP packages published by the account nhattuanbl, with identical payloads in nhattuanbl/lara-helper and nhattuanbl/simple-queue and a transitive vector via nhattuanbl/lara-swagger.nhattuanbl/lara-swaggerpayloads in nhattuanbl/lara-helper and nhattuanbl/simple-queue and a transitive vector via nhattuanbl/lara-swagger.nhattuanbl/simple-queuepublished by the account nhattuanbl, with identical payloads in nhattuanbl/lara-helper and nhattuanbl/simple-queue and a transitive vector via nhattuanbl/lara-swagger.