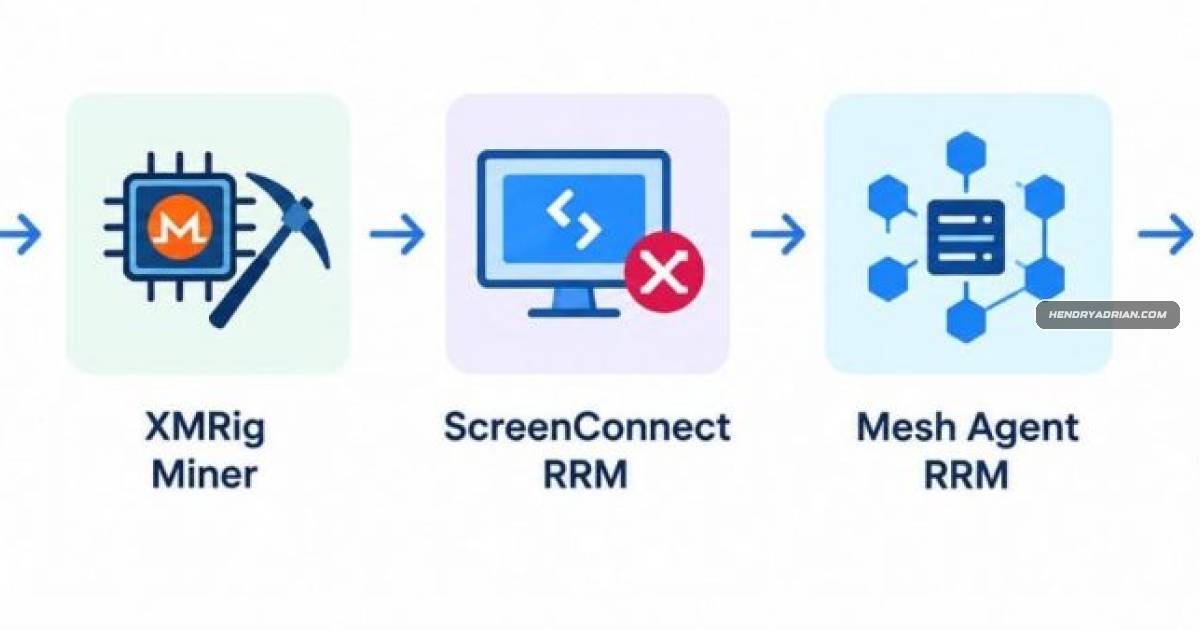
KMS Auto Abuse Led to Mining, Remote Access Tools and Ransomware-Themed Scareware; APT36 Link Unconfirmed
K7 Labs describes a multi-stage intrusion beginning with KMS Auto, followed by XMRig, ScreenConnect, MeshAgent and scareware that did not encrypt files. APT36/Transparent Tribe attribution remains inconclusive.