
ClearSky Moderately Attributes BadPaw and MeowMeow Campaign Targeting Ukraine to APT28
Summary
ClearSky details a phishing campaign targeting Ukrainian entities with BadPaw and MeowMeow, including HTA delivery, sandbox checks, scheduled-task persistence and backdoor capabilities; it attributes the activity to APT28 with moderate confidence.
Key points
- Phishing emails sent from ukr[.]net link to a ZIP archive containing a Ukrainian-language HTA lure.
- The HTA drops a decoy government document and checks the operating system’s installation age, aborting if it is under ten days old.
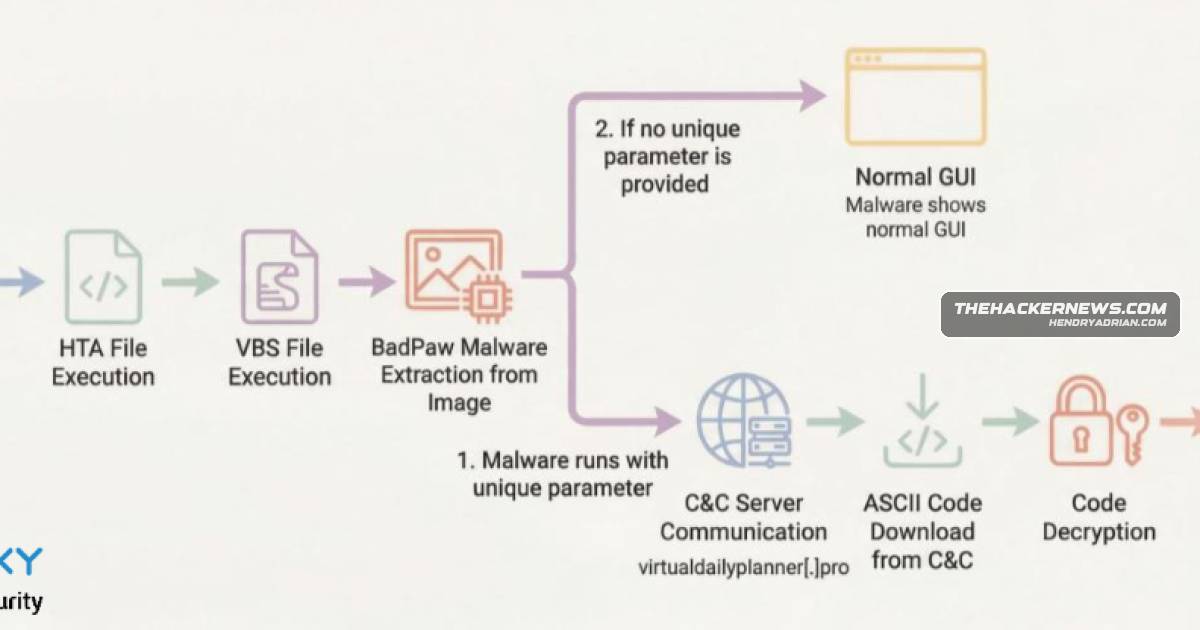
- The HTA extracts a VBScript and PNG containing BadPaw loader code, then creates a scheduled task for persistence.
- BadPaw is a .NET loader that contacts a command-and-control server to download and deploy the MeowMeow backdoor.
- MeowMeow activates with a specific parameter, checks for sandbox and monitoring tools, and supports remote PowerShell commands and file operations.
- ClearSky attributes the campaign to APT28 with moderate confidence, citing targeting, lures and technique overlaps; Russian-language strings are also reported.
Article Details
- Attack Vectors
- Phishing emails sent from ukr[.]net linked victims to a ZIP archive containing a Ukrainian-language HTA lure.
- Launching the HTA dropped a decoy document and initiated follow-on stages, including a VBScript and a PNG containing embedded malicious code.
- The VBScript extracted the BadPaw loader, which contacted a remote server to download and deploy the MeowMeow backdoor.
- Defensive Notes
- The HTA checked the Windows InstallDate registry value and aborted if the operating system was less than ten days old.
- The malware created a scheduled task to execute the VBScript.
- MeowMeow checked for sandbox execution and for running analysis or monitoring tools, including Wireshark, Procmon, Ollydbg, and Fiddler.
MITRE ATT&CK
T1012 · Query RegistryThe HTA queried the Windows Registry InstallDate value to assess the system's age.T1053.005 · Scheduled TaskThe HTA created a scheduled task to execute the extracted VBScript for persistence.T1057 · Process DiscoveryMeowMeow checked whether named forensic and monitoring tools were running in the background.T1059.001 · PowerShellMeowMeow could remotely execute PowerShell commands on the compromised host.T1105 · Ingress Tool TransferBadPaw contacted a remote server to download additional components, including MeowMeow.T1204.002 · Malicious FileThe attack chain required the victim to launch the HTA file extracted from the ZIP archive.T1497.001 · System ChecksThe malware checked the system's age and whether it was running in a sandbox or on an actual endpoint.T1566.002 · Spearphishing LinkThe phishing email linked to a ZIP archive used to deliver the HTA lure.
Threat Actors
Malware
BadPawResearchers disclosed a Russian-linked campaign targeting Ukrainian entities that uses phishing emails and HTA lures to deploy two previously undocumented malware families, BadPaw and MeowMeow.MeowMeowResearchers disclosed a Russian-linked campaign targeting Ukrainian entities that uses phishing emails and HTA lures to deploy two previously undocumented malware families, BadPaw and MeowMeow.
Products
Tools
Fiddleras opposed to a sandbox, and no forensic and monitoring tools like Wireshark, Procmon, Ollydbg, and Fiddler are running in the background.OllyDbgactual endpoint as opposed to a sandbox, and no forensic and monitoring tools like Wireshark, Procmon, Ollydbg, and Fiddler are running in the background.Procmonon an actual endpoint as opposed to a sandbox, and no forensic and monitoring tools like Wireshark, Procmon, Ollydbg, and Fiddler are running in the background.Wiresharkit’s running on an actual endpoint as opposed to a sandbox, and no forensic and monitoring tools like Wireshark, Procmon, Ollydbg, and Fiddler are running in the background.