
Check Point Details Silver Dragon Campaigns and Custom Malware
Summary
Check Point Research details Silver Dragon campaigns against government and other high-profile organizations in Southeast Asia and Europe, describing infection chains, custom tools and C2. It assesses Chinese-nexus ties and a likely APT41 connection.
Key points
- Researchers describe three infection chains—AppDomain hijacking, service DLL deployment and phishing with weaponized LNK files—that delivered Cobalt Strike beacons.
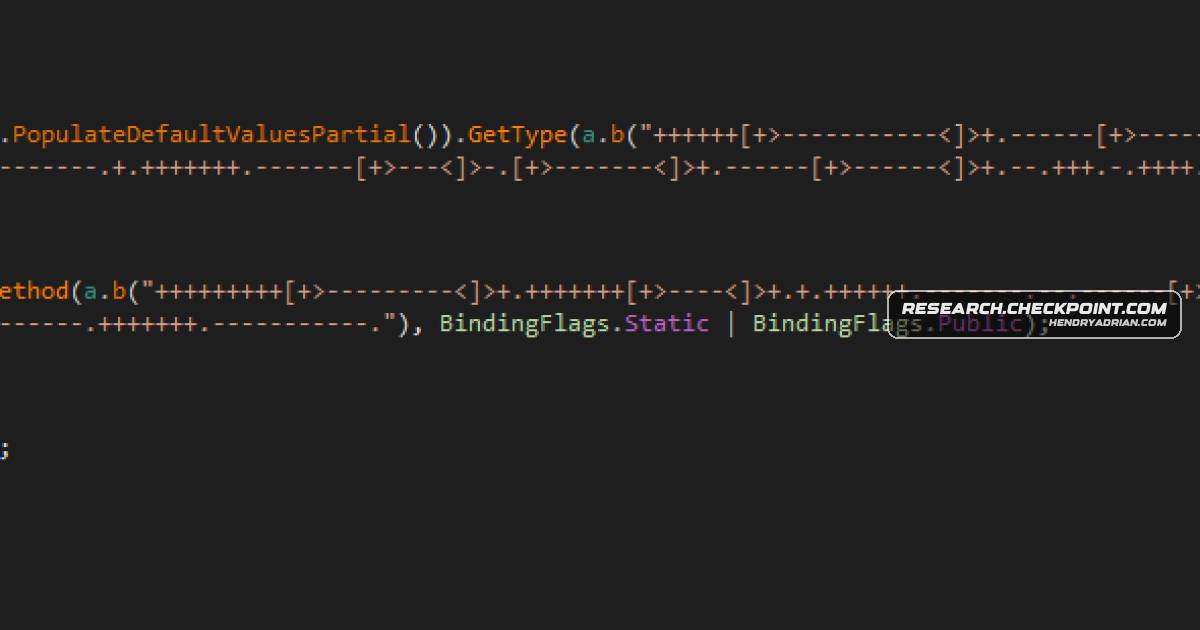
- BamboLoader decrypts and decompresses staged payloads before injecting them into Windows processes; MonikerLoader uses obfuscated strings and in-memory execution.
- GearDoor uses Google Drive for file-based C2, including command delivery and file transfer; the researchers also describe its encryption and tasking mechanisms.
- Silver Dragon’s reported toolset includes SilverScreen, which captures screenshots, and SSHcmd, which supports remote command execution and file transfer.
- Observed C2 methods include DNS tunneling, HTTP, SMB and Google Drive; the report also details service hijacking and other persistence techniques.
- Check Point assesses the activity as Chinese-nexus and likely within the APT41 umbrella, citing similarities in service-registration scripts, Cobalt Strike watermarks, loader patterns and timestamps.
Article Details
- Attack Vectors
- Silver Dragon gained initial access by exploiting publicly exposed vulnerable servers.
- Phishing emails, observed primarily in a campaign targeting Uzbekistan, carried weaponized LNK attachments containing embedded payloads that were extracted and run using PowerShell.
- A phishing-chain executable, GameHook.exe, was abused to DLL-side-load BamboLoader.
- AppDomain hijacking used a malicious dfsvc.exe.config to redirect execution to MonikerLoader.
- BamboLoader was registered as a Windows service to maintain persistence; the report also describes service DLL persistence involving legitimate Windows services.
- Observed command-and-control channels included DNS tunneling, HTTP, SMB between compromised hosts, and file-based communication through Google Drive.
- GearDoor could upload files from infected hosts to Google Drive; SilverScreen captured and stored screenshots for later collection or exfiltration.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | ampolice[.]org | Listed in the report as a Silver Dragon C2 domain. |
| DOMAIN | bigflx[.]net | Listed in the report as a Silver Dragon C2 domain. |
| DOMAIN | copilot-cloud[.]net | Listed in the report as a Silver Dragon C2 domain. |
| DOMAIN | drivefrontend[.]pa-clients[.]workers[.]dev | Listed in the report as a Silver Dragon C2 domain. |
| DOMAIN | exchange4study[.]com | Listed as a C2 domain and used in Cobalt Strike configuration. |
| DOMAIN | mindssurpass[.]com | Listed in the report as a Silver Dragon C2 domain. |
| DOMAIN | oicm[.]org | Listed in the report as a Silver Dragon C2 domain. |
| DOMAIN | onedriveconsole[.]com | Listed as a C2 domain and used in Cobalt Strike configuration. |
| DOMAIN | protacik[.]com | Listed in the report as a Silver Dragon C2 domain. |
| DOMAIN | revitpourtous[.]com | Listed in the report as a Silver Dragon C2 domain. |
| DOMAIN | splunkds[.]com | Listed in the report as a Silver Dragon C2 domain. |
| DOMAIN | wikipedla[.]blog | Listed in the report as a Silver Dragon C2 domain. |
| DOMAIN | zhydromet[.]com | Listed in the report as a Silver Dragon C2 domain. |
| SHA256 | 166e777cb72a7c4e126f8ed97e0a82e7ca9e87df7793fea811daf34e1e7e47a6 | Phishing LNK sample hash listed in the report's indicators. |
| SHA256 | 2f787c1454891b242ab221b8b8b420373c3eb0a1c1fdcb624dd800c50758bbb0 | MonikerLoader stage 2 sample hash listed in the report's indicators. |
| SHA256 | 3128bdb8efaaa04c0ba96337252f4cc2dc795021cbc410f74ace9dde958bac1d | BamboLoader sample hash listed in the report's indicators. |
| SHA256 | 43f8f94ca5aa0af7bfb0cc1d2f664a46500a161b2d082b48b516d084ef485348 | BamboLoader sample hash listed in the report's indicators. |
| SHA256 | 44e769efed3e4f9f04c52dcd13f15cead251a1a08827a2cb6ea68427522c7fbb | SilverScreen sample hash listed in the report's indicators. |
| SHA256 | 4f93be0c46a53701b1777ab8df874c837df3d8256e026f138d60fc2932e569a8 | GearDoor sample hash listed in the report's indicators. |
| SHA256 | 51684a0e356513486489986f5832c948107ff687c8501d64846cdc4307429413 | Phishing LNK sample hash listed in the report's indicators. |
| SHA256 | 5341c7256542405abdd01ee288b08e49dcb6d1782be6b7bea63b459d80f9a8f5 | MonikerLoader sample hash listed in the report's indicators. |
| SHA256 | 5ad857df8976523cb3ad2fdf30e87c0e7daa64135716b139ffdcd209b98e1654 | MonikerLoader sample hash listed in the report's indicators. |
| SHA256 | 740a09fcdefa5a5f79355b720f54ff09efa64062229fb388adbccd9c829e9ff0 | MonikerLoader sample hash listed in the report's indicators. |
| SHA256 | 7f89a4d5af47bc00a9ad58f0bcbe8a7be2662953dcd03f0e881cc5cbf6b7bca8 | GearDoor sample hash listed in the report's indicators. |
| SHA256 | 85a03d2e74ae84093a74699057693d11e5c61f85b62e741778cbc5fc9f89022f | SilverScreen sample hash listed in the report's indicators. |
| SHA256 | 948468aba5c851952ebe56a5bf37904ed83a6c8cb520304db6938d79892f0a1b | Phishing LNK sample hash listed in the report's indicators. |
| SHA256 | 967b5c611d304385807ea2d865fa561c15cde0473dd63e768679a4f29f0e4563 | BamboLoader sample hash listed in the report's indicators. |
| SHA256 | b93560c4d18120e113fb8b04a8aa05f66a12116d1fbf18a93186f6314381e97e | BamboLoader sample hash listed in the report's indicators. |
| SHA256 | bcbe2f0a8134c0e7fce18d0394ababc1d910e6f7b77b8c07643434cd14f4c5d6 | SSHcmd sample hash listed in the report's indicators. |
| SHA256 | e3b016f2fc865d0f53f635f740eb0203626517425ed9a2908058f96a3bcf470d | BamboLoader sample hash listed in the report's indicators. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationMonikerLoader obfuscated strings with a Brainfuck-based routine; the report also describes extensive obfuscation in BamboLoader.T1053.005 · Scheduled TaskGearDoor's exec command could run commands through a scheduled task mechanism.T1055 · Process InjectionBamboLoader injected decrypted payloads into Windows processes such as taskhost.exe.T1059.001 · PowerShellThe LNK payload invoked PowerShell to extract embedded components and execute the next stage.T1059.003 · Windows Command ShellThe LNK chain launched cmd.exe, which invoked PowerShell.T1071.001 · Web ProtocolsSome Cobalt Strike implants used HTTP-based communication, including servers protected behind Cloudflare.T1071.004 · DNSCobalt Strike beacons used DNS tunneling for command-and-control communication.T1102 · Web ServiceGearDoor used Google Drive for file-based command-and-control, exchanging commands, heartbeats, and results.T1134.001 · Token Impersonation/TheftSilverScreen used token impersonation to relaunch in the active desktop session, and GearDoor supported stealing a process token.T1190 · Exploit Public-Facing ApplicationThe report says Silver Dragon gained initial access by exploiting publicly exposed vulnerable servers.T1543.003 · Windows ServiceThe operators registered BamboLoader as a Windows service and recreated legitimate service entries for persistence.T1566.001 · Spearphishing AttachmentPhishing emails delivered weaponized LNK attachments that embedded payload components.T1567.002 · Exfiltration to Cloud StorageGearDoor encrypted files taken from infected hosts and uploaded them to Google Drive.T1574.001 · DLLThe phishing chain used GameHook.exe to sideload the BamboLoader DLL.T1574.014 · AppDomainManagerA malicious dfsvc.exe.config redirected execution to MonikerLoader through AppDomain hijacking.
Threat Actors
Silver DragonCheck Point Research identifies Silver Dragon as the cluster behind campaigns targeting organizations in Southeast Asia and Europe, using exploited public-facing servers, phishing, custom malware, and Cobalt Strike.SPIRE CASTLEThe report assesses Silver Dragon as likely operating within the APT41 umbrella, citing tradecraft similarities and Cobalt Strike overlaps; it presents this relationship as likely rather than conclusive.
Malware
BamboLoaderThe group leverages custom tooling and persistence techniques — notably GearDoor (Google Drive C2), BamboLoader/MonikerLoader, SilverScreen and SSHcmd — and conducts C2 via DNS tunneling, Cloudflareâprotected HTTP,GearDoorThe group leverages custom tooling and persistence techniques — notably GearDoor (Google Drive C2), BamboLoader/MonikerLoader, SilverScreen and SSHcmd — and conducts C2 via DNS tunneling, Cloudflareâprotected HTTP,MonikerLoaderleverages custom tooling and persistence techniques — notably GearDoor (Google Drive C2), BamboLoader/MonikerLoader, SilverScreen and SSHcmd — and conducts C2 via DNS tunneling, Cloudflareâprotected HTTP, and GoogleSilverScreentooling and persistence techniques — notably GearDoor (Google Drive C2), BamboLoader/MonikerLoader, SilverScreen and SSHcmd — and conducts C2 via DNS tunneling, Cloudflareâprotected HTTP, and Google Drive.
Products
Google DriveThe group leverages custom tooling and persistence techniques — notably GearDoor (Google Drive C2), BamboLoader/MonikerLoader, SilverScreen and SSHcmd — and conducts C2 via DNS tunneling, Cloudflareâprotected HTTP,Microsoft WindowsPersistence and stealth techniques include AppDomain hijacking, hijacking legitimate Windows services (service DLL registration), heavy string obfuscation (Brainfuckâbased), and process injection into legitimate host
Tools
Cobalt Strikein Southeast Asia and Europe that use exploited publicâfacing servers and phishing to deliver Cobalt Strike.SSHcmdpersistence techniques — notably GearDoor (Google Drive C2), BamboLoader/MonikerLoader, SilverScreen and SSHcmd — and conducts C2 via DNS tunneling, Cloudflareâprotected HTTP, and Google Drive.