
Huntress Reconstructs RDP-to-DLL-Sideloading Intrusion Linked to MuddyWater
Summary
Huntress reconstructs an intrusion at an Israeli customer involving RDP access, SSH tunnels and DLL side-loading. The activity aligns with reporting on MuddyWater, but the attribution is not stated as confirmed.
Key points
- Huntress found the activity in historical data from a customer incident report dated January 24, 2026; the customer was an Israeli company.
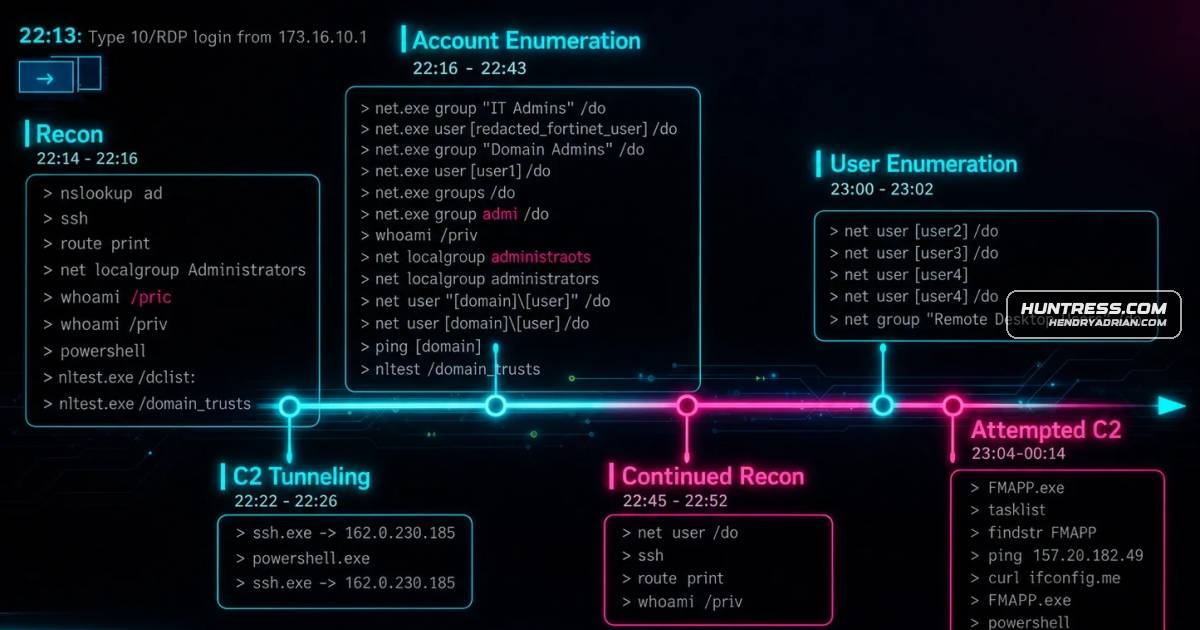
- The attacker gained endpoint access through RDP, then established SSH tunnels using remote forwarding.
- The attacker used reconnaissance commands and opened a fresh PowerShell session before re-establishing a tunnel.
- A legitimate Fortemedia FMAPP.exe loaded a malicious FMAPP.dll, which Huntress says communicated with a C2 IP address.
- The attacker checked whether FMAPP.exe was running, pinged the C2 address and queried ifconfig[.]me.
- Huntress says detections and response interrupted the continued activity; the observed techniques align with reporting on MuddyWater.
Article Details
- Attack Vectors
- Initial access through a Terminal Services/RDP login.
- The attacker established SSH reverse tunnels to the endpoint using OpenSSH.
- DLL side-loading: the legitimate FMAPP.exe loaded a malicious FMAPP.dll from the same folder for C2 communications.
- Defensive Notes
- Monitor for unexpected inbound RDP logins and subsequent SSH reverse-tunnel activity.
- Detect legitimate FMAPP.exe loading an unexpected FMAPP.dll, and investigate the DLL's network connections.
- Review endpoint process activity for suspicious PowerShell and command-line reconnaissance, including account and group enumeration.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 157[.]20[.]182[.]49 | C2 IP address contacted by the malicious FMAPP.dll. |
| IPV4 | 162[.]0[.]230[.]185 | IP address used as the SSH tunnel endpoint during the intrusion. |
| SHA256 | 589ecb0bb31adc6101b9e545a4e5e07ae2e97d464b0a62242a498e613a7740b6 | SHA-256 hash identified for the malicious DLL used for C2. |
MITRE ATT&CK
T1016 · System Network Configuration DiscoveryThe attacker queried ifconfig.me to check the victim machine's public IP address.T1033 · System Owner/User DiscoveryThe attacker ran whoami to identify the current account context.T1059.001 · PowerShellThe attacker used PowerShell sessions during the intrusion.T1087.001 · Local AccountThe attacker ran whoami and attempted local account and group enumeration.T1133 · External Remote ServicesThe intrusion gained initial access through a Terminal Services/RDP login.T1572 · Protocol TunnelingThe attacker established SSH reverse tunnels to the compromised endpoint.T1574.002 · DLL Side-LoadingThe legitimate FMAPP.exe loaded a malicious FMAPP.dll from the same folder.
People
Threat Actors
Vendors
Products
FMAPP.dllThe attack involved RDP initial access, establishing an SSH tunnel, and deploying malware via DLL side-loading using the legitimate FMAPP.exe to load a malicious FMAPP.dll for C2 communications.FMAPP.exeThe attack involved RDP initial access, establishing an SSH tunnel, and deploying malware via DLL side-loading using the legitimate FMAPP.exe to load a malicious FMAPP.dll for C2 communications.