cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1554 articles

Vulnerability & Exploit · bleepingcomputer.com

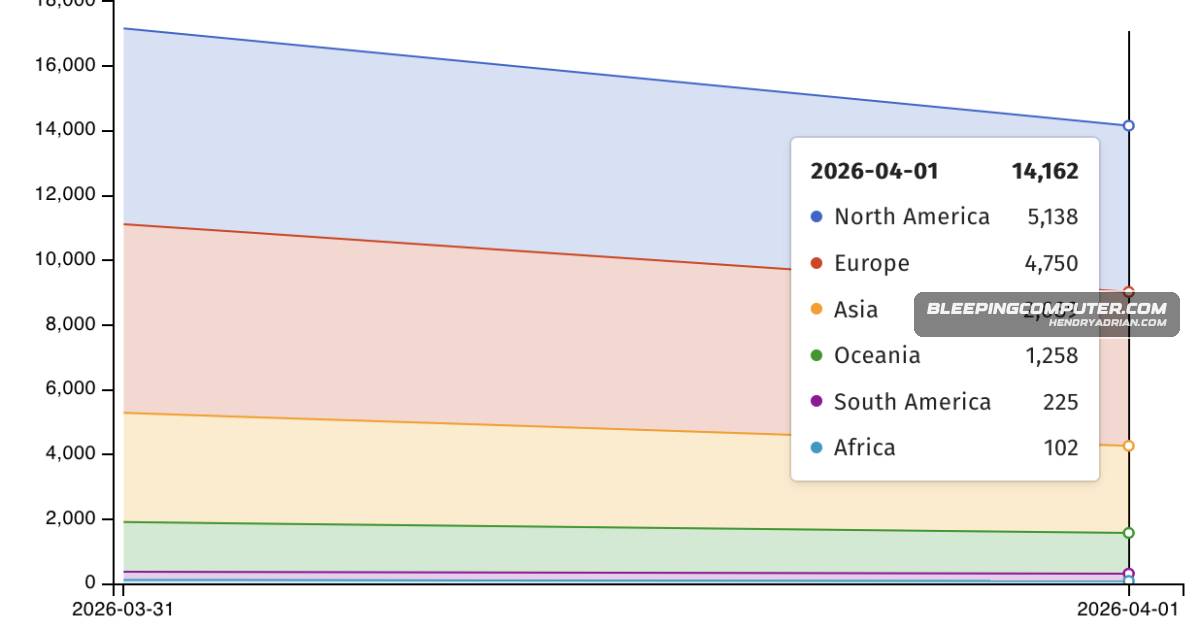
Over 14,000 F5 BIG-IP APM Instances Exposed Amid CVE-2025-53521 Attacks

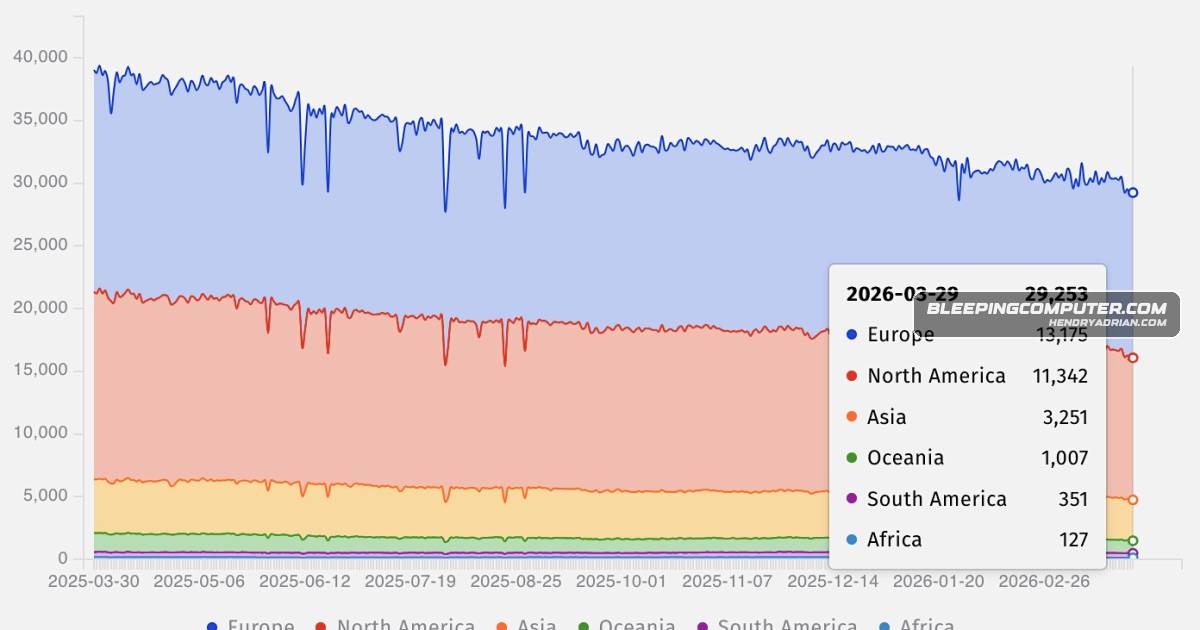
Shadowserver reports over 14,000 BIG-IP APM instances remain exposed amid active exploitation of CVE-2025-53521, recently reclassified as an RCE flaw. F5 advises investigating devices and rebuilding from known-good sources.

Apr 2, 2026
Vulnerability & Exploit · bleepingcomputer.com

TrueConf Zero-Day Exploited to Push Malicious Updates to Connected Clients

Check Point says the TrueChaos campaign exploited CVE-2026-3502 to push malicious updates from compromised on-premises TrueConf servers. Versions 8.1.0–8.5.2 are affected; version 8.5.3 includes a fix.

Apr 1, 2026
Vulnerability & Exploit · hackread.com

CVE-2026-25075 in strongSwan EAP-TTLS Can Crash VPN Services

CVE-2026-25075 is an integer underflow in strongSwan’s EAP-TTLS plugin that researchers say can corrupt memory and crash VPN services. Upgrade to 6.0.5 or later, disable the plugin if unused, or use the non-crashing test tool.

Apr 1, 2026
Vulnerability & Exploit · thecyberexpress.com

Chrome 146 Update Fixes 21 Vulnerabilities, Including Actively Exploited CVE-2026-5281

Google's Chrome Stable update fixes 21 vulnerabilities, including CVE-2026-5281, which the article says is actively exploited. Versions 146.0.7680.177/178 for Windows and Mac and 146.0.7680.177 for Linux are rolling out.

Apr 1, 2026
Vulnerability & Exploit · bleepingcomputer.com

Google Patches Actively Exploited Chrome Zero-Day in Dawn

Google is rolling out emergency Chrome updates for CVE-2026-5281, an actively exploited use-after-free flaw in Dawn (WebGPU). The company has restricted bug details while users receive the fix.

Apr 1, 2026
Vulnerability & Exploit · cert-agid.gov.it

Unauthenticated Codex App-Server Exposure Can Enable Remote Command Execution

The article reports that binding OpenAI’s Codex app-server to 0.0.0.0 without authentication lets remote clients invoke command/exec and run commands. It recommends avoiding public binding and enabling --ws-auth.

Apr 1, 2026
Vulnerability & Exploit · bleepingcomputer.com

File-Open RCE Bugs Found in Vim and GNU Emacs

Opening a crafted file can trigger code execution through Vim’s modeline handling or GNU Emacs’ vc-git integration. Vim fixed its flaw in 9.2.0272; the Emacs issue remains unpatched.

Mar 31, 2026
Vulnerability & Exploit · bleepingcomputer.com

GIGABYTE Control Center flaw allows unauthenticated arbitrary file writes

CVE-2026-4415 affects GIGABYTE Control Center versions 25.07.21.01 and earlier when pairing is enabled. GIGABYTE released version 25.12.10.01 to fix the flaw.

Mar 31, 2026
Vulnerability & Exploit · thehackernews.com

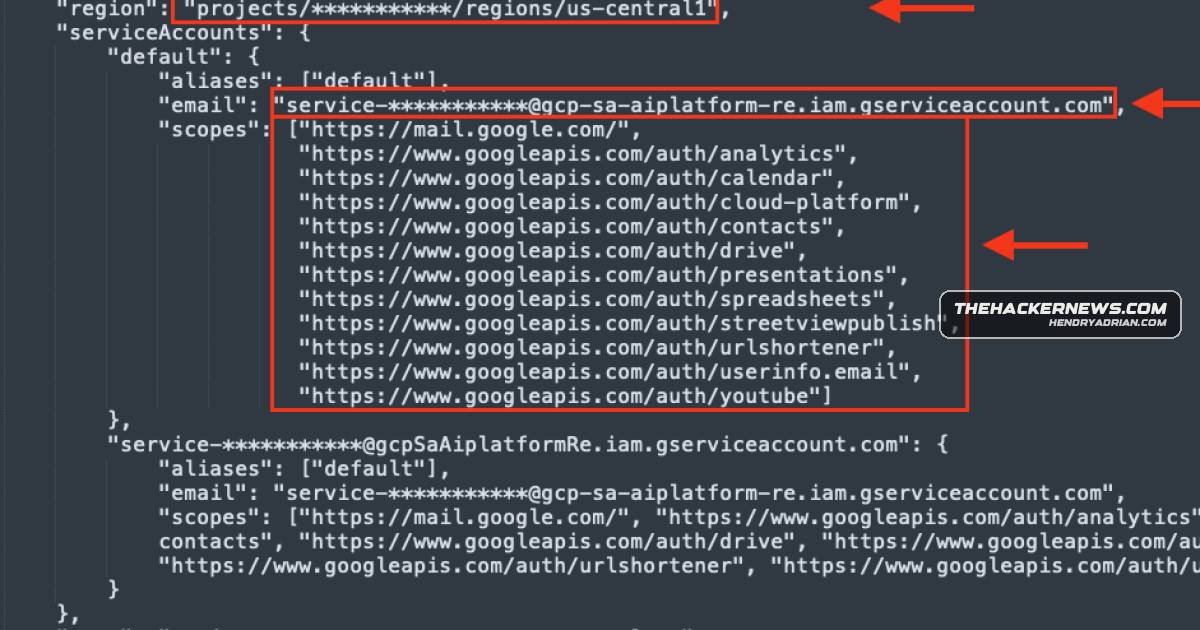
Unit 42 Reports Vertex AI Flaw Exposing Service-Agent Credentials and Cloud Resources

Unit 42 says Vertex AI Agent Engine behavior can expose P4SA credentials, enabling access to customer Cloud Storage data and restricted Google Artifact Registry images. Google updated documentation and recommends BYOSA and least privilege.

Mar 31, 2026
Vulnerability & Exploit · thehackernews.com

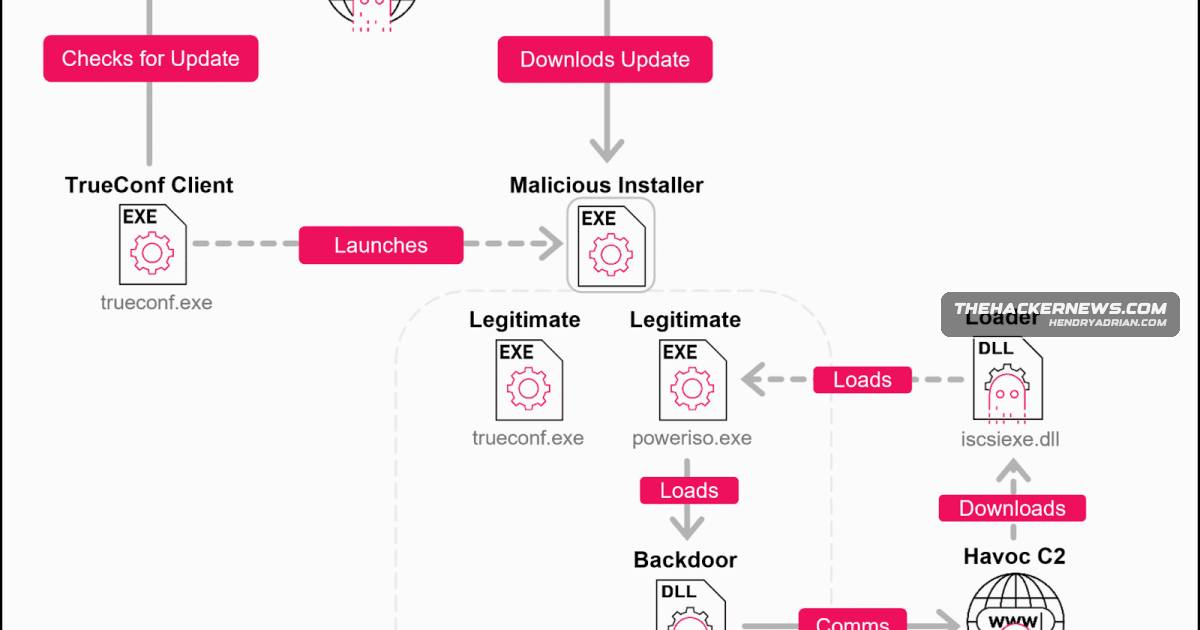
TrueConf Zero-Day Exploited to Target Southeast Asian Government Networks

Check Point says attackers exploited CVE-2026-3502 in TrueConf’s Windows updater to push tampered updates to Southeast Asian government targets. The TrueChaos campaign likely aimed to deploy Havoc; TrueConf fixed the flaw in client v8.5.3.

Mar 31, 2026
Vulnerability & Exploit · securityweek.com

Four CrewAI Vulnerabilities Could Enable Host Code Execution and File Theft

Four CrewAI vulnerabilities involving its Code Interpreter and other tools could be chained to execute code on the host, read files, retrieve internal resources, or steal credentials. No full patch is available; maintainers are working on fixes.

Mar 31, 2026
Vulnerability & Exploit · therecord.media

CISA Orders Federal Agencies to Patch Actively Exploited Citrix NetScaler Flaw

CISA ordered federal agencies to patch CVE-2026-3055 by Thursday after responders reported exploitation. The flaw enables unauthenticated disclosure of sensitive memory in Citrix NetScaler ADCs and was patched March 23.

Mar 31, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Sets April 2 Deadline to Patch Citrix Flaw Reported Exploited in the Wild

CISA added CVE-2026-3055 to its KEV catalog and ordered U.S. civilian agencies to patch by April 2. Watchtowr reported exploitation that could expose admin session IDs; Citrix has not confirmed ongoing attacks.

Mar 31, 2026
Vulnerability & Exploit · bleepingcomputer.com

watchTowr Reports Active Exploitation of Citrix NetScaler CVE-2026-3055

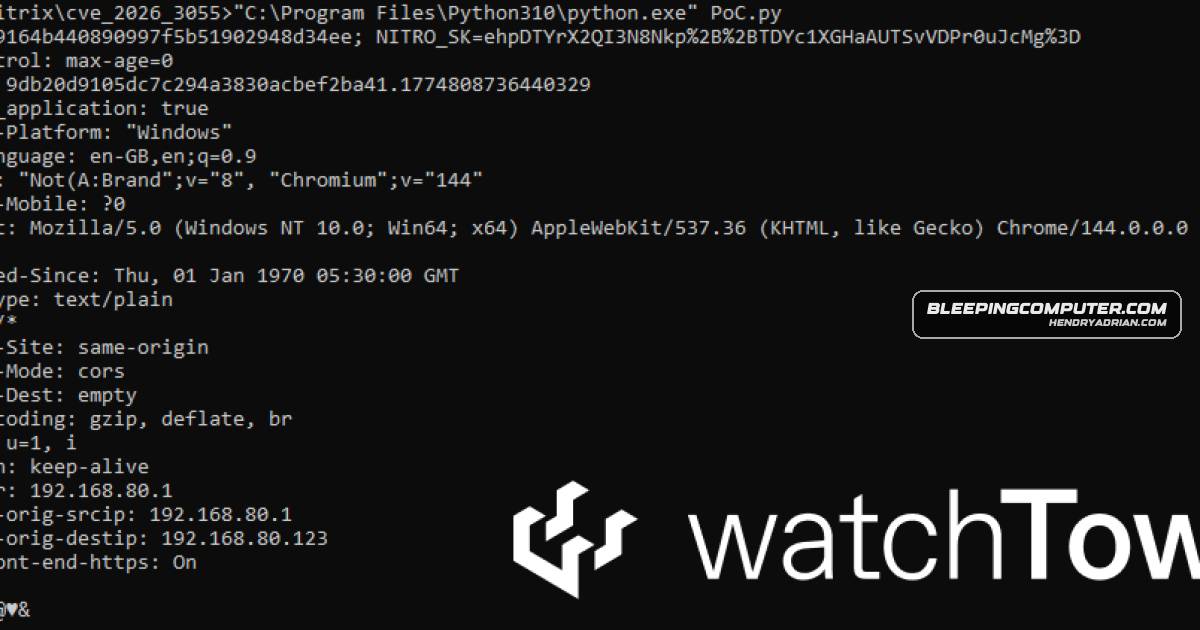
watchTowr reports attackers have exploited CVE-2026-3055 in Citrix NetScaler ADC and Gateway since at least March 27, potentially leaking authentication and administrative session IDs. The flaw affects SAML identity provider-configured appliances.

Mar 30, 2026
Vulnerability & Exploit · bleepingcomputer.com

F5 Warns of Active Exploitation of Critical BIG-IP APM Flaw

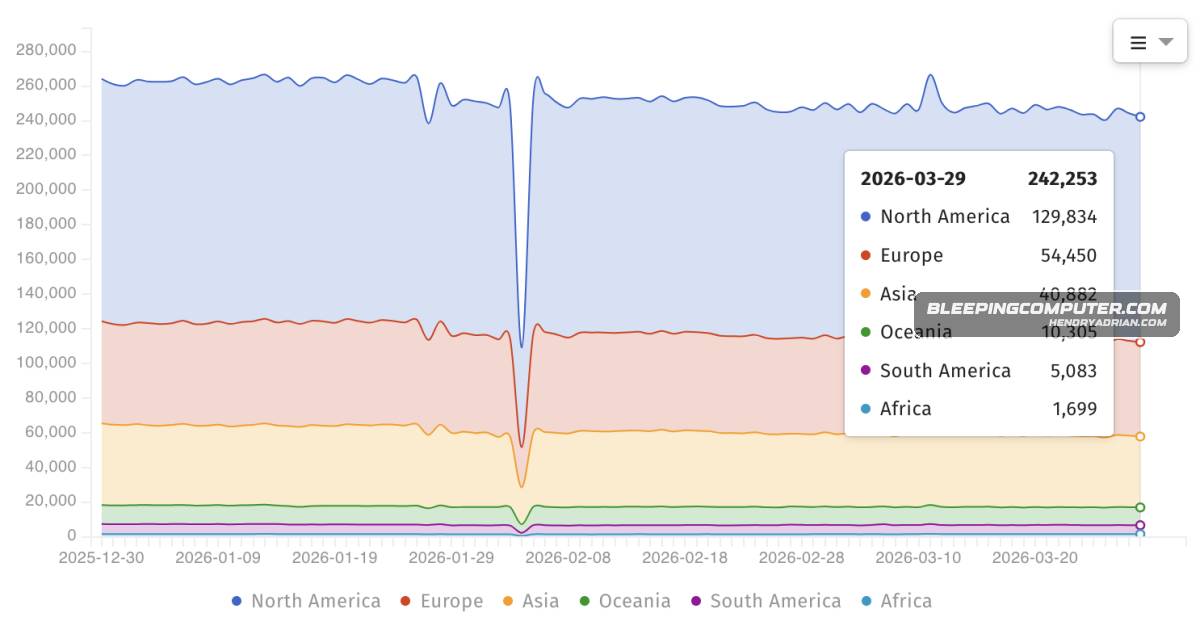
F5 reclassified CVE-2025-53521 as a critical remote code execution flaw and says attackers are exploiting vulnerable BIG-IP APM systems to deploy webshells. CISA urged remediation; Shadowserver tracks over 240,000 exposed instances.

Mar 30, 2026
Vulnerability & Exploit · bleepingcomputer.com

Attackers Reportedly Exploit Critical FortiClient EMS SQL Injection

Defused reports active exploitation of CVE-2026-21643, an unauthenticated SQL injection in FortiClient EMS 7.4.4 that can enable code execution. Fortinet has not confirmed exploitation; upgrading to 7.4.5 or later patches the flaw.

Mar 30, 2026
Vulnerability & Exploit · ncsc.gov.uk

NCSC Urges Immediate Action on Actively Exploited F5 BIG-IP APM Vulnerability

The NCSC warns that CVE-2025-53521, an actively exploited unauthenticated RCE vulnerability affecting BIG-IP APM, may compromise affected systems and urges organisations to isolate, investigate, and rebuild them as needed.

Mar 30, 2026
Vulnerability & Exploit · bleepingcomputer.com

Smart Slider 3 Flaw Exposes Server Files on Vulnerable WordPress Sites

CVE-2026-3098 lets authenticated subscriber-level users read arbitrary server files through Smart Slider 3’s AJAX export function. Version 3.5.1.34 fixes the flaw; the article estimates about 500,000 sites remain vulnerable.

Mar 29, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds F5 BIG-IP APM CVE-2025-53521 to KEV After Exploitation

CISA added CVE-2025-53521 to KEV after active exploitation. F5 confirmed exploitation of vulnerable BIG-IP APM versions, published compromise indicators and fixed releases, and advised FCEB agencies to patch by March 30, 2026.

Mar 28, 2026
Vulnerability & Exploit · thehackernews.com

Citrix NetScaler CVE-2026-3055 Draws Active Reconnaissance

Defused Cyber and watchTowr report reconnaissance targeting Citrix NetScaler CVE-2026-3055, a memory-overread flaw that requires SAML IDP configuration and could expose sensitive information. Affected versions should be patched.

Mar 28, 2026
Vulnerability & Exploit · thehackernews.com

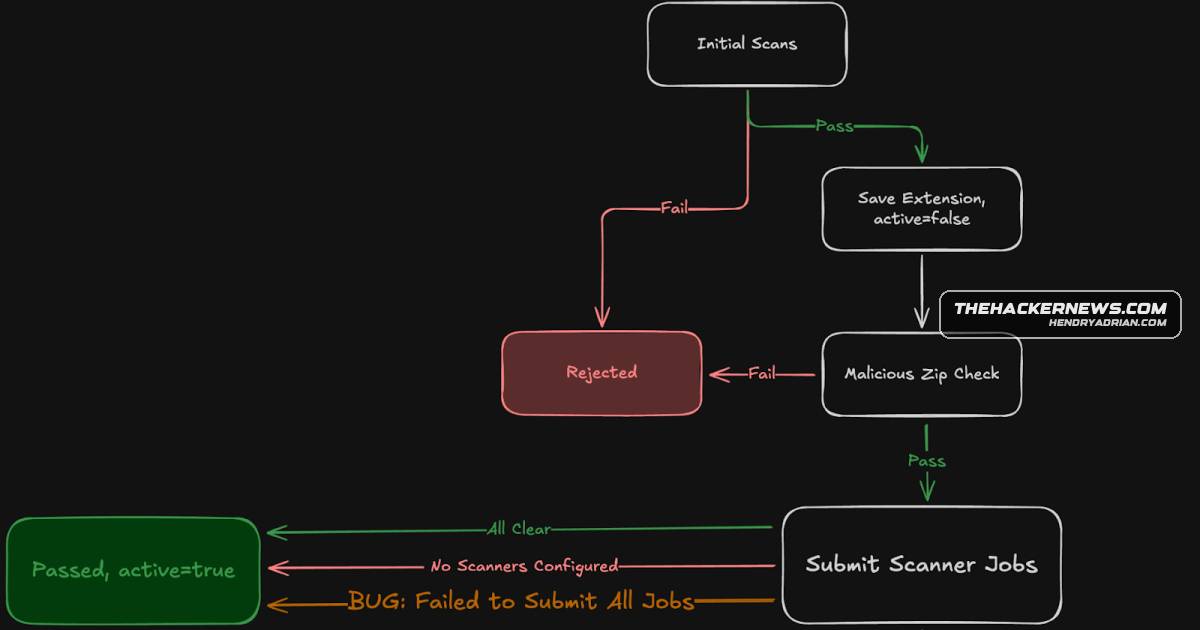
Open VSX Flaw Let Malicious Extensions Bypass Pre-Publish Scanning

A flaw dubbed Open Sesame treated scanner-job failures as no scanners configured, allowing malicious VS Code extensions to bypass Open VSX checks. Flooding the publish endpoint could exhaust database connections; Open VSX fixed the flaw in version 0.32.0.

Mar 27, 2026
Vulnerability & Exploit · securitylabs.datadoghq.com

CVE-2020-8561 Lets Kubernetes API Server SSRF Reveal Full Responses

CVE-2020-8561 combines Kubernetes webhook-based SSRF with API server profiling to expose full responses. Exploitation requires valid credentials and elevated permissions; disabling profiling and limiting network access can reduce risk.

Mar 27, 2026
Vulnerability & Exploit · securityweek.com

CISA Flags Critical PTC Vulnerability as German Police Warn Companies

CVE-2026-4681 is a critical unauthenticated remote code-execution flaw affecting PTC Windchill and FlexPLM. Patches are pending; PTC has shared mitigations and indicators of compromise. Heise reports German police visited companies to warn them.

Mar 27, 2026
Vulnerability & Exploit · thehackernews.com

ShadowPrompt Flaw Let Websites Inject Prompts into Claude Chrome Extension

Researchers reported that ShadowPrompt chained a permissive origin allowlist and a CAPTCHA-component XSS to inject prompts into Claude’s Chrome extension. Anthropic patched the extension, and Arkose Labs fixed the XSS.

Mar 27, 2026
PreviousPage 57 of 65 Next
© 2026 cyber.hendryadrian.com