
F5 Warns of Active Exploitation of Critical BIG-IP APM Flaw
Summary
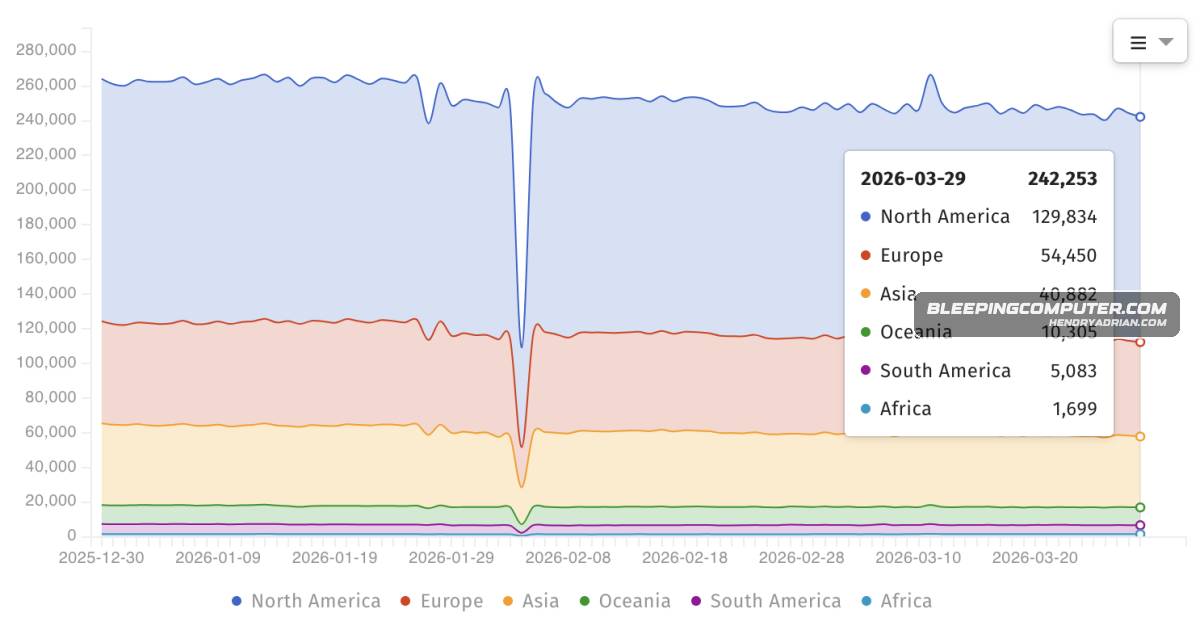
F5 reclassified CVE-2025-53521 as a critical remote code execution flaw and says attackers are exploiting vulnerable BIG-IP APM systems to deploy webshells. CISA urged remediation; Shadowserver tracks over 240,000 exposed instances.
Key points
- F5 reclassified CVE-2025-53521 from a denial-of-service flaw to critical remote code execution after receiving new information in March 2026.
- The flaw can enable unauthenticated remote code execution on BIG-IP APM systems with access policies configured on a virtual server.
- F5 says attackers have exploited vulnerable systems to deploy webshells and published indicators of compromise.
- F5 advises checking affected systems’ disks, logs, and terminal history and following forensic procedures before recovery.
- CISA added the flaw to its actively exploited list and directed federal agencies to secure affected systems by March 30.
- Shadowserver tracks over 240,000 BIG-IP instances exposed online, but the article says it is unknown how many have a vulnerable configuration or are already secured.
Article Details
- Vulnerability Types
- Remote code execution (RCE)
- Severity
- Critical
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available