
Google Patches Actively Exploited Chrome Zero-Day in Dawn
Summary
Google is rolling out emergency Chrome updates for CVE-2026-5281, an actively exploited use-after-free flaw in Dawn (WebGPU). The company has restricted bug details while users receive the fix.
Key points
- Google says it is aware of in-the-wild exploitation of CVE-2026-5281, but has not shared details about the incidents.
- The flaw is a use-after-free vulnerability in Dawn, Chromium’s implementation of WebGPU.
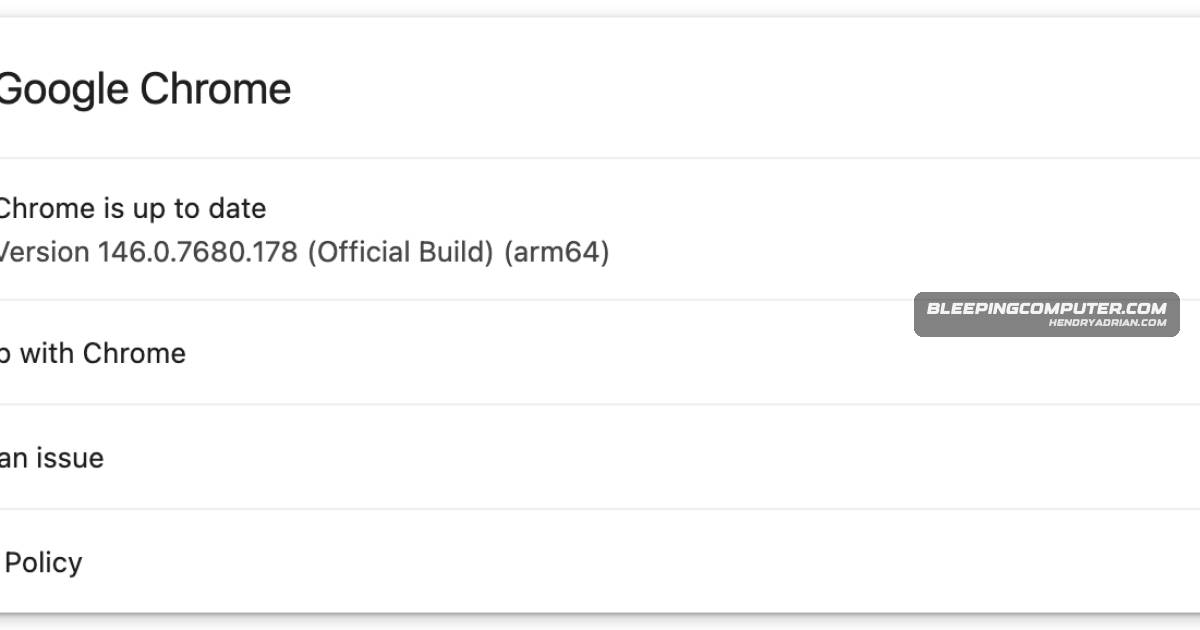
- Google’s out-of-band Stable Desktop update is rolling out for Windows, macOS, and Linux; listed versions include macOS 146.0.7680.177/178 and Linux 146.0.7680.177.
- Google is restricting access to bug details until most users are updated, and may retain restrictions while dependent third-party libraries remain unpatched.
- This is the fourth actively exploited Chrome zero-day Google has patched this year, according to the article.
Article Details
- Vulnerability Types
- Use-after-free
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
CVE
CVE-2026-2441Google · ChromeThis is the fourth actively exploited Chrome zero-day fixed this year, following CVE-2026-2441, CVE-2026-3909, and CVE-2026-3910.CVE-2026-3909Google · ChromeThis is the fourth actively exploited Chrome zero-day fixed this year, following CVE-2026-2441, CVE-2026-3909, and CVE-2026-3910.CVE-2026-3910Google · ChromeThis is the fourth actively exploited Chrome zero-day fixed this year, following CVE-2026-2441, CVE-2026-3909, and CVE-2026-3910.CVE-2026-5281Google · ChromeGoogle released emergency updates to patch a use-after-free vulnerability in Dawn (WebGPU) tracked as CVE-2026-5281 that was being exploited in the wild, marking the fourth Chrome zero-day fixed this year.