
TrueConf Zero-Day Exploited to Target Southeast Asian Government Networks
Summary
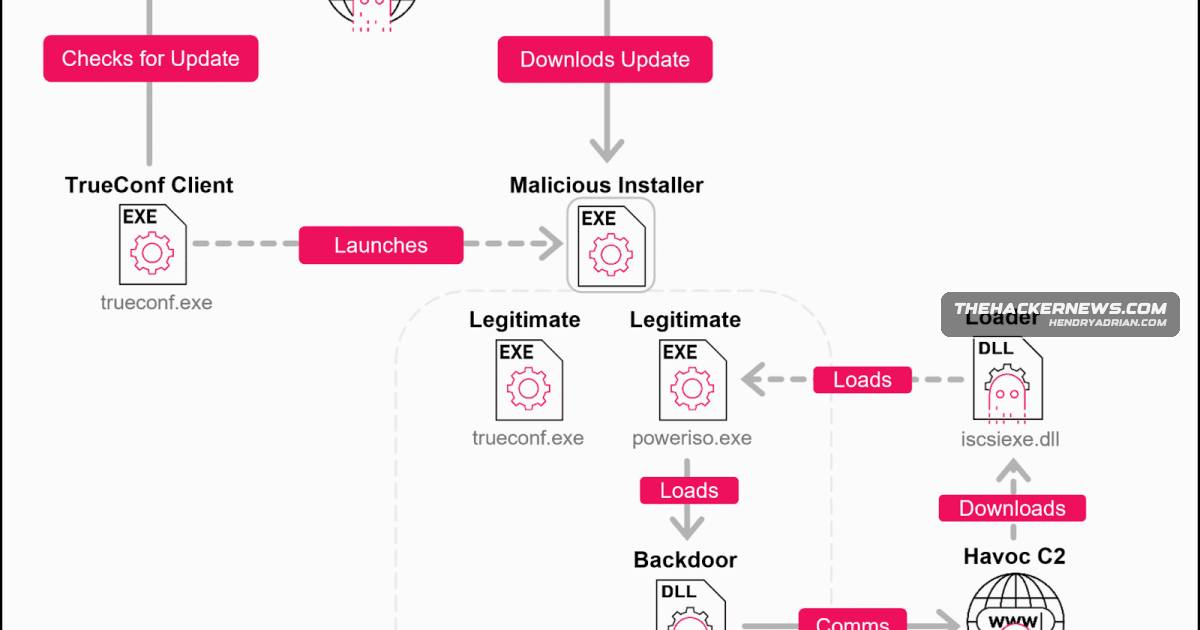
Check Point says attackers exploited CVE-2026-3502 in TrueConf’s Windows updater to push tampered updates to Southeast Asian government targets. The TrueChaos campaign likely aimed to deploy Havoc; TrueConf fixed the flaw in client v8.5.3.
Key points
- CVE-2026-3502 (CVSS 7.8) allows tampered update code because TrueConf’s Windows client does not adequately validate updates.
- An attacker controlling an on-premises TrueConf server can push a malicious update to connected clients.
- Check Point observed exploitation beginning in early 2026 in the TrueChaos campaign targeting government entities in Southeast Asia.
- A DLL backdoor, 7z-x64.dll, was observed conducting reconnaissance, establishing persistence, and retrieving iscsiexe.dll from an FTP server at 47.237.15[.]197.
- The retrieved payload uses poweriso.exe to sideload the backdoor; the exact final-stage malware is unclear, though deployment of the Havoc C2 framework is assessed as likely.
- Attribution to a Chinese-nexus actor is assessed with moderate confidence, based on observed tactics and infrastructure and a report that the same victim was targeted by ShadowPad during the same period.
- TrueConf patched the flaw in Windows client version 8.5.3.
Article Details
- Vulnerability Types
- Missing integrity checks in the update mechanism, allowing tampered updates to execute arbitrary code
- Severity
- High (CVSS 7.8)
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 47[.]237[.]15[.]197 | FTP server used to retrieve additional payloads during the TrueChaos activity. |
MITRE ATT&CK
T1105 · Ingress Tool TransferThe DLL implant retrieved additional payloads, including iscsiexe.dll, from an FTP server.T1195.002 · Compromise Software Supply ChainThe attacker replaced a legitimate TrueConf client update with a malicious update distributed through the product's update mechanism.T1574.002 · DLL Side-LoadingThe attack used DLL side-loading to launch a DLL backdoor, with poweriso.exe used to sideload it.