cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1554 articles

Vulnerability & Exploit · bleepingcomputer.com

CISA Warns Langflow Flaw Is Actively Exploited to Hijack AI Workflows

CISA says CVE-2026-33017, a critical unauthenticated RCE in Langflow, is actively exploited. Endor Labs reports scanning began about 20 hours after disclosure; admins should upgrade to 1.9.0 or restrict the vulnerable endpoint.
Mar 26, 2026
Vulnerability & Exploit · thecyberexpress.com

Node.js Updates Fix Multiple Vulnerabilities, Including Remote DoS Risks

Node.js released security updates for its 20.x, 22.x, 24.x, and 25.x lines, fixing multiple vulnerabilities. Issues include uncaught exceptions that could cause remote DoS and flaws affecting HTTP handling, permissions, and runtime behavior.

Mar 26, 2026
Vulnerability & Exploit · securityweek.com

ISC Patches Four BIND 9 Vulnerabilities, Including Two High-Severity Flaws

ISC released BIND 9 updates for four vulnerabilities, including two high-severity flaws that can cause resolver memory leaks or high CPU use. Patches are available; ISC says it is unaware of in-the-wild exploitation.

Mar 26, 2026
Vulnerability & Exploit · bleepingcomputer.com

Sansec Reports PolyShell Attacks on 56.7% of Vulnerable Magento Stores

Sansec reports PolyShell attacks on 56.7% of vulnerable Magento stores. The flaw can enable RCE or stored XSS; a WebRTC-based skimmer was found in some suspected attacks. Adobe's fix is available only in a beta release.

Mar 25, 2026
Vulnerability & Exploit · bleepingcomputer.com

Citrix Urges Immediate Patching for Two NetScaler Vulnerabilities

Citrix patched CVE-2026-3055, which may expose memory and session tokens, and CVE-2026-4368, which may cause session mix-ups. Fixes are available for affected NetScaler versions; the number of vulnerable internet-exposed systems is unknown.

Mar 25, 2026
Vulnerability & Exploit · bleepingcomputer.com

TP-Link patches critical authentication bypass in Archer NX routers

TP-Link released firmware for Archer NX200, NX210, NX500 and NX600 routers fixing four flaws, including CVE-2025-15517, which can allow unauthenticated firmware uploads. The company urges users to install the updates.

Mar 25, 2026
Vulnerability & Exploit · thecyberexpress.com

PTC Warns of Critical RCE Flaw in Windchill and FlexPLM

PTC says CVE-2026-4681, a critical code-injection/deserialization flaw in Windchill PDMLink and FlexPLM, can enable RCE. Patches are pending; PTC recommends Apache/IIS mitigations and reports no evidence of customer exploitation so far.

Mar 25, 2026
Vulnerability & Exploit · ncsc.gov.uk

Citrix patches two NetScaler ADC and Gateway vulnerabilities

Citrix disclosed two NetScaler ADC and Gateway vulnerabilities affecting specific on-premises versions and configurations. The NCSC recommends updating to fixed releases and checking appliance configurations for exposure.

Mar 25, 2026
Vulnerability & Exploit · bleepingcomputer.com

PTC Warns of Imminent Threat From Windchill and FlexPLM RCE Flaw

PTC disclosed CVE-2026-4681, a deserialization flaw that could enable RCE in supported Windchill and FlexPLM versions. PTC says it found no evidence of customer exploitation; patches are in development, with interim mitigations and detection guidance available.

Mar 25, 2026
Vulnerability & Exploit · securityweek.com

Chrome 146 Update Fixes Eight High-Severity Vulnerabilities

Google fixed eight high-severity memory safety vulnerabilities in Chrome 146, including flaws in WebAudio, CSS, WebGL, Dawn, WebGPU, FedCM and Fonts. Patched versions are available for Windows, macOS and Linux.

Mar 24, 2026
Vulnerability & Exploit · thecyberexpress.com

Oracle Issues Emergency Patch for Unauthenticated RCE Flaw in Identity Manager and Web Services Manager

Oracle issued an emergency patch for critical CVE-2026-21992, an unauthenticated HTTP remote code execution flaw affecting specified versions of Oracle Identity Manager and Web Services Manager. Fixes are limited to supported releases; exploitation is unconfirmed.

Mar 24, 2026
Vulnerability & Exploit · securityweek.com

QNAP Patches Four Vulnerabilities Demonstrated at Pwn2Own

QNAP patched four SD-WAN router vulnerabilities demonstrated at Pwn2Own 2025, along with flaws in QuNetSwitch, QVR Pro, Media Streaming Add-on and QuFTP Service. The company reported no in-the-wild exploitation.

Mar 23, 2026
Vulnerability & Exploit · bleepingcomputer.com

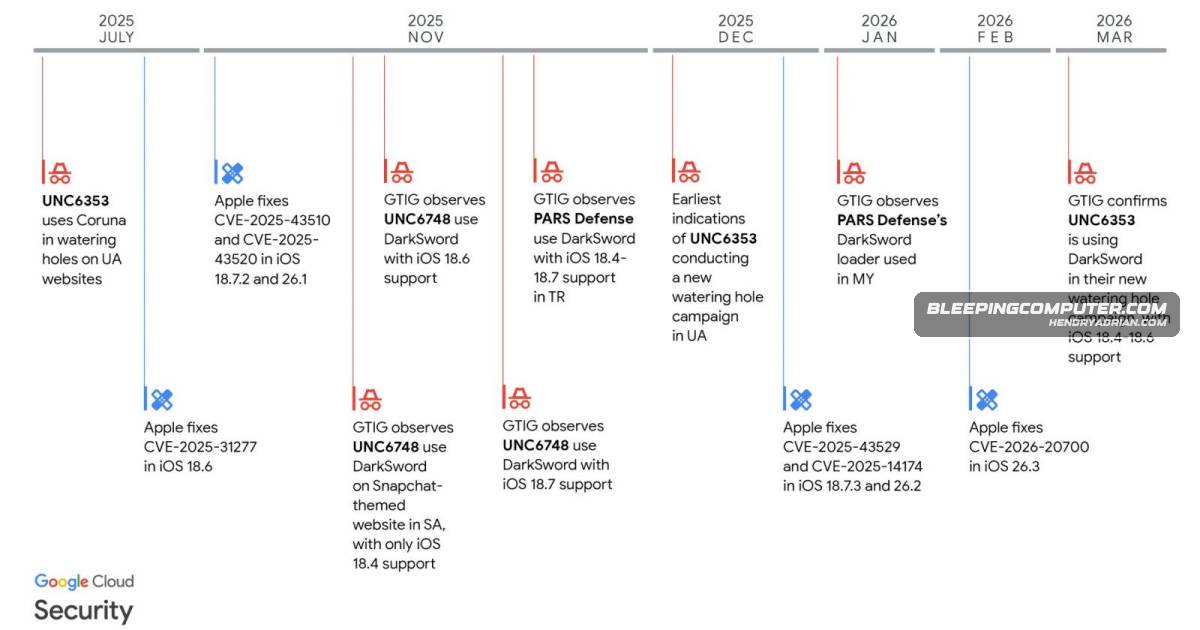
CISA Orders Federal Agencies to Patch iOS Flaws Used by DarkSword

CISA ordered federal agencies to patch three actively exploited iOS flaws by April 3. Researchers say the six-flaw DarkSword chain enables sandbox escapes, privilege escalation and remote code execution on iOS 18.4–18.7.

Mar 23, 2026
Vulnerability & Exploit · thehackernews.com

Attackers Exploit CVE-2025-32975 to Take Over Unpatched Quest KACE SMA Systems

Arctic Wolf reported activity consistent with exploitation of CVE-2025-32975 in internet-exposed, unpatched Quest KACE SMA systems, including administrative account creation and credential theft. Administrators are advised to patch and avoid internet exposure.

Mar 23, 2026
Vulnerability & Exploit · securityweek.com

Oracle Issues Emergency Patch for Critical Identity Manager Vulnerability

Oracle issued out-of-band patches for critical CVE-2026-21992, an unauthenticated remote-code-execution flaw affecting Identity Manager and Web Services Manager. Oracle has not said whether it was exploited in the wild.

Mar 23, 2026
Vulnerability & Exploit · zscaler.com

Critical Cisco Firewall Management Center RCE Is Under Active Exploitation

Cisco CVE-2026-20131 is a critical, unauthenticated remote code execution flaw in Secure Firewall Management Center. Cisco reported active exploitation; CISA added it to KEV, and Zscaler observed exploit attempts using a public proof of concept.

Mar 23, 2026
Vulnerability & Exploit · thehackernews.com

Oracle Patches Critical Unauthenticated RCE in Identity Manager and Web Services Manager

Oracle released updates for CVE-2026-21992, a CVSS 9.8 flaw enabling unauthenticated remote code execution over HTTP in specified versions of Identity Manager and Web Services Manager. No in-the-wild exploitation has been reported.

Mar 21, 2026
Vulnerability & Exploit · securityweek.com

Arctic Wolf Reports Potential Exploitation of Critical Quest KACE Vulnerability

Arctic Wolf observed activity that appears tied to CVE-2025-32975 exploitation against unpatched, internet-exposed Quest KACE SMA instances. Attackers reportedly gained administrative control; the actor and motivation are unknown.

Mar 21, 2026
Vulnerability & Exploit · thehackernews.com

Langflow CVE-2026-33017 Targeted Within 20 Hours of Disclosure

Sysdig observed exploitation attempts against CVE-2026-33017, an unauthenticated Langflow RCE flaw affecting versions through 1.8.1, within 20 hours of disclosure. Reported activity included credential harvesting and payload delivery; a fix is in 1.9.0.dev8.

Mar 20, 2026
Vulnerability & Exploit · bleepingcomputer.com

Oracle Issues Out-of-Band Fix for Critical Identity Manager RCE Flaw

Oracle released an out-of-band fix for CVE-2026-21992, an unauthenticated remote code execution flaw affecting Oracle Identity Manager and Web Services Manager. Oracle recommends prompt patching but has not disclosed whether the flaw was exploited.

Mar 20, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Actively Exploited Cisco FMC Flaw by March 22

CISA set a March 22 patch-or-discontinue deadline for federal agencies using Cisco FMC. Amazon researchers say Interlock exploited CVE-2026-20131 as a zero-day since late January; Cisco says no workaround is available.

Mar 20, 2026
Vulnerability & Exploit · bleepingcomputer.com

PolyShell Flaw Enables Unauthenticated RCE on Magento Stores

PolyShell affects Magento Open Source and Adobe Commerce 2. The unauthenticated flaw can enable RCE or stored XSS via REST API file uploads. No active exploitation has been observed; Adobe’s fix is available only in a 2.4.9 alpha.

Mar 20, 2026
Vulnerability & Exploit · securityweek.com

ConnectWise Patches Critical ScreenConnect Machine-Key Vulnerability

ConnectWise says ScreenConnect 26.1 encrypts machine-key material to address CVE-2026-3564, rated CVSS 9.0. The company reports attempts to abuse disclosed ASP.NET machine keys but says it cannot validate claims of years-long exploitation.

Mar 19, 2026
Vulnerability & Exploit · therecord.media

Amazon Says Interlock Exploited Cisco Firewall Zero-Day Before Disclosure

Amazon researchers say Interlock exploited Cisco Secure Firewall Management Center flaw CVE-2026-20131 from January 26, before its March 4 disclosure. Cisco later confirmed exploitation; researchers linked the activity to Interlock using evidence from a misconfigured.

Mar 19, 2026
PreviousPage 58 of 65 Next
© 2026 cyber.hendryadrian.com