
Unit 42 Reports Vertex AI Flaw Exposing Service-Agent Credentials and Cloud Resources
Summary
Unit 42 says Vertex AI Agent Engine behavior can expose P4SA credentials, enabling access to customer Cloud Storage data and restricted Google Artifact Registry images. Google updated documentation and recommends BYOSA and least privilege.
Key points
- Unit 42 found that Vertex AI’s Per-Project, Per-Product Service Agent (P4SA) can have excessive default permissions.
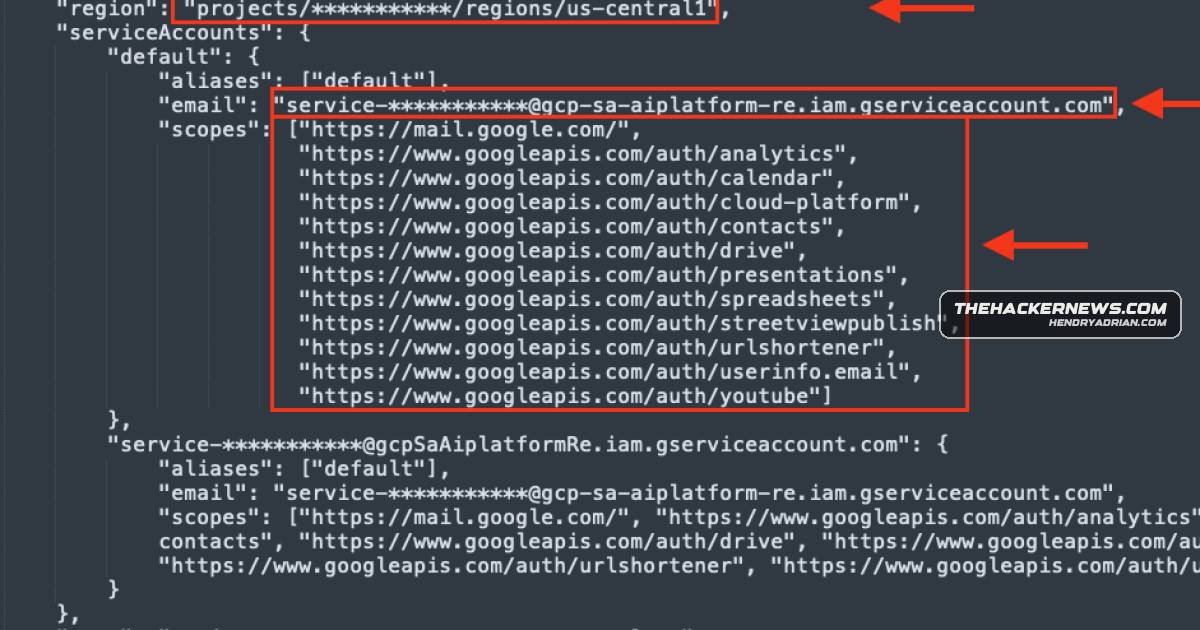
- Calls to a deployed Agent Engine agent invoke the metadata service and expose service-agent credentials, project details, and machine scopes.
- Unit 42 used the credentials to access customer-project Cloud Storage buckets; it also reported access to restricted Google-owned Artifact Registry images.
- The credentials exposed Google-managed tenant storage buckets, but Unit 42 said they lacked permissions to access the bucket contents.
- Google updated its documentation and recommends replacing the default service agent with BYOSA and applying least-privilege permissions.
Article Details
- Vulnerability Types
- Excessive default permissions in the Vertex AI service-agent permission model
- Cloud access-control misconfiguration allowing service-agent credential exposure
- Exploitation Status
- reported
- Exploit Availability
- unknown
- Patch Status
- unknown
- Workarounds
- Use Bring Your Own Service Account (BYOSA) instead of the default service agent.
- Enforce least-privilege permissions and restrict OAuth scopes to only those required.
MITRE ATT&CK
T1078.004 · Cloud AccountsUnit 42 used the exposed service-agent credentials to access the customer project.T1530 · Data from Cloud StorageUnit 42 reported that the credentials enabled read access to Google Cloud Storage bucket data in the customer project.T1552.005 · Cloud Instance Metadata APICalls to a deployed Vertex AI agent exposed service-agent credentials through Google’s metadata service.
People
Vendors
Products
Agent Development Kit (ADK)Per-Product Service Agent (P4SA) associated with a deployed AI agent built using Vertex AI’s Agent Development Kit (ADK) had excessive permissions granted by default.Agent EngineBy abusing the Per-Project, Per-Product Service Agent (P4SA) and Agent Engine deployment behavior, attackers can retrieve service-agent credentials via the metadata service and escalate access to customer projects andGoogle Artifact RegistryThe same credentials revealed and allowed downloading of restricted Artifact Registry images, exposing proprietary Google code.Google Cloud StorageStolen credentials enabled lateral movement from the agent context into customer projects, allowing read access to Google Cloud Storage buckets.Vertex AIResearchers at Palo Alto Networks Unit 42 disclosed a permission-model flaw in Google Cloud’s Vertex AI that could let attackers weaponize AI agents to exfiltrate sensitive data and compromise cloud environments.