
Attackers Reportedly Exploit Critical FortiClient EMS SQL Injection
Summary
Defused reports active exploitation of CVE-2026-21643, an unauthenticated SQL injection in FortiClient EMS 7.4.4 that can enable code execution. Fortinet has not confirmed exploitation; upgrading to 7.4.5 or later patches the flaw.
Key points
- Defused reports that attackers began exploiting CVE-2026-21643; Fortinet has not confirmed the activity or updated its advisory to flag in-the-wild exploitation.
- The SQL injection affects FortiClient EMS 7.4.4 and can let unauthenticated attackers execute arbitrary code through the web interface.
- The reported exploit smuggles SQL statements through the HTTP 'Site' header.
- Fortinet recommends upgrading to FortiClient EMS 7.4.5 or later.
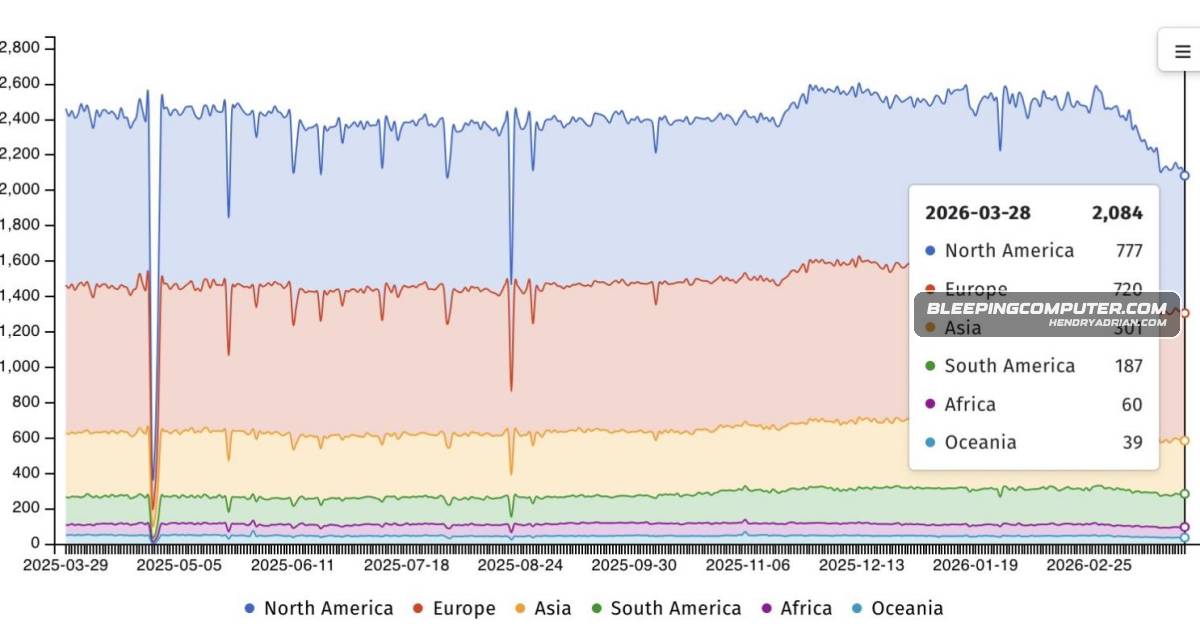
- Shadowserver was tracking more than 2,000 EMS instances with web interfaces exposed online, including over 1,400 IPs in the United States and Europe.
Article Details
- Vulnerability Types
- SQL injection
- Severity
- Critical
- Affected Versions
- FortiClient EMS 7.4.4
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
CVE
CVE-2026-21643Fortinet · FortiClientEMSAttackers are actively exploiting CVE-2026-21643, a critical SQL injection in Fortinet’s FortiClient EMS that allows unauthenticated actors to execute arbitrary code via the EMS web interface.CVE-2026-24858Fortinet · FortiAnalyzer; Fortinet · FortiManager; +5 moreMost recently, Fortinet mitigated CVE-2026-24858 zero-day attacks by blocking FortiCloud SSO connections from devices running vulnerable firmware versions.
People
Threat Actors
Vendors
Products
FortiClient EMSAttackers are actively exploiting CVE-2026-21643, a critical SQL injection in Fortinet’s FortiClient EMS that allows unauthenticated actors to execute arbitrary code via the EMS web interface.FortiCloud SSOMost recently, Fortinet mitigated CVE-2026-24858 zero-day attacks by blocking FortiCloud SSO connections from devices running vulnerable firmware versions.