
CISA Sets April 2 Deadline to Patch Citrix Flaw Reported Exploited in the Wild
Summary
CISA added CVE-2026-3055 to its KEV catalog and ordered U.S. civilian agencies to patch by April 2. Watchtowr reported exploitation that could expose admin session IDs; Citrix has not confirmed ongoing attacks.
Key points
- CISA added CVE-2026-3055 to its Known Exploited Vulnerabilities catalog and ordered federal civilian agencies to secure affected appliances by April 2.
- The input-validation flaw affects Citrix ADC and Gateway appliances configured as SAML identity providers.
- The flaw can expose sensitive information; Watchtowr reported that attackers could steal administrator session IDs and potentially take over unpatched appliances.
- Watchtowr reported abuse in the wild after Citrix released security updates on March 23, but Citrix has not confirmed that attacks are ongoing.
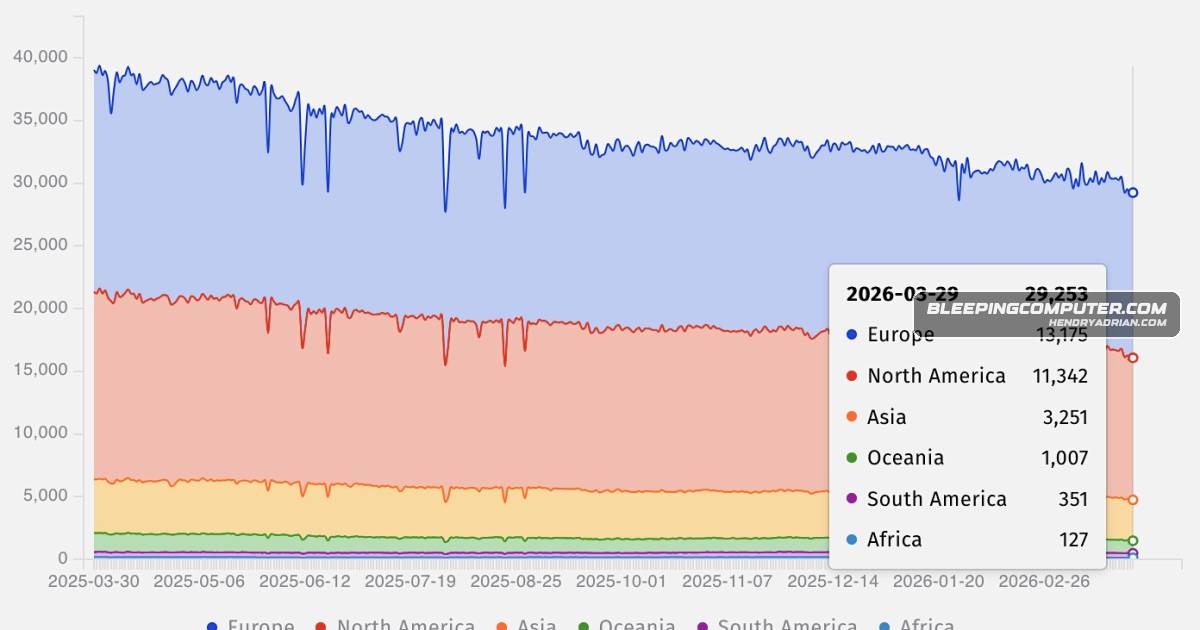
- Shadowserver tracks nearly 30,000 exposed NetScaler ADC appliances and more than 2,300 Gateway instances; the number vulnerable or already patched is unknown.
- CISA urged private-sector defenders as well as federal agencies to prioritize patching and follow vendor mitigation guidance.
Article Details
- Vulnerability Types
- Insufficient input validation
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Apply mitigations per vendor instructions; discontinue use if mitigations are unavailable.
MITRE ATT&CK
CVE
Vendors
Products
Citrix ADCThe vulnerability stems from insufficient input validation and affects Citrix ADC and Citrix Gateway appliances configured as SAML identity providers.Citrix GatewayThe vulnerability stems from insufficient input validation and affects Citrix ADC and Citrix Gateway appliances configured as SAML identity providers.Citrix NetScalerfederal agencies to patch Citrix NetScaler appliances by April 2 to address CVE-2026-3055, an actively exploited input-validation flaw that can expose sensitive SAML IDP data.